
On this page
- Quick Reference (60 Seconds)
- What the Standard Actually Requires
- Why Outsourced Development Security Matters
- Scope and Applicability
- Key Definitions and Terminology
- Relationship to Other Controls
- Implementation Roadmap (Week-by-Week)
- Detailed Implementation Guidance
- Tools, Technologies, and Solutions
- Policy and Procedure Templates
- Risk Assessment and Treatment
- Audit and Compliance Checklist
- Metrics and KPIs
- Common Pitfalls and How to Avoid Them
- Illustrative Scenarios
- Multi-Framework Mapping
- Regulatory and Industry Context
- Roles and Responsibilities (RACI)
- Documentation and Evidence Requirements
- Continuous Improvement
- FAQ
- References and Further Reading
Quick Reference (60 Seconds)
Control: A.8.30, Outsourced Development
Purpose: Ensure security requirements are defined, communicated, and enforced when software development is outsourced to third parties, protecting the organization from supply chain risks.
Who it applies to: All organizations that use third-party developers, offshore teams, contractors, or managed development services.
Minimum viable actions:
- Include security requirements in all outsourcing contracts and RFPs
- Conduct security due diligence before selecting vendors
- Require vendors to comply with your secure development lifecycle
- Perform security acceptance testing on all vendor deliverables
- Maintain audit rights and right-to-assess clauses in contracts
Key deliverables: Outsourced Development Security Policy, Vendor Security Requirements, Contract Security Clauses, Vendor Assessment Report, Security Acceptance Checklist.
Audit questions you should be able to answer:
- How do you ensure outsourced developers follow your security requirements?
- What security clauses are in your outsourcing contracts?
- How do you assess vendor security before engagement?
- What security testing is performed on vendor-delivered code?
What the Standard Actually Requires
Figure · Process
What A.8.30 asks you to do
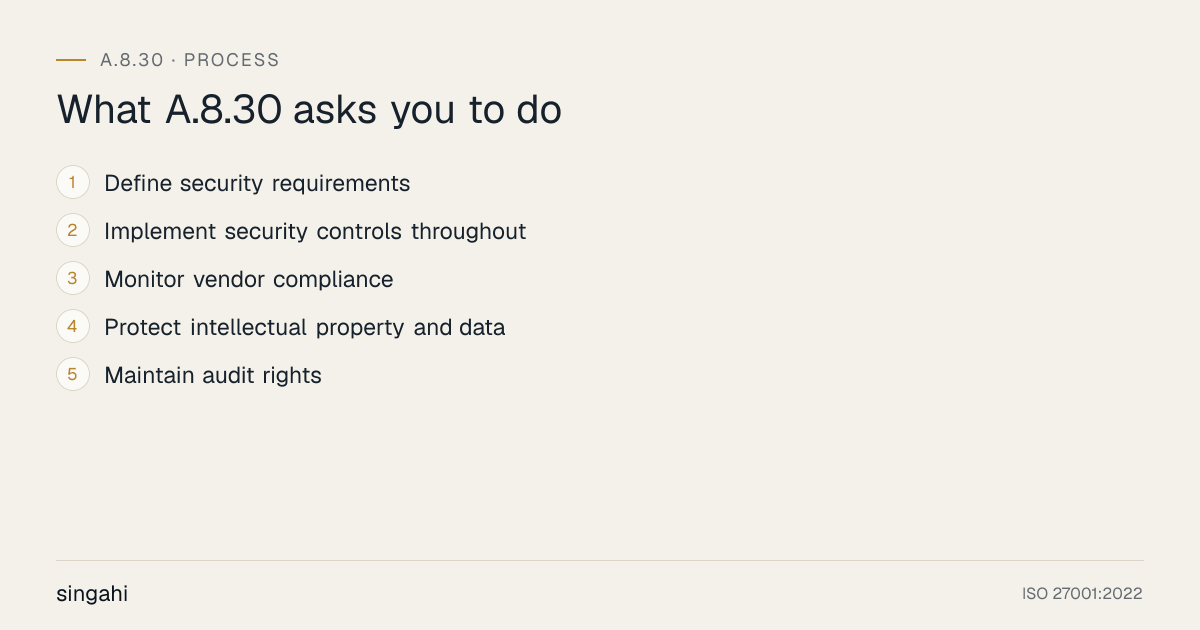
Annex A 8.30 asks organizations to direct, monitor, and review outsourced system development.
This control is about supply chain security in software development. The standard expects organizations to:
- Define security requirements for outsourcing, Security must be explicitly addressed in outsourcing arrangements
- Implement security controls throughout the outsourced development lifecycle, From vendor selection to delivery to ongoing monitoring
- Monitor vendor compliance, Regular assessment and verification that security requirements are being met
- Protect intellectual property and data, Ensure vendor access to sensitive information is controlled and monitored
- Maintain audit rights, The organization must be able to verify vendor security independently
What the Standard Does NOT Require
- The standard does not mandate that all development be in-house
- It does not require specific vendor certifications (though they may be beneficial)
- It does not require continuous monitoring of every vendor action, but rather appropriate oversight based on risk
- It does not prevent offshore or nearshore development when security controls are applied
Why Outsourced Development Security Matters
The Supply Chain Risk
Outsourced development introduces a supply chain risk that is often underestimated. The vendor has:
- Access to your source code, architecture, and business logic
- Access to your data (test data, production data, customer data)
- Access to your systems (development environments, repositories, CI/CD pipelines)
- The ability to introduce backdoors, vulnerabilities, or malicious code
- Control over components that will run in your production environment
Real-world incidents:
- SolarWinds (2020): Attackers compromised the software build process of a third-party vendor, inserting backdoors into updates that were distributed to 18,000+ organizations, including Fortune 500 companies and government agencies.
- Codecov (2021): Attackers compromised the Bash Uploader script used by Codecov, a code coverage tool. The script was used by thousands of organizations, and the compromise exposed environment variables and credentials from CI/CD pipelines.
- Kaseya VSA (2021): Attackers exploited a zero-day vulnerability in Kaseya's VSA software, a remote management tool used by MSPs. The attack impacted up to 1,500 downstream businesses through the supply chain.
- Log4j (2021): While not an outsourcing issue per se, it demonstrated how a single third-party component can create systemic risk across millions of applications.
The Indian Context
- Massive outsourcing volume: Indian vendors serve Fortune 500 companies, governments, and startups globally
- Offshore access: Vendors have remote access to client systems, repositories, and data
- Data residency concerns: Client data may be processed in India, requiring DPDP Act 2023 compliance
- IP protection: Source code and algorithms are valuable intellectual property at risk of theft or misuse
- Subcontracting: Vendors may further subcontract work, creating invisible supply chain risks
- Regulatory compliance: Vendors must comply with client regulations (PCI DSS, GDPR, HIPAA, RBI)
- Talent turnover: High employee turnover in Indian IT services can lead to knowledge gaps and security inconsistencies
Scope and Applicability
In Scope
This control applies to:
- Full outsourcing: Complete application development by third-party vendors
- Partial outsourcing: Modules, components, or features developed by contractors
- Offshore development: Development performed by teams in other countries
- Nearshore development: Development performed by teams in neighboring countries
- Staff augmentation: Contract developers working within your organization
- Managed services: Third-party teams managing development operations
- Subcontracting: Vendors further subcontracting work to other parties
- Open source development: Customization of open source components by third parties
- Cloud development services: Using cloud-based development platforms managed by third parties
Out of Scope (with caveats)
- COTS software procurement (covered by A.5.24, A.8.9)
- Unmodified SaaS services (covered by A.5.24, A.8.8)
- Hardware procurement (covered by A.7.10, A.8.1)
- IT support services without development (covered by A.6.1, A.8.1)
Caveat: If a SaaS vendor customizes code for you, or if COTS requires significant customization, outsourced development controls apply.
Applicability by Organization Type
| Organization Type | Applicability | Typical Outsourcing Scenarios |
|---|---|---|
| Large enterprises | Critical | Full application outsourcing, offshore development centers |
| Growing companies | High | Staff augmentation, project-based outsourcing |
| Startups | High | MVP development, offshore teams, contractor-based development |
| Government | Critical | E-governance projects, vendor development of citizen portals |
| Financial services | Critical | Core banking systems, fintech partnerships, payment processing |
| Healthcare | Critical | EHR development, telemedicine platforms, health apps |
| E-commerce | High | Platform development, mobile apps, payment integration |
| NGOs | Moderate | Website development, CRM customization, grant management systems |
Key Definitions and Terminology
| Term | Definition |
|---|---|
| Outsourced Development | Software development activities performed by a third-party vendor rather than in-house staff |
| Vendor Security Assessment | Evaluation of a vendor's security posture before engagement |
| Right-to-Audit Clause | Contractual provision allowing the client to audit vendor security controls |
| Code Escrow | Arrangement where source code is held by a third party and released under defined conditions |
| Service Level Agreement (SLA) | Contractual commitment defining service standards, including security |
| Statement of Work (SOW) | Document defining the scope, deliverables, and timeline for outsourced work |
| Master Service Agreement (MSA) | Overarching contract governing the relationship, including security terms |
| Non-Disclosure Agreement (NDA) | Contract protecting confidential information shared with the vendor |
| Data Processing Agreement (DPA) | Contract governing how personal data is processed by the vendor |
| Backdoor | Hidden access mechanism in code that bypasses normal authentication |
| Subcontractor | A third party engaged by the primary vendor to perform part of the work |
| Knowledge Transfer (KT) | Process of transferring project knowledge from vendor to client |
| Acceptance Testing | Testing performed by the client to verify that deliverables meet requirements |
| Vendor Risk Management | Process of identifying, assessing, and mitigating risks from third-party vendors |
| Supply Chain Attack | Cyberattack that targets less secure elements in the supply chain to compromise the ultimate target |
| Software Bill of Materials (SBoM) | Inventory of all components, libraries, and dependencies in software |
| Audit Trail | Record of all activities performed by the vendor, including access and changes |
Relationship to Other Controls
Directly Related Controls
| Control | Relationship |
|---|---|
| A.5.1, Policies for information security | Outsourced development policy must align with the overarching information security policy |
| A.5.8, Information security in project management | Security must be embedded in outsourced project management |
| A.5.9, Inventory of information and other associated assets | Vendor access to assets must be inventoried and controlled |
| A.5.10, Acceptable use of information and other associated assets | Vendor acceptable use must be defined and enforced |
| A.5.18, Intellectual property rights | IP protection clauses must be in outsourcing contracts |
| A.5.19, Records of intellectual property rights | Vendor contributions to IP must be documented |
| A.5.20, Information security in supplier relationships | Vendor relationships must be managed securely |
| A.5.21, Monitoring and review of supplier services | Vendor services must be monitored and reviewed |
| A.5.22, Information security in use of cloud services | Cloud development platforms must be managed securely |
| A.5.24, Information security incident management planning and preparation | ICT services used by vendors must be managed securely |
| A.5.25, Assessment and decision on information security events | Vendor risks must be assessed and treated |
| A.5.36, Compliance with policies, rules and standards | Vendors must comply with client security policies |
| A.5.37, Documented operating procedures | Vendor procedures must be documented |
| A.6.1, Screening | Vendor personnel must be screened |
| A.6.2, Terms and conditions of employment | Vendor employment terms must include security responsibilities |
| A.8.25, Secure development life cycle | Vendor must follow client's SDLC or equivalent |
| A.8.26, Application security requirements | Security requirements must be communicated to vendors |
| A.8.27, Secure system architecture | Vendor architecture must be reviewed for security |
| A.8.28, Secure coding | Vendor code must be written securely |
| A.8.29, Security testing in development and acceptance | Vendor deliverables must be security tested |
| A.8.31, Separation of development, test and production environments | Vendor must maintain environment separation |
| A.8.33, Test data | Vendor must handle test data securely |
| A.8.34, Protection of information systems during audit testing | Vendor must protect client systems during testing |
Framework Mapping
| Framework | Relevant Control / Reference |
|---|---|
| NIST CSF 2.0 | GV.SC-1 (Supply chain risk management), GV.SC-2 (Supplier vetting), PR.IP-3 (Change management) |
| NIST SP 800-53 Rev 5 | SA-9 (External information system services), SA-12 (Supply chain protection), SR-2 (Supply chain risk management), SR-3 (Trustworthiness) |
| PCI DSS 4.0 | Req 12.8 (Third-party service providers), Req 12.8.3 (Vendor due diligence), Req 12.8.4 (Vendor acceptance) |
| COBIT 2019 | APO10.01 (Managed vendor relationships), APO10.02 (Managed contracts), APO10.03 (Managed vendor risk), BAI03.01 (Managed solutions) |
| CIS Controls v8 | Control 15 (Service provider management), Control 16 (Application software security) |
| OWASP SAMM | Governance (Strategy & Metrics, Policy & Compliance), Implementation (Secure Build) |
| BSIMM | SR (Software Security Initiatives), SFD (Security Features and Design) |
| GDPR | Art 28 (Processors), Art 32 (Security of processing) |
| DPDP Act 2023 | Section 8 (Data Fiduciaries), Section 8(5) (Reasonable security safeguards)) |
Implementation Roadmap (Week-by-Week)
Figure · Tiers
Maturity levels for outsourced development
- OptimizingContinuous improvement
- Quantitatively ManagedMetrics tracked, risk-based vendor tiers
- DefinedStandardized assessment for all vendors
- ManagedBasic assessment for some vendors
- Ad-hocNo vendor security assessment
Phase 1: Foundation (Weeks 1–3)
Week 1: Policy and Contract Templates
- Draft the Outsourced Development Security Policy
- Create security requirements template for RFPs
- Develop contract security clauses (MSA, SOW, NDA, DPA)
- Define vendor security assessment criteria
Week 2: Vendor Assessment Framework
- Create vendor security assessment questionnaire
- Define vendor risk scoring methodology
- Establish vendor security tiers (critical, high, medium, low)
- Create vendor onboarding security checklist
Week 3: Baseline Assessment
- Inventory all current outsourced development vendors
- Assess current vendor security posture
- Identify gaps and high-risk vendors
- Document baseline metrics
Deliverables: Policy draft, Contract templates, Assessment framework, Vendor inventory, Baseline report
Phase 2: Pilot (Weeks 4–6)
Week 4-5: Pilot Vendor Assessment
- Select 2-3 critical vendors for pilot assessment
- Conduct security assessments using the questionnaire
- Review vendor contracts and add security clauses
- Test security acceptance process for one deliverable
Week 6: Refinement
- Refine assessment questionnaire based on pilot feedback
- Update contract templates with lessons learned
- Improve acceptance testing process
- Train vendor managers on security requirements
Deliverables: Pilot assessments, Updated templates, Improved process, Trained staff
Phase 3: Rollout (Weeks 7–12)
Week 7-9: Organization-Wide Deployment
- Assess all existing vendors using the framework
- Update all contracts with security clauses (where feasible)
- Implement security acceptance testing for all vendor deliverables
- Establish vendor monitoring and review schedule
Week 10-12: Process Integration
- Integrate vendor security into procurement process
- Integrate vendor security into project management
- Establish vendor security dashboard
- Implement ongoing vendor monitoring
Deliverables: All vendor assessments, Updated contracts, Acceptance testing deployed, Monitoring established
Phase 4: Optimization (Weeks 13–16)
Week 13-14: Metrics and Monitoring
- Define and collect KPIs (see Section 13)
- Conduct first internal audit of vendor security process
- Identify gaps and improvement opportunities
Week 15-16: Continuous Improvement
- Update assessment questionnaire with new threats
- Implement automated vendor monitoring where possible
- Enhance vendor security training
- Update contract templates with regulatory changes
Deliverables: KPI dashboard, Internal audit report, Updated templates, Automated monitoring
Maturity Model
| Level | Description | Typical Timeline |
|---|---|---|
| 1, Ad-hoc | No vendor security assessment, contracts lack security clauses, no acceptance testing | Pre-implementation |
| 2, Managed | Basic assessment for some vendors, generic security clauses, informal acceptance | Weeks 1–3 |
| 3, Defined | Standardized assessment for all vendors, tailored security clauses, formal acceptance testing, monitoring | Weeks 4–8 |
| 4, Quantitatively Managed | Metrics tracked, risk-based vendor tiers, automated monitoring, regular re-assessment | Weeks 9–12 |
| 5, Optimizing | Continuous improvement, real-time vendor monitoring, predictive risk analytics, automated compliance verification | Ongoing |
Detailed Implementation Guidance
Figure · Matrix
Comparison: 90-100 to <50
The Outsourced Development Security Lifecycle
Vendor Selection → Contract Negotiation → Onboarding → Development →
Delivery → Acceptance → Deployment → Monitoring → Offboarding
Stage 1: Vendor Selection
Security Due Diligence Checklist:
| Category | Assessment Questions | Evidence Requested |
|---|---|---|
| Certifications | Does the vendor hold ISO 27001, SOC 2, CMMI? | Certificate copies, audit reports |
| Security Organization | Does the vendor have a CISO, security team, secure SDLC? | Org chart, security team profiles |
| Past Incidents | Has the vendor had security breaches in the past 3 years? | Incident disclosure, remediation evidence |
| Data Handling | How does the vendor handle client data? | Data handling policy, encryption standards |
| Access Controls | How does the vendor control access to client environments? | Access control policy, MFA evidence |
| Code Security | Does the vendor use SAST, DAST, secure coding? | Tool screenshots, process documentation |
| Subcontracting | Does the vendor subcontract? If so, how is it managed? | Subcontractor policy, security clauses |
| Personnel Security | Does the vendor screen employees? | Background check policy, screening evidence |
| Physical Security | Are development centers physically secure? | Physical security assessment, photos |
| Business Continuity | Does the vendor have BCP/DR plans? | BCP/DR documentation, test records |
| Compliance | Can the vendor comply with client regulations (PCI DSS, GDPR, DPDP)? | Compliance attestation, audit reports |
| IP Protection | How does the vendor protect client IP? | IP policy, code escrow capability |
| Exit Management | How does the vendor handle project termination? | Exit management process, data deletion |
| Insurance | Does the vendor have cyber insurance? | Insurance certificate |
| References | Can the vendor provide security references from similar clients? | Reference contacts |
Vendor Risk Scoring:
| Score | Risk Tier | Action Required |
|---|---|---|
| 90-100 | Low Risk | Standard contract clauses, annual review |
| 70-89 | Medium Risk | Enhanced contract clauses, bi-annual review, spot checks |
| 50-69 | High Risk | Extensive contract clauses, quarterly review, mandatory testing, on-site audits |
| <50 | Critical Risk | Not recommended for sensitive work; if necessary, extensive controls, continuous monitoring, escrow |
Stage 2: Contract Negotiation
Essential Security Contract Clauses:
1. Security Requirements Clause:
Vendor shall comply with all security requirements specified in
Attachment A (Security Requirements). Vendor shall implement
security controls at least equivalent to the client's ISO 27001
security controls. Vendor shall not introduce vulnerabilities,
backdoors, or malicious code into deliverables.
2. Data Protection Clause:
Vendor shall process all client data in accordance with the
Data Processing Agreement (Attachment B). Vendor shall encrypt
all client data in transit (TLS 1.3) and at rest (AES-256).
Vendor shall not use client data for any purpose other than
performing the services. Vendor shall delete all client data
within 30 days of contract termination.
3. Right-to-Audit Clause:
Client reserves the right to audit vendor's security controls
with 30 days' notice, not more than twice per year. Vendor
shall provide access to relevant personnel, documentation,
and systems. Vendor shall remediate any findings within 60 days.
4. Code Quality and Security Testing Clause:
All deliverables shall undergo SAST, DAST, and SCA before delivery.
Vendor shall provide security test reports with each deliverable.
Zero critical vulnerabilities and no more than [X] high
vulnerabilities are acceptable. All medium vulnerabilities
must be tracked for remediation.
5. Subcontracting Clause:
Vendor shall not subcontract any work without client's prior
written consent. Any approved subcontractor must sign security
agreements equivalent to this contract. Vendor remains
liable for subcontractor security breaches.
6. Incident Notification Clause:
Vendor shall notify client of any security incident affecting
client data or systems within 24 hours of discovery. Vendor
shall cooperate fully in incident investigation and remediation.
7. IP Protection Clause:
All intellectual property created during the engagement shall
be owned by client. Vendor shall not use client IP for any
other purpose. Vendor shall not disclose client code or
architecture to third parties. Code escrow arrangement shall
be maintained per Attachment C.
8. Personnel Security Clause:
Vendor shall conduct background checks on all personnel
accessing client systems or data. Vendor shall ensure
personnel sign confidentiality agreements. Vendor shall
notify client of personnel changes affecting the engagement.
9. Compliance Clause:
Vendor shall comply with all applicable regulations including
PCI DSS, GDPR, DPDP Act 2023, RBI guidelines, and SEBI
regulations as applicable. Vendor shall provide compliance
attestations annually.
10. Liability and Insurance Clause:
Vendor shall maintain cyber insurance with minimum coverage
of [X] crore. Vendor shall be liable for damages resulting
from vendor-introduced security breaches. Vendor shall indemnify
client for regulatory fines resulting from vendor negligence.
Stage 3: Onboarding
Vendor Onboarding Security Checklist:
| # | Checklist Item | Status |
|---|---|---|
| 1 | Security contract clauses signed | ☐ |
| 2 | NDA signed by all vendor personnel | ☐ |
| 3 | Vendor personnel background checks completed | ☐ |
| 4 | Vendor access to client systems provisioned with least privilege | ☐ |
| 5 | MFA enabled for all vendor access | ☐ |
| 6 | Vendor workstation security requirements communicated | ☐ |
| 7 | Secure development environment provisioned | ☐ |
| 8 | Code repository access configured with branch protection | ☐ |
| 9 | CI/CD pipeline access configured with security scanning | ☐ |
| 10 | Test data provided (no production data) | ☐ |
| 11 | Security requirements walkthrough completed | ☐ |
| 12 | Security incident reporting process communicated | ☐ |
| 13 | Vendor security contact established | ☐ |
| 14 | Vendor security training completed | ☐ |
| 15 | Code escrow arrangement activated | ☐ |
| 16 | Monitoring and logging configured for vendor activity | ☐ |
| 17 | Subcontractor approval obtained (if applicable) | ☐ |
| 18 | Compliance attestation obtained | ☐ |
Stage 4: Development Monitoring
Ongoing Vendor Security Monitoring:
| Activity | Frequency | Method |
|---|---|---|
| Code review | Every sprint/iteration | Automated SAST + manual review for critical code |
| Security scanning | Every build | SAST, SCA integrated into CI/CD |
| Access review | Monthly | Review vendor access logs, remove unnecessary access |
| Progress review | Weekly | Security status in project status meetings |
| Vulnerability tracking | Continuous | Track vendor vulnerabilities in client system |
| Compliance check | Quarterly | Verify vendor compliance attestations |
| Security audit | Annually (or bi-annually for high-risk) | On-site or remote audit of vendor controls |
| Incident monitoring | Continuous | Monitor for vendor-reported incidents |
| Subcontractor monitoring | Quarterly | Verify subcontractor security status |
Vendor Activity Monitoring:
- All vendor access to client systems is logged
- Vendor code commits are reviewed for security
- Vendor access to production is restricted and monitored
- Vendor data downloads are tracked and alerted
- Vendor VPN/access sessions are time-limited and reviewed
Stage 5: Delivery and Acceptance
Security Acceptance Process:
- Deliverable Submission: Vendor submits code with security test report (SAST, DAST, SCA results)
- Automated Validation: Client runs SAST, SCA, and secrets detection on delivered code
- Manual Review: Client security team reviews critical/high-risk code paths
- Penetration Testing: Client or third party conducts penetration test on delivered application
- Vulnerability Triage: Findings are triaged, severity assigned, and remediation timeline agreed
- Remediation: Vendor fixes vulnerabilities within SLA
- Re-testing: Client verifies fixes
- Security Sign-off: Client security team approves deliverable for deployment
- Deployment: Code is deployed through client's change management process
Acceptance Criteria:
- Zero critical vulnerabilities in SAST/DAST/SCA
- All high vulnerabilities remediated or risk-accepted with security lead approval
- No hardcoded secrets detected
- All dependencies scanned and approved
- Security test report provided and reviewed
- Architecture diagram provided and reviewed
- Data handling verified (no production data used in testing)
- Compliance requirements verified
Stage 6: Deployment and Ongoing Monitoring
Post-Deployment Vendor Security:
- Vendor access to production is revoked or severely restricted
- Vendor support access requires ticket-based approval with time limits
- Vendor patches and updates are security tested before deployment
- Vendor component vulnerabilities are monitored via SCA
- Vendor security incidents are tracked and evaluated
- Vendor compliance attestations are reviewed annually
Stage 7: Offboarding
Vendor Offboarding Security Checklist:
| # | Checklist Item | Status |
|---|---|---|
| 1 | All vendor access to client systems revoked | ☐ |
| 2 | All vendor accounts disabled/deleted | ☐ |
| 3 | Vendor VPN access revoked | ☐ |
| 4 | All vendor code commits reviewed and merged | ☐ |
| 5 | Code escrow updated with final codebase | ☐ |
| 6 | Knowledge transfer completed | ☐ |
| 7 | Documentation transferred and reviewed | ☐ |
| 8 | Vendor data deletion verified | ☐ |
| 9 | Vendor backup destruction verified | ☐ |
| 10 | Subcontractor access revoked | ☐ |
| 11 | Final security audit conducted | ☐ |
| 12 | Security incident review completed | ☐ |
| 13 | IP transfer verification completed | ☐ |
| 14 | Final payment contingent on security clearance | ☐ |
| 15 | Lessons learned documented | ☐ |
| 16 | Vendor relationship closed in vendor management system | ☐ |
Special Scenarios
Offshore Development (India to US/EU/UK)
Additional Considerations:
- Data residency: EU data must stay in EU; consider data localization requirements
- GDPR/DPDP Act: Cross-border data transfer requirements (SCCs, adequacy decisions)
- Time zone coordination: Security incident response across time zones
- Cultural differences: Security awareness and practices may differ
- Regulatory compliance: Vendor must comply with both Indian and client-country regulations
- Export controls: Technology export restrictions (cryptography, defense-related)
- Tax and legal: Contract jurisdiction, dispute resolution, liability
Mitigation Strategies:
- Use dedicated offshore development centers with enhanced security
- Implement data minimization (only necessary data leaves the client country)
- Use synthetic/anonymized data for offshore development
- Implement strong encryption for all data transfers
- Establish 24/7 security operations with overlap hours
- Conduct regular on-site audits of offshore facilities
Subcontracting Management
Subcontracting Risks:
- Primary vendor may subcontract to unknown parties
- Security requirements may not flow down to subcontractors
- Client may not know who is actually writing the code
- Subcontractors may be in high-risk jurisdictions
Mitigation Strategies:
- Contractual prohibition on subcontracting without approval
- Mandatory subcontractor security assessment
- Subcontractor security clauses equivalent to primary contract
- Primary vendor liability for subcontractor breaches
- Right to audit subcontractors
- Subcontractor personnel screening requirements
Open Source Development with Vendor Customization
Risks:
- Vendor introduces vulnerable open source components
- Customizations may introduce new vulnerabilities
- Open source license compliance issues
- Community support vs. vendor support confusion
Mitigation:
- SCA for all open source components in deliverables
- License compliance review
- Vendor responsible for open source vulnerability patching
- Community vs. vendor support model documented
- Backporting policy for security patches
Cloud-Based Development (Vendor-Managed Platforms)
Risks:
- Vendor uses cloud platforms (GitHub, GitLab, AWS CodeCommit) with shared infrastructure
- Multi-tenant environments may have data leakage risks
- Vendor's cloud security posture affects client security
- API keys and credentials in cloud environments
Mitigation:
- Vendor cloud security assessment
- Dedicated cloud instances where possible
- Cloud access logging and monitoring
- Encryption of data at rest in cloud
- Vendor cloud security configuration review
Tools, Technologies, and Solutions
Vendor Risk Management Platforms
| Tool | Best For | licensing Range |
|---|---|---|
| RiskRecon | Vendor risk assessment, continuous monitoring | Enterprise licensing |
| MetricStream | GRC platform with vendor risk | Enterprise licensing |
| Archer | Enterprise GRC, vendor risk | Enterprise licensing |
| ServiceNow VRM | Vendor risk management module | Enterprise licensing |
| Shared Assessments SIG | Standardized vendor assessment questionnaire | Free / Premium |
| Excel/Spreadsheet | Small organizations | Free |
Code Security and Repository Tools
| Tool | Best For | licensing |
|---|---|---|
| SonarQube | SAST, code quality | Free (Community) / Enterprise |
| Checkmarx | Enterprise SAST | Enterprise licensing |
| Veracode | Enterprise SAST, DAST, SCA | Enterprise licensing |
| Git-secrets | Pre-commit secret detection | Free |
| TruffleHog | Secret scanning in repositories | Free |
| GitGuardian | Enterprise secret detection | Commercial |
Contract and Document Management
| Tool | Best For | licensing Range |
|---|---|---|
| Ironclad | Contract lifecycle management | Enterprise licensing |
| DocuSign CLM | Contract management, e-signatures | Enterprise licensing |
| Icertis | Enterprise contract management | Enterprise licensing |
| Conga | Contract management, Salesforce integration | Enterprise licensing |
| Microsoft Word + SharePoint | Simple document management | Included in Microsoft 365 |
Vendor Monitoring and Audit Tools
| Tool | Best For | licensing |
|---|---|---|
| Hyperproof | Compliance management, vendor assessments | Commercial |
| Tugboat Logic | Security assurance, vendor management | Commercial |
| StandardFusion | GRC platform, vendor management | Commercial |
| Google Forms / Typeform | Vendor questionnaires | Free / Pro |
| Excel | Small vendor portfolios | Free |
Indian Vendor Security Assessment Resources
| Resource | Description | URL |
|---|---|---|
| NASSCOM | Indian IT industry body, security guidelines | https://nasscom.in |
| Data Security Council of India (DSCI) | Data protection and security best practices | https://dsci.in |
| MeitY | Ministry of Electronics and IT, security guidelines | https://www.meity.gov.in |
| STQC | Standardization Testing and Quality Certification | https://stqc.gov.in |
| CERT-In | Indian Computer Emergency Response Team | https://www.cert-in.org.in |
Indian Vendor Security Service Providers
| Vendor | Offering | Website |
|---|---|---|
| Singahi | Vendor security assessment, outsourced development security, contract review | / |
| Protiviti | Vendor risk consulting, third-party risk management | https://www.protiviti.com |
Policy and Procedure Templates
Outsourced Development Security Policy (Template)
Template
Outsourced Development Security Policy
Document ID: POL-OUT-SEC-001 Version: 1.0 Effective Date: [DATE] Owner: CISO / Procurement Security Lead Approved By: [Name], [Title] Review Cycle: Annual
1. Purpose
This policy establishes the security requirements for all outsourced software development engagements at [Organization].
2. Scope
This policy applies to:
- Full application outsourcing to third-party vendors
- Partial outsourcing (modules, components, features)
- Offshore, nearshore, and onshore development
- Staff augmentation and contract developers
- Managed development services
- Subcontracting arrangements
- Open source customization by vendors
3. Policy Statements
3.1 Vendor Selection Security
- All vendors must undergo security due diligence before engagement.
- Vendor security assessment must be completed using the standard questionnaire.
- Vendors scoring below 50 (critical risk) require CISO approval for engagement.
- Vendors must provide security certifications (ISO 27001, SOC 2) or equivalent evidence.
3.2 Contract Security Requirements
- All outsourcing contracts must include security clauses per the standard template.
- Security requirements must be attached as an appendix to every SOW.
- Right-to-audit clauses must be included in all critical/high-risk vendor contracts.
- Data protection agreements must be signed for all engagements involving personal data.
- IP protection clauses must be included in all contracts.
- Subcontracting must be explicitly controlled and approved.
3.3 Vendor Onboarding Security
- All vendor personnel must sign NDAs before accessing client information.
- Vendor personnel must complete security awareness training before accessing client systems.
- Vendor access must be provisioned with least privilege and MFA.
- Vendor workstations must meet minimum security standards.
- Code escrow must be established for all critical application development.
3.4 Development Security
- Vendor must follow client's secure development life cycle or equivalent.
- Vendor must comply with client's secure coding standards.
- All vendor code must be scanned by SAST and SCA before delivery.
- Vendor must not use production data for testing or development.
- Vendor must report all security incidents within 24 hours.
- Vendor code commits must be reviewed by client security team for critical projects.
3.5 Delivery and Acceptance
- All deliverables must pass security acceptance testing before deployment.
- Vendor must provide security test reports with each major deliverable.
- Zero critical vulnerabilities are acceptable in delivered code.
- Client reserves the right to conduct independent penetration testing.
- Security sign-off is required before production deployment.
3.6 Monitoring and Review
- Vendor security must be reviewed at least annually (bi-annually for critical/high-risk).
- Vendor access must be reviewed monthly and revoked when no longer needed.
- Vendor security incidents must be tracked and evaluated.
- Vendor compliance attestations must be reviewed annually.
- Subcontractor security must be verified quarterly.
3.7 Offboarding
- Vendor access must be revoked within 24 hours of contract termination.
- Vendor data deletion must be verified and documented.
- Code escrow must be updated with final codebase.
- Knowledge transfer must be completed and verified.
- Final security audit must be conducted before closure.
4. Roles and Responsibilities
- CISO: Owns the policy, approves critical/high-risk vendor engagements, approves risk acceptance
- Procurement Security Lead: Manages vendor security assessments, contract clauses, onboarding
- Vendor Manager: Monitors vendor compliance, coordinates security reviews, manages relationships
- Security Lead: Reviews vendor code, conducts acceptance testing, approves security sign-off
- Legal/Contracts: Drafts and negotiates security contract clauses
- Development Lead: Reviews vendor technical deliverables, manages integration
- Compliance Officer: Ensures vendor regulatory compliance
5. Exceptions
Exceptions require written CISO approval with documented risk acceptance and compensating controls.
6. Enforcement
Non-compliance may result to contract termination, audit findings, or legal action.
7. Related Documents
- Information Security Policy (POL-INFO-001)
- Vendor Management Policy (POL-VEND-001)
- Secure Development Life Cycle Policy (POL-SDLC-001)
- Secure Coding Policy (POL-SEC-CODE-001)
- Data Protection Policy (POL-DATA-001)
- Security Testing Policy (POL-SEC-TEST-001)
8. Revision History
| Version | Date | Author | Changes |
|---|---|---|---|
| 1.0 | [DATE] | [Name] | Initial version |
Vendor Security Assessment Questionnaire (Template)
Template
Vendor Security Assessment Questionnaire
Vendor Name: ___________________
Assessment Date: ___________________
Assessed By: ___________________
Risk Tier: ☐ Critical ☐ High ☐ Medium ☐ Low
1. Organization and Governance
1.1 Does your organization have a dedicated security function? ☐ Yes ☐ No
1.2 Who is your Chief Information Security Officer (CISO) or equivalent?
1.3 Does your organization hold ISO 27001 certification? ☐ Yes ☐ No (Certificate #:)
1.4 Does your organization hold SOC 2 Type II certification? ☐ Yes ☐ No
1.5 Has your organization had a security breach in the past 3 years? ☐ Yes ☐ No
If yes, please describe: ___________________
2. Secure Development
2.1 Do you follow a Secure Development Life Cycle (SDLC)? ☐ Yes ☐ No
2.2 Do you use static application security testing (SAST)? ☐ Yes ☐ No (Tool:)
2.3 Do you use dynamic application security testing (DAST)? ☐ Yes ☐ No (Tool:)
2.4 Do you use software composition analysis (SCA)? ☐ Yes ☐ No (Tool:)
2.5 Do you conduct manual security code reviews? ☐ Yes ☐ No
2.6 Do you conduct penetration testing? ☐ Yes ☐ No (Frequency:)
2.7 Do you have secure coding standards? ☐ Yes ☐ No (Standard:)
2.8 Do you train developers on secure coding? ☐ Yes ☐ No (Frequency:)
3. Data Protection
3.1 How do you encrypt data in transit? ___________________
3.2 How do you encrypt data at rest? ___________________
3.3 Do you use production data for testing? ☐ Yes ☐ No
3.4 Do you have a data retention and deletion policy? ☐ Yes ☐ No
3.5 Do you have a data breach notification process? ☐ Yes ☐ No (Timeline:)
4. Access Control
4.1 Do you require multi-factor authentication for all systems? ☐ Yes ☐ No
4.2 Do you enforce least privilege access? ☐ Yes ☐ No
4.3 Do you review access permissions quarterly? ☐ Yes ☐ No
4.4 Do you monitor and log all access to client data? ☐ Yes ☐ No
4.5 Do you restrict remote access to client systems? ☐ Yes ☐ No
5. Personnel Security
5.1 Do you conduct background checks on employees? ☐ Yes ☐ No
5.2 Do employees sign confidentiality agreements? ☐ Yes ☐ No
5.3 Do you have a security awareness training program? ☐ Yes ☐ No
5.4 What is your average employee turnover rate? ___________________
6. Subcontracting
6.1 Do you subcontract any work? ☐ Yes ☐ No
6.2 If yes, how do you ensure subcontractor security? ___________________
6.3 Do subcontractors sign security agreements? ☐ Yes ☐ No
7. Business Continuity
7.1 Do you have a business continuity plan? ☐ Yes ☐ No
7.2 Do you have a disaster recovery plan? ☐ Yes ☐ No
7.3 What is your RTO/RPO for critical systems? ___________________
7.4 Do you have cyber insurance? ☐ Yes ☐ No (Coverage:)
8. Compliance
8.1 Can you comply with PCI DSS? ☐ Yes ☐ No
8.2 Can you comply with GDPR? ☐ Yes ☐ No
8.3 Can you comply with DPDP Act 2023? ☐ Yes ☐ No
8.4 Can you comply with RBI cybersecurity guidelines? ☐ Yes ☐ No
8.5 Can you provide compliance attestations? ☐ Yes ☐ No
9. IP Protection
9.1 Do you have an IP protection policy? ☐ Yes ☐ No
9.2 Can you support code escrow? ☐ Yes ☐ No
9.3 Do you have IP theft prevention controls? ☐ Yes ☐ No
10. References
10.1 Can you provide 3 security references from similar clients? ☐ Yes ☐ No
Scoring
| Category | Score (1-5) | Weight | Weighted Score |
|---|---|---|---|
| Organization & Governance | 15% | ||
| Secure Development | 25% | ||
| Data Protection | 20% | ||
| Access Control | 15% | ||
| Personnel Security | 10% | ||
| Subcontracting | 5% | ||
| Business Continuity | 5% | ||
| Compliance | 5% | ||
| Total Score |
Risk Tier
| Score | Tier |
|---|---|
| 90-100 | Low |
| 70-89 | Medium |
| 50-69 | High |
| <50 | Critical |
Assessment Decision
☐ Approved, Low risk, standard controls
☐ Approved with Conditions, Medium risk, enhanced controls required
☐ Conditionally Approved, High risk, extensive controls required, quarterly review
☐ Not Approved, Critical risk, engagement not recommended
Conditions (if applicable)
Approver
Name: ___________________
Title: ___________________
Signature: ___________________
Date: ___________________
Risk Assessment and Treatment
Risk Assessment for Outsourced Development
| Risk ID | Risk Description | Likelihood | Impact | Risk Level | Mitigation |
|---|---|---|---|---|---|
| R-001 | Vendor introduces backdoors or malicious code | Low | Critical | High | SAST, manual code review, penetration testing, code escrow, right-to-audit |
| R-002 | Vendor has inadequate security, leading to client data breach | Medium | Critical | Critical | Vendor assessment, contract clauses, monitoring, data minimization |
| R-003 | Vendor subcontractors to unsecured parties | Medium | High | High | Subcontracting controls, approval requirements, liability clauses |
| R-004 | Vendor steals client IP or source code | Low | High | High | IP clauses, code escrow, access logging, legal protections |
| R-005 | Vendor uses production data for testing/development | Medium | High | High | Data handling clauses, monitoring, synthetic data policy |
| R-006 | Vendor does not patch vulnerabilities in delivered code | Medium | High | High | SCA monitoring, patch SLA, maintenance contract |
| R-007 | Vendor access is not revoked after engagement ends | Medium | High | High | Offboarding checklist, access review, automated deprovisioning |
| R-008 | Vendor introduces vulnerable open source components | High | Medium | High | SCA, dependency review, vendor vulnerability management |
| R-009 | Vendor security incidents are not reported to client | Medium | High | High | Incident notification clause, monitoring, contractual penalties |
| R-010 | Vendor compliance failures expose client to regulatory penalties | Medium | High | High | Compliance clauses, vendor attestation, audit rights, liability |
| R-011 | Vendor development environment is compromised | Medium | High | High | Vendor environment security, code signing, build verification |
| R-012 | Vendor personnel lack security awareness | High | Medium | High | Training requirements, personnel screening, security champion program |
| R-013 | Vendor code quality issues lead to security vulnerabilities | Medium | High | High | Acceptance testing, code review, quality metrics, SAST enforcement |
| R-014 | Vendor does not follow secure development practices | Medium | High | High | SDLC requirements, contract clauses, audit rights, monitoring |
| R-015 | Geopolitical risks affect vendor operations (sanctions, data access) | Low | High | Medium | Contract jurisdiction, data localization, backup vendors, exit planning |
Risk Treatment Options
| Risk | Treatment | Residual Risk |
|---|---|---|
| R-001 | Multi-layer code validation + legal deterrent | Low |
| R-002 | Assessment + contract + monitoring + data minimization | Low |
| R-003 | Subcontractor controls + approval + liability | Low |
| R-004 | IP clauses + escrow + logging + legal | Low |
| R-005 | Data handling policy + synthetic data + monitoring | Low |
| R-006 | SCA + patch SLA + maintenance contract | Low |
| R-007 | Offboarding checklist + access review + automation | Low |
| R-008 | SCA + dependency review + vendor management | Low |
| R-009 | Notification clause + monitoring + penalties | Low |
| R-010 | Compliance clauses + attestation + audit + liability | Low |
| R-011 | Code signing + build verification + vendor audit | Low |
| R-012 | Training requirements + screening + mentoring | Low |
| R-013 | Acceptance testing + code review + quality metrics | Low |
| R-014 | SDLC requirements + contract + audit + monitoring | Low |
| R-015 | Contract jurisdiction + data localization + backup | Low |
Audit and Compliance Checklist
Pre-Audit Self-Assessment
| # | Question | Evidence | Status |
|---|---|---|---|
| 1 | Is there a documented Outsourced Development Security Policy? | Policy document | ☐ |
| 2 | Are vendor security assessments conducted before engagement? | Assessment records | ☐ |
| 3 | Do outsourcing contracts include security clauses? | Contract samples | ☐ |
| 4 | Are NDAs signed by all vendor personnel? | NDA records | ☐ |
| 5 | Is vendor access provisioned with least privilege and MFA? | Access provisioning records | ☐ |
| 6 | Do vendors comply with the secure development life cycle? | SDLC compliance records | ☐ |
| 7 | Is vendor code scanned by SAST/SCA before delivery? | Scan reports | ☐ |
| 8 | Is security acceptance testing performed on vendor deliverables? | Acceptance test records | ☐ |
| 9 | Are security sign-offs required before vendor code deployment? | Sign-off records | ☐ |
| 10 | Is vendor access reviewed and revoked when no longer needed? | Access review records | ☐ |
| 11 | Is vendor security reviewed at least annually? | Review records | ☐ |
| 12 | Are subcontractor security controls verified? | Subcontractor records | ☐ |
| 13 | Is code escrow maintained for critical applications? | Escrow records | ☐ |
| 14 | Do vendors report security incidents within contractual timelines? | Incident records | ☐ |
| 15 | Are vendor security incidents tracked and evaluated? | Incident tracking | ☐ |
| 16 | Is vendor data deletion verified at offboarding? | Deletion verification | ☐ |
| 17 | Are vendor compliance attestations reviewed annually? | Compliance records | ☐ |
| 18 | Is there a right-to-audit clause in critical vendor contracts? | Contract review | ☐ |
| 19 | Are vendor security findings remediated within SLA? | Remediation tracking | ☐ |
| 20 | Is vendor security integrated into procurement? | Procurement records | ☐ |
| 21 | Are vendor personnel screened before access? | Screening records | ☐ |
| 22 | Do vendors complete security awareness training? | Training records | ☐ |
| 23 | Is vendor code reviewed for backdoors or malicious code? | Code review records | ☐ |
| 24 | Are vendor development environments secure? | Environment assessment | ☐ |
| 25 | Is vendor IP protection verified? | IP protection records | ☐ |
| 26 | Are vendor security metrics tracked? | Metrics dashboard | ☐ |
| 27 | Is there a vendor offboarding security checklist? | Offboarding checklist | ☐ |
| 28 | Are vendor security requirements communicated clearly? | Communication records | ☐ |
| 29 | Are vendor security lessons learned documented? | Lessons learned | ☐ |
| 30 | Are vendor security controls audited? | Audit records | ☐ |
Auditor Interview Questions
Be prepared to answer:
- "How do you assess vendor security before engagement?"
- "What security clauses are in your outsourcing contracts?"
- "Can you show me a vendor security assessment?"
- "How do you ensure vendor code is secure before acceptance?"
- "What happens if a vendor introduces a security vulnerability?"
- "How do you handle vendor subcontracting?"
- "Are vendor security incidents reported to you?"
- "How do you protect your IP when outsourcing?"
- "What is your vendor offboarding process?"
- "How do you monitor vendor compliance with security requirements?"
Common Audit Findings and How to Avoid Them
| Finding | Cause | Prevention |
|---|---|---|
| "No vendor security assessment conducted" | Process gap | Mandatory assessment before engagement |
| "Contracts lack security clauses" | Legal gap | Standard contract template with security clauses |
| "Vendor code accepted without security testing" | Testing gap | Mandatory acceptance testing, sign-off |
| "Vendor access not revoked after engagement" | Offboarding gap | Offboarding checklist, access review |
| "No monitoring of vendor security" | Monitoring gap | Annual review, continuous monitoring |
| "Vendor uses production data for testing" | Data handling gap | Data handling policy, synthetic data, monitoring |
| "Subcontractor security not verified" | Subcontracting gap | Subcontractor approval, security verification |
| "No code escrow for critical applications" | IP protection gap | Code escrow requirement in contracts |
| "Vendor incidents not reported" | Communication gap | Incident notification clause, monitoring |
| "Vendor compliance not verified" | Compliance gap | Annual attestation, audit rights, compliance checklist |
Metrics and KPIs
Figure · Measures
The measures that show A.8.30 is working
- Vendor Assessment Coverage100%Quarterly
- Contract Security Clause Coverage100%Quarterly
- Vendor Onboarding Compliance100%Monthly
- Security Acceptance Rate> 95%Monthly
- Vendor Access Review Rate100%Quarterly
Process Metrics
| Metric | Formula | Target | Frequency |
|---|---|---|---|
| Vendor Assessment Coverage | (# of vendors assessed / # of active vendors) × 100 | 100% | Quarterly |
| Contract Security Clause Coverage | (# of contracts with security clauses / # of contracts) × 100 | 100% | Quarterly |
| Vendor Onboarding Compliance | (# of vendors with completed onboarding / # of new vendors) × 100 | 100% | Monthly |
| Security Acceptance Rate | (# of deliverables passing acceptance / # of deliverables tested) × 100 | > 95% | Monthly |
| Vendor Access Review Rate | (# of vendors with quarterly access review / # of vendors) × 100 | 100% | Quarterly |
| Vendor Security Review Rate | (# of vendors with annual security review / # of vendors) × 100 | 100% | Annually |
| Subcontractor Approval Rate | (# of approved subcontractors / # of subcontractors) × 100 | 100% | Quarterly |
| Vendor Incident Reporting Rate | (# of vendor incidents reported / # of vendor incidents) × 100 | 100% | Per incident |
| Offboarding Compliance | (# of vendors with completed offboarding / # of terminated vendors) × 100 | 100% | Monthly |
| Vendor Training Compliance | (# of vendor personnel trained / # of vendor personnel) × 100 | 100% | Quarterly |
Outcome Metrics
| Metric | Formula | Target | Frequency |
|---|---|---|---|
| Vendor-Introduced Vulnerabilities | Vulnerabilities introduced by vendor code per quarter | < 2 | Quarterly |
| Vendor Security Incident Rate | Security incidents caused by vendors per year | < 1 | Annually |
| Vendor Data Breach Rate | Data breaches involving vendor access per year | 0 | Annually |
| IP Theft Incidents | IP theft or misuse incidents per year | 0 | Annually |
| Vendor Compliance Score | Average vendor compliance score | > 80/100 | Annually |
| Vendor Remediation SLA | (# of vendor vulns fixed within SLA / # of vendor vulns) × 100 | > 90% | Monthly |
| Vendor Audit Findings | Findings from vendor audits per year | < 5 | Annually |
| Time to Vendor Security Assessment | Average days to complete vendor assessment | < 5 days | Per vendor |
| Vendor Security Satisfaction | Client satisfaction with vendor security | > 4.0/5.0 | Annually |
| impact of Vendor Security Incidents | Financial impact of vendor security incidents per year | Decreasing | Annually |
Dashboard Sample
┌─────────────────────────────────────────────────────────────────────┐
│                  OUTSOURCED DEVELOPMENT SECURITY DASHBOARD          │
│                    [Organization] — [Month Year]                    │
├─────────────────────────────────────────────────────────────────────┤
│  VENDOR ASSESSMENT: 100%     ██████████████████████  Target: 100%  │
│  CONTRACT CLAUSES: 100%      ██████████████████████  Target: 100%  │
│  ACCEPTANCE PASS: 97%        ████████████████████░░  Target: 95%  │
│  ACCESS REVIEW: 100%       ██████████████████████  Target: 100%  │
│  VENDOR INCIDENTS: 0       ░░░░░░░░░░░░░░░░░░░░░░  Target: <1/y  │
│  VENDOR VULNS: 1/q         █░░░░░░░░░░░░░░░░░░░░░  Target: <2/q  │
│  COMPLIANCE SCORE: 86/100  ████████████████████░░  Target: >80   │
│  AUDIT FINDINGS: 2         ██░░░░░░░░░░░░░░░░░░░░  Target: <5/y  │
│  REMEDIATION SLA: 95%        ████████████████████░░  Target: 90%  │
│  OFFBOARDING: 100%         ██████████████████████  Target: 100%  │
└─────────────────────────────────────────────────────────────────────┘
Common Pitfalls and How to Avoid Them
Pitfall 1: "We Trust Our Vendor"
Symptom: Organization skips vendor assessment because "we've worked with them for years."
Reality: Long-term relationships can create complacency. Vendor security posture changes over time (turnover, new management, budget cuts, acquisitions).
Solution:
- Annual re-assessment of all vendors
- Continuous monitoring for security incidents and rating changes
- Don't let relationship duration override security due diligence
- Include security in contract renewals
Pitfall 2: "Security Clauses Are Boilerplate"
Symptom: Generic security clauses copied from internet templates without customization.
Reality: Boilerplate clauses may not address your specific risks, technology stack, or regulatory requirements. They may not be enforceable in your jurisdiction.
Solution:
- Customize security clauses for each engagement based on risk tier
- Have legal review security clauses for enforceability
- Include specific technical requirements (encryption standards, MFA, etc.)
- Reference specific compliance requirements (PCI DSS, DPDP Act, etc.)
Pitfall 3: "We Can't Find Secure Vendors"
Symptom: Organization accepts vendors with poor security because "all vendors are the same."
Reality: Vendor security varies significantly. Some vendors invest heavily in security; others treat it as a overhead center. The difference is visible in certifications, tools, and processes.
Solution:
- Use vendor security ratings (BitSight, SecurityScorecard) as a screening tool
- Require minimum security standards (ISO 27001, SOC 2, or equivalent)
- Use vendor risk tiers to differentiate treatment
- Invest in vendor security improvement programs rather than accepting poor security
Pitfall 4: "Offboarding Is Just Access Revocation"
Symptom: Vendor offboarding only revokes access without complete data deletion, IP transfer, and knowledge transfer.
Reality: Incomplete offboarding creates lingering risks: data remnants, orphaned accounts, IP gaps, and operational continuity issues.
Solution:
- Use complete offboarding checklist
- Verify data deletion with evidence
- Update code escrow with final codebase
- Conduct knowledge transfer and document it
- Perform final security audit
- Close vendor relationship in vendor management system
Pitfall 5: "We Don't Need to Monitor Long-Term Vendors"
Symptom: Continuous monitoring is limited to the first year of engagement.
Reality: Vendor security posture degrades over time without oversight. Incidents, compliance changes, and personnel changes affect security continuously.
Solution:
- Annual security review for all vendors
- Continuous monitoring for critical/high-risk vendors
- Quarterly access review for all vendors with system access
- Incident monitoring (vendor breach notifications, security rating changes)
- Re-assessment when vendor has significant changes (acquisition, leadership change)
Pitfall 6: "Subcontracting Is the Vendor's Problem"
Symptom: Organization ignores subcontracting because "the vendor is responsible."
Reality: While the vendor is contractually responsible, the client bears the operational and reputational risk of subcontractor breaches. SolarWinds showed how supply chain attacks propagate.
Solution:
- Contractual control over subcontracting (approval required)
- Subcontractor security assessment
- Subcontractor liability clauses
- Right to audit subcontractors
- Monitoring of subcontractor activity
Pitfall 7: "overhead Overrides Security"
Symptom: Cheaper vendors are selected despite poor security posture.
Reality: The impact of a vendor breach (data breach, IP theft, regulatory fines, reputational damage) far exceeds the overhead difference between a secure vendor and a cheap vendor.
Solution:
- Include security as a weighted factor in vendor selection (not just overhead)
- Calculate overall value including security risk
- Use risk-adjusted licensing in vendor comparison
- Executive sponsorship for security-aware vendor selection
Pitfall 8: "Vendor Security Is Procurement's Job"
Symptom: Security team is not involved in vendor selection or management.
Reality: Procurement teams optimize for overhead and delivery; security teams optimize for risk. Both must be involved.
Solution:
- Security team involvement in vendor selection (assessment, contract review)
- Security team involvement in acceptance testing
- Security team involvement in ongoing monitoring
- Cross-functional vendor management committee (procurement, security, legal, development)
Illustrative Scenarios
Illustrative scenario, a composite example for guidance, not a specific Singahi engagement or a verified outcome.
Illustrative Scenario 1: Indian E-commerce Platform, Vendor Security Transformation
Organization: A rapidly growing e-commerce platform in India with 30 million users. Context: 50 in-house developers, 200+ contract developers across 5 vendors. Platform built on microservices architecture with 150+ services. PCI DSS compliance required. Challenge: No vendor security program. Vendors had unrestricted access to code repositories. No security clauses in contracts. First vendor audit revealed that one vendor had been using production data for testing for 18 months. Another vendor had subcontracted 40% of work to an unapproved subcontractor. Approach:
- Week 1-2: Singahi conducted vendor security assessment for all 5 vendors. Found: 2 vendors at high risk, 2 at medium risk, 1 at low risk.
- Week 3-4: Negotiated security contract addendums with all vendors. Added: right-to-audit, data handling clauses, subcontracting controls, incident notification, security testing requirements.
- Week 5-6: Implemented vendor onboarding security checklist. All 200+ vendor personnel re-onboarded with NDAs, MFA, least privilege access, and security training.
- Week 7-8: Deployed SAST/SCA scanning for all vendor code commits. Implemented mandatory security code review for vendor changes to critical services.
- Week 9-12: Established quarterly vendor security reviews. Implemented continuous monitoring for vendor access. Conducted first annual vendor security audit (on-site for 2 high-risk vendors). Results:
- Vendor security assessment coverage: 100% (all 5 vendors + 3 new vendors since program start)
- Vendor-introduced vulnerabilities: 2 per quarter (down from 15)
- Vendor data handling incidents: 0 (after synthetic data policy implementation)
- Subcontractor approval: 100% of subcontractors now approved and assessed
- PCI DSS compliance: achieved on first audit after vendor program implementation
- Vendor security satisfaction: 4.2/5.0 (vendors appreciate clear security expectations)
- impact of vendor security program: /year (assessments, monitoring, audits)
- impact of potential data breach (30 million users): + (based on DPDP Act penalties and customer impact) Key Lesson: Vendor security is not "set and forget." Continuous monitoring, clear contracts, and quarterly reviews are essential for sustained security.
Illustrative Scenario 2: Indian Bank, Outsourced Core Banking System Security
Organization: A national bank with 1,000+ branches, implementing a new core banking system through a vendor. Context: Vendor: a large Indian IT services company. Project: 3-year engagement, contract. 300+ vendor developers. RBI compliance mandatory. Data: 5 million+ customer records, financial transactions, KYC data. Challenge: Vendor had ISO 27001 but no specific banking security experience. Contract lacked detailed security clauses. No code escrow. No right-to-audit. Vendor was using offshore team (Eastern Europe) that the bank was not aware of. RBI inspection flagged "inadequate vendor security governance." Approach:
- Phase 1 (Month 1): Singahi conducted complete vendor security assessment. Found subcontracting to Eastern Europe (unapproved), insufficient data handling controls, and no code escrow.
- Phase 2 (Months 2-3): Renegotiated contract with detailed security clauses. Added: right-to-audit (2x/year), code escrow, data localization (all Indian customer data stays in India), subcontracting approval, incident notification (4 hours), security testing requirements, and RBI compliance clauses.
- Phase 3 (Months 4-6): Established vendor security governance committee (bank CISO, vendor CISO, project manager). Monthly security review meetings. Implemented code review process: all vendor code to critical modules reviewed by bank security team.
- Phase 4 (Months 7-9): Conducted first on-site vendor audit (development center in India). Verified physical security, access controls, and personnel screening. Conducted code escrow verification.
- Phase 5 (Months 10-12): Security acceptance testing for first major deliverable. Independent penetration testing by Singahi. Found 12 vulnerabilities (all medium/low). All remediated before go-live. Security sign-off obtained.
- Phase 6 (Ongoing): Quarterly vendor security reviews. Annual on-site audit. Continuous monitoring of vendor access. Subcontractor approval process for all new subcontractors. Results:
- RBI inspection: zero findings on vendor security governance
- Vendor security audit findings: 8 (first audit) → 2 (second audit) → 0 (third audit)
- Vendor-introduced vulnerabilities in production: 0 (first 18 months)
- Data localization: 100% compliance, all customer data in India
- Subcontractor visibility: 100% (all subcontractors known and assessed)
- Code escrow: verified and tested annually
- Vendor security governance: adopted as bank-wide standard for all vendor engagements
- impact of vendor security program: /year
- impact of RBI penalty + potential breach avoided: + Key Lesson: Large vendor engagements require enterprise-grade security governance. Monthly security reviews, on-site audits, and code escrow are non-negotiable for critical systems.
Multi-Framework Mapping
NIST SP 800-53 Rev 5 Mapping
| NIST Control | Description | A.8.30 Mapping |
|---|---|---|
| SA-9 | External information system services | Vendor security for outsourced services |
| SA-12 | Supply chain protection | Supply chain security for outsourced development |
| SR-2 | Supply chain risk management | Vendor risk assessment and management |
| SR-3 | Trustworthiness | Vendor trustworthiness assessment |
| SR-4 | Provenance | Code provenance and integrity |
| SR-5 | Acquisition strategies | Security in vendor acquisition |
| SR-6 | Supplier assessments | Vendor security assessments |
| SR-7 | Supply chain operations security | Ongoing vendor monitoring |
| SA-4 | Acquisition process | Security in acquisition process |
| SA-21 | Developer security testing | Vendor security testing requirements |
COBIT 2019 Mapping
| COBIT Practice | Description | A.8.30 Mapping |
|---|---|---|
| APO10.01 | Managed vendor relationships | Vendor relationship management |
| APO10.02 | Managed contracts | Contract security management |
| APO10.03 | Managed vendor risk | Vendor risk assessment and management |
| APO10.04 | Managed vendor performance | Vendor security performance monitoring |
| BAI03.01 | Managed solutions identification | Vendor selection security |
| BAI03.03 | Managed solutions development | Vendor development security |
| BAI09.01 | Managed services | Service provider security |
| BAI09.02 | Managed service agreements | Service agreement security |
| BAI09.03 | Managed service performance | Service security monitoring |
| MEA01.01 | Managed performance and conformance monitoring | Vendor security monitoring |
PCI DSS 4.0 Mapping
| PCI DSS Requirement | Outsourced Development Focus |
|---|---|
| Req 12.8 | Third-party service provider management |
| Req 12.8.3 | Vendor due diligence |
| Req 12.8.4 | Vendor acceptance and monitoring |
| Req 12.8.5 | Vendor security responsibility documentation |
| Req 6.3 | Security in software development (applies to vendor code) |
| Req 11.3 | Penetration testing (applies to vendor-developed systems) |
DPDP Act 2023 Mapping
| DPDP Act Section | Outsourced Development Implication |
|---|---|
| Section 8 | Data Fiduciaries must ensure processors (vendors) comply with data protection |
| Section 8(5) | Reasonable security safeguards, vendors must implement appropriate safeguards |
| Section 8(4) | Appropriate technical and organisational measures, vendors must implement data protection in design |
| Section 8(6) | Personal data breach intimation, vendors must notify fiduciaries of breaches |
| Section 28 | Data Principals' rights, vendors must support data subject requests |
OWASP SAMM Mapping
| SAMM Practice | Maturity Level | A.8.30 Mapping |
|---|---|---|
| Governance - Strategy & Metrics | Level 1-3 | Vendor security strategy |
| Governance - Policy & Compliance | Level 1-3 | Vendor compliance requirements |
| Implementation - Secure Build | Level 1-3 | Vendor secure build requirements |
| Implementation - Defect Management | Level 1-3 | Vendor vulnerability management |
| Verification - Security Testing | Level 1-3 | Vendor security testing |
CIS Controls v8 Mapping
| CIS Control | Implementation Group | A.8.30 Mapping |
|---|---|---|
| Control 15 | IG3 | Service provider management |
| Control 16 | IG2 | Application software security (vendor code) |
| Control 7 | IG2 | Continuous vulnerability management (vendor components) |
| Control 1 | IG1 | Inventory and control of enterprise assets (vendor access) |
| Control 6 | IG1 | Access control management (vendor access) |
Regulatory and Industry Context
India
| Regulation | Outsourced Development Relevance | Key Mandates |
|---|---|---|
| DPDP Act 2023 | Critical | Section 8: Data Fiduciaries responsible for vendor compliance; Section 8(5): Vendor security safeguards |
| IT Act 2000 | High | Section 43A: Reasonable security practices include vendor management |
| RBI Guidelines | Critical for banks | Cybersecurity framework requires vendor risk management for outsourcing |
| SEBI Regulations | Critical for markets | Cyber resilience requires vendor security for market infrastructure |
| IRDAI Guidelines | Critical for insurance | Information security requires vendor management for IT outsourcing |
| Cert-In | High | Security best practices include vendor security assessment |
| MeitY | High | Guidelines for IT outsourcing security, data localization |
International
| Regulation | Relevance | Key Mandates |
|---|---|---|
| GDPR | Critical for EU data | Art 28: Processor requirements, data processing agreements, vendor liability |
| PCI DSS 4.0 | Critical for card data | Req 12.8: Third-party service provider management, vendor security responsibility |
| HIPAA | Critical for health | Business Associate Agreements (BAAs) for vendor access to PHI |
| SOX | High for public companies | Vendor management for IT general controls, financial systems |
| NIST CSF 2.0 | High | GV.SC: Supply chain risk management |
| CCPA/CPRA | High | Vendor contracts must include data security requirements |
| LGPD | High | Processor requirements, data processing agreements |
| PDPA | High | Data protection obligations for vendors |
Roles and Responsibilities (RACI)
RACI Matrix for Outsourced Development Security
| Activity | CISO | Procurement Security Lead | Vendor Manager | Security Lead | Legal | Development Lead | Compliance Officer |
|---|---|---|---|---|---|---|---|
| Define vendor security policy | A | R | C | C | I | I | C |
| Create vendor assessment questionnaire | I | R/A | C | C | I | I | C |
| Conduct vendor security assessment | I | R/A | C | C | I | I | C |
| Negotiate security contract clauses | C | C | C | C | R/A | I | C |
| Approve vendor engagement (security) | A | R | C | C | I | C | C |
| Onboard vendor security | I | R | R/A | C | I | C | I |
| Monitor vendor development security | I | C | R/A | C | I | C | I |
| Review vendor code security | I | I | C | R/A | I | C | I |
| Security acceptance testing | I | I | C | R/A | I | C | I |
| Security sign-off | A | C | C | R | I | C | I |
| Monitor vendor compliance | I | C | R/A | C | I | I | C |
| Conduct vendor audit | A | R | C | C | I | I | C |
| Manage vendor offboarding | I | C | R/A | C | I | C | I |
| Track vendor metrics | R/A | C | C | C | I | I | C |
| Handle vendor incidents | A | C | R | C | C | I | C |
| Manage subcontractor security | I | C | R/A | C | I | I | C |
| Vendor training | I | R | C | C | I | I | I |
| Code escrow management | I | C | R | I | C | I | I |
| Vendor compliance attestation | I | C | R | I | I | I | A |
Legend: R = Responsible, A = Accountable, C = Consulted, I = Informed
Role Descriptions
| Role | Key Responsibilities | Required Skills |
|---|---|---|
| CISO | Policy ownership, risk acceptance for critical vendors, incident oversight, board reporting | Security leadership, risk management, vendor governance |
| Procurement Security Lead | Vendor assessments, contract security clauses, onboarding, offboarding, vendor portfolio management | Procurement, contract negotiation, security assessment, vendor management |
| Vendor Manager | Day-to-day vendor relationship, security compliance monitoring, incident coordination, performance tracking | Relationship management, project management, security awareness, communication |
| Security Lead | Code review, acceptance testing, security sign-off, vulnerability assessment, audit support | Application security, penetration testing, code review, risk assessment |
| Legal/Contracts | Contract drafting, security clause negotiation, IP protection, liability, dispute resolution | Contract law, IP law, data protection law, negotiation |
| Development Lead | Technical oversight, integration, code quality, acceptance criteria, knowledge transfer | Software development, architecture, integration, vendor management |
| Compliance Officer | Regulatory compliance verification, vendor compliance attestation, audit support, DPDP Act compliance | Regulatory knowledge, compliance frameworks, audit, data protection |
Documentation and Evidence Requirements
Mandatory Documentation
| Document | Purpose | Retention | Owner |
|---|---|---|---|
| Outsourced Development Security Policy | Governance framework | 7 years | CISO |
| Vendor Security Assessment Questionnaire | Standard assessment template | Current version | Procurement Security Lead |
| Vendor Assessment Report | Per-vendor assessment results | 7 years | Procurement Security Lead |
| Vendor Security Contract Clauses | Standard contract templates | Current version | Legal |
| Master Service Agreement (MSA) | Overarching vendor contract | 7 years | Legal |
| Statement of Work (SOW) | Per-engagement scope and security requirements | 7 years | Vendor Manager |
| Non-Disclosure Agreement (NDA) | Confidentiality protection | 7 years | Legal |
| Data Processing Agreement (DPA) | Data protection terms | 7 years | Legal |
| Code Escrow Agreement | IP protection arrangement | 7 years | Legal |
| Vendor Onboarding Checklist | Security onboarding evidence | 7 years | Vendor Manager |
| Vendor Access Provisioning Records | Access control evidence | 7 years | Vendor Manager |
| Vendor Security Test Reports | Deliverable security testing | 7 years | Security Lead |
| Security Acceptance Test Report | Acceptance testing evidence | 7 years | Security Lead |
| Security Sign-off Document | Deployment approval | 7 years | Security Lead |
| Vendor Security Review Records | Ongoing monitoring evidence | 7 years | Vendor Manager |
| Vendor Audit Records | Audit findings and remediation | 7 years | Procurement Security Lead |
| Vendor Incident Records | Security incident documentation | 7 years | Vendor Manager |
| Vendor Offboarding Checklist | Offboarding evidence | 7 years | Vendor Manager |
| Vendor Compliance Attestations | Compliance evidence | 7 years | Compliance Officer |
| Vendor Metrics Reports | KPI tracking | 7 years | Procurement Security Lead |
| Subcontractor Assessment Records | Subcontractor security evidence | 7 years | Vendor Manager |
| Vendor Training Records | Vendor personnel training evidence | 7 years | Vendor Manager |
| Lessons Learned | Post-engagement review | 7 years | Vendor Manager |
| Audit Records | Internal and external audit findings | 7 years | CISO |
Evidence for Audit
| Audit Question | Evidence Required |
|---|---|
| "Show me the outsourced development security policy" | Approved policy document |
| "How do you assess vendor security?" | Assessment questionnaire, assessment reports |
| "What security clauses are in contracts?" | Contract samples, clause templates |
| "Can you show me a vendor security assessment?" | Completed assessment report |
| "How do you ensure vendor code is secure?" | Acceptance test reports, sign-off records |
| "How do you handle vendor incidents?" | Incident records, notification records |
| "How do you manage vendor offboarding?" | Offboarding checklist, completion records |
| "Are vendor security reviews conducted?" | Review records, meeting minutes |
| "How do you handle subcontracting?" | Subcontractor approval records, assessments |
| "Are vendor compliance attestations reviewed?" | Attestation records, review documentation |
Continuous Improvement
Improvement Cycle
Plan → Implement → Measure → Review → Improve
Plan: Set targets for vendor assessment coverage, contract clause coverage, acceptance pass rate, incident rate.
Implement: Assess vendors, negotiate contracts, onboard securely, monitor, test deliverables, audit, offboard.
Measure: Track KPIs, conduct surveys, analyze audit results, monitor incidents.
Review: Quarterly vendor review, annual complete review, post-incident review, post-engagement review.
Improve: Update assessment questionnaire, refine contract templates, enhance monitoring, adopt new tools, improve training.
Improvement Triggers
| Trigger | Action |
|---|---|
| New vendor engagement | Apply latest assessment questionnaire, contract templates, onboarding checklist |
| Vendor security incident | Root cause analysis, update controls, assess other vendors for similar gaps |
| New regulation | Update contract clauses, compliance checklist, assessment criteria |
| Audit finding | Update process, template, or control to address finding |
| Vendor acquisition or merger | Re-assess vendor security, review contract terms, evaluate new risks |
| New threat intelligence | Update monitoring, add new assessment criteria, enhance controls |
| Vendor feedback | Refine contract terms, improve onboarding, clarify requirements |
| Industry benchmark | Compare metrics, set improvement targets |
| Tool evolution | Evaluate new vendor risk management tools, migrate if beneficial |
| Contract renewal | Re-assess vendor, update security clauses, renegotiate terms |
Maturity Advancement Path
| From Level | To Level | Key Actions | Typical Timeline |
|---|---|---|---|
| 1 (Ad-hoc) | 2 (Managed) | Create policy + assessment template; assess 3-5 critical vendors; add basic contract clauses | 1–2 months |
| 2 (Managed) | 3 (Defined) | Standardize across all vendors; implement acceptance testing; establish monitoring; train vendor managers | 3–4 months |
| 3 (Defined) | 4 (Quantified) | Metrics tracked; risk-based tiers; automated monitoring; quarterly reviews; code escrow for critical | 3–4 months |
| 4 (Quantified) | 5 (Optimizing) | Continuous improvement; real-time monitoring; predictive risk analytics; automated compliance; vendor security ecosystem | 6–12 months |
FAQ
Q1: Do we need to assess all vendors, or just critical ones?
A: All vendors should be assessed, but the depth varies by risk tier. Critical vendors get complete on-site assessments; low-risk vendors get lightweight questionnaire-based assessments. The key is that no vendor is "unassessed."
Q2: What if a vendor refuses to sign security clauses?
A: This is a red flag. If a vendor refuses basic security requirements (NDA, data handling, incident notification), consider alternative vendors. For critical vendors, you may need to accept enhanced monitoring and compensating controls, but this should be risk-accepted by the CISO.
Q3: How do we handle vendor code escrow?
A: Code escrow protects your IP if the vendor goes out of business or breaches contract. Use a third-party escrow agent (Iron Mountain, NCC Group, EscrowTech). Deposit source code, build instructions, and documentation. Verify escrow annually by performing a test build.
Q4: What is the difference between vendor assessment and vendor audit?
A: Vendor assessment is a questionnaire-based evaluation conducted before engagement. Vendor audit is an on-site or deep-dive examination of vendor controls, typically conducted annually or when concerns arise. Assessment is broader (all vendors); audit is deeper (critical vendors).
Q5: How do we monitor vendor security continuously?
A: Use security rating services (BitSight, SecurityScorecard) for continuous monitoring. Review vendor access logs monthly. Monitor vendor security news and breach notifications. Conduct quarterly security check-ins. Annual complete re-assessment.
Q6: What if our vendor is a large company with good security but poor execution on our project?
A: Large company security ≠ project security. The vendor may have good enterprise security but assign junior developers to your project with minimal oversight. Conduct project-specific security assessments, review code from your project specifically, and monitor project-level security practices.
Q7: How do we handle vendor security incidents?
A: Activate the incident notification clause immediately. Require vendor to provide detailed incident report within 24 hours. Conduct joint investigation. Assess client impact. Require vendor to remediate root cause. Review contract penalties. Consider vendor termination for severe incidents.
Q8: Can we use the same security clauses for all vendors?
A: No. Security clauses should be risk-tiered. Critical vendors get extensive clauses (right-to-audit, code escrow, incident notification). Low-risk vendors get basic clauses (NDA, data handling). Customizing clauses increases enforceability and vendor acceptance.
Q9: How do we ensure vendor compliance with DPDP Act 2023?
A: Include DPDP Act compliance in contract clauses. Require vendor to process data only in India (or approved jurisdictions). Require data processing agreement. Require vendor to support data principal rights (access, correction, deletion, grievance). Require vendor to notify you of breaches within 24 hours.
Q10: What about open source components in vendor deliverables?
A: Require SCA scanning in vendor CI/CD. Require vendor to provide SBoM with each deliverable. Include open source vulnerability patching in maintenance SLA. Require vendor to comply with open source licenses. Monitor for new CVEs affecting vendor dependencies.
Q11: How do we manage vendor access to our cloud environments?
A: Use cloud IAM with least privilege. Enable MFA for all vendor access. Use temporary credentials (AWS STS, Azure PIM). Monitor vendor access with cloud trail logs. Restrict vendor access to non-production environments. Require just-in-time access approval for production.
Q12: What is the role of procurement in vendor security?
A: Procurement should include security as a weighted evaluation criterion (not just overhead). Procurement should use standard contract templates with security clauses. Procurement should not engage vendors without security assessment. Procurement should coordinate with security team on vendor selection.
Q13: How do we handle vendor security in Agile/Scrum engagements?
A: Include security acceptance criteria in sprint definitions of done. Require vendor security test reports per sprint for critical features. Conduct sprint security reviews. Include security retrospectives. Use automated SAST/SCA in shared CI/CD pipeline.
Q14: What if a vendor's country has sanctions or data access laws?
A: This is a geopolitical risk. Include contract jurisdiction clauses. Consider data localization (keep data in your country). Use encryption that you control (not vendor-controlled). Have backup vendors for critical functions. Monitor geopolitical developments. Consult legal counsel on sanctions compliance.
Q15: How do we measure vendor security effectiveness?
A: Track vendor-introduced vulnerabilities, vendor security incidents, vendor compliance scores, time to remediate vendor vulnerabilities, and impact of vendor security incidents. See Section 13 for a full KPI framework.
References and Further Reading
Standards and Guidelines
- ISO/IEC 27001:2022, Information Security, Cybersecurity and Privacy Protection, Information Security Management Systems, Requirements. ISO, 2022.
- ISO/IEC 27002:2022, Information Security, Cybersecurity and Privacy Protection, Information Security Controls. ISO, 2022.
- ISO/IEC 27036, Information technology, Security techniques, Information security for supplier relationships. ISO, 2014.
- NIST SP 800-53 Rev 5, Security and Privacy Controls for Information Systems and Organizations. NIST, 2020.
- NIST SP 800-161 Rev 1, Cybersecurity Supply Chain Risk Management Practices. NIST, 2022.
- NIST CSF 2.0, Cybersecurity Framework. NIST, 2024.
- PCI DSS v4.0, Payment Card Industry Data Security Standard. PCI SSC, 2022.
- CIS Controls v8, Center for Internet Security, 2021.
- OWASP Software Assurance Maturity Model (SAMM) v2.0. OWASP, 2020.
- BSIMM12, Building Security In Maturity Model. Synopsys, 2023.
Supply Chain Security Resources
- "Supply Chain Security: A Complete Guide", Various authors, NIST, 2022.
- "The Software Supply Chain Security Handbook", Various, Linux Foundation, 2023.
- SolarWinds Post-Incident Report, CISA, 2021.
- CISA Supply Chain Risk Management, https://www.cisa.gov/supply-chain-risk-management
- ENISA Supply Chain Security, https://www.enisa.europa.eu/topics/cybersecurity-policy/supply-chain-security
Contract and Legal Resources
- Shared Assessments Standardized Information Gathering (SIG), https://sharedassessments.org/
- ISO/IEC 27036-2, Supplier relationships, Requirements. ISO, 2014.
- Cloud Security Alliance (CSA) STAR, https://cloudsecurityalliance.org/star/
- SOC 2 Trust Services Criteria, AICPA, 2022.
- ISAE 3402 / SSAE 18, Assurance reporting on service organizations.
Indian Regulatory Resources
- Digital Personal Data Protection Act 2023, Government of India, 2023.
- RBI Master Direction on Cyber Security Framework, Reserve Bank of India, 2024.
- SEBI Cybersecurity and Cyber Resilience Framework, Securities and Exchange Board of India, 2023.
- IRDAI Guidelines on Information and Cybersecurity, Insurance Regulatory and Development Authority of India, 2023.
- IT Act 2000 (as amended), Ministry of Electronics and Information Technology, India.
- MeitY IT Outsourcing Guidelines, Ministry of Electronics and Information Technology, India.
- DSCI Data Security Framework, Data Security Council of India, https://dsci.in
- NASSCOM Security Guidelines, National Association of Software and Service Companies, https://nasscom.in
Industry Research
- IBM impact of a Data Breach Report 2024, IBM Security and Ponemon Institute, 2024.
- Verizon Data Breach Investigations Report 2024, Verizon, 2024.
- Gartner Market Guide for Vendor Risk Management Solutions, Gartner, 2024.
- Forrester Wave: Third-Party Risk Management Platforms, Forrester Research, 2023.
- SolarWinds Supply Chain Attack Analysis, CISA, FireEye, 2021.
- Singahi AI/ML Security Master Course, /