
On this page
- Quick Reference (60 Seconds)
- What the Standard Actually Requires
- Why This Control Matters
- Scope and Applicability
- Key Definitions and Terminology
- Relationship to Other Clauses and Frameworks
- Detailed Implementation Guidance, The Improvement-Opportunity-to-Maturity-Advancement Loop
- Tools, Technologies, and Solutions
- Policy and Procedure Templates
- Improvement-Risk and Treatment
- Audit and Compliance Checklist
- Metrics and KPIs
- Common Pitfalls and Audit Failures
- Illustrative Scenario 1: Failure, Maruti Consumer Brands and the Improvement-as-Corrective-Action Confusion (Illustrative)
- Illustrative Scenario 2: Success, Agni FinTech Builds the Maturity-Advancement Loop (Illustrative)
- Multi-Framework Mapping
- Implementation Roadmap
- FAQ
- Industry-Specific Requirements
- Maturity Model
- Emerging Trends
- References and Further Reading
Quick Reference (60 Seconds)
| Attribute | Detail |
|---|---|
| Clause | ISO/IEC 27701:2025 Clause 10.1, Continual Improvement. The first sub-clause of the PIMS Improvement block (Clause 10), structurally aligned to the Harmonized Structure shared by ISO/IEC 27001:2022 Clause 10.1, ISO 22301:2019 Clause 10.2, ISO 9001:2015 Clause 10.3 and ISO/IEC 42001:2023 Clause 10.1. Clause 10.2 reacts to nonconformities; Clause 10.1 proactively raises the bar on a PIMS that already conforms but could work better. Together they close the Plan-Do-Check-Act "Act" loop on the PIMS, and once Clause 10.1 is discharged, the management-system obligations under the standard are complete (Clause 10 is the last operational clause in the MSS). Without 10.1, the PIMS plateaus at its certification-baseline maturity and decays against the moving regulatory and technological context. |
| What it asks for (paraphrase) | ISO/IEC 27701:2025 Clause 10.1 asks organizations to continually improve the PIMS. Four load-bearing ideas sit inside that paraphrase, and the certification auditor tests each separately. The organisation continually improves, improvement is a planned, cadenced, programme-level activity, not an occasional ad-hoc effort. The organisation improves the PIMS, the scope, the policy, the objectives, the risk methodology, the processes, the controls, the documented information, the culture, the technology stack, not just the symptoms. The improvement is proactive, driven by opportunities surfaced from trend analysis, audit observations, management-review direction, corrective-action lessons, regulatory change, technology change, customer feedback and principal expectations, not solely by detected nonconformities. The improvement is sustained, every improvement cycle produces a higher maturity floor, a richer evidence base, a more capable privacy function, and feeds the next cycle. |
| The marquee insight competitors miss | Most practitioner commentary treats Clause 10.1 as a one-line "and the organisation shall continually improve" footnote at the end of Clause 10. That under-uses the clause for a PIMS in four ways. First, in a PIMS the improvement opportunity surface is the privacy programme, the seven operational processes (consent, ROPA, rights, DPIA, processor management, transfer, breach), the Annex A.1 / A.2 / A.3 control set, the SDF section 10 obligations, the privacy-by-design depth, the culture, the technology stack. A PIMS improvement opportunity is not "fix the policy"; it is "raise the consent-quality KPI from 92 to 97 percent", "compress the rights-response median from fourteen days to seven", "extend the DPIA pipeline coverage to all new processing activities", "automate the sub-processor change-notification workflow", "adopt privacy-enhancing technologies for the analytics environment", "mature the algorithmic-software review from periodic to continuous". Second, the line between 10.2 (reactive corrective) and 10.1 (proactive improvement) is the most-confused PIMS demarcation after 9.1 / 9.2 / 9.3: a corrective action under 10.2 closes a detected nonconformity (something went wrong); an improvement under 10.1 raises the bar on a conforming PIMS (something could be better). Third, the DPDP-first improvement drivers are the load-bearing Indian signature: the DPDP Rules 2025 phased commencement creates a stream of improvement-trigger events; the SDF section 10 maturation curve (DPO accountability, SDF DPIA cadence, independent-data-audit findings, algorithmic-software review) is itself a multi-year improvement programme; the DPBI's early enforcement orders feed a regulator-driven improvement loop that has no analogue in the GDPR ecosystem. Fourth, the maturity-advancement loop is the load-bearing 10.1 design, every cycle raises the maturity floor (L1 to L5); the L5 target is a moving frontier, not a fixed state. |
| Domain | Improvement (Clause 10). 10.1 sits beside 10.2 (Nonconformity and Corrective Action) as the proactive complement to 10.2's reactive stance. The Clause 10 block is the last operational block in the management-system standard, once 10.2 and 10.1 are discharged, the PDCA cycle for the period is complete and the next cycle (Clause 6 re-planning → Clause 7 support → Clause 8 operation → Clause 9 evaluation → Clause 10 improvement) begins. 10.1 is where the PIMS learns from itself, raises its own bar, and proves to the certification auditor and to the regulator that the management system is not a static compliance artefact but a living, advancing programme. |
| What you must produce | (a) a PIMS Continual Improvement Policy (toolkit doc 01), the top-management commitment to the cadenced, programme-level improvement discipline; (b) a Continual Improvement Procedure (toolkit doc 02), the eight-step operational discipline (identify, capture, triage, prioritise, plan, implement, verify, sustain); (c) an Improvement Opportunities Register (toolkit doc 03, the load-bearing artefact), the single source of truth for every identified opportunity; (d) a Prioritisation Matrix (toolkit doc 04), the five-dimension scoring rubric (privacy-principal benefit, regulatory benefit, commercial benefit, feasibility, strategic-fit); (e) an Improvement Action Tracker (toolkit doc 05); (f) a Maturity Advancement Roadmap (toolkit doc 06), the L1-to-L5 multi-year progression across twelve privacy dimensions; (g) a Lessons-Learned Log (toolkit doc 07), the cumulative intelligence from every Clause 9 source, every Clause 10.2 corrective-action cycle, every operational event, every improvement cycle. |
| Typical owner | Top management owns the continual-improvement discipline at the strategic level, Clause 10.1 derives its authority from Clause 5.1 leadership commitment. The DPO / Privacy Lead owns the discipline operationally (the Register, the Matrix, the Tracker, the Log, the Roadmap). Business-process owners own the improvement on their process area (Head of Marketing for consent-quality; Head of Customer Service for rights-response-latency; Head of Procurement for processor-chain automation; Head of Engineering for privacy-by-design). The CISO co-owns the security-overlay improvements; the Head of Internal Audit provides the audit-observation stream; the Head of Legal provides the regulatory-change stream. The Improvement Steering Group (the DPO, the CISO, the Head of Legal, the Head of Internal Audit, the top business-process owners, the chair or delegate) meets on a cadence (typically quarterly) to prioritise the portfolio and resource the top-rank improvements. Top management receives the maturity-advancement report at the Clause 9.3 management review. |
| Minimum viable actions | (1) Stand up a single Improvement Opportunities Register (toolkit doc 03) covering all ten source families (9.1 monitoring, 9.2 internal audit, 9.3 outputs, 10.2 lessons, Clause 8 events, customer feedback, regulator engagements, technology-change scanning, workforce surveys, PII-principal expectation scanning); (2) build the Prioritisation Matrix (toolkit doc 04); (3) run the first Prioritisation workshop; commission the top three to five improvements; (4) stand up the Action Tracker (toolkit doc 05); (5) run the eight-step discipline on each commissioned improvement; (6) build the Lessons-Learned Log (toolkit doc 07); (7) draft the Maturity Advancement Roadmap (toolkit doc 06) across the twelve privacy dimensions; (8) wire the recurring-improvement-overdue pattern into the Clause 9.3 input and the structural-treatment pipeline; (9) for SDFs, document the DPDP-driven improvement drivers. |
| Maturity floor (L1) | A "we re-certified, what is there to improve?" discipline: the PIMS passed Stage 2; the Statement of Applicability was signed; the policy was published; the team moved on to operational firefighting; no Register exists; no Matrix exists; no Tracker exists; the maturity is the certification-baseline maturity and is decaying against the moving context. The single most common Clause 10.1 audit nonconformity in the Indian growing-company segment, and a frequently cited PIMS surveillance-audit finding in tier-1 cert-body practitioner commentary. |
| Maturity target (L4 to L5) | A "privacy-programme advancement" PIMS: the Register is a first-class artefact; the Matrix drives the rank-ordered portfolio; the eight-step discipline is operational end-to-end; the Roadmap is the multi-year north star; the Log is the cumulative intelligence; the recurring-improvement pattern triggers structural treatment; the DPDP-driven improvement drivers are wired into the programme; the privacy-enhancing-technology adoption is on the roadmap; the algorithmic-fairness maturity is advancing; the SDF section 10 obligations are maturing on a multi-year curve; the certification auditor can pick any of the last four improvement cycles and walk the opportunity-to-implementation-to-maturity-advancement chain end-to-end. |
| Audit red flag | A Register with zero entries across two consecutive cycles (the no-improvement-culture failure); a portfolio with every entry marked "in progress" and zero closed in the last cycle (the no-implementation failure); an improvement closed at "implemented" with no effectiveness check (the open-loop failure, the 10.2 pathologies migrate to 10.1); a portfolio whose entries are all corrective actions mis-labelled as improvements (the demarcation failure); an improvement programme with no Log (the no-cumulative-intelligence failure); an improvement programme with no Roadmap (the no-north-star failure); an improvement programme that does not reflect the DPDP Rules 2025 phased-commencement stream (the regulatory-blindness failure). The 10.1 audit test is always the same: the auditor opens the Register and asks "show me the top three improvements commissioned in the last cycle, the implementation evidence, the effectiveness verification, and the maturity advancement that resulted." |
| Time to implement (first cycle) | Growing companies (50 to 250 staff): 6 to 12 weeks for the first defensible cycle (the Register, the Matrix, the Tracker, the eight-step discipline on the first three commissioned improvements, the Log). Mid-sized (250 to 2,000): 12 to 20 weeks, usually requiring the integration with the enterprise GRC platform, the multi-process-owner RACI, the SDF-designation-driven sub-portfolio and the multi-year Maturity Advancement Roadmap. Multi-entity enterprise or Significant Data Fiduciary under DPDP section 10: 6 to 9 months, integrated with the enterprise improvement function, the SDF section 10 maturation cycle and the multi-jurisdiction regulatory-change pipeline. |
| Related clauses | 4.1 (context refresh drives the regulatory and technological scanning that feeds the opportunity set), 4.2 (interested-party expectations refresh drives the customer-feedback and principal-expectation input), 4.3 (scope change is a Clause 6.3 planned change that 10.1 may recommend), 4.4 (the PIMS itself is what 10.1 improves), 5.1 (top management owns the improvement programme, 10.1 is the operational test of 5.1), 5.2 (policy refresh is a frequent 10.1 output), 5.3 (roles may be revised as the maturity advances), 6.1 (privacy risk register and opportunity thinking, 10.1 implements the "opportunities" half of 6.1), 6.2 (objective reset is a canonical 10.1 output), 6.3 (planned changes, the demarcation: 6.3 is the planned PIMS change pipeline; 10.1 commissions 6.3 changes), 7.1 to 7.5 (resource, competence, awareness, communication, documented information updates per improvement), 8.1 to 8.3 (the seven privacy processes are the primary improvement surface; the risk methodology and treatment are improved by 10.1), 9.1 (trend patterns are the load-bearing 10.1 source), 9.2 (audit observations, second source), 9.3 (management-review improvement-output route, third source), 10.2 (corrective-action lessons, fourth source; 10.2 reactive plus 10.1 proactive equals the full improvement engine), Annex A.1 / A.2 / A.3 (the controls whose maturity 10.1 advances). Every Clause 9 finding and every Clause 10.2 lesson that is not turned into a 10.1 improvement is a learning that did not compound. |
| Critical Indian context-bearing instruments the programme must reflect | DPDP Act 2023 (Act 22/2023, enacted 11 August 2023), section 8 (general obligations; 8(5) safeguards and 8(6) the breach clock (intimation without delay; seventy-two-hour report) in DPDP Rules 2025 Rule 7 are continuous improvement subjects); section 9 (children, verifiable-parental-consent mechanism and no-behavioural-monitoring control mature through 10.1); section 10 (SDF, the DPO-based-in-India accountability; SDF DPIA cadence; independent-data-audit findings; algorithmic-software review, the entire SDF overlay is a multi-year improvement programme); sections 11 to 14 (rights, latency and Grievance Officer SLA under section 13 are continuous KPIs); section 16 (cross-border negative list); section 18 (DPBI, the regulator's enforcement-feedback loop drives the regulator-driven improvement stream); section 33 plus Schedule (penalty maxima, up to two hundred and fifty crore rupees for section 8(5) failure; up to two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10). DPDP Rules 2025 (notified 13 November 2025, phased commencement through approximately 2027), the phased commencement is itself a stream of improvement-trigger events. Puttaswamy v. Union of India (2017) 10 SCC 1; Aadhaar judgment (2019) 1 SCC 1. CERT-In Directions 20(3)/2022-CERT-In (28 April 2022), the six-hour clock. Companies Act 2013, section 134(3)(n) (board-report discloses the risk-management framework; maturity advancement is board-reportable) and section 177 (Audit Committee's risk-management oversight remit). SEBI LODR Regulation 21 (Risk Management Committee for listed entities). RBI Storage of Payment System Data (6 April 2018); RBI Digital Lending Guidelines (2 September 2022); SEBI CSCRF (20 August 2024); IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023). Every commissioned improvement should name the instrument and the section it derives from. |
If you only read one thing: Clause 10.1 is where the PIMS proactively raises its own bar. A 10.1-conformant PIMS is one in which the organisation, on a documented cadence, scans its Clause 9 sources (the 9.1 trend patterns, the 9.2 audit observations, the 9.3 management-review outputs, the 10.2 corrective-action lessons), scans its forward-looking drivers (regulatory change, technology change, customer feedback, principal expectations, workforce feedback), captures the improvement opportunities in a Register, prioritises them on a multi-dimensional rubric, commissions the top-rank improvements on the Action Tracker, implements them with the eight-step discipline, verifies the effectiveness, sustains the gains, and advances the maturity floor. Not a "we re-certified, what is there to improve?" discipline; an improvement programme that proves itself in the Register, the Tracker, the effectiveness-verification record and the maturity advancement. The certification auditor will walk an improvement from the source through the implementation to the maturity advancement; the DPBI will, after a complaint or a breach, ask whether the underlying control had been on a maturity-advancement trajectory. Get 10.1 wrong, no Register, no Matrix, no Tracker, no Roadmap, no Log, and however strong the Clause 8 operations, the Clause 9 evaluations and the Clause 10.2 corrective actions are, the PIMS cannot demonstrate that it is advancing, which under DPDP section 8(5) reasonable security safeguards and GDPR Article 24(1) "ongoing basis" controller responsibility is itself a nonconformity.
What the Standard Actually Requires
The paraphrased requirement
ISO/IEC 27701:2025 Clause 10.1 asks organizations to continually improve the PIMS. Four load-bearing ideas sit inside that paraphrase, and the certification auditor tests each separately.
The organisation must improve continually. "Continually" is the operative word; it distinguishes Clause 10.1 from Clause 10.2 (which reacts to detected nonconformities) and from Clause 6.3 (which plans specific changes). Continually means the improvement discipline is cadenced, programme-level and resourced, not occasional, not ad-hoc, not a one-off after a major audit finding. The Singahi calibration for the cadence is quarterly for the Improvement Steering Group (the portfolio review); semi-annual for the Maturity Advancement Roadmap refresh; annual for the Lessons-Learned Log consolidation; continuous for the opportunity-scan. The cadence is fixed in the Continual Improvement Procedure (toolkit doc 02) and is itself an improvement subject (an organisation that runs the Steering Group twice a year and finds the portfolio stale is itself a 10.1 finding).
The organisation must improve the PIMS. The scope of "the PIMS" is the scope fixed under Clause 4.3, controller, processor, or both; all in-scope processing activities; all applicable Annex A.1 / A.2 / A.3 controls; all in-scope business units and geographies. The improvement surface is therefore the entire management system: the context (Clause 4.1), the leadership (5.1), the policy (5.2), the roles (5.3), the risk methodology (6.1.2), the objectives (6.2), the change-planning (6.3), the resources (7.1), the competence (7.2), the awareness (7.3), the communications (7.4), the documented information (7.5), the seven operational processes (8.1), the privacy risk assessment (8.2), the privacy risk treatment and the SoA (8.3), the Annex A controls, the SDF section 10 obligations.
The improvement must be proactive. Proactivity is the load-bearing distinction between Clause 10.2 and Clause 10.1. The 10.2 trigger is a detected nonconformity, something went wrong, the loop reacts. The 10.1 trigger is an opportunity, something could be better, the loop advances. The 10.1 sources are the trend patterns from 9.1 (a KPI that is plateauing, a control whose effectiveness is decaying, a process whose cycle time is lengthening), the audit observations from 9.2 (an opportunity-for-improvement finding; a structural observation that suggests a treatment change), the management-review direction from 9.3 (the improvement-output routing), the corrective-action lessons from 10.2 (a recurring-nonconformity pattern that suggests a structural improvement rather than another corrective action), the regulatory-change stream (the DPDP Rules 2025 phased commencement; the EDPB guidelines; the cross-border regime evolution), the technology-change stream (the privacy-enhancing-technology maturation; the generative-AI risk surface), the customer-feedback stream (the enterprise-customer privacy-audit findings), the principal-expectation stream (the Grievance Officer complaints trend), the workforce-feedback stream (the privacy-awareness survey).
The improvement must be sustained. Sustaining the gain is the load-bearing test that 10.1-conformant organisations pass and 10.2-only organisations fail. A one-off improvement that decays back to the baseline within two cycles is not a 10.1-conformant improvement; it is a transient change. The sustainment test is the effectiveness-verification at 30, 60 and 90 days post-implementation, the maturity-floor indicator (does the L-level advance), the lessons-learned capture, the documentation update, the training refresh, the operational-handover to the business-process owner. The sustainment is the discipline that turns the improvement into the new baseline.
The privacy improvement-portfolio, twelve dimensions
Most practitioner commentary discusses Clause 10.1 in generic ISO-management-system terms, "the organisation shall continually improve the suitability, adequacy and effectiveness of the management system". That framing leaves the most important question unanswered for a PIMS: what counts as a privacy improvement? The Singahi privacy improvement-portfolio (toolkit doc 03 Section 4) operationalises the answer. The portfolio has twelve dimensions; the first seven mirror the seven privacy-process families under Clause 8.1, the next three are the PIMS-specific additions, and the last two are the cross-cutting dimensions.
Dimension 1, Consent and notice quality. The improvement subjects: the consent-record completeness rate (the share of consent records that capture all seven DPDP section 6 qualities, free, specific, informed, unconditional, unambiguous, clear affirmative action, easily withdrawable); the notice-currency rate; the withdrawal-mechanism latency; the Consent Manager integration integrity; the consent-revocation propagation latency through the processor chain. The improvement trajectory: from a paper-based consent archive (L1) through a structured-form consent with a database (L2), a tiered-consent flow with the seven qualities auto-validated (L3), a Consent Manager-integrated revocable consent (L4), a continuous-consent-quality monitoring with the principal-side dashboard (L5).
Dimension 2, ROPA and record-keeping. The improvement subjects: the ROPA-to-reality reconciliation rate; the new-processing-activity intake to ROPA-entry latency; the customer-of-processor ROPA exchange completeness; the periodic reconciliation cadence. The improvement trajectory: from a static ROPA spreadsheet (L1) through a ROPA database with periodic reconciliation (L2), a ROPA wired into the change-intake (L3), an automated ROPA-from-source-system discovery (L4), a continuous ROPA with the principal-side transparency layer (L5).
Dimension 3, Data-principal rights fulfilment. The improvement subjects: the rights-response median latency; the rights-response completeness rate; the nomination-handling turnaround; the access-response to the recipients-of-disclosure field completeness; the erasure through the processor chain propagation latency; the Grievance Officer SLA adherence under DPDP section 13. The improvement trajectory: from a manual ticketing system with periodic SLA misses (L1) through a rights-request platform with SLA monitoring (L2), an automated triage and workflow (L3), a self-service principal portal with status tracking (L4), an AI-assisted rights operation with proactive triage and continuous SLA optimisation (L5).
Dimension 4, DPIA pipeline. The improvement subjects: the DPIA-coverage rate (the share of trigger-meeting processing activities with a DPIA completed); the DPIA-to-launch lead time; the DPIA quality score; the prior-consultation register maintenance; the SDF DPIA cadence (for SDFs); the review-on-change discipline. The improvement trajectory: from a reactive DPIA on regulator prompting (L1) through a trigger-test checklist at the change-intake (L2), a DPIA pipeline with the Article 35(7) / ISO 29134 structure (L3), an automated DPIA-trigger detection from the change-management system (L4), a continuous risk-monitoring with the DPIA-as-a-living-document discipline (L5).
Dimension 5, Processor and sub-processor chain. The improvement subjects: the processor-due-diligence coverage rate; the DPA-terms coverage rate; the sub-processor change-notification adherence; the infringing-instruction drill cadence; the audit-cooperation cycle adherence; the deletion-certification intake rate. The improvement trajectory: from a contract-based processor management (L1) through a processor register with periodic due-diligence (L2), a tiered processor-risk-classification with risk-based due-diligence depth (L3), an automated sub-processor change-notification workflow with the customer notification pre-approved (L4), a continuous processor-risk-monitoring with the sub-processor real-time inventory and the customer-facing transparency portal (L5).
Dimension 6, Cross-border transfer. The improvement subjects: the transfer-basis coverage rate; the transfer-impact-assessment freshness; the supplementary-measures effectiveness; the transfer register completeness. The improvement trajectory: from a contract-based transfer management (L1) through a transfer register with periodic TIA (L2), a tiered transfer-risk-classification with risk-based TIA depth (L3), an automated transfer-trigger detection from the data-flow map (L4), a continuous transfer-monitoring with the regulator-regime-change alerting and the principal-side transfer-transparency layer (L5).
Dimension 7, Breach detection, notification, response. The improvement subjects: the breach-detection-to-awareness latency; the awareness-to-Board-notification latency (the DPDP section 8(6) breach clock (intimation without delay; seventy-two-hour report); the CERT-In six-hour clock; the sector-regulator clocks, RBI six hours, SEBI six hours, IRDAI twenty-four to seventy-two hours); the principal-notification dispatch latency; the table-top drill cadence; the lessons-learned integration. The improvement trajectory: from a manual incident response with chronic clock misses (L1) through a runbook-based response with periodic drills (L2), a platform-based incident-response with the dual-clock / triple-clock automation (L3), a SOAR-integrated response with the regulator-portal API submission (L4), a continuous-threat-detection with the automated breach-impact-assessment and the principal-notification dispatch (L5).
Dimension 8, Privacy by design and by default. The improvement subjects: the privacy-by-design review coverage (the share of new processing activities, systems and features with a PbD review at the design stage); the default-settings privacy-protectiveness; the data-minimisation rate; the pseudonymisation and anonymisation adoption; the privacy-enhancing-technology adoption. The improvement trajectory: from a privacy-by-design afterthought (L1) through a PbD checklist at the design stage (L2), a PbD review with the seven PbD principles embedded (L3), a PbD automation with the privacy-engineering toolchain (L4), a PbD-as-code with the privacy tests in the CI/CD pipeline and the differential-privacy / secure-multi-party-computation adoption for the analytics environment (L5).
Dimension 9, Children-data controls. The improvement subjects: the verifiable-parental-consent rate; the age-assurance coverage; the no-behavioural-monitoring-or-targeted-advertising enforcement; the children-data retention discipline. The improvement trajectory: from a self-declared-age mechanism (L1) through an age-assurance platform integration (L2), a verifiable-parental-consent workflow with the Consent Manager (L3), a continuous-age-assurance with the no-targeted-advertising automation (L4), a child-rights-by-design with the age-appropriate-design code embedded and the ongoing impact-assessment (L5).
Dimension 10, SDF section 10 obligations. The improvement subjects: the DPO function maturity; the SDF DPIA cadence adherence; the independent-data-audit closeout rate; the algorithmic-software review coverage and depth; the board-reporting pack quality. The improvement trajectory: from a vacant-or-figurative DPO (L1) through an India-based DPO with the section 10 obligations documented (L2), a DPO function with the SDF DPIA / audit / algorithmic-software review cadence operating (L3), a board-grade DPO function with the board-reporting pack on the SEBI LODR cycle (L4), a privacy-centre-of-excellence with the DPO as the board-level privacy strategist and the algorithmic-fairness a continuous-discipline (L5).
Dimension 11, Privacy culture and awareness. The improvement subjects: the privacy-awareness training coverage; the role-specific training depth; the privacy-champions network; the workforce-feedback-survey score; the privacy-by-design uptake in the engineering culture; the privacy-incident reporting rate (the upward trend is a leading indicator of a healthy reporting culture, not of a deteriorating operation). The improvement trajectory: from an annual compliance training (L1) through a role-based curriculum (L2), a privacy-champions network with the business-process owners (L3), a continuous-learning programme with the privacy-engineering depth and the design-partnership with HR (L4), a privacy-as-a-core-value with the culture metrics in the board-reporting pack and the privacy-by-default mindset across the workforce (L5).
Dimension 12, Privacy technology and automation. The improvement subjects: the GRC-with-privacy platform adoption; the ROPA automation; the consent-management integration; the DSAR-platform adoption; the breach-response SOAR; the privacy-enhancing-technology adoption; the AI-driven processing governance. The improvement trajectory: from a spreadsheet-based operation (L1) through a GRC platform with privacy modules (L2), a privacy-platform-integrated operation with the consent / ROPA / DSAR / breach modules (L3), a privacy-automation with the AI-assisted triage and the privacy-enhancing-technology adoption (L4), a privacy-as-code with the policy-as-code, the privacy-tests-in-CI/CD and the continuous-compliance-monitoring (L5).
The twelve dimensions are not mutually exclusive. A single improvement opportunity often engages several, a Consent Manager integration engages dimensions 1, 3 and 5; a privacy-enhancing-technology adoption for the analytics environment engages dimensions 2, 4 and 8. The 10.1 discipline is that each dimension has its own maturity trajectory, so that when an improvement engages several, each advances along its own curve.
The line between 10.2, 10.1, 6.3 and Clause 8.x operational change
The most-confused PIMS demarcation sits in the Improvement block. Four change-handling constructs touch each other and practitioners routinely mis-route them. The certification auditor's 10.1 test probes the demarcation explicitly.
Clause 10.2, Nonconformity and Corrective Action. The trigger is a detected nonconformity (a Clause 9.1 KPI threshold breach; a Clause 9.2 audit finding; a Clause 9.3 management-review output; an operational event; a regulator direction; a customer-audit finding). The work is root-cause analysis, containment, correction, corrective action to eliminate the root cause, and verification that the nonconformity does not recur. The orientation is reactive and backward-looking (what went wrong; how to fix the cause so it does not happen again). The artefacts are the nonconformity register and the corrective-action plan.
Clause 10.1, Continual Improvement. The trigger is an opportunity (a trend pattern; an audit observation; a management-review direction; a regulatory change; a technology change; a customer expectation; a principal expectation; a workforce signal). The work is the eight-step discipline (identify, capture, triage, prioritise, plan, implement, verify, sustain). The orientation is proactive and forward-looking (what could be better; how to raise the maturity floor). The artefacts are the Improvement Opportunities Register, the Prioritisation Matrix, the Action Tracker, the Roadmap, the Log.
Clause 6.3, Planning of Changes. The trigger is a planned change to the PIMS (a scope change; a policy refresh; an organisational restructure; a technology migration; a regulatory-change response). The work is the planned-change discipline (the purpose; the consequences; the integrity of the PIMS during the change; the resource availability; the allocation of responsibilities). The orientation is the structured management of a specific change. The artefacts are the change request, the change impact assessment, the change plan. Clause 6.3 governs how changes happen; 10.1 governs what changes the organisation commissions as improvements.
Clause 8.x, Operational change. The trigger is a routine operational event (a new processing activity; a new processor engagement; a new product feature; a customer-data-subject request). The work is the operational-process discipline (the ROPA intake; the DPIA trigger test; the DPA execution; the rights-response workflow). The orientation is the day-to-day operation of the PIMS. The artefacts are the operational records.
The four constructs overlap but do not duplicate. A new processing activity is an 8.x operational change; if its DPIA reveals a higher-than-acceptable residual risk, the treatment plan may commission an 8.3 risk-treatment change; if the treatment design is novel and represents an advance on the existing SoA, the design choice is captured as a 10.1 improvement opportunity; if the DPIA itself was missed and surfaced as an audit finding, the fix is a 10.2 corrective action. The Singahi routing rules:
- Detected nonconformity → Clause 10.2 corrective action.
- Opportunity to raise the bar → Clause 10.1 improvement.
- Planned PIMS change → Clause 6.3 (often commissioned by a 10.1 improvement or by a regulator change).
- Operational event → Clause 8.x (the day-to-day PIMS operation).
The recurring-nonconformity pattern is the demarcation test. When the same nonconformity recurs two or three times, the root cause is structural; the corrective action under 10.2 is no longer the right instrument, the structural improvement under 10.1 is. The Internal Audit function (under 9.2) flags the recurrence; the management review (under 9.3) routes the recurrence to 10.1; the 10.1 programme commissions the structural improvement. This 10.2-to-10.1 escalation is the most operationally consequential demarcation in the Improvement block, and the certification auditor's deepest 10.1 question.
The companion guidance, Annex B is normative in 2025
In 27701:2019 the implementation guidance lived in informative Annex F. In 27701:2025 the guidance lives in Annex B (Implementation Guidance for PII Controllers and Processors), and Annex B is normative. For Clause 10.1 specifically, the Annex B guidance explains how the continual-improvement discipline should be designed, how the opportunities should be sourced, how the prioritisation rubric should be calibrated, how the maturity-advancement loop should be evidenced and how the lessons-learned capture should be wired into the PDCA cycle. Auditors test against Annex B, not just against the clause text.
Five external anchors are most relevant for Clause 10.1.
- ISO/IEC 27001:2022 Clause 10.1 (Continual improvement) is structurally identical on the infosec side; the integrated-with-distinction posture uses the shared structure.
- ISO/IEC 27002:2022 is the source of the operational security controls whose effectiveness the continual-improvement programme advances; only control 5.34 (Privacy and protection of PII) is PII-specific.
- GDPR Article 24(1) "ongoing basis" controller responsibility makes continuous improvement a statutory obligation for EU-relevant processing. Article 5(2) accountability principle reinforces the demonstrability duty. Article 32(1)(d) "regular testing, assessing and evaluating the effectiveness" is the explicit effectiveness-evaluation anchor that 10.1 discharges. The EDPB Guidelines on DPIA review-on-change (post-Schrems II, post the modernised SCCs) describe the transfer-regime improvement dimension.
- NIST Privacy Framework v1.0 (NIST.CSWP.01162020, 16 January 2020), the Govern-P function's "risk-management strategy" subcategory is the closest cross-framework analogue of the 10.1 maturity-advancement discipline.
- SOC 2 Privacy TSC (AICPA 2017 Trust Services Criteria with 2022 Points of Focus update), CC4.1 / CC4.2 (Monitoring) and CC5.2 / CC5.3 (Change management) plus P8.0 (Monitoring for Compliance) close the SOC 2 improvement loop.
What auditors actually check
The certification auditor's Clause 10.1 examination has seven predictable moves.
First, the auditor opens the Register. Is there one? Is it populated? Are entries from each of the ten source families (9.1, 9.2, 9.3, 10.2, Clause 8, customer, regulator, technology, workforce, principal)? Are entries dated and attributed? If the artefact does not exist, or exists with zero entries across two cycles, major nonconformity.
Second, the auditor opens the Prioritisation Matrix. Is the rubric documented? Are the weights defended? Are the recent scoring decisions traceable to the rank-ordering? Is the rubric applied to every commissioned improvement? If the Matrix exists but was applied once and forgotten, the discipline is perfunctory.
Third, the auditor opens the Action Tracker. How many improvements are commissioned? How many are implementing? How many are closed in the last cycle? What is the closeout-with-effectiveness-verification rate? Are the owners named and the due dates set? An empty Tracker, or one in which every entry is permanently "in progress", is a major nonconformity.
Fourth, the auditor walks an improvement end-to-end. From the source (the 9.1 KPI trend; the 9.2 audit observation; the 9.3 management-review decision; the 10.2 corrective-action lesson) → to the Register entry (the description, the benefit case, the cost estimate, the dimension impact) → to the Matrix scoring → to the Steering Group commissioning decision → to the Tracker entry (the plan, the owner, the due date) → to the implementation evidence → to the effectiveness verification → to the sustainment (the documentation update, the training refresh, the operational handover) → to the maturity-floor advancement (the L-level move on the Roadmap). If any link is missing, the loop is not closing; the finding cascades.
Fifth, the auditor opens the Maturity Advancement Roadmap. Is the twelve-dimension framework in use? Is the L1-to-L5 trajectory populated per dimension? Are the milestones, dependencies and cost bands documented? Is the trajectory reconciled with the actual advancement over the last two cycles?
Sixth, the auditor opens the Lessons-Learned Log. Is the structured capture in use? Are the lessons generalised across dimensions? Are the recurring patterns escalated to the structural-improvement pipeline? An empty Log, or one that records lessons without actioning them, is a major nonconformity.
Seventh, the auditor tests the demarcation. Are the 10.2 corrective actions correctly distinguished from the 10.1 improvements in the Register? Are the recurring-nonconformity patterns escalated to 10.1? Are the planned changes under 6.3 distinguished from the improvements under 10.1? Are the operational events under 8.x distinguished from both?
Why This Control Matters
The improvement programme as the PDCA "Act" closing the loop
Without Clause 10.1, the PIMS is a system that generates data, assurance and decisions but never compounds the learning. The Clause 9.1 Dashboard shows the consent-quality KPI plateauing at 92 percent for three quarters; the Clause 9.2 audit raises an observation that the DPIA pipeline does not catch the new-AI-feature changes; the Clause 9.3 management review directs an improvement to the change-intake wiring; the Clause 10.2 corrective action closes a specific nonconformity on a missed DSAR. Without Clause 10.1, none of these signals becomes a structural improvement. The Dashboard plateaus forever; the audit observation recurs next cycle; the management-review direction lands in the operational backlog; the corrective action fixes one DSAR but the rights-response median does not move.
The 10.1 programme is the compounding engine. Each cycle takes the signals, turns them into prioritised opportunities, implements them with discipline, verifies the effectiveness, sustains the gain, and advances the maturity floor. The result is a PIMS that demonstrably moves from L2 to L3 to L4 across the twelve dimensions over four to six cycles. The certification auditor's deepest question is not "is the PIMS conforming today?" but "is the PIMS demonstrably advancing across cycles?", and 10.1 is the only clause that produces the evidence to answer yes.
This is why 10.1 is the most consequential Clause 10 sub-clause from a programme-maturity standpoint. The 10.2 corrective action and the 9.1 / 9.2 / 9.3 evaluation disciplines are necessary but not sufficient; without the 10.1 improvement programme, the learnings do not compound. The PIMS passes recertification each cycle but never matures; in the moving Indian regulatory and technological context, a stationary PIMS is a decaying PIMS.
The Indian regulatory weight behind 10.1
In India, Clause 10.1 has a regulatory weight that goes beyond the ISO standard itself. The DPDP Act 2023 (Act 22/2023) and the DPDP Rules 2025 (notified 13 November 2025) make continuous improvement a statutory necessity for several operational obligations.
The DPDP Rules 2025 phased commencement is the load-bearing Indian external driver. The Rules came into force in phases, Rules 1, 2 and 17 to 21 on the notification date (13 November 2025); the core operational provisions (the consent-notice content and language; the verifiable parental consent mechanism; the SDF thresholds; the breach-notification format; the retention and erasure timelines; the Consent Manager registration; the grievance-redressal response periods) on later dates through approximately May 2027 for full enforceability. Each commencement is an improvement-trigger event, the PIMS must adapt the consent flow, the age-assurance mechanism, the breach-notification format, the deletion workflow, the consent-manager integration, the Grievance Officer SLA, the SDF obligations. The continual-improvement programme is the operational vehicle by which the organisation absorbs each phase on the commencement timeline. An organisation that treats each Rule as a one-off compliance project misses the 10.1 discipline; an organisation that wires each commencement into the Register, prioritises the maturation work and advances the maturity floor is the 10.1-conformant organisation.
The DPDP section 10 SDF maturation curve is the load-bearing Indian multi-year improvement programme. For a Significant Data Fiduciary, the section 10 obligations, the DPO based in India and accountable to the board; the SDF DPIA per processing activity; the periodic independent data audit; the algorithmic-software review, are themselves a multi-year maturation programme that no single corrective action can deliver. The DPO function matures from a vacancy or a figurative appointment (L1) to a fully-staffed privacy centre of excellence (L5); the SDF DPIA cadence matures from ad-hoc to continuous; the independent-data-audit findings closeout rate matures from 50 percent to 100 percent; the algorithmic-software review matures from periodic to continuous. The 10.1 programme is the operational vehicle by which the SDF maturation is delivered.
The DPBI enforcement feedback loop is the load-bearing Indian regulator-driven improvement stream. The Data Protection Board of India (under section 18) is emerging through 2026 and 2027. Its early orders, its interpretation of the Schedule penalty maxima (up to two hundred and fifty crore rupees for section 8(5) failure; up to two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10), its engagement patterns, its precedent on the breach-notification clock, and its operational portal for section 8(6) notifications will reshape the improvement portfolio continuously. Every material DPBI order against a peer organisation produces a Register entry (the lesson, the PIMS impact, the maturation recommended); every DPBI engagement against the organisation itself engages Clause 10.2 (the corrective-action loop) and Clause 10.1 (the structural improvement). No other jurisdiction matches the DPBI-driven regulator-feedback loop with the DPDP section 10 SDF board-DPO accountability, the 10.1 programme is the operational mechanism by which the organisation absorbs the regulator feedback.
The Companies Act 2013 section 134(3)(n) board-reporting duty and the section 177 Audit Committee remit (read with the SEBI LODR Regulation 21 Risk Management Committee for listed entities) link the maturity advancement to the corporate-governance apparatus. The board's annual report discloses the risk-management framework, of which the PIMS is part; the maturity advancement trajectory is the board-reportable material. The section 33 penalty exposure underscores the improvement weight, the Schedule maxima attach to operational failures that the 10.1 trend-aware improvements can prevent; the DPBI, in determining the penalty, will consider whether the Fiduciary had the maturity-advancement programme in place and whether the underlying control was on a maturity-advancement trajectory.
The lineage is the wedge. K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (judgment delivered 24 August 2017 by a nine-judge Bench) declared the right to privacy a fundamental right. The Aadhaar judgment, (2019) 1 SCC 1 (26 September 2018) set the proportionality test. The DPDP Act was enacted 11 August 2023; the DPDP Rules 2025 notified 13 November 2025; ISO/IEC 27701:2025 published 14 October 2025. The right to privacy, having been declared fundamental, is delivered through the operational obligations of the DPDP Act, which are in turn demonstrated through ISO/IEC 27701:2025, and Clause 10.1 is the programme instrument by which the demonstration compounds across cycles.
The cost of non-compliance
The cost of a Clause 10.1 failure breaks down into four bands.
The certification band. A 10.1 major nonconformity, typically the missing-programme pattern, the empty-Register pattern, the no-effectiveness-verification pattern or the demarcation-failure pattern, triggers surveillance-audit remediation. The certification body requires the organisation to stand up the programme within a defined window (typically 60 to 90 days), produce the Register with a credible entry set, run the first Steering Group cycle, and evidence at least one closed improvement with effectiveness verification. Repeated 10.1 findings cascade into certificate suspension.
The regulatory band. After a personal-data breach or a principal-complaint spike, the DPBI (under section 18) and the sector regulators will examine whether the underlying control was on a maturity-advancement trajectory. The absence of the 10.1 programme, or the absence of the relevant improvement on the relevant dimension, is treated as an aggravating factor in the penalty determination under section 33. The Schedule maxima (up to two hundred and fifty crore rupees for section 8(5) failure; up to two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10) make the aggravation material.
The customer band. Enterprise customers run privacy audits of their Indian vendors; the 10.1 evidence (the Register, the Matrix, the Tracker, the Roadmap, the Log, the last cycle's improvement portfolio) is a standard ask in the mature enterprise segment. The absence is a red flag in the vendor risk score; the consequence is the customer's remediation request, the contractual change, or, in the high-stakes enterprise segment, the offboarding. The customer-driven improvement stream is itself a load-bearing 10.1 source for the ITeS / SaaS / BPO segment that depends on enterprise contracts.
The opportunity band. A PIMS that does not advance loses the cross-framework use. The GDPR equivalence (under the 2025 Annex D correspondence map), the SOC 2 Privacy TSC alignment, the NIST Privacy Framework Govern-P mapping, each depends on a PIMS that demonstrates the maturity-advancement discipline. An Indian SaaS firm targeting global enterprise customers cannot defend its privacy posture on a PIMS that has not advanced in three years; the customer audit will surface the maturity floor and the contract will be lost to a competitor with the demonstrable advancement.
Scope and Applicability
Organisational scope
Clause 10.1 applies to every organisation that has scoped a PIMS under Clause 4.3, controller, processor, or both; BFSI, healthcare, IT-ITeS, e-commerce, edtech, manufacturing; growing company, mid-sized, enterprise, SDF. The improvement discipline scales with the organisation but does not disappear for any size. A 50-person organisation can run the 10.1 programme as a quarterly DPO review with a 20-entry Register on a spreadsheet; a 2,000-person growing firm typically runs a quarterly Steering Group with a 100-entry Register on the privacy-management platform; an SDF runs a board-grade programme with the section 10 maturation sub-portfolio and the Audit Committee engagement.
Scope of the improvement programme
The 10.1 scope covers the entire PIMS, the context and scope (clauses 4.1 to 4.3), the leadership and policy (clauses 5.1 to 5.3), the planning (clauses 6.1 to 6.3), the support (clauses 7.1 to 7.5), the operation (clauses 8.1 to 8.3), the performance evaluation (clauses 9.1 to 9.2), the improvement (clauses 10.2 to 10.1), and the applicable Annex A.1 / A.2 / A.3 controls. The twelve dimensions in Section 2 are the operational decomposition of that scope.
What is NOT in 10.1 scope
- Information-security performance unrelated to privacy is partially in 10.1 scope where it overlaps with the Annex A.3 security controls the PIMS depends on. The ISMS Clause 10.1 covers the rest; the integrated-with-distinction posture from Clause 6.1 carries through.
- Operational performance unrelated to the PIMS is not in 10.1 scope.
- Financial performance is not in 10.1 scope unless the organisation has set a privacy objective tied to a financial metric.
- AI / algorithmic performance unrelated to privacy is in 10.1 scope only where the AI processes personal data and the algorithmic-software review under DPDP Rule 13(3) applies (for SDFs). The ISO/IEC 42001:2023 AI Management System Clause 10.1 covers the broader AI-performance improvement.
The DPDP and sector-regulator scope overlay
For Indian organisations, the 10.1 scope is overlaid by the DPDP Act (every Data Fiduciary and Data Processor) and by the sector regulators (RBI for banks / NBFCs / payment aggregators; SEBI for market intermediaries; IRDAI for insurers; CERT-In for every ICT operator). The sector-regulator improvement obligations, the continuous-improvement expectations of the RBI Cybersecurity Directions 2026; the SEBI CSCRF "Learn" function; the IRDAI annual compliance report's maturity-advancement trajectory, must be reconciled with the 10.1 programme to avoid duplicative steering groups; the integrated-with-distinction posture runs a single improvement programme with sector-regulator labelling. The DPDP section 10 SDF overlay adds the board-DPO accountability and the section 10 maturation sub-portfolio.
Key Definitions and Terminology
- Continual Improvement, the proactive, cadenced, programme-level activity by which the organisation raises the suitability, adequacy and effectiveness of the PIMS, distinct from the reactive corrective action under Clause 10.2.
- Improvement Opportunity, any signal from the ten source families (9.1 trend patterns; 9.2 audit observations; 9.3 management-review outputs; 10.2 corrective-action lessons; Clause 8 operational events; customer feedback; regulator engagements; technology-change scanning; workforce-feedback surveys; PII-principal expectation scanning) that suggests the PIMS could work better.
- Improvement Opportunities Register, the single source of truth for every identified opportunity, with the source, the description, the benefit case, the cost estimate, the priority, the owner, the lifecycle state, the verification method.
- Prioritisation Matrix, the multi-dimensional scoring rubric (privacy-principal benefit, regulatory benefit, commercial benefit, feasibility, strategic-fit) that drives the rank-ordered portfolio.
- Improvement Action Tracker, the per-improvement plan with the owner, the due date, the implementation evidence, the effectiveness-check schedule, the sustainment plan.
- Maturity Advancement Roadmap, the multi-year north star; the twelve-dimension × L1-to-L5 progression with the milestone, the dependency, the cost band, the indicator per level.
- Lessons-Learned Log, the cumulative intelligence from every Clause 9 source, every Clause 10.2 corrective-action cycle, every operational event, every improvement cycle; the structured capture of the lesson, the generalisation, the action, the dimension impact, the maturity-floor effect.
- Eight-Step Discipline, identify, capture, triage, prioritise, plan, implement, verify, sustain, the operational lifecycle of every commissioned improvement.
- Improvement Steering Group, the cross-functional body that owns the continual-improvement programme; meets quarterly; chaired by the DPO; sponsored by the chief executive.
- Proactive, the orientation of 10.1 (opportunity-driven, forward-looking), distinct from the reactive orientation of 10.2 (nonconformity-driven, backward-looking).
- Sustained, the test that the improvement produces a permanent floor advancement, verified by the 30 / 60 / 90-day effectiveness check and the maturity-floor indicator.
- Maturity Floor, the lowest L-level across the twelve dimensions; the floor advancement is the load-bearing 10.1 outcome (the worst dimension is the rate-limiting constraint on the PIMS effectiveness).
- Effectiveness Verification, the independent check (at 30, 60 and 90 days post-implementation) that the improvement produced the intended outcome; the verifier is independent of the implementer.
- Recurring-Nonconformity Pattern, the demarcation signal; a nonconformity that recurs two or three times despite corrective action; escalates from 10.2 to 10.1 for the structural-improvement treatment.
- Privacy Enhancement Technology (PET), the technology class whose adoption advances dimension 12; includes differential privacy, secure multi-party computation, homomorphic encryption, federated learning, pseudonymisation, anonymisation, synthetic data.
- SDF Overlay, the additional improvement sub-portfolio for a Significant Data Fiduciary under DPDP section 10 (the DPO function maturation; the SDF DPIA cadence; the independent-data-audit closeout; the algorithmic-software review).
- DPBI Enforcement Feedback Loop, the regulator-driven improvement stream; the DPBI's early orders, penalty determinations, engagement patterns feed the Register continuously.
- Integrated-with-Distinction Posture, for organisations running an ISMS alongside the PIMS, the single Steering Group, single Register, single Matrix, single Tracker, single Roadmap, single Log with the ISMS / PIMS labels.
- Demarcation, the routing rules that distinguish 10.2 corrective action from 10.1 improvement from 6.3 planned change from 8.x operational change.
- Maturity Dimension, one of the twelve privacy dimensions along which the PIMS advances (consent and notice quality; ROPA and record-keeping; data-principal rights fulfilment; DPIA pipeline; processor and sub-processor chain; cross-border transfer; breach detection, notification, response; privacy by design and by default; children-data controls; SDF section 10 obligations; privacy culture and awareness; privacy technology and automation).
Relationship to Other Clauses and Frameworks
Within ISO/IEC 27701:2025
10.1 derives its opportunities from 9.1 (the trend patterns), 9.2 (the audit observations), 9.3 (the management-review improvement-output route) and 10.2 (the corrective-action lessons). The improvement programme implements the "opportunities" half of Clause 6.1 (the other half is the privacy risk register). The commissioned improvements may route to clauses 5.2 (policy refresh), 6.2 (objective reset), 6.3 (planned changes), 7.1 (resource allocation), 7.2 (competence uplift), 7.3 (awareness), 7.4 (communication), 7.5 (documented information update), 8.1 (operational process redesign), 8.2 (privacy risk methodology refresh), 8.3 (treatment and SoA update), and advance the maturity of the applicable Annex A.1 / A.2 / A.3 controls. The recurring-nonconformity pattern escalates from 10.2 to 10.1.
ISO/IEC 27001:2022 Clause 10.1
Structurally identical on the infosec side. For organisations running both certifications, the integrated 10.1 programme has a single Steering Group, a single Register with the ISMS / PIMS tags, a single Matrix, a single Tracker, a single Roadmap with the dimension labels, a single Log. The DPO and the CISO jointly own the programme; the chief executive or managing director sponsors.
GDPR
GDPR Article 24(1) "ongoing basis" controller responsibility is the closest statutory analogue; the controller must "review and update" the measures. Article 5(2) accountability principle reinforces the demonstrability duty, improvement must be evidenced. Article 32(1)(d) "regular testing, assessing and evaluating the effectiveness" is the explicit effectiveness-evaluation anchor that 10.1 discharges. The EDPB Guidelines on DPIA review-on-change (post-Schrems II, post the modernised SCCs) describe the transfer-regime improvement dimension. The EDPB Recommendations 01/2020 on supplementary measures feed the cross-border-transfer improvement pipeline.
DPDP Act 2023 + DPDP Rules 2025
Section 8 (general obligations; section 8(5) safeguards; section 8(6) the breach clock (intimation without delay; seventy-two-hour report), continuous improvement subjects). Section 9 (children and persons with disability, the verifiable-parental-consent mechanism and the no-behavioural-monitoring control mature through 10.1). Section 10 (SDF, the entire SDF overlay is a multi-year improvement programme). Sections 11 to 14 (rights turnaround, continuous improvement KPIs). Section 13 (grievance-redressal response period, Grievance Officer SLA improvement). Section 16 (cross-border negative list, transfer-screening maturity advances through 10.1). Section 18 (DPBI engagement, the regulator-driven improvement stream). Section 33 plus Schedule (penalty maxima, the avoided penalty exposure funds the improvement programme).
Companies Act 2013 + SEBI LODR
Section 134(3)(n) (board-report discloses the risk-management framework; the maturity advancement is board-reportable). Section 177 (Audit Committee's risk-management oversight remit). SEBI LODR Regulation 21 (Risk Management Committee composition and remit for listed entities). The 10.1 Roadmap trajectory is the board-reportable maturity-advancement narrative.
NIST Privacy Framework v1.0
The Govern-P function's "risk-management strategy" subcategory is the closest cross-framework analogue. The Govern-P "monitoring and review" subcategory maps to the effectiveness-verification discipline. The Communicate-P "reporting" subcategory maps to the management-review input route. The five Functions (Identify-P, Govern-P, Control-P, Communicate-P, Protect-P) each contribute a 10.1 dimension.
SOC 2 Privacy TSC + Common Criteria
CC4.1 / CC4.2 (Monitoring) plus CC5.2 / CC5.3 (Change management) plus P8.0 (Monitoring for Compliance) close the SOC 2 improvement loop. A combined PIMS + SOC 2 continual-improvement discipline is common in the Indian SaaS / ITeS segment.
ISO/IEC 27002:2022
Only 5.34 (Privacy and protection of PII) is PII-specific. The information-security improvement lineage (5.35 Independent review of information security; 5.36 Compliance with policies, rules and standards; 5.37 Documented operating procedures) feeds the ISMS Clause 10.1; the PIMS Clause 10.1 advances the 5.34 effectiveness specifically.
Other ISO siblings
ISO/IEC 29134:2017 (DPIA guidelines), the review-on-change discipline. ISO/IEC 27018:2019 (cloud PII processor), the sub-processor chain improvement. ISO 31000:2018 (risk management), Clause 6 Monitoring and Review. ISO/IEC 42001:2023 (AI Management System), Clause 10.1 alignment for the AI-driven processing improvement, the algorithmic-software review maturity advancement.
Detailed Implementation Guidance, The Improvement-Opportunity-to-Maturity-Advancement Loop
The 10.1 implementation is the four-step chain: stand up the programme (the Steering Group, the Register, the Matrix, the Tracker, the Roadmap, the Log); compile the opportunities (the source scan); prioritise and commission (the Steering Group decision); implement and sustain (the eight-step discipline on each commissioned improvement). Section 7 walks each in turn.
Step 1, Stand up the programme (the artefacts)
The artefact set is the load-bearing 10.1 design. Drafting it is the first 10.1 implementation step.
(a) The Improvement Steering Group. The Charter (in the Continual Improvement Policy, toolkit doc 01) names the standing members: the chief executive or managing director (the sponsor; may delegate to the COO); the DPO (the chair of the Steering Group); the CISO (the security-overlay member); the Head of Legal (the regulatory-change member); the Head of Internal Audit (the audit-observation member); the standing business-process owners (the Head of Marketing for the consent-quality dimension; the Head of Customer Service for the rights-response dimension; the Head of Procurement for the processor-chain dimension; the Head of Engineering for the privacy-by-design and the privacy-technology dimensions; the Head of People for the awareness and culture dimension); the Company Secretary for the board-governance linkage (for SDFs and listed entities). The Steering Group meets quarterly; the quorum is the DPO plus two of the three core-function heads (CISO / Legal / Internal Audit).
(b) The Improvement Opportunities Register. The Register (toolkit doc 03) is the single source of truth. The schema: the unique ID; the source (9.1 / 9.2 / 9.3 / 10.2 / Clause 8 / customer / regulator / technology / workforce / principal); the source reference (the KPI trend; the audit observation reference; the management-review decision ID; the corrective-action ID; the operational event ID; the customer-audit reference; the regulator-engagement reference; the technology-scan reference; the survey reference; the principal-feedback reference); the description; the benefit case (the privacy-principal benefit; the regulatory benefit; the commercial benefit); the cost estimate (the internal effort; the external advisory; the technology; the training); the feasibility score; the strategic-fit score; the priority score (the rubric output); the owner; the lifecycle state (identified, triaged, prioritised, planned, implementing, verifying, sustained, closed); the verification method; the maturity-dimension impact (which of the twelve dimensions the opportunity advances); the maturity-floor effect (does it raise the floor).
(c) The Prioritisation Matrix. The Matrix (toolkit doc 04) is the scoring rubric. The five dimensions:
- Privacy-principal benefit (0 to 5): the extent to which the improvement advances the privacy-principal outcome (the consent quality, the rights latency, the breach prevention, the transfer-screening depth).
- Regulatory benefit (0 to 5): the extent to which the improvement advances the regulatory posture (the DPDP conformity; the SDF section 10 maturation; the sector-regulator expectations; the cross-border regime).
- Commercial benefit (0 to 5): the extent to which the improvement advances the commercial position (the enterprise-customer audit; the contract-win rate; the brand position; the operational efficiency).
- Feasibility (0 to 5): the extent to which the improvement is implementable in the next cycle (the resource availability; the technology readiness; the organisational readiness; the dependency profile).
- Strategic-fit (0 to 5): the extent to which the improvement aligns with the Maturity Advancement Roadmap and the organisation's strategic direction.
The composite score is the weighted sum; the Singahi default weights are 30 / 25 / 15 / 15 / 15 (the principal benefit is the heaviest; the regulatory benefit is the second; the commercial and the feasibility and the strategic-fit carry the rest). The rank-ordering is the output.
(d) The Improvement Action Tracker. The Tracker (toolkit doc 05) is the per-improvement plan. Every commissioned improvement becomes a Tracker entry with the plan, the owner, the due date, the implementation evidence, the effectiveness-check schedule, the sustainment plan.
(e) The Maturity Advancement Roadmap. The Roadmap (toolkit doc 06) is the multi-year north star. The Roadmap has the twelve dimensions on the rows and the L1-to-L5 trajectory on the columns; each cell has the milestone, the dependency, the cost band, the indicator. The Roadmap is refreshed semi-annually; the Steering Group tests the trajectory against the actual advancement.
(f) The Lessons-Learned Log. The Log (toolkit doc 07) is the cumulative intelligence. The schema: the date; the source (the improvement cycle; the corrective action; the operational event; the audit observation); the lesson (the structured capture); the generalisation (the cross-dimension applicability); the action (the Register entry it generates); the dimension impact; the maturity-floor effect.
Step 2, Compile the opportunities (the source scan)
The source scan is the cadenced activity that populates the Register. The Singahi calibration:
Monthly, the DPO function runs the 9.1 trend-pattern scan (the KPIs that are plateauing, decaying, or showing variance patterns that suggest a structural opportunity); the operational-event scan (the Clause 8 events that suggest a structural opportunity); the technology-change scan (the new privacy-enhancing technologies; the new AI / generative-AI capabilities; the new privacy-engineering tools).
Quarterly, the Steering Group runs the 9.2 audit-observation scan (the opportunities-for-improvement findings; the structural observations); the 9.3 management-review-output scan (the improvement-output routing); the 10.2 corrective-action-lesson scan (the recurring-nonconformity patterns that suggest a structural improvement); the customer-feedback scan (the enterprise-customer audit findings; the customer-DPA monitoring signals); the regulator-engagement scan (the DPBI early orders; the CERT-In advisories; the sector-regulator instruments).
Semi-annually, the workforce-feedback scan (the privacy-awareness survey; the privacy-champions network feedback); the principal-expectation scan (the Grievance Officer complaint themes; the rights-request patterns).
Annually, the SDF section 10 maturation scan (for SDFs; the DPO function, the SDF DPIA cadence, the independent-data-audit findings, the algorithmic-software review, the board-reporting pack); the DPDP Rules 2025 phased-commencement scan (the Rules coming into force in the next phase); the Maturity Advancement Roadmap trajectory check.
Each scan produces a batch of Register entries; the DPO function triages the batch (the duplicates merge; the overlaps link; the infeasible are deferred with the rationale); the prioritised batch goes to the next Steering Group.
Step 3, Prioritise and commission (the Steering Group)
The Steering Group meets quarterly. The standard agenda:
- Opening (5 minutes), the chair (the DPO) confirms the quorum; conflicts-of-interest are declared.
- The Register review (15 minutes), new entries since the last cycle; source and dimension distribution; duplicates and overlaps.
- The Matrix scoring workshop (30 minutes), the Steering Group scores the top ten new entries on the five-dimension rubric; consensus-based, dissent recorded.
- The portfolio review (20 minutes), the currently-implementing improvements (Tracker view); closeout trajectory; effectiveness-check results; sustainment status.
- The Roadmap check (15 minutes), maturity-floor advancement since the last cycle; the dimension-level trajectory; the strategic-fit test.
- The commissioning decision (20 minutes), the top-three-to-five new improvements commissioned; owners assigned; due dates set; budget committed.
- The demotion / deferral decision (10 minutes), entries deferred (low score, low feasibility, low strategic-fit) with rationale; entries demoted; entries closed.
- The lessons-learned review (10 minutes), Log entries since the last cycle; the generalisations; the cross-dimension applicability.
- The closing (5 minutes), next-cycle date; action items; the board-reporting-pack deadline (for SDFs and listed entities).
The Minutes are circulated within 14 days; the commissioned improvements enter the Tracker; the deferred and demoted entries remain in the Register with the rationale.
Step 4, Implement and sustain (the eight-step discipline)
The eight-step discipline runs on each commissioned improvement.
Step 1, Identify. The opportunity is captured in the Register with the full schema.
Step 2, Capture. The DPO function triages; duplicates merge, overlaps link, infeasible are deferred with rationale. The triaged opportunity goes to the Steering Group with the proposed Matrix scoring.
Step 3, Triage. The Steering Group scores the opportunity on the five-dimension rubric; the composite score and the rank-ordering follow.
Step 4, Prioritise. The Steering Group decides whether to commission, defer, or close. The decision is documented in the Minutes.
Step 5, Plan. The commissioned opportunity becomes a Tracker entry. The named owner drafts the improvement plan (scope, deliverables, milestones, resources, dependencies, risks, verification method, sustainment plan); the plan is reviewed at the next Steering Group.
Step 6, Implement. The owner runs the plan with implementation evidence captured per milestone; material deviations escalate to the Steering Group chair.
Step 7, Verify. The effectiveness-check runs at 30, 60 and 90 days post-implementation. The verifier is independent of the implementer (the DPO function for business-process-owner improvements; the Internal Audit function for DPO-function improvements). The result is recorded in the Tracker (Effective / Partially-effective / Not-effective).
Step 8, Sustain. The sustained improvement is the new baseline. The documentation is updated (the policy, the procedure, the SoA, the ROPA, the training material); the training is refreshed; the operational handover to the business-process owner is completed; the indicator monitoring continues; the lessons-learned entry is captured in the Log.
The maturity-advancement loop
The eight-step discipline produces a maturity advancement on one or more of the twelve dimensions. The advancement is recorded in the Roadmap (the L-level moves up; the indicator changes; the milestone is achieved). The maturity-floor effect is recorded (the floor moves up if the advancement was on the lowest-L dimension).
The maturity-advancement loop is the cumulative engine. Each cycle produces a small advancement; the cumulative advancement over four to six cycles moves the organisation from L2 to L4. The certification auditor tests the loop by walking a dimension's trajectory across cycles; the regulator tests the loop by examining the maturity-floor advancement after a major event.
The DPDP-driven improvement drivers (the Indian signature)
The three Indian external-driver streams are wired into the programme.
The DPDP Rules 2025 phased-commencement stream. The Head of Legal maintains the commencement tracker (the Rule, the commencement date, the operative obligation, the PIMS impact, the Register entry). Each phase produces a batch of Register entries; the Steering Group prioritises the maturation work; the implementation is on the phase-commencement timeline.
The SDF section 10 maturation stream. For SDFs (and for organisations approaching the SDF thresholds), the DPO function maintains the SDF maturation roadmap (the section 10 obligation, the current state, the target state, the milestone, the dependency, the cost, the indicator). The maturation is itself a multi-year programme that the Steering Group governs alongside the dimension-level improvements.
The DPBI enforcement-feedback stream. The Head of Legal monitors the DPBI's early orders (the published decisions; the penalty determinations; the corrective-direction patterns; the engagement portal updates). Each material order against a peer organisation produces a Register entry (the order, the lesson, the PIMS impact, the maturation recommended). Each order against the organisation itself engages Clause 10.2 (the corrective-action loop) and Clause 10.1 (the structural improvement).
The integrated-with-distinction posture
For organisations running an ISMS (ISO/IEC 27001:2022) alongside the PIMS, the integrated 10.1 programme is the default. The integrated posture: a single Steering Group with the ISMS and the PIMS labels; a single Register with the system tags; a single Matrix with the system dimension; a single Tracker; a single Roadmap with the ISMS and the PIMS dimension labels; a single Log. The DPO and the CISO jointly own the programme; the chief executive or managing director sponsors.
The integrated-with-distinction discipline does not mean the two systems are conflated. The PIMS-specific improvements (the consent quality; the rights latency; the DPIA pipeline; the processor-chain automation; the SDF overlay) are presented in their own right; the ISMS-specific improvements (the vulnerability management; the patch latency; the security operations throughput) are presented in their own right. The shared improvements (the breach detection; the training; the records currency; the GRC platform adoption) are presented once, with the ISMS and the PIMS dimensions labelled.
The certification-cycle alignment
The 10.1 cadence is reconciled with the certification cycle. The Singahi default: the annual improvement cycle is calibrated so that at least one improvement is closed with effectiveness verification before each surveillance audit; the surveillance-audit-ready state is the Tracker with at least three closed improvements in the last twelve months, the Register with at least one entry per source family, the Roadmap with the L-level advancement reconciled. For the Stage 1 / Stage 2 cycle, the first 10.1 cycle is run after the first full Clause 9.1 cycle, the first Clause 9.2 audit and the first Clause 9.3 management review, the 10.1 programme operationalises the lessons from the three evaluation cycles. For the recertification cycle, the Roadmap trajectory across the three-year cycle is the marquee recertification evidence; the certification auditor will walk a dimension's advancement across the three-year window.
Tools, Technologies, and Solutions
The tool categories
GRC-with-privacy platforms (the GRC flavour that supports the privacy improvement programme). These are the platforms that host the Register, the Matrix, the Tracker, the Roadmap, the Log. Selection criteria: India-DPDP coverage (most global platforms are GDPR-heavy and DPDP-thin); the improvement-programme artefact support as first-class objects (the Register entry, the Matrix scoring, the Tracker entry, the Roadmap dimension-level) rather than free-form text fields; the SDF-overlay support for the section 10 sub-portfolio; the integrated-with-distinction support for the PIMS + ISMS combined programme.
Privacy-enhancing-technology (PET) platforms. The technology class whose adoption advances dimension 12.
Consent-management platforms with Consent Manager interoperability. Hosts the consent records, the notice delivery, the withdrawal workflow, and (as the ecosystem matures) the Consent Manager integration. Selection criteria: India-DPDP support (the seven consent qualities from section 6; the withdrawal-as-easily-as-given mechanism); the Consent Manager interoperability for when the first Consent Managers are registered.
DSAR / rights-request platforms. Hosts the rights-request intake, triage, workflow, SLA monitoring, response compilation, principal communication.
Privacy-engineering toolchains. Embeds privacy into the software-development lifecycle: privacy-tests-in-CI/CD; policy-as-code; data-flow-discovery; privacy-by-design review at the design stage.
ROPA automation platforms. Discovers processing activities from source systems and maintains a continuous ROPA.
Breach-response SOAR platforms. Automates the breach-detection-to-notification workflow; the dual-clock / triple-clock automation; the regulator-portal API submission; the principal-notification dispatch.
Selection criteria + build vs buy
Select on: India-DPDP coverage (the seven consent qualities, the section 8(6) breach clock, the SDF section 10 overlay, the section 13 Grievance Officer SLA); the integrated-with-distinction posture (PIMS and ISMS improvement in one platform with role-tagging); the twelve-dimension support as first-class objects; the integration with the existing GRC / ITSM / board-portal stack; the SDF-overlay support (the SDF DPIA cadence, the independent-data-audit-findings intake, the algorithmic-software review record).
Most growing companies should buy the GRC-with-privacy platform and the consent-management platform; build the Steering Group Charter, the Prioritisation Matrix rubric and the Maturity Advancement Roadmap in-house (these are organisation-specific and too strategically load-bearing to outsource); use external advisory for the first-cycle construction; migrate the Register compilation and the Tracker maintenance to in-house operation by year two; adopt the PET platforms selectively (the differential-privacy adoption for the analytics environment is often the highest-ROI 10.1 improvement for an Indian SaaS firm; the federated-learning adoption is the highest-ROI for an Indian healthcare or financial-data consortium).
Indicative effort (growing company, per cycle)
- Internal effort for the DPO function: 80 to 200 person-hours per quarterly cycle.
Policy and Procedure Templates
PIMS Continual Improvement Policy (sample of our own drafting)
The organisation shall continually improve the suitability, adequacy and effectiveness of the PIMS, in accordance with the PIMS Continual Improvement Procedure and the Improvement Steering Group Charter. Continual improvement is a planned, cadenced, programme-level activity, distinct from the reactive corrective action under Clause 10.2. The organisation maintains the Improvement Opportunities Register as the single source of truth, sourced from the ten families (9.1 monitoring trends; 9.2 audit observations; 9.3 management-review outputs; 10.2 corrective-action lessons; Clause 8 operational events; customer feedback; regulator engagements; technology-change scanning; workforce-feedback surveys; PII-principal expectation scanning). The organisation maintains the Prioritisation Matrix (privacy-principal benefit, regulatory benefit, commercial benefit, feasibility, strategic-fit), the Action Tracker, the twelve-dimension Maturity Advancement Roadmap, and the Lessons-Learned Log. For SDFs under DPDP section 10, the SDF maturation sub-portfolio is governed alongside the dimension-level improvements.
Improvement Steering Group Charter Policy (sample of our own drafting)
The Improvement Steering Group Charter fixes the membership (the chief executive or managing director as the sponsor; the DPO as the chair; the CISO; the Head of Legal; the Head of Internal Audit; the standing business-process owners; the Company Secretary for the board-governance linkage); the quorum (the DPO plus two of the three core-function heads); the cadence (quarterly minimum; monthly for early cycles or post-incident); the input set (Register, Matrix, Tracker, Roadmap, Log); the output set (commissioning, deferral, demotion, closeout decisions); the routing rules. The Charter is signed by the chief executive or managing director and archived per Clause 7.5.
Eight-Step Discipline Policy (sample of our own drafting)
Every commissioned improvement runs through the eight-step discipline: (1) Identify, captured in the Register; (2) Capture, triaged by the DPO function; (3) Triage, scored on the five-dimension rubric; (4) Prioritise, commission / defer / close decision; (5) Plan, Tracker entry with the improvement plan; (6) Implement, the owner runs the plan, evidence per milestone; (7) Verify, the effectiveness-check at 30, 60 and 90 days, verifier independent of the implementer; (8) Sustain, the new baseline; documentation, training, operational handover completed; indicator monitoring continues; lessons-learned captured.
Maturity Advancement Policy (sample of our own drafting)
The organisation maintains the twelve-dimension × L1-to-L5 Maturity Advancement Roadmap as the multi-year north star of the continual-improvement programme. The twelve dimensions are: (1) consent and notice quality; (2) ROPA and record-keeping; (3) data-principal rights fulfilment; (4) DPIA pipeline; (5) processor and sub-processor chain; (6) cross-border transfer; (7) breach detection, notification, response; (8) privacy by design and by default; (9) children-data controls; (10) SDF section 10 obligations; (11) privacy culture and awareness; (12) privacy technology and automation. The maturity-floor advancement (the lowest L-level moves up) is the load-bearing 10.1 outcome. The Roadmap is refreshed semi-annually; top management receives the maturity-advancement report at the Clause 9.3 management review.
The four procedure structures (sample, of our own drafting)
The 10.1 procedure set follows the same structure: (1) purpose and scope; (2) the Steering Group; (3) the artefact set; (4) the source scan; (5) the prioritisation and the commissioning; (6) the eight-step discipline; (7) the maturity-advancement loop; (8) the DPDP-driven improvement drivers; (9) the integrated-with-distinction posture; (10) the Documented Information control per Clause 7.5. The full text is in toolkit docs 02 (the operational procedure), 03 (the Register), 04 (the Matrix), 05 (the Tracker), 06 (the Roadmap), 07 (the Log).
Improvement-Risk and Treatment
This section is the operational complement to the Clause 6.1 risk methodology. Where 6.1 builds the framework and 8.2 applies it per processing activity, the improvement-risk layer (the 10.1 contribution) assesses the risk that the improvement discipline fails, that the opportunities are missed, that the prioritisation is biased, that the implementation stalls, that the effectiveness is not verified.
The improvement-risk dimensions
For the improvement discipline as a whole, the improvement-risk assessment evaluates four dimensions:
Dimension 1, Opportunity-capture completeness. The risk that the ten source families are not all scanned; the Register receives entries from 9.1 / 9.2 / 9.3 but the customer-feedback and the principal-expectation families are absent; the technology-change scan is irregular; the regulator-engagement scan misses the DPBI orders against peer organisations.
Dimension 2, Prioritisation bias. The risk that the Matrix is gamed, the commercial-benefit dimension is overweighted; the privacy-principal benefit is under-scored; the strategic-fit is manipulated to favour pet projects; the feasibility is inflated for low-effort / low-impact improvements.
Dimension 3, Implementation discipline. The risk that the commissioned improvements stall, the owners do not have the time; the resources are not committed; the dependencies are not resolved; the deviations are not escalated; the closeout drifts to the next cycle.
Dimension 4, Effectiveness verification integrity. The risk that the effectiveness check is perfunctory, the verifier is the implementer's colleague; the check is a tick-box; the KPI trend is not examined; the maturity-floor advancement is not tested.
The improvement-risk register
The Singahi improvement-risk register (folded into toolkit doc 09 Section 4) records, per risk: the dimension, the risk description, the integrity control (the Internal Audit's 9.2 test of the 10.1 discipline; the certification auditor's walk-through; the Audit Committee challenge for SDFs), the residual risk, the risk owner, the review date.
The 12 canonical 10.1 improvement-risks
| Risk | Dimension | Treatment |
|---|---|---|
| Register missing or empty | All | Stand up the Register (toolkit doc 03); retro-load twelve months of sources; quarterly Steering Group |
| Source coverage incomplete (families absent) | Opportunity-capture | Wire each source family to a named owner; report source coverage as a 10.1 KPI |
| Matrix rubric undefined or unused | Prioritisation bias | Define the rubric (toolkit doc 04); apply to every entry; the Steering Group tests a sample |
| Commercial benefit overweighted | Prioritisation bias | The default weights (30 / 25 / 15 / 15 / 15) anchor the principal benefit; the Steering Group documents the deviation if it changes the weights |
| Tracker not maintained | Implementation discipline | Stand up the Tracker (toolkit doc 05); report closeout rate at every Steering Group |
| Owners do not have capacity | Implementation discipline | Top-management sponsors the programme; the Charter fixes the owner commitment; the resourcing is on the Steering Group agenda |
| Effectiveness check perfunctory | Effectiveness verification | Independence rule: the verifier is not the implementer; the KPI trend is examined; the maturity-floor advancement is tested |
| Closeout-without-sustainment | Effectiveness verification | The eight-step discipline's Step 8 (Sustain) is the load-bearing step; the documentation update, the training refresh, the operational handover are verified |
| Recurring-improvement-overdue pattern | Implementation discipline | Escalate to the chair between cycles; the root-cause analysis on the implementation discipline |
| DPDP-Rules phased-commencement not reflected | Opportunity-capture | The Head of Legal maintains the commencement tracker; each phase produces a batch of Register entries |
| SDF overlay absent (for SDFs) | All | Stand up the SDF maturation sub-portfolio; the DPO function owns the section 10 obligations |
| Demarcation failure (10.2 mis-labelled as 10.1) | All | The Register has the source-tag; the Internal Audit tests the demarcation under 9.2 |
The high-impact, high-likelihood risks to treat first are: the missing-Register risk; the closeout-without-sustainment risk; the effectiveness-check-perfunctory risk; the demarcation-failure risk. These four account for most of the 10.1 audit nonconformities in the Indian growing-company segment.
Audit and Compliance Checklist
The 25 questions below cover the audit-evidence surface for Clause 10.1. Expected evidence and red flags noted. Most can be answered from the toolkit doc 09 audit-evidence checklist.
- Is there a PIMS Continual Improvement Policy? Expected: dated, version-controlled, signed by the chief executive or managing director, counter-signed by the DPO and the Company Secretary; covers the Steering Group, the artefact set, the eight-step discipline, the twelve-dimension Roadmap, the DPDP-driven drivers. Red flag: missing or unsigned.
- Is the Improvement Steering Group constituted per the Charter? Are the standing members named? Is the quorum defined? Is the cadence fixed at quarterly minimum?
- Does the Improvement Opportunities Register exist as the single source of truth? Is it populated with entries from each of the ten source families?
- Is the Prioritisation Matrix documented? Are the five-dimension rubric and the default weights (30 / 25 / 15 / 15 / 15) defended? Is the rubric applied to every commissioned improvement?
- Is the Action Tracker maintained? Are the commissioned improvements with the plan, the owner, the due date, the implementation evidence, the effectiveness-check, the sustainment plan recorded?
- Is the Maturity Advancement Roadmap populated across the twelve dimensions × L1-to-L5? Are the milestones, the dependencies, the cost bands, the indicators documented?
- Is the Lessons-Learned Log maintained? Are the lessons structured (the lesson, the generalisation, the action, the dimension impact, the maturity-floor effect)?
- Are the Minutes of the Steering Group circulated within 14 days? Are the commissioning, deferral, demotion and closeout decisions documented?
- Is the effectiveness-check independent (the verifier is not the implementer)? Is the check at 30, 60 and 90 days post-implementation? Is the result recorded (Effective / Partially-effective / Not-effective)?
- Is the demarcation between 10.2 (corrective action) and 10.1 (improvement) evidenced? Are the source-tags applied correctly in the Register?
- Is the recurring-nonconformity pattern escalated from 10.2 to 10.1? Is the escalation documented in the Register and the Log?
- Is the integrated-with-distinction posture evidenced (for organisations running an ISMS alongside the PIMS)? Combined Steering Group; combined Register; combined Matrix; combined Tracker; combined Roadmap; combined Log?
- Is the DPDP Rules 2025 phased-commencement tracker maintained? Does each phase produce a batch of Register entries?
- For SDFs, is the SDF section 10 maturation sub-portfolio governed alongside the dimension-level improvements? Is the board-reporting pack delivered on the SEBI LODR cycle (for listed entities)?
- Is the DPBI enforcement-feedback stream monitored? Does each material DPBI order against a peer organisation produce a Register entry?
- Is the certification-cycle alignment evidenced? At least three improvements closed with effectiveness verification before each surveillance audit? The Roadmap trajectory across the three-year recertification cycle?
- Has the Internal Audit function (under Clause 9.2) tested the 10.1 discipline? The Register; the Matrix; the Tracker; the Roadmap; the Log; the demarcation; the eight-step discipline on a sample?
- Is the source coverage complete? Are all ten source families represented in the Register? Is the source-coverage reported as a 10.1 KPI?
- Is the closeout rate tracked as a 10.1 KPI (target 100 percent within the due date)? Are the recurring-overdue improvements escalated?
- Is the effectiveness-verification rate tracked as a 10.1 KPI (target 100 percent of closed improvements with the effectiveness recorded)?
- Is the maturity-floor advancement tracked across cycles? Is the L-level movement on each dimension reported?
- Are the lessons-learned entries actioned? Does each lesson generate a Register entry? Are the recurring patterns escalated to the structural-improvement pipeline?
- Are the privacy-enhancing-technology (PET) adoption opportunities on the Register for the analytics, AI-training, and cross-border-transfer scenarios?
- Are the AI-driven processing improvements on the Register? Is the algorithmic-software review on a maturation trajectory (for SDFs)?
- Are the board-reporting outputs (for SDFs and listed entities) aligned to the Companies Act 134(3)(n) / section 177 overlay? Is the maturity advancement board-reportable?
Common Stage-1 nonconformities the auditor will write up
- NC pattern 1: Continual-improvement programme missing. Major NC. Remediation: stand up the programme (the Charter, the Register, the Matrix, the Tracker, the Roadmap, the Log), 6 to 12 weeks.
- NC pattern 2: Register empty across two cycles. Major NC. This is the "no-improvement-culture" nonconformity, one of the most frequently cited PIMS surveillance-audit findings in tier-1 cert-body practitioner commentary. Remediation: retro-load twelve months of sources; run the first Steering Group cycle, 6 to 10 weeks.
- NC pattern 3: Improvement-as-corrective-action demarcation failure. Major or minor NC. The Register is populated entirely with 10.2 corrective actions mis-labelled as improvements. Remediation: re-tag the entries; build the 10.1-specific portfolio, 4 to 8 weeks.
- NC pattern 4: Closeout-without-effectiveness verification. Major or minor NC. The improvements are marked closed without testing whether the underlying KPI moved. Remediation: add the effectiveness-verification field; re-verify the closed improvements, 4 to 10 weeks.
- NC pattern 5: No Maturity Advancement Roadmap. Minor or major NC. Remediation: build the Roadmap across the twelve dimensions, 6 to 12 weeks.
- NC pattern 6: No Lessons-Learned Log. Minor NC. Remediation: stand up the Log; retro-load the lessons from the last twelve months, 4 to 8 weeks.
- NC pattern 7: DPDP-Rules phased-commencement blind. Minor or major NC (depending on the cycle). Remediation: stand up the commencement tracker; produce the batch of Register entries per phase, 4 to 8 weeks.
- NC pattern 8: SDF overlay absent (for SDFs). Major NC. Remediation: stand up the SDF maturation sub-portfolio; the DPO function owns the section 10 obligations, 8 to 16 weeks.
Metrics and KPIs
Figure · Measures
The measures that show Clause 10.1 is working
- Register entry count per source familyat least oneper cycle
- Register triage timeliness100%per cycle
- Steering Group cadence adherence100%per cycle
- Commissioning decision count per cycletrend insightper cycle
- Action Tracker closeout rate100%per cycle
The 16 KPIs below are the load-bearing measurement set for the 10.1 continual-improvement discipline. Each has a formula, a target, a threshold (green / amber / red), and a frequency.
- Register entry count per source family, Formula: count of Register entries per source family per cycle. Target: at least one entry per family per cycle. Threshold: green if all ten families represented; amber seven to nine; red below seven. Frequency: per cycle.
- Register triage timeliness, Formula: share of new entries triaged within 30 days of identification. Target: 100%. Threshold: green 100%, amber 80 to 99%, red below 80%. Frequency: per cycle.
- Steering Group cadence adherence, Formula: share of planned Steering Group meetings held on the Charter-fixed cadence. Target: 100%. Threshold: green 100%, amber 80 to 99%, red below 80%. Frequency: per cycle.
- Commissioning decision count per cycle, Formula: count of improvements commissioned per cycle. Target: trend insight, under 3 suggests a passive programme; over 15 suggests under-prioritisation. Frequency: per cycle.
- Action Tracker closeout rate, Formula: share of commissioned improvements closed within the due date. Target: 100%. Threshold: green 100%, amber 80 to 99%, red below 80%. Frequency: per cycle.
- Effectiveness-verification rate, Formula: share of closed improvements with the 30 / 60 / 90-day effectiveness recorded. Target: 100%. Threshold: green 100%, amber 90 to 99%, red below 90%. Frequency: per cycle.
- Sustainment rate at six months, Formula: share of closed improvements with the gain sustained at six months post-implementation. Target: 90%+. Threshold: green 90%+, amber 70 to 89%, red below 70%. Frequency: per cycle.
- Recurring-improvement-overdue pattern rate, Formula: share of overdue improvements that recurred across two or more cycles. Target: 0%. Threshold: green 0%, amber 1 to 10%, red above 10%. Frequency: per cycle.
- Maturity-floor advancement, Formula: the lowest L-level across the twelve dimensions, recorded per cycle. Target: the floor moves up by one L-level every four to six cycles. Threshold: green if floor advanced; amber if flat; red if declined. Frequency: per cycle.
- Dimension-level advancement, Formula: count of dimensions with the L-level advanced in the cycle. Target: at least one dimension per cycle. Frequency: per cycle.
- Lessons-learned action rate, Formula: share of lessons-learned entries that generated a Register entry. Target: 80%+. Frequency: per cycle.
- DPDP-Rules phased-commencement tracker currency, Formula: share of DPDP Rules 2025 commencement events with the corresponding Register entry in place before the commencement date. Target: 100%. Frequency: per cycle.
- Source-coverage breadth, Formula: count of source families represented in the Register per cycle (out of ten). Target: ten. Threshold: green 10, amber 7 to 9, red below 7. Frequency: per cycle.
- Clause 9.3 routing rate, Formula: count of improvement opportunities routed from the 9.3 management review into the Register per cycle. Target: at least three per annual cycle. Frequency: per cycle.
For SDFs, the additional KPIs:
- SDF section 10 maturation trajectory, Formula: the L-level movement on Dimension 10 per cycle. Target: at least one L-level every two cycles for the early-cycle SDF; stabilises at L4 by year three. Frequency: per cycle.
- Algorithmic-software review coverage, Formula: share of AI-driven processing activities with the algorithmic-software review completed in the cycle. Target: 100%. Frequency: per cycle.
Common Pitfalls and Audit Failures
Pitfall 1, The "we re-certified, what is there to improve?" failure. The PIMS passed Stage 2; the team moved on to operational firefighting; no Register exists; the maturity is decaying. Treatment: stand up the programme; retro-load twelve months of sources; run the first Steering Group cycle.
Pitfall 2, The "improvement-as-corrective-action" failure. The Register is populated entirely with 10.2 corrective actions mis-labelled as improvements. Treatment: re-tag the entries; build the 10.1-specific portfolio.
Pitfall 3, The vanity-Register failure. The Register has three generic entries with no source, no benefit case, no Matrix scoring. Treatment: rebuild the Register with the full schema per entry; the retro-load produces 30 to 100 real entries for a typical Indian growing company.
Pitfall 4, The closeout-without-effectiveness failure. Improvements are marked closed without testing whether the underlying KPI moved. Treatment: add the 30 / 60 / 90-day effectiveness-verification discipline; the verifier is independent of the implementer.
Pitfall 5, The no-sustainment failure. Improvements are closed but the gain decays back to the baseline within two cycles. Treatment: the Step 8 (Sustain) discipline verifies the documentation, training, and operational handover.
Pitfall 6, The recurring-overdue failure. The same improvements carry forward cycle after cycle; closeout is chronically below 80 percent. Treatment: escalate to the chair between cycles; the root-cause analysis on the implementation discipline.
Pitfall 7, The Matrix-rubric-undefined-or-gamed failure. The Matrix is unused, or is gamed to favour commercial benefit. Treatment: the default weights (30 / 25 / 15 / 15 / 15) anchor the principal benefit; the Internal Audit tests a sample under 9.2.
Pitfall 8, The no-Roadmap failure. No Maturity Advancement Roadmap; the twelve dimensions are not framed; the maturity-floor is not tracked. Treatment: build the Roadmap; refresh semi-annually; report to top management at the 9.3 review.
Pitfall 9, The no-Log failure. No Lessons-Learned Log; the cumulative intelligence is lost. Treatment: stand up the Log with the structured capture template; the lessons are actioned into the Register.
Pitfall 10, The DPDP-blindness failure. The programme does not reflect the DPDP Rules 2025 phased commencement; the DPBI orders against peers are not monitored. Treatment: stand up the commencement tracker; the regulator-engagement scan; the DPBI-feedback loop.
Pitfall 11, The SDF-overlay-absent failure (for SDFs). The section 10 maturation sub-portfolio is not governed; the algorithmic-software review is not on a maturation trajectory. Treatment: stand up the SDF maturation sub-portfolio.
Pitfall 12, The 10.2-to-10.1 escalation failure. The recurring-nonconformity pattern is not escalated from 10.2 to 10.1. Treatment: the Internal Audit flags the recurrence; the management review routes it to 10.1; the programme commissions the structural improvement.
Pitfall 13, The integrated-programme-conflation failure. The combined PIMS + ISMS programme conflates the two systems; the PIMS-specific improvements are lost. Treatment: maintain the integrated-with-distinction discipline.
Pitfall 14, The effectiveness-check-by-the-implementer failure. The verifier is the implementer's colleague; the KPI trend is not examined. Treatment: the independence rule, the DPO function verifies business-process-owner improvements; Internal Audit verifies DPO-function improvements.
Pitfall 15, The technology-blindness failure. The PET maturation and the AI / generative-AI risk surface are not scanned. Treatment: stand up the technology-change scan; the PET adoption opportunities on the Register.
Pitfall 16, The principal-expectation-blindness failure. The Grievance Officer complaint themes and the rights-request patterns are not examined for the structural signal. Treatment: stand up the principal-expectation scan; the Head of Customer Support owns the input.
Pitfall 17, The board-overlay-absent failure (for SDFs and listed entities). The board reporting on the maturity advancement is absent. Treatment: deliver the board reporting pack on the corporate-governance cadence; the Company Secretary owns the linkage.
Pitfall 18, The certification-cycle-misalignment failure. Zero closed improvements before the surveillance audit; the Tracker shows the same open entries cycle after cycle. Treatment: calibrate the annual cycle so at least three improvements are closed with effectiveness verification before each surveillance audit.
Pitfall 19, The portfolio-bias failure. The portfolio is biased to low-effort / low-impact improvements; the high-impact improvements (PET adoption, Consent Manager integration, SDF maturation) are perpetually deferred. Treatment: the Matrix rubric with the principal-benefit weight; the Roadmap trajectory check.
Illustrative Scenario 1: Failure, Maruti Consumer Brands and the Improvement-as-Corrective-Action Confusion (Illustrative)
Illustrative scenario, a composite example for guidance, not a specific Singahi engagement or a verified outcome.
Illustrative scenario. Maruti Consumer Brands is a fictional Mumbai-based direct-to-consumer wellness and personal-care brand with 480 staff, three offices, and approximately 2.1 million registered customers on its e-commerce platform; the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation. It is set after 13 May 2027, when the DPDP Act's duties take effect.
Maruti Consumer Brands achieved ISO/IEC 27701:2019 certification in late 2024 ahead of an enterprise-retail-partner contract. The PIMS was operationally thin but Stage-2-defensible: the SoA was signed; the privacy policy was published; the ROPA was a spreadsheet; the consent flow was a generic checkbox; the DSAR process was a customer-support queue. The certification body's surveillance audit in Q2 2028 raised a Clause 10.1 major nonconformity, the continual-improvement programme did not exist. The DPO responded by populating a "Continual Improvement Register" with eight entries, every one of which was a Clause 10.2 corrective action extracted from the previous cycle's nonconformity log. The Matrix was a single-row spreadsheet with a "priority" column. The Action Tracker was the corrective-action tracker re-labelled. The maturity-advancement roadmap did not exist.
The surveillance auditor's Stage-2 re-visit in Q3 2028 raised the same Clause 10.1 major nonconformity again, this time with the explicit finding that the demarcation between 10.2 and 10.1 was not understood and the proactive improvement programme was not operated. The certification body required a 90-day remediation. In the same window, the DPDP Rules 2025 phased commencement was producing operative obligations on the verifiable-parental-consent mechanism (Maruti had a small but growing minor-customer base on the wellness platform), the Consent Manager registration ecosystem was emerging, and a peer D2C brand received a DPBI preliminary inquiry on a consent-quality complaint that surfaced in trade media. Maruti had no Register entry for any of these, the regulator-engagement scan was absent; the principal-expectation scan was absent.
The remediation stood up the full programme: the Steering Group was chartered with the chief executive as the sponsor; the DPO as the chair; the standing members were named; the twelve-dimension Roadmap was drafted; the retro-load produced 47 Register entries across all ten source families; the first cycle commissioned five improvements; the first closeout with effectiveness verification was completed before the Q1 2029 surveillance audit.
The lessons: a continual-improvement programme is not a relabelling of the corrective-action tracker; the demarcation between reactive and proactive is the load-bearing 10.1 design decision; the DPDP Rules 2025 phased commencement produces operative obligations that demand a continuous programme, not a one-off compliance project; the SDF trajectory (Maruti was approaching the section 10 thresholds on volume) made the maturation sub-portfolio an urgent addition; the enterprise-customer privacy audit treated the 10.1 evidence as a contract-renewal factor.
Illustrative Scenario 2: Success, Agni FinTech Builds the Maturity-Advancement Loop (Illustrative)
Illustrative scenario. Agni FinTech is a fictional Bengaluru-based digital-lending platform with 1,100 staff, 6 offices, approximately 4.8 million borrower accounts, and an SDF designation under DPDP section 10 (confirmed in Q1 2028); the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation. It is set after 13 May 2027, when the DPDP Act's duties take effect.
Agni FinTech ran a mature ISO/IEC 27001:2022 ISMS programme with a strong ISMS Clause 10.1 improvement culture (the ISMS improvement programme was L4-equivalent on the infosec side). The PIMS Clause 10.1 programme was thinner, the privacy improvement portfolio was folded into the ISMS programme as a tag; the twelve privacy dimensions were not framed; the SDF section 10 maturation sub-portfolio was absent; the algorithmic-software review on the credit-scoring engine and the fraud-detection engine was periodic, not on a maturity trajectory.
In Q4 2027 the DPO commissioned a 10.1 refresh ahead of the 27701:2025 transition and the SDF designation analysis. The framing workshop surfaced six material shifts: (1) the Steering Group was re-chartered with the chief executive as the sponsor; the DPO as the chair; the Audit Committee as the board-engagement body (for the SDF overlay); the cadence was fixed at quarterly for the operational Steering Group and semi-annual for the board overlay; (2) the twelve-dimension Roadmap was built from scratch, with the L1-to-L5 trajectory per dimension; the maturity-floor was Diagnosed at L2 (consent and rights dimensions were L2; the SDF overlay was L1; the privacy technology was L2; the culture was L3); the target was L4 across all dimensions by the end of year three; (3) the SDF section 10 maturation sub-portfolio was stood up, the DPO function maturation (a four-FTE privacy team with the India-based DPO accountable to the board), the SDF DPIA cadence (every 12 months, with each new lending product assessed at launch), the first independent-data-audit cycle commissioned for Q1 2028 (5 nonconformities and 11 observations; the closeout programme ran to 100 percent within 90 days), the algorithmic-software review matured from periodic to continuous on the credit-scoring engine (the disparate-impact metric monitored monthly); (4) the PET adoption was commissioned, differential privacy for the aggregate analytics environment; synthetic data for the test-and-development environment; tokenisation for the cross-border analytics; the adoption ran to L3 by year two; (5) the Consent Manager integration was scoped against the regime in force since 13 November 2026; (6) the DPBI-feedback loop was stood up, the Head of Legal monitors the DPBI orders weekly; the material peer-finding produces a Register entry within seven days.
The avoided costs were substantial, the first cycle's regulator-engagement scan surfaced a DPBI preliminary inquiry pattern against peer digital-lending platforms on the consent-bundle design that would have produced a section 8(6) exposure if untreated; the corrective-and-improvement response (the consent-bundle redesign, the Consent Manager integration scoping, the principal-side consent dashboard design) removed the penalty exposure; the algorithmic-fairness maturity advancement on the credit-scoring engine removed the section 10 exposure; the PET adoption on the analytics environment enabled three enterprise-customer contracts (the differential-privacy layer was a customer requirement) worth approximately 14 crore rupees in annualised revenue; the maturity-advancement evidence supported the 27701:2025 transition audit with zero 10.1 findings.
The lessons: the twelve-dimension Roadmap is the highest-use 10.1 move for most Indian growing companies; the SDF maturation sub-portfolio is the regulatory hedge for organisations operating above the section 10 thresholds; the PET adoption is the commercial lever in the enterprise segment; the DPBI-feedback loop is the regulatory hedge that has no analogue in the GDPR ecosystem; the algorithmic-AI fairness maturity advancement is the marquee SDF-specific 10.1 outcome.
Multi-Framework Mapping
| 27701:2025 10.1 theme | GDPR article | DPDP Act (India) section | NIST Privacy Framework | SOC 2 TSC + Common Criteria | ISO 27001 / 27002 / siblings | Companies Act / SEBI LODR |
|---|---|---|---|---|---|---|
| Continual improvement (10.1 umbrella) | Art 24(1) "ongoing basis"; Art 24(2); Art 5(2) | s.8 general obligations; s.10 SDF (multi-year maturation) | Govern-P (Risk Management Strategy; Monitoring and Review) | CC4.1 / CC4.2 (Monitoring); CC5.2 / CC5.3 (Change mgmt); P8.0 | 27001 Clause 10.1 (infosec twin); 31000 Clause 6; 27002 5.36 | Companies Act 2013 s.134(3)(n); s.177; SEBI LODR Reg. 21 (RMC) |
| The 9.1 trend-pattern input | Art 32(1)(d) "regular testing, assessing, evaluating" | s.8(5) safeguards | Govern-P (Monitoring and Review) | CC4; P8.0 | 27001 Clause 9.1; 27002 5.34 | (implicit, risk framework) |
| The 9.2 audit-observation input | Art 32(1)(d); Art 29 | s.8; s.10 SDF audit | Govern-P | CC4; P8.0 | 27001 Clause 9.2; 27002 5.35 | (Audit Committee remit under s.177) |
| The 9.3 management-review-output input | Art 24(2) | s.10 SDF (DPO board accountability) | Govern-P (Governance Structure) | CC1; P8.0 | 27001 Clause 9.3 | (board-reporting overlay) |
| The 10.2 corrective-action-lesson input | Art 5(2); Art 24(2) | s.33 + Schedule | Govern-P | CC4; CC8 | 27001 Clause 10.2 | (Audit Committee follow-up) |
| Consent-quality dimension advancement | Art 7; Art 7(3) withdrawal | s.6 (seven qualities); s.2(1)(g) Consent Manager | Control-P; Communicate-P | P2.0 | 27002 5.34; ISO/IEC 29100 | (implicit) |
| Rights-fulfilment dimension advancement | Arts 12 to 22 | ss.11 to 14; s.13 grievance | Communicate-P | P5.0; P6.0 | 27002 5.34 | (board-oversight of complaints) |
| DPIA-pipeline dimension advancement | Art 35; Art 35(11) review; Art 36 | s.10 SDF (DPIA) | Identify-P; Govern-P | P8.0 | ISO/IEC 29134:2017; 27001 Clause 8.2 | (implicit) |
| Processor-chain dimension advancement | Art 28; Art 28(3)(h); Art 33(2) | s.8 (Fiduciary accountability for processor) | Control-P (DUA); Govern-P | CC9.2; P6.0 | 27002 5.19 to 5.23; 27018:2019 | (risk framework) |
| Transfer dimension advancement | Chapter V; Schrems II TIA; SCCs 2021/914; EU-US DPF 10 Jul 2023 | s.16 cross-border negative list | Control-P | P6.0 | 27017:2015 | (implicit) |
| Breach dimension advancement | Arts 33 to 34 | s.8(6) (without delay to Board; detailed report within 72 hours); CERT-In 6h; sector clocks | Protect-P (recovery) | CC7.3; CC7.4; P6.0 | 27002 5.24 to 5.27 | (board-reporting overlay) |
| Privacy-by-design dimension advancement | Art 25 | s.2(1)(g); s.9 children design | Control-P; Protect-P | P4.0 | 27002 5.34; ISO/IEC 27557 | (implicit) |
| Children-data dimension advancement | Art 8 | s.9 (verifiable parental consent; no behavioural monitoring) | Control-P | P2.0 | 27002 5.34 | (implicit) |
| SDF section 10 maturation dimension | (no direct EU-analogue) | s.10 SDF (DPO, SDF DPIA, independent data audit, algorithmic-software review) | Govern-P | CC1.3; CC1.5 | 42001:2023 Clause 10.1 | Companies Act 2013 s.134(3)(n); s.177; SEBI LODR Reg. 21 |
| PET adoption dimension | Art 25; Art 32(1)(a) pseudonymisation | s.8(5) safeguards | Control-P; Protect-P | (implicit in CC7) | ISO/IEC 27557 | (implicit) |
| Algorithmic-software dimension | Art 22; Art 22(4) | s.10 SDF (algorithmic-software review) | Govern-P | CC1.1 | 42001:2023 Clause 10.1 | (board-oversight of AI fairness) |
The densest cross-framework mappings are at the continual-improvement umbrella row (GDPR Art 24 / DPDP s.8 + s.10 / NIST Govern-P / SOC 2 CC4 + CC5 + P8 / ISO 27001 Clause 10.1 / Companies Act 134(3)(n) + s.177), the consent-quality row (GDPR Art 7 / DPDP s.6 + s.2(1)(g) / NIST Control-P + Communicate-P / SOC 2 P2 / ISO 29100 consent-and-choice principle), and the SDF section 10 maturation row (DPDP s.10 / SOC 2 CC1.3 + CC1.5 / 42001 Clause 10.1 / Companies Act 134(3)(n) + s.177 + SEBI LODR Reg. 21). The unique-to-India row is the DPBI-feedback loop, no other jurisdiction matches the DPDP section 10 SDF board-DPO accountability with the DPBI enforcement-feedback loop driving the regulator-driven improvement stream.
Implementation Roadmap
30 days
- Convene the continual-improvement framing workshop (the chief executive or designate, the DPO, the CISO, the Head of Legal, the Head of Internal Audit, the top three business-process owners, the Company Secretary for the board-governance linkage).
- Draft the PIMS Continual Improvement Policy (toolkit doc 01). Confirm the Steering Group, the cadence, the artefact set, the eight-step discipline, the twelve-dimension Roadmap, the DPDP-driven drivers.
- Issue the Policy for top-management sign-off. Archive per Clause 7.5.
- Stand up the Improvement Opportunities Register (toolkit doc 03). Retro-load the improvement candidates from the last twelve months of sources.
- Stand up the Prioritisation Matrix (toolkit doc 04) with the five-dimension rubric and the default weights.
90 days
- Run the first Steering Group cycle. Score the retro-loaded entries; commission the top three to five improvements; defer the rest with the rationale.
- Stand up the Action Tracker (toolkit doc 05). Enter the commissioned improvements; assign the owners; set the due dates.
- Stand up the Maturity Advancement Roadmap (toolkit doc 06) with the twelve dimensions; diagnose the current L-level per dimension; set the target trajectory.
- Stand up the Lessons-Learned Log (toolkit doc 07) with the structured capture template.
- Begin the eight-step discipline on the first commissioned improvements. Plan documented; implementation underway.
- For SDFs (and for organisations approaching the SDF thresholds), stand up the SDF section 10 maturation sub-portfolio.
180 days
- Complete the first wave of commissioned improvements. Run the effectiveness-verification at 30, 60 and 90 days post-implementation.
- Run the second Steering Group cycle. Score the new entries; commission the next three to five improvements; review the closeout trajectory.
- Refresh the Roadmap trajectory. Reconcile the actual advancement with the planned advancement.
- Run the first internal-audit (Clause 9.2) test of the 10.1 discipline. The Internal Auditor tests the Register, the Matrix, the Tracker, the Roadmap, the Log, the demarcation, the eight-step discipline on a sample.
- For SDFs, complete the first independent-data-audit cycle (under DPDP section 10); wire the findings into the Register.
- Calibrate the programme against the first cycle's experience. Refresh the Policy if material changes are needed.
12 months
- Run the third and the fourth Steering Group cycles. Report the full year's closeout rate, the effectiveness-verification rate, the sustainment rate, the maturity-floor advancement.
- Calibrate the twelve dimensions against the year's experience. Refresh the Roadmap.
- Reassess the SDF designation analysis in light of the data-volume growth.
- For SDFs, run the second independent-data-audit cycle; the second algorithmic-software review; the second board engagement cycle (the Companies Act / SEBI LODR overlay).
- Run the certification-audit readiness check: the Register, the Matrix, the Tracker, the Roadmap, the Log, the SDF overlay, the integrated-with-distinction posture, the certification-cycle alignment.
- Refresh the DPDP-Rules phased-commencement tracker. Confirm the operative-obligation response for the next-phase commencement dates.
FAQ
Q1. Our Clause 10.2 corrective-action tracker is well-populated. Can we re-label it as the 10.1 Register?
No, the demarcation between 10.2 and 10.1 is load-bearing. The 10.2 corrective actions react to detected nonconformities; the 10.1 improvements proactively raise the bar on a PIMS that already conforms. Re-labelling the corrective-action tracker as the 10.1 Register is the most common 10.1 audit finding in the Indian growing-company segment. Stand up a separate Register with the ten source families and the eight-step discipline.
Q2. We do not have time to run a quarterly Steering Group. Can we run it annually?
Annually is below the Singahi minimum cadence (quarterly). The certification auditor will challenge an annual programme as "not continual", the continual-improvement discipline is the operational test of Clause 5.1 leadership commitment. For an early-cycle organisation, monthly may be more appropriate than quarterly; for a mature organisation, quarterly is the default. Annual Steering Group plus monthly DPO-function triage is a defensible compromise for very small organisations.
Q3. Our CEO is sceptical of "privacy programme advancement", she sees it as overhead. How do we frame it?
Frame it in three rupee-denominated bands. (a) The regulatory hedge, the DPDP Schedule maxima attach to operational failures that the maturity advancement prevents; a single avoided section 8(6) penalty at the lower end of the section 33 range funds the programme for several years. (b) The commercial lever, the enterprise-customer privacy audit treats the 10.1 evidence as a contract-renewal factor; the PET adoption unlocks the high-stakes contracts.
Q4. Our Internal Audit team tested the 10.1 discipline under Clause 9.2 and found the Register incomplete. Can the Internal Auditor help the DPO compile the Register?
No, the 9.2 / 10.1 independence requires that the Internal Auditor does not operate the 10.1 programme. The Internal Auditor tests; the DPO function compiles. If the Register is incomplete, the Internal Audit finding routes through Clause 10.2 corrective action; the DPO function remediates; the Internal Auditor verifies the closeout.
Q5. How is 10.1 different from 9.3 management review?
9.3 is the top-management decision forum that directs the improvement outputs; 10.1 is the operational programme that runs on those outputs. The 9.3 input set includes the trend patterns and the audit observations; the 9.3 output routes the improvement opportunities to 10.1; the 10.1 programme captures the opportunities in the Register, prioritises them on the Matrix, commissions them on the Tracker, implements them with the eight-step discipline, verifies the effectiveness, sustains the gains, advances the maturity floor, and feeds the lessons back into the 9.3 input set as the maturity-advancement report. The two are sequential and complementary.
Q6. We are an SDF under DPDP section 10. What does the 10.1 programme need to do that a non-SDF programme does not?
The SDF section 10 maturation sub-portfolio: the DPO function maturation; the SDF DPIA cadence; the independent-data-audit closeout; the algorithmic-software review; the board-reporting pack delivery on the SEBI LODR cycle (for listed entities) or the board-meeting cycle (for unlisted SDFs). The DPO is statutorily accountable to the board; the 10.1 programme is the operational mechanism by which the SDF section 10 obligations mature on a multi-year curve.
Q7. We are a processor for overseas customers. Does the twelve-dimension portfolio apply to us?
Yes, with the processor-side load. The consent family is replaced by the instruction-handling family; the rights family is the cooperation-with-the-controller family; the DPIA family cooperates with the controller's DPIAs; the processor-chain family is the sub-processor-management family; the breach family is the breach-notification-to-controller clock family. Your improvement portfolio derives from the customer DPAs and from Annex A.2.
Q8. Our Maturity Advancement Roadmap shows zero dimension advancement in the last cycle. What should we do?
Treat it as a 10.1 KPI deviation. Three layers: (a) the root-cause analysis, were the commissioned improvements under-resourced, under-owned, under-tracked, or genuinely time-consuming? (b) the portfolio review, was the Matrix rubric correctly applied, or was the portfolio biased to the low-effort / low-impact improvements? (c) the maturity-floor check, if the floor dimension did not advance, the structural-improvement pipeline is under-powered; the Steering Group commissions a structural improvement on the floor dimension for the next cycle.
Q9. Our effectiveness-verification rate is 100 percent but the maturity floor is not advancing. How can that be?
The effectiveness check is probably perfunctory, the verifier is the implementer's colleague; the check is a tick-box; the KPI trend is not examined. The 10.1 KPI cascade is: source-coverage breadth → Register entry count → Matrix rubric application → commissioning → closeout → effectiveness verification → sustainment → maturity-floor advancement. The cascade must be walked end-to-end; a break at any link produces a 100 percent effectiveness rate with zero maturity advancement. The Internal Audit function (under 9.2) tests the cascade; the certification auditor walks it.
Q10. Our DPDP-Rules commencement tracker shows we have not produced Register entries for the last two phases. What is the risk?
Major nonconformity risk under Clause 10.1 (the regulatory-blindness failure) and under Clause 4.2 / 4.4 (the interested-party expectations and the PIMS not refreshed). The DPDP Rules 2025 phased commencement is itself a stream of improvement-trigger events; the programme must absorb each phase on the commencement timeline. The Head of Legal owns the commencement tracker; the DPO function owns the Register entries produced per phase.
Q11. We have a Privacy Engineering team that adopts PETs organically. Does that count as the 10.1 programme?
Partially, the PET adoption is one of the twelve dimensions (Dimension 12). But the twelve dimensions are interdependent; a programme that advances Dimension 12 alone is not a 10.1-conformant programme. Stand up the Steering Group; build the Roadmap across all twelve dimensions; commission the dimension-level improvements with the eight-step discipline.
Q12. Our 10.1 programme and our 9.3 management review run on different cadences. Is that conformant?
Yes, with discipline. The 9.3 management review is annual or semi-annual; the 10.1 Steering Group is quarterly. The two are reconciled at the annual cycle, the 10.1 programme produces the maturity-advancement report that is the 9.3 input; the 9.3 management review produces the improvement-output routing that is the 10.1 input. The two cadences are complementary, not duplicative.
Q13. Our board does not engage with the maturity-advancement trajectory. Is that a 10.1 finding?
For an SDF or a listed entity, yes, the board-engagement overlay under the Companies Act 134(3)(n) / section 177 / SEBI LODR Reg. 21 is the load-bearing Indian governance construct. The board reporting pack (delivered on the SEBI LODR cycle for listed entities, or the board-meeting cycle for unlisted SDFs) is the operational vehicle by which the board discharges its oversight duty. For a non-SDF unlisted entity, the executive-committee engagement is sufficient.
Industry-Specific Requirements
BFSI
Banks, NBFCs, payment aggregators, payment gateways, insurers. The twelve dimensions carry the heaviest regulatory load: the DPDP section 8(5) safeguards, section 8(6) breach notification (intimation without delay and a seventy-two-hour report), section 10 SDF obligations (most large BFSI players are likely SDFs); the RBI Storage of Payment System Data directive (6 April 2018), payment-system data stored end-to-end in India; the RBI Digital Lending Guidelines (2 September 2022), borrower consent, device-data minimisation; the RBI Cybersecurity Directions 2026 (31 July 2026); the RBI CICRA Master Direction for credit-information handling; the SEBI CSCRF (20 August 2024); the IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023). The 10.1 programme must advance the triple-clock pattern (CERT-In six hours, DPDP without delay plus a seventy-two-hour detailed report, RBI and SEBI six hours, IRDAI per its own guidelines) per actual event and per drill in Dimension 7; the algorithmic-fairness metric in Dimensions 8 and 10 for credit-scoring, fraud-detection and collections engines; the Payment Aggregator / Payment Gateway / card-network / core-banking / CRM / analytics / cloud provider chain in Dimension 5. The board-governance overlay is mandatory (most BFSI entities are listed or SDFs); the board reporting pack is delivered to the Audit Committee and the Risk Management Committee on the SEBI LODR cycle.
Healthcare
Hospitals, telemedicine platforms, healthtech, insurers processing health data. The programme must flag the heightened sensitivity of health data (the DPDP section 9 analog for vulnerable data subjects; the SPDI Rules' explicit inclusion of health data; clinical-data-confidentiality expectations; the IRDAI framework where insurance is involved). The DPIA-coverage KPI threshold is low, most material processing activities require DPIA treatment; the DPIA-pipeline dimension (Dimension 4) is load-bearing. The breach family (Dimension 7) carries the dual-clock pattern plus the IRDAI clock for insurers. The consent family (Dimension 1) must measure the Consent Manager integration for patient-facing services; the rights family (Dimension 3) must measure the access-to-medical-records turnaround. The algorithmic-fairness metric in Dimensions 8 and 10 is critical for AI-driven diagnostic engines, the AI-driven chronic-care management engines, the AI-driven triage engines. The board-governance overlay applies for listed hospital chains and health insurers.
IT-ITeS and SaaS
IT services firms, BPOs, SaaS providers, cloud processors. The twelve dimensions are almost always "both", the customer's principals reached through the organisation's processing (processor-side risks), and the organisation's own employees, marketing-lead contacts and beta-test users (controller-side risks). The cross-border transfer dimension (Dimension 6) is central; the standalone-PIMS scoping decision lets SaaS firms scope a PIMS to the customer-data plane only. The sub-processor change-notification adherence KPI is the load-bearing Dimension 5 control (cloud SaaS firms often run hundreds of sub-processors). The infringing-instruction drill cadence KPI is exercised more frequently than in other sectors. The breach-notification-to-controller clock KPI (typically twenty-four to seventy-two hours in the customer DPA) is the processor-side analogue of the dual-clock in Dimension 7. The customer-feedback source family is particularly load-bearing, the enterprise-customer privacy audits are frequent and detailed.
E-commerce and Retail
D2C brands, marketplaces, e-commerce platforms, omni-channel retailers. The programme must address consumer-privacy expectations at scale, the children's-data regime where minors are in the user base, the marketing-lead consent regime, the supplier-ecosystem processor chains, the payment-data overlays (RBI Tokenisation, the Payment Aggregator obligations). The Consent Manager integration KPI is particularly relevant in Dimension 1; the consent-quality KPI is a frequent finding. The breach family (Dimension 7) must handle large-scale consumer notifications, often in multiple languages, the principal-notification-dispatch latency KPI is the load-bearing sub-KPI. The grievance Dimension 3 component is high-volume for consumer-facing brands; the Grievance Officer SLA adherence is operationally tested.
Edtech
K-12 platforms, higher-edtech, skilling platforms, test-prep. The children's-data regime (DPDP section 9) is the central operational issue, the principal is a minor, the consent dynamic is parental, the section 9 verifiable-parental-consent plus no-behavioural-monitoring-or-targeted-advertising regime is load-bearing. The Dimension 9 (children-data controls) is the marquee improvement surface: the verifiable-parental-consent rate and the no-behavioural-monitoring enforcement. The DPIA-coverage threshold is low; the DPIA-cadence (Dimension 4) is a critical input. The breach family for children's data is high-sensitivity, the section 9 penalty exposure (up to two hundred crore) demands a particularly rigorous improvement programme.
Manufacturing
Discrete and process manufacturing, automotive, chemicals, pharma manufacturing. The programme must address the OT-IT convergence (operational technology systems increasingly connected, with PII exposure in HR, contractor and visitor data), the supply-chain processor ecosystem, the geopolitical context for cross-border manufacturing data flows. The principal set includes employees, contractors, visitors, customers (where D2C), and patients (for pharma manufacturing with patient-level pharmacovigilance data). The Dimension 5 processor-chain typically includes the ERP / MES / SCADA / CRM / HR / cloud providers; the OT-IT convergence increases the Dimension 12 (privacy technology) density. The breach Dimension 7 must address the operational-technology angle (the OT breach can have physical-safety consequences, not just data consequences).
Cross-sector patterns
Three patterns recur across sectors and are worth flagging in any 10.1 architecture regardless of industry.
The SDF-designation trajectory. Indian ITeS, BPO, SaaS, BFSI and healthcare firms typically process personal data at volumes that easily cross the DPDP SDF thresholds. The SDF-designation analysis must be on the annual Roadmap trajectory; the SDF maturation sub-portfolio must be in the programme even if the consumer brand is small.
The dual-regulator pattern. BFSI and listed entities carry dual-regulator exposure, DPDP via the Data Protection Board plus the sector regulator (RBI, SEBI, IRDAI). The Dimension 7 breach family must capture both regulatory streams and the dual-clock / triple-clock pattern they create; the regulator-engagement source family must monitor both streams.
The board-governance overlay pattern. For listed entities, the SEBI LODR Regulation 21 Risk Management Committee is the canonical board-engagement body; for unlisted SDFs, the board reporting pack under the Companies Act 134(3)(n) / section 177 overlay is the board-engagement instrument. The two patterns converge on the same discipline, the 10.1 programme must produce a board-grade maturity-advancement output for the Audit Committee / Risk Management Committee / board consumption.
Maturity Model
Figure · Tiers
Maturity levels for continual improvement
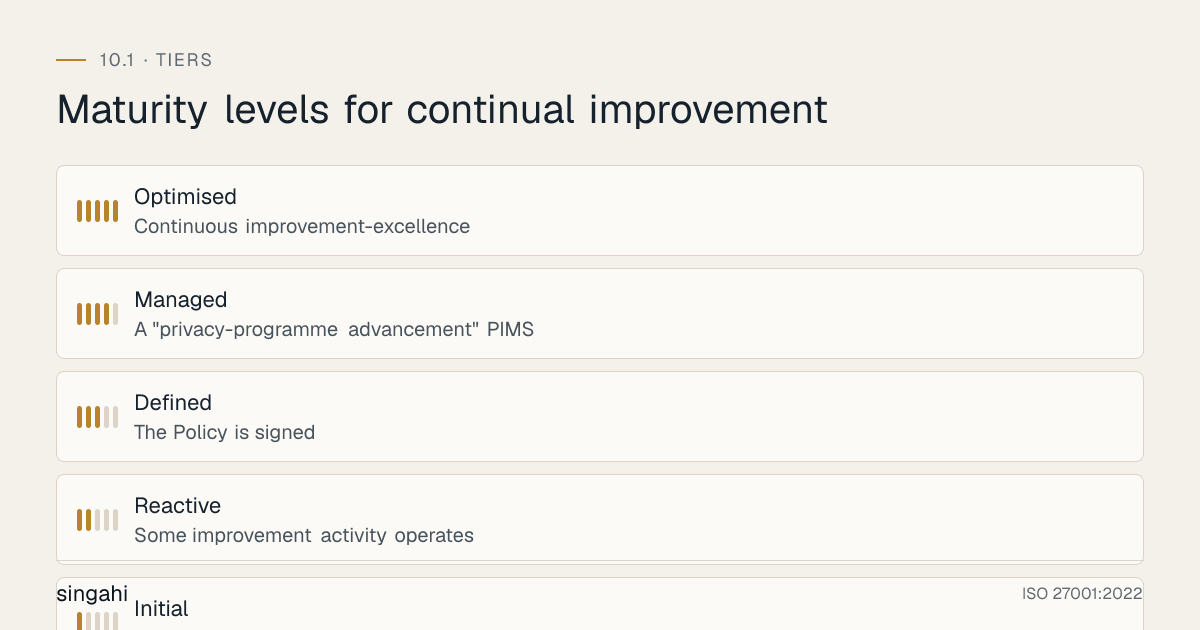
| Level | Description |
|---|---|
| L1, Initial | A "we re-certified, what is there to improve?" programme: the PIMS passed Stage 2; the team moved on to operational firefighting; no Register exists; no Matrix exists; no Tracker exists; no Roadmap; no Log; the maturity is the certification-baseline maturity and is decaying against the moving context. The single most common Clause 10.1 audit nonconformity in the Indian growing-company segment. |
| L2, Reactive | Some improvement activity operates but it is reactive, the programme absorbs the 10.2 corrective actions, the customer-audit findings, the regulator directions; the Steering Group meets irregularly; the Matrix is partial; the Tracker is partial; the closeout rate is not tracked; the maturity floor does not advance. The Internal Audit (9.2) tests the discipline and finds gaps. |
| L3, Defined | The Policy is signed; the Steering Group meets quarterly; the Register is populated with entries from all ten source families; the Matrix is applied; the Action Tracker routes every commissioned improvement; the closeout rate is tracked; the Roadmap is drafted across the twelve dimensions; the Log is in use; the SDF maturation sub-portfolio is in design. The integrated-with-distinction posture is evidenced for ISMS organisations. |
| L4, Managed | A "privacy-programme advancement" PIMS: every commissioned improvement runs the eight-step discipline with the effectiveness verification independent of the implementer; the closeout rate is at 100 percent or trending toward it; the recurring-overdue pattern is escalated; the maturity-floor advancement is tracked and reported to top management at the 9.3 review; the SDF maturation sub-portfolio is operational (for SDFs); the board reporting pack is delivered on the SEBI LODR cycle (for listed entities); the Internal Audit's 9.2 test of 10.1 has zero major findings. Cross-framework reconciliation (DPDP / GDPR / NIST / SOC 2 / ISO 27001 / 27002 / 27018 / 27017 / 29100 / 29134 / 31000 / 42001 / Companies Act / SEBI LODR). The PET adoption is on the roadmap; the algorithmic-software review is on a maturation trajectory. |
| L5, Optimised | Continuous improvement-excellence capability. The programme is wired into the operational cadence (the monthly source-scan, the quarterly Steering Group, the semi-annual Roadmap refresh, the annual board reporting). The Maturity Advancement Roadmap is the single source of truth for the Audit Committee / Risk Management Committee / board. The twelve-dimension trajectory is the board-reportable narrative. The lessons-learned Log is consumed by the board, the regulators (on request), and the enterprise customers (under NDA) as the cumulative intelligence. The 10.1 outputs demonstrably drive every downstream clause and are the spine of the PIMS forward motion. For SDFs, the DPO is statutorily accountable to the board and the maturation sub-portfolio is fully operational. The Audit Committee tests a sample of improvements every cycle. The PET adoption is continuous; the algorithmic-software review is continuous; the cross-border-transfer monitoring is continuous. |
Emerging Trends
DPBI operational emergence and the enforcement-feedback loop. The Data Protection Board of India (under DPDP section 18) is emerging through 2026 and 2027. Its early orders, its interpretation of the Schedule penalty maxima, its engagement patterns on DPIA consultations, its precedent on the breach-notification clock, and its operational portal for section 8(6) notifications will reshape the regulator-engagement source family. The DPBI-feedback stream is a default 10.1 input for every Indian Data Fiduciary; the Head of Legal monitors the orders weekly; the material peer-finding produces a Register entry within seven days. The board reporting pack must add the DPBI-engagement summary as the Board's enforcement activity scales.
SDF designations and the section 10 maturation sub-portfolio. The first SDF designations are expected through 2026 and 2027 as the DPDP Rules phased commencement completes; designated SDFs must operationalise the independent-data-audit / SDF DPIA / algorithmic-software review cadence under section 10. The SDF maturation sub-portfolio becomes the default Dimension 10 programme; the board-DPO accountability under section 10 is the load-bearing Indian governance construct.
Consent Manager ecosystem emergence. The DPDP Rules 2025 prescribe Consent Manager registration conditions; the first Consent Managers are expected to be registered through 2026 and 2027. The Consent Manager integration metric (the share of consent signals correctly received, honoured and reconciled) becomes a default Dimension 1 KPI for consumer-facing Data Fiduciaries as the ecosystem emerges. The improvement programme must surface the Consent Manager integration as a commissioned improvement ahead of the operational-dependency window.
AI-driven processing and the algorithmic-fairness maturity advancement. The Rule 13(3) algorithmic-software review, the parallel development of ISO/IEC 42001:2023 (AI Management System), and the growing customer and regulator focus on AI-driven processing are reshaping Dimensions 8, 10 and 12. The use of generative AI inside the privacy function itself (ROPA automation, DPIA drafting, rights-request triage, breach-notification drafting, Register compilation) is a 10.1 risk in its own right, the programme must consider the generative-AI-specific risks (training-data leakage, prompt-injection-driven disclosure, model hallucination) and the integrity of AI-generated improvement inputs.
Privacy-enhancing technologies (PETs), the maturation frontier. The differential-privacy adoption for the aggregate analytics; the SMPC and HE adoption for the cross-organisation analytics; the federated-learning adoption for the AI model training; the synthetic-data adoption for the test-and-development data, each PET class is maturing from research to operational. The PET adoption is the marquee Dimension 12 advancement; the high-effort / high-impact improvements (the PET adoption) must not be perpetually deferred by the portfolio-bias failure.
Integrated management systems. The harmonized structure enables integrated 27001 + 27701 + 42001 + 22301 governance. The Clause 10.1 programme is the natural point of integration, a single combined Steering Group, a single combined Register with the system labels, a single combined Roadmap. The integrated-with-distinction posture from Clause 6.1 carries through to 10.1.
Cross-border transfer regime evolution. The DPDP negative list under section 16, the EU-US Data Privacy Framework adequacy decision (10 July 2023), the UK IDTA / Addendum, the China PIPL cross-border mechanisms, and the geopolitical risk environment are all in flux. The Dimension 6 advancement is the load-bearing transfer-regime improvement; the multi-jurisdiction processor-portfolio Dimension 5 decisions are operationally tested every cycle.
Sector-regulator convergence. RBI, SEBI and IRDAI are each tightening their privacy-adjacent rules (RBI Digital Lending; SEBI CSCRF; IRDAI ICS 2023). The DPDP Act sits as a horizontal layer above these sectoral instruments; the regulator-engagement source family must monitor both streams. The triple-clock Dimension 7 pattern becomes the default for BFSI.
Privacy as a board-level discipline. The 10.1 board reporting pack is increasingly the board's instrument for privacy oversight, the Audit Committee / Risk Management Committee / the board receives the Pack on the SEBI LODR cadence. The maturity-advancement trajectory is the board-reportable narrative. The maturity target for Indian growing companies is the L4 Pack consumed by the board on the quarterly cadence.
The continuous-compliance frontier. The maturity-advancement loop is converging with the continuous-compliance-monitoring frontier, the policy-as-code; the privacy-tests-in-CI/CD; the ROPA-from-source-system discovery; the breach-detection via the SOAR platform; the algorithmic-fairness metric in the model-monitoring stack. The L5 organisation runs the privacy programme as a continuous data-and-automation discipline, not as a quarterly-cycle manual programme. The Indian growing-company segment is two to four years behind the frontier; the 10.1 programme is the operational vehicle by which the gap closes.
References and Further Reading
Primary instruments (India). DPDP Act 2023 (Act 22/2023, enacted 11 August 2023), MeitY, sections 4 to 10 (obligations), 11 to 14 (rights), 16 (cross-border negative list), 18 (DPBI), 33 plus Schedule (penalty maxima). DPDP Rules 2025 (notified 13 November 2025), Rule 7; phased commencement through approximately 2027. Information Technology Act, 2000 (sections 43A, 72A, 70B); IT (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011. CERT-In Directions 20(3)/2022-CERT-In (28 April 2022). Companies Act 2013, section 134(3)(n); section 177. SEBI LODR Regulation 21. RBI Storage of Payment System Data (6 April 2018); RBI Digital Lending Guidelines (2 September 2022); RBI Tokenisation (22 September 2021); RBI Cybersecurity Directions 2026 (31 July 2026). SEBI CSCRF (20 August 2024). IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023).
Primary jurisprudence (India). K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (nine-judge Bench, 24 August 2017). Justice K.S. Puttaswamy (Retd.) v. Union of India (Aadhaar), (2019) 1 SCC 1 (five-judge Bench, 26 September 2018).
Primary instruments (global). Regulation (EU) 2016/679 (GDPR), OJ L 119, 4.5.2016, p. 1; application from 25 May 2018, Article 5(2) accountability; Article 24(1) "ongoing basis"; Article 24(2) review and update; Article 25 data protection by design and by default; Article 32(1)(a) pseudonymisation; Article 32(1)(d) "regular testing, assessing and evaluating the effectiveness"; Article 35(11) DPIA review; Article 36 prior consultation. European Commission Implementing Decision (EU) 2021/914 (modernised SCCs, 4 June 2021). EU-US Data Privacy Framework adequacy decision (10 July 2023). Schrems II, CJEU C-311/18 (16 July 2020). EDPB Recommendations 01/2020 on supplementary measures. EDPB Guidelines 9/2022 on personal data breach notification. NIST Privacy Framework v1.0, NIST.CSWP.01162020, 16 January 2020, Govern-P (Risk Management Strategy; Monitoring and Review); Identify-P; Control-P; Communicate-P; Protect-P. AICPA, 2017 Trust Services Criteria (with 2022 Points of Focus update), CC4.1 / CC4.2 (Monitoring); CC5.2 / CC5.3 (Change management); CC7.3, CC7.4 (Incident Response and Recovery); CC9.2 (Vendor Risk); P8.0 (Monitoring for Compliance). Brazil LGPD, Lei no 13.709/2018. China PIPL, Article 38 (cross-border mechanisms), Article 55 (mandatory PIA).
ISO/IEC standards. ISO/IEC 27701:2025 (2nd ed., published 14 October 2025), Clause 10.1, Clause 9.1 / 9.2 / 9.3 (the input set), Clause 10.2 (corrective-action lessons), Clause 6.1 / 6.3 (planning), Annex A.1 / A.2 / A.3 (the controls whose maturity 10.1 advances), Annex B (normative in 2025, implementation guidance). ISO/IEC 27701:2019 (1st ed., transition reference, Annex F guidance, informative). ISO/IEC 27001:2022 Clause 10.1 (infosec structural twin). ISO/IEC 27002:2022, only 5.34 is PII-specific; 5.35 / 5.36 / 5.37 are general security. ISO/IEC 27018:2019 (cloud PII processor); ISO/IEC 27017:2015 (cloud security); ISO/IEC 29100:2011 (privacy framework, 11 principles); ISO/IEC 29134:2017 (DPIA guidelines); ISO/IEC 27557 (privacy impact assessment criteria); ISO 31000:2018 (risk management, Clause 6 Monitoring and Review); ISO/IEC 42001:2023 (AI Management System, Clause 10.1 alignment); ISO/IEC 27706:2025 (PIMS cert-scheme competence).
Edition-transition sources. ANAB Heads Up 550 (transition timeline, certification-body deadline 31 October 2026; organisation transition deadline 31 October 2028). The 2025 edition's structure, the harmonized-structure Clause 10.1 alignment, the Annex A.1 / A.2 / A.3 consolidation, the normative-Annex-B change, and the continual-improvement emphasis are confirmed from the official 2025 PDF (OCR) and corroborated by tier-1 cert-body practitioner commentary. The common-nonconformity patterns (the missing programme; the empty Register; the demarcation failure; the closeout-without-effectiveness; the no-Roadmap; the no-Log; the DPDP-blindness; the SDF-overlay-absent) are drawn from tier-1 cert-body practitioner commentary. All clause text in this guide is paraphrased; the official text is copyrighted by ISO/IEC and has not been reproduced.
Singahi references. The Singahi Clause 10.1 toolkit (17 docs plus README) accompanies this guide. The Singahi 27701:2025 series covers all MSS clauses (4 to 10) and Annex A.1 / A.2 / A.3 controls; sibling guides for 4.1, 4.2, 4.3, 4.4, 5.x, 6.x, 7.x, 8.x, 9.1, 9.2, 9.3, 10.2 and the Annex A controls are available.
This guide is published by Singahi. The ISO/IEC 27701:2025 clause text is copyrighted by ISO/IEC and has not been reproduced; all requirements are paraphrased. Brand names of competitors, cert bodies, and reference books are intentionally omitted. Scenarios are illustrative and should not be attributed to any real organisation.