
On this page
- Quick Reference (60 Seconds)
- What the Standard Actually Requires
- Why This Control Matters
- Scope and Applicability
- Key Definitions and Terminology
- Relationship to Other Clauses and Frameworks
- Detailed Implementation Guidance, The Six Operational Moves
- Tools, Technologies, and Solutions
- Policy and Procedure Templates
- Operational Risk Treatment and Effectiveness
- Audit and Compliance Checklist
- Metrics and KPIs
- Common Pitfalls and Audit Failures
- Illustrative Scenario 1: Failure, Public-Health Contact-Tracing Healthtech and the Future-State SoA Behind an Algorithmic Triage Engine (Illustrative)
- Illustrative Scenario 2: Success, Tarang Fintech Operationalises the 8.3 Treatment Loop (Illustrative)
- Multi-Framework Mapping
- Implementation Roadmap
- FAQ
- Industry-Specific Requirements
- Maturity Model
- Emerging Trends
- References and Further Reading
Quick Reference (60 Seconds)
| Attribute | Detail |
|---|---|
| Clause | ISO/IEC 27701:2025 Clause 8.3, Privacy Risk Treatment. The third sub-clause of the PIMS Operation block (Clause 8), structurally aligned to the Harmonized Structure shared by ISO/IEC 27001:2022 Clause 8.3 (information security risk treatment in operations) and the operational treatment-execution tradition of ISO/IEC 27005:2022 and ISO 31000:2018. Where 6.1.3 produces the planning-layer treatment decisions (the modify / retain / avoid / share option selected per material risk, the planning-layer Statement of Applicability that documents which Annex A controls are applicable and why, the planning-layer risk-treatment plan), 8.3 is the operational-layer execution, implementing that plan in the live PIMS environment, producing and maintaining the operational Statement of Applicability that documents the current-state implementation of every applicable Annex A.1 / A.2 / A.3 control with a defensible justification for every exclusion, accepting residual risk operationally through a signed record by the named risk owner, and evaluating the effectiveness of the treatment at planned intervals and on material change. 8.3 is where the planning architecture becomes a running system that controls are actually operating in, and where the certification auditor traces each control from the SoA row to the operational evidence. |
| What it asks for (paraphrase) | ISO/IEC 27701:2025 Clause 8.3 asks organizations to operationally execute the privacy risk treatment, implementing the treatment plan produced under 6.1.3, producing and maintaining the operational Statement of Applicability as a current-state artefact, accepting residual risk through a documented and signed record, and evaluating the effectiveness of the treatment. Five load-bearing ideas do the work. The organisation implements the treatment option selected under 6.1.3, modify (apply controls), retain (accept residual risk), avoid (terminate the processing activity), share (transfer part of the risk through insurance or contractual allocation), and produces operational evidence that the controls are actually in operation. The organisation produces and maintains the operational Statement of Applicability, a current-state, version-controlled document cross-walking every Annex A.1 (controller), A.2 (processor) and A.3 (security) control to its applicability status, its justification (which risk or which requirement it treats), its implementation state (current-state, evidenced, never future-state) and its documented exclusion reasoning where not applicable. The organisation accepts residual risk through a documented and signed record, every risk above the risk-acceptance threshold has a signed acceptance by the named risk owner, with the rationale, the conditions and the review date. The organisation evaluates the effectiveness of the treatment at planned intervals and on material change, for each treatment decision, did the residual-risk projection hold? Did the controls operate as designed? Did the DPIA conclusion remain valid? And the organisation maintains the operational residual-risk register that reconciles with the live Privacy Risk Register from 8.2 and drives the management-review input under Clause 9.3. |
| The marquee insight competitors miss | Three facts make 8.3 the most consequential operational sub-clause in the 2025 edition, and the one most practitioner commentary under-buys. First, the 6.1.3 (planning) versus 8.3 (operational) demarcation is the second-most-confused clause pair in the standard (after 6.1.2 / 8.2). Most commentary collapses the two into a single "do the treatment" instruction with no implementation discipline, no operational SoA, no residual-risk acceptance record, no effectiveness evaluation. The 2025 edition inherits the harmonized-structure split: 6.1.3 is the decision (which option per risk, which controls selected, the planning-layer SoA that documents the design intent, the planning-layer RTP), 8.3 is the execution (the controls actually operating in production, the operational SoA that documents current state with justified exclusions, the residual-risk acceptance record signed operationally, the effectiveness evaluation that closes the loop). Conflating the two is a Stage 1 finding on either 6.1 or 8.3 (and frequently both). Second, the operational Statement of Applicability is the load-bearing 8.3 artefact, a current-state, version-controlled, reconciled document that cross-walks every Annex A.1, A.2 and A.3 control to its operational status. The three discipline rules are non-negotiable: current-state only (a control marked applicable where the implementation is planned but not yet in operation is a nonconformity, the canonical 6.1.3 / 8.3 audit failure); justified exclusions (every not-applicable control has a documented reason, a missing or boilerplate justification is a nonconformity); no hypothetical-future-applicability (a control marked applicable on a hypothetical future relationship, "we may have a joint controller next year", is a nonconformity). The operational SoA is updated on every risk-register change, every DPIA completion, every new or amended requirement, every 6.3 change, and at the planned-interval cycle. Third, treatment effectiveness evaluation is the operational loop that closes the PIMS. 8.2 produces the residual-risk projection; 8.3 implements the treatment; the effectiveness evaluation tests whether the residual-risk projection held, whether the controls operated as designed, whether the DPIA conclusion remained valid, whether new risks emerged that the original treatment did not anticipate. Without the effectiveness evaluation, the PIMS is a register with controls but no feedback loop; the controls drift, the residual-risk projection becomes theoretical, and the next surveillance audit surfaces a major nonconformity on either 8.3 or 9.1. |
| Domain | Operation (Clause 8). 8.3 sits between 8.2 (operational privacy risk assessment, produces the live Privacy Risk Register and the DPIA Register that 8.3 treats) and 9.1 (monitoring, measurement, analysis and evaluation, tests the residual-risk trajectory that 8.3 produces). The Clause 8 block is where the PIMS stops being a planning artefact and becomes a running system; 8.3 is the operational treatment engine that makes the controls live. Without 8.3, the 6.1.3 plan is theory and the 8.2 register has no operational consequence. |
| What you must produce | (a) An Operational Privacy Risk Treatment Procedure (the operational artefact, distinct from the 6.1.3 planning-layer Risk Treatment Plan) covering the implementation discipline, the operational SoA maintenance rules, the residual-risk acceptance workflow, the effectiveness evaluation cycle, the operational residual-risk register maintenance, the integration with the 8.2 live register, the roles and the Documented Information control; (b) the operational Statement of Applicability, a current-state, version-controlled, reconciled document cross-walking every Annex A.1, A.2 and A.3 control to its applicability status, its justification, its current-state implementation evidence and its exclusion reasoning where not applicable; (c) the operational residual-risk register, the current-state view of every material risk with its treatment option, the controls applied, the residual-risk rating, the risk-owner acceptance record, the review date and the effectiveness-evaluation cross-reference; (d) the residual-risk acceptance records, one signed record per risk above the risk-acceptance threshold, recording the risk owner, the rationale, the conditions, the mitigation commitments, the review date; (e) the treatment effectiveness evaluation records, at the planned interval and on material change, an evaluation per material treatment decision recording the projected residual risk, the actual residual risk, the control-operation evidence, the DPIA conclusion currency and the emerging-risk review; (f) the SDF DPIA findings log for Indian Significant Data Fiduciaries under DPDP section 10, recording each SDF DPIA finding, the treatment option selected, the operational implementation, the effectiveness evaluation; (g) the Consent Manager integrity control evidence where the organisation uses a Consent Manager under DPDP section 2(1)(g) and section 6, the integrity controls that protect the consent record, the withdrawal-signal honouring, the interoperability interface; (h) the Documented Information control set per Clause 7.5. |
| Typical owner | Top management owns the operational treatment discipline at the strategic level, Clause 8.3, like the rest of Clause 8, derives its authority from Clause 5.1 (leadership and commitment). The DPO / Privacy Lead is the canonical owner of the Operational Procedure, the operational SoA, the residual-risk register and the effectiveness evaluation programme, mandatory in India if the organisation is a Significant Data Fiduciary under DPDP section 10. The CISO / Security Lead owns the Annex A.3 implementation evidence, the security controls that operationalise the modify option for security-relevant privacy risks. Legal and Compliance own the regulatory-treatment axis, the controls that satisfy specific DPDP / GDPR / sectoral obligations. Business-process owners are the named risk owners for the risks generated by their processing activities, risk ownership follows processing-activity ownership, and the residual-risk acceptance signature sits with the business-process owner. Internal Audit tests the operational SoA, the residual-risk register, the acceptance records and the effectiveness evaluation at the internal audit (Clause 9.2). For SDFs, the DPO based in India (per DPDP section 10) is accountable to the Board for the SDF DPIA findings log, the algorithmic-software review as a treatment control, and the Consent Manager integrity controls. |
| Minimum viable actions | (1) Issue or refresh the Operational Privacy Risk Treatment Procedure, distinct from the 6.1.3 planning-layer RTP; (2) build or refresh the operational SoA cross-walking every Annex A.1 / A.2 / A.3 control to current-state implementation evidence, with documented exclusion reasoning for every not-applicable control; (3) confirm the integrated-with-distinction posture, the operational SoA is reconciled with the ISMS SoA (ISO/IEC 27001:2022 Clause 6.1.3 / 8.3); (4) run the residual-risk acceptance workflow, every risk above the threshold has a signed acceptance record; (5) stand up the treatment-effectiveness evaluation cycle at the planned interval and on material change; (6) for SDFs, build the SDF DPIA findings log and wire it into the operational treatment cycle; (7) for organisations using a Consent Manager, document the Consent Manager integrity controls (Annex A.1.2.4, A.1.3.5, A.1.4 cross-references); (8) wire the operational residual-risk trajectory into the management review (Clause 9.3); (9) run the first effectiveness evaluation cycle and document the outcome; (10) reconcile the operational residual-risk register with the 8.2 live register, the ROPA, the requirements register, the contract inventory and the change log. |
| Maturity floor (L1) | A "point-in-time" treatment discipline: the operational SoA is updated in the thirty days before the surveillance audit; the residual-risk acceptance records are missing or unsigned; the effectiveness evaluation does not exist; the operational residual-risk register is a print-out of the 6.1.3 planning-layer RTP; the 6.1.3 / 8.3 demarcation is not made. The single most common Clause 8.3 audit nonconformity in the Indian growing-company segment. |
| Maturity target (L4 to L5) | An "operationally treatment-literate" PIMS: the Operational Procedure runs at the planned cadence and on every event trigger; the operational SoA is current-state, version-controlled, justified on every exclusion, reconciled with the ISMS SoA; every risk above the threshold has a signed residual-risk acceptance record; the effectiveness evaluation runs at the planned interval and feeds back into the treatment cycle; the operational residual-risk register reconciles with the 8.2 live register, the ROPA, the requirements register, the contract inventory and the change log; for SDFs, the SDF DPIA findings log drives the treatment cycle; the Consent Manager integrity controls are evidenced. |
| Audit red flag | An operational SoA whose last-update date is the same as the last surveillance audit, OR an operational SoA that documents controls as applicable where the implementation is "in progress" or "planned". The 8.3 audit test is always the same: the auditor picks a control marked applicable in the operational SoA (e.g. A.1.2.4 consent capture, A.1.4.5 PII minimisation, A.2.2.5 infringing-instruction handling, A.3.23 secure authentication) and asks "show me the current-state operational evidence, the procedure, the system, the records, the owner, the last review". If the answer is "we're rolling it out next quarter" or "the vendor is implementing it", the PIMS has an 8.3 finding. The second-most-common red flag is the 6.1.3 / 8.3 conflation, a single Risk Treatment Plan with no operational SoA, no operational residual-risk register, no effectiveness evaluation. The third is the unsigned residual-risk acceptance, risks above the threshold are listed but not signed by the named risk owner. |
| Quick win | Run a 90-minute operational-SoA reconciliation workshop with the DPO, the CISO, the Head of Legal and the top five business-process owners. Use the Singahi operational SoA template (toolkit doc 03) on a shared screen. Walk every Annex A.1 / A.2 / A.3 control currently marked applicable: is the implementation current-state (in operation today), or future-state (planned / in progress / vendor-dependent)? For every future-state row, either downgrade to not-applicable with a documented exclusion reason, or commit to a remediation target date and remove the row from the audit-evidence set until the control is live. Most Indian growing companies surface five to fifteen future-state rows in the first workshop, each one is a Stage 1 nonconformity waiting to be written. Closing that gap is the cheapest 8.3 remediation move. |
| Time to implement (first cycle) | Growing companies (50 to 250 staff): 6 to 12 weeks for the first operational pass, including the operational SoA for the full Annex A.1 / A.2 / A.3 set, the residual-risk register for the top 10 to 30 material risks, the acceptance records for risks above the threshold, and the first effectiveness evaluation cycle. Mid-sized (250 to 2,000): 12 to 20 weeks, usually requiring the integrated-with-distinction posture with the existing ISMS risk-treatment cycle, the Consent Manager integrity control evidence, and the SDF DPIA findings log if designated. Multi-entity enterprise: 6 to 10 months, integrated with the enterprise risk management function, the operational SoA programme at group level plus entity-level annexes, and the algorithmic-software review pipeline for AI-driven processing activities. |
| Related clauses | 4.1 (context drives the risk landscape; changes in context trigger treatment-effectiveness re-evaluation), 4.2 (requirements are the canonical treatment target), 4.3 (scope defines the operational treatment boundary), 4.4 (the PIMS is run through 8.3 operationally), 5.1, 5.2, 5.3 (leadership, policy, roles, risk owners sign the acceptance records), 6.1 (the planning-layer methodology, 6.1.3 produces the planning-layer treatment decisions; 8.3 implements them; the demarcation is load-bearing), 6.2, 6.3 (every material change triggers an 8.3 treatment revision), 7.2, 7.3, 7.4, 7.5 (Documented Information, the operational SoA, the residual-risk register, the acceptance records, the effectiveness evaluation), 8.1 (the umbrella over the seven core PIMS processes, 8.3 is the treatment engine inside 8.1), 8.2 (the operational risk assessment that 8.3 treats), 9.1 (monitoring tests the residual-risk trajectory and the control-operation effectiveness), 9.2 (internal audit tests the operational SoA, the residual-risk register, the acceptance records, the effectiveness evaluation), 9.3 (management review receives the operational residual-risk trajectory), 10.2, 10.1. Annex A.1 (controllers), A.2 (processors), A.3 (security, the integrated-with-distinction bridge with the ISMS). |
| Critical Indian context-bearing instruments | DPDP Act 2023 (Act 22/2023), section 8(5) reasonable security safeguards (the modify-option control surface), section 8(6) breach notification (intimation without delay and a seventy-two-hour report), section 9 children (the avoid-option trigger for prohibited processing), section 10 SDF (SDF DPIA findings log drives the operational treatment), section 2(1)(g) + section 6 Consent Manager (the integrity controls), section 11 rights, section 16 cross-border negative list, section 18 DPBI, section 33 + Schedule (penalty maxima up to two hundred and fifty crore for section 8(5) failure; two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10); DPDP Rules 2025 (notified 13 November 2025), Rule 7, SDF thresholds, Consent Manager registration; Puttaswamy (2017) 10 SCC 1; Aadhaar (2019) 1 SCC 1 (the proportionality test); CERT-In Directions 20(3)/2022-CERT-In of 28 April 2022 (the six-hour clock and the dual-clock pattern); RBI, SEBI and IRDAI sectoral instruments. Full instrument list in Section 24. |
If you only read one thing: Clause 8.3 is where the planning-layer 6.1.3 treatment decisions become a running operational discipline. An 8.3-conformant PIMS is one in which the organisation implements the treatment plan in the live environment, produces and maintains an operational Statement of Applicability that documents current-state implementation of every applicable Annex A.1 / A.2 / A.3 control with a defensible justification for every exclusion, accepts residual risk through a signed record by the named risk owner, evaluates the effectiveness of the treatment at planned intervals and on material change, and feeds the operational residual-risk trajectory into the management review. Not an operational SoA updated once a year for the surveillance audit with controls marked applicable where the implementation is "in progress". The certification auditor will pick a control marked applicable in the operational SoA and walk it through to the operational evidence; the Data Protection Board of India will, after a complaint or a breach, ask whether the SDF DPIA findings were treated, whether the Consent Manager integrity controls were operating, whether the residual-risk acceptance was actually signed by the named owner. Get 8.3 wrong, future-state SoA, hypothetical-future-applicability, unsigned residual-risk acceptance, no effectiveness evaluation, conflate with 6.1.3, and however strong the planning architecture, the PIMS does not operate as a controlled system. Get it right, and every other clause becomes easier to evidence because the operational treatment engine is sound.
What the Standard Actually Requires
The paraphrased requirement
ISO/IEC 27701:2025 Clause 8.3 asks organizations to operationally execute the privacy risk treatment, implementing the treatment plan produced under 6.1.3, producing and maintaining the operational Statement of Applicability as a current-state artefact, accepting residual risk through a documented and signed record, and evaluating the effectiveness of the treatment. Five load-bearing ideas sit inside that paraphrase, and auditors test each separately.
The organisation must implement the treatment option selected under 6.1.3. The four options inherited from ISO 31000:2018 and ISO/IEC 27005:2022 are: modify (apply controls to reduce the likelihood or the impact, the canonical option for most privacy risks; the controls are selected from Annex A.1, A.2 and A.3 and implemented operationally); retain (accept the residual risk above the threshold through a documented and signed acceptance record); avoid (terminate the processing activity that generates the risk, the option for risks that exceed the risk appetite and cannot be modified, e.g. behavioural monitoring of children under DPDP section 9); and share (transfer part of the risk through insurance or contractual allocation, share does not eliminate the risk; the principal-impact is not transferable and the organisation remains accountable to the principal regardless of the contractual allocation). 8.3 is the operational execution: the modify option means the controls are actually operating in production (not "planned"); the retain option means the acceptance record is actually signed; the avoid option means the processing activity is actually terminated; the share option means the insurance and the contractual allocation are actually in place.
The organisation must produce and maintain the operational Statement of Applicability. The operational SoA is the load-bearing 8.3 artefact. It cross-walks every Annex A.1, A.2 and A.3 control to four columns: (a) the applicability status (applicable / not applicable); (b) the justification (the risk it treats, cross-referenced to the live Privacy Risk Register, or the requirement it satisfies, cross-referenced to the requirements register); (c) the implementation state, current-state, evidenced, never future-state, never "in progress", never "planned"; (d) the exclusion reasoning where not applicable. The operational SoA is updated on every risk-register change, every DPIA completion, every new or amended requirement, every 6.3 change, and at the planned-interval cycle. The operational SoA is the single artefact the certification auditor opens first at a surveillance audit.
The organisation must accept residual risk through a documented and signed record. For every risk above the risk-acceptance threshold, the named risk owner signs a residual-risk acceptance record. The record includes the risk description, the residual-risk rating, the treatment option selected, the rationale for the acceptance, the conditions (e.g. mitigation commitments, monitoring requirements), the review date, and the risk owner's signature with date. The acceptance is reported to the management review (Clause 9.3); the open acceptance record count is a KPI (Section 12). A risk above the threshold without a signed acceptance record is the canonical 8.3 audit failure on the residual-risk-acceptance dimension.
The organisation must evaluate the effectiveness of the treatment at planned intervals and on material change. For each material treatment decision, the effectiveness evaluation tests: did the residual-risk projection from 6.1.3 hold? Did the controls operate as designed (the operation evidence, logs, reviews, tests, incidents)? Did the DPIA conclusion remain valid? Did new risks emerge that the original treatment did not anticipate? The evaluation feeds back into the treatment cycle, controls that did not operate as designed trigger corrective action (Clause 10.2); DPIA conclusions that did not remain valid trigger a re-run under 8.2; emerging risks trigger a re-assessment under 8.2 and a treatment revision under 8.3. Without the effectiveness evaluation, the PIMS has no feedback loop and the residual-risk projection becomes theoretical.
The organisation must maintain the operational residual-risk register. The operational residual-risk register is the current-state view of every material risk with its treatment option, the controls applied, the residual-risk rating, the risk-owner acceptance record, the review date and the effectiveness-evaluation cross-reference. The register reconciles with the 8.2 live Privacy Risk Register (every risk in the 8.2 register has a corresponding entry in the 8.3 register with the treatment state); the ROPA (every processing activity has a corresponding risk-treatment set); the requirements register (every material requirement is satisfied by a control in the operational SoA); the contract inventory (every processor-side risk has a corresponding DPA entry); and the change log (every material change has a corresponding treatment revision). The operational residual-risk register is the artefact the management review receives; it is also the artefact the Data Protection Board of India will request after a breach.
The 6.1.3 / 8.3 demarcation, the second-most-confused pair in the standard
The second-most-confused clause pair in ISO/IEC 27701:2025 (after 6.1.2 / 8.2) is 6.1.3 (the planning-layer privacy risk-treatment decisions) and 8.3 (the operational-layer privacy risk-treatment execution). The conflation produces a single "do the treatment" instruction with no implementation discipline, no operational SoA, no residual-risk acceptance record, no effectiveness evaluation, and that conflation is a Stage 1 finding on either 6.1 or 8.3 (and frequently both). The demarcation is load-bearing.
6.1.3 is the planning layer. It establishes the decisions, the treatment option selected per material risk (modify / retain / avoid / share), the planning-layer Statement of Applicability that documents the design intent, the planning-layer Risk Treatment Plan that records per-risk the option, the controls selected, the implementation owner, the target date, the resource estimate and the residual-risk projection. 6.1.3 produces the plan.
8.3 is the operational layer. It implements the plan in the live environment. 8.3 produces the operational SoA (current-state implementation, evidenced), the operational residual-risk register (current-state treatment state per risk), the residual-risk acceptance records (signed by the named risk owner), and the treatment effectiveness evaluation records (closing the loop).
The two layers reconcile in three places. First, the decision-to-implementation trace, every treatment option in the 6.1.3 RTP has a corresponding operational implementation in the 8.3 residual-risk register. Second, the SoA-to-SoA reconciliation, the planning-layer SoA documents the design intent; the operational SoA documents the current state; where the two diverge, the gap is either a remediation commitment or a nonconformity. Third, the effectiveness feedback, the effectiveness evaluation (8.3) tests whether the planning-layer residual-risk projection (6.1.3) held in operation; where it did not, the planning-layer methodology is revised (Clause 10.1) and the RTP is updated.
The practitioner pattern that survives the audit: a single Risk Treatment Plan (6.1.3) that explicitly references the Operational Privacy Risk Treatment Procedure (8.3) and the operational SoA (8.3 evidence), and a single live set of residual-risk acceptance records and effectiveness evaluations that trace back to the 6.1.3 decisions. The two clauses are separate; the artefact set is integrated.
The 8.2 → 8.3 operational loop, the assess-treat-verify engine
8.2 and 8.3 are inseparable operationally. 8.2 produces the live Privacy Risk Register and the DPIA Register; 8.3 implements the treatment decisions on that register and produces the operational residual-risk register. The two clauses form the operational assess-treat-verify engine.
Assess (8.2). The privacy risk assessment is run at planned intervals and on every event trigger. For each in-scope processing activity, the risks are identified, analysed (likelihood × principal-impact × organisational-impact), evaluated against the documented risk criteria, and recorded in the live Privacy Risk Register. The DPIA pipeline runs on every triggered processing activity. The 8.2 output is the residual-risk projection per material risk, the risk after the planning-layer controls, before the operational treatment.
Treat (8.3). For each material risk in the 8.2 register, the treatment option is implemented operationally. The modify option selects controls from Annex A.1, A.2 and A.3 and implements them in the live environment; the operational SoA documents the current-state implementation. The retain option produces a signed residual-risk acceptance record. The avoid option terminates the processing activity. The share option puts the insurance and the contractual allocation in place. The 8.3 output is the operational residual-risk register, the actual residual risk after the operational treatment.
Verify (8.3 + 9.1). At the planned interval and on material change, the effectiveness evaluation tests whether the treatment held. The evaluation feeds back into the assess step (8.2 re-assessment) and the treat step (8.3 treatment revision). Clause 9.1 provides the continuous-monitoring spine; 8.3 effectiveness evaluation is the periodic deep-dive.
The loop is operational, not annual. A material change (the seven-trigger catalog from the Clause 6.3 guide) breaks the steady state, the assess step re-runs, the treat step is revised, the verify step is re-baselined. A breach, a complaint, an audit finding, a regulator engagement, each is a trigger that re-opens the loop.
The operational Statement of Applicability, the load-bearing 8.3 artefact
The operational SoA is the single most-tested artefact in the 8.3 evidence set. Three discipline rules are non-negotiable, and most operator nonconformities sit at one of these three.
Rule 1, Current-state, evidenced. A control marked applicable must have current-state implementation evidence, the control is in operation today, not "planned", not "in progress", not "rolling out next quarter". The evidence is the procedure, the system, the records, the owner, the last review. A future-state row is the canonical 6.1.3 / 8.3 audit failure flagged in tier-1 practitioner commentary.
Rule 2, Justified exclusions. A control marked not-applicable must have a documented, specific, defensible exclusion reason (the organisation does not act in the role; the control does not treat a material risk and does not satisfy a material requirement). Boilerplate ("not relevant to our business") is a nonconformity.
Rule 3, No hypothetical-future-applicability. A control must not be marked applicable on a hypothetical future relationship. The canonical example is A.1.2.8 (joint PII controller) marked applicable because "we may enter a joint-controller arrangement next year", the control is not applicable until the arrangement exists; on the day the arrangement is signed, the control becomes applicable and the operational SoA is updated.
The operational SoA is structured as a single matrix with one row per Annex A control and the four columns. The Singahi operational SoA template (toolkit doc 03) provides the structure with all 78 Annex A controls pre-populated. The operational SoA reconciles with the planning-layer SoA (6.1.3) on applicability, the operational SoA adds the current-state implementation column, and with the ISMS SoA (ISO/IEC 27001:2022 Clause 6.1.3 / 8.3) on the Annex A.3 controls, where the two SoAs share the evidence.
The residual-risk acceptance record, the discipline most organisations miss
For every risk above the risk-acceptance threshold, the named risk owner signs a residual-risk acceptance record. The acceptance record documents the organisation's informed decision to operate with the residual risk rather than invest in further treatment, terminate the activity, or transfer part of the risk. The record includes the risk ID, the risk description, the residual-risk rating, the treatment option selected, the rationale (specific, not boilerplate), the conditions (mitigation commitments, monitoring requirements, review date), the risk-owner signature with date, the DPO countersignature for risks above a higher threshold, and the top management sign-off for risks at the highest threshold (critical risks affecting a material principal population; risks with section 33 penalty exposure). The acceptance is reported to the management review (Clause 9.3); the open acceptance record count is a KPI (Section 12). A risk above the threshold without a signed acceptance record is the canonical 8.3 audit failure on the residual-risk-acceptance dimension, and a frequent finding because the planning-layer RTP lists the risks but the operational acceptance records are never produced.
The treatment effectiveness evaluation, closing the operational loop
The effectiveness evaluation is the operational loop that closes the PIMS. Without it, the treatment cycle is open-loop, the controls are implemented, the residual risk is projected, but no one tests whether the projection held. The evaluation runs at the planned interval (annual minimum; semi-annual for SDFs and listed entities; quarterly for high-volatility sectors) and on material change. For each material treatment decision the evaluation records: the projected residual risk (from the 6.1.3 RTP); the actual residual risk (observed in operation); the control-operation evidence (testing results, log reviews, metrics, incident records, audit findings); the DPIA conclusion currency (did the conclusion remain valid?); the emerging-risk review (the threat-intelligence feed, the regulator-engagement feed, the post-incident review feed); the effectiveness conclusion (effective / partially effective / ineffective); and the treatment revision (confirmed / adjusted / re-engineered). The evaluation feeds back into the assess step (8.2 re-assessment for ineffective treatments), the treat step (8.3 treatment revision for partially effective treatments), the planning layer (6.1.3 RTP update for systematically wrong projections), and the continual improvement cycle (10.1 for systemic findings). The evaluation is the operational expression of the Clause 9.1 monitoring discipline.
What the standard does NOT require (the demarcation)
- 8.3 does not require re-running the planning-layer treatment decision every cycle. The 6.1.3 decisions persist; 8.3 implements them.
- 8.3 does not require every Annex A control to be implemented. The operational SoA documents both the applicable and the not-applicable controls, with the justification for each.
- 8.3 does not require zero residual risk. The discipline is to implement, document, accept and evaluate, including risk-acceptance above the threshold.
- 8.3 does not require a specific tool. A spreadsheet-based operational SoA is acceptable for the first cycle; a GRC platform is a maturity upgrade. The test is whether the operational SoA is current-state, justified, and reconciled.
- 8.3 does not require the operational SoA to be a public document. The SoA is internal Documented Information; a summary may appear in the transparency report.
- 8.3 does not require the DPO to be the risk owner. Risk ownership follows processing-activity ownership; the business-process owner is the canonical risk owner and the residual-risk acceptance signature sits with that owner. The DPO maintains the SoA and the residual-risk register.
- 8.3 does not require quantitative residual-risk analysis. A qualitative rating with documented criteria is sufficient.
- 8.3 does not require cyber-insurance. The share option may use cyber-insurance, contractual allocation, or both.
What auditors actually check
The certification auditor's Clause 8.3 examination has seven predictable moves. First, open the operational SoA, is it dated, version-controlled, signed; does it cover every Annex A control; is each applicable control justified; is each not-applicable control justified; is the implementation current-state; are there hypothetical-future-applicability rows? Second, test the 6.1.3 / 8.3 demarcation, are they distinct artefacts; do they reconcile? Third, pick a control marked applicable and trace it forward to the operational evidence, A.1.2.4 (consent capture) to the consent management system and the consent record format; A.1.3.5 (withdrawal mechanism) to the withdrawal workflow and the latency metric; A.1.4.5 (PII minimisation) to the data-minimisation review; A.2.2.5 (infringing-instruction handling) to the process for handling a customer instruction that would breach DPDP; A.3.23 (secure authentication) to the authentication standard and the MFA deployment evidence. Any break in the trace is a finding. Fourth, open the residual-risk register and the acceptance records, for each above-threshold risk, is the acceptance signed by the named risk owner with a specific rationale and documented conditions? Fifth, open the effectiveness evaluation records, is there an evaluation per material treatment decision with the per-decision structure populated? Sixth, test the integration with 8.2 and 9.1, does the operational residual-risk register reconcile with the 8.2 live register; does the effectiveness evaluation feed back into the 8.2 re-assessment cycle? Seventh, test the SDF-specific evidence where applicable, the SDF DPIA findings log, the algorithmic-software review as a treatment control, the Consent Manager integrity control evidence.
Why This Control Matters
The operational treatment engine of the PIMS
Every other clause of ISO/IEC 27701:2025 inherits its operational currency from Clause 8.3. The policy (5.2) commits to risk-based privacy; the operational SoA (8.3) documents which controls actually operate to deliver that commitment. The objectives (6.2) are calibrated to the residual-risk trajectory the 8.3 effectiveness evaluation produces. The awareness programme (7.3) trains staff on the operational controls the 8.3 SoA documents. The operational processes (Clause 8) implement the treatment the 8.3 SoA justifies. The DPIA programme (Annex A.1.2.6) produces the findings the 8.3 SDF DPIA findings log treats. The internal audit (9.2) and the management review (9.3) test whether the operational treatment discipline is sound. The corrective action (10.2) responds when the effectiveness evaluation shows the treatment did not hold. Without 8.3, the 6.1.3 plan is theory and the 8.2 register has no operational consequence.
This is not a stylistic observation. It is the operational reality the certification auditor and the Data Protection Board of India converge on. A PIMS that runs 8.3 once a year for the surveillance audit, updating the operational SoA in the thirty days before the audit, producing acceptance records the night before, running a tick-box effectiveness evaluation, is, in auditor language, a "system without operational treatment literacy", a structural finding that cascades into every other Clause 8 sub-clause because the operational treatment engine is dark between audits. A PIMS that runs 8.3 at the planned cadence and on every event trigger is defensible end-to-end.
The Indian regulatory weight behind 8.3
In India, Clause 8.3 carries a regulatory weight that goes beyond the ISO standard because the DPDP Act 2023 and the DPDP Rules 2025 impose affirmative operational obligations that engage exactly when the organisation processes personal data. The SDF DPIA findings under section 10 must be treated under 8.3: every 12 months, the SDF DPIA produces findings (the systematic description, the necessity-and-proportionality test, the principal-impact analysis, the residual-risk projection, the consultation record); the 8.3 operational treatment implements the controls that respond to those findings. The breach-notification obligation under section 8(6), intimation without delay and a seventy-two-hour report to the Board, presupposes that the operational controls (the incident-response control, the breach-detection control, the notification workflow) are actually in operation; the 8.3 operational SoA documents the current-state implementation of those controls. The children's-data regime under section 9 presupposes that the operational controls (the verifiable-parental-consent control, the no-behavioural-monitoring control, the no-targeted-advertising control) are actually in operation; the avoid option under 8.3 terminates any processing activity that would breach section 9. The Consent Manager regime under section 2(1)(g) and section 6 presupposes that the operational controls (the consent-record integrity control, the withdrawal-signal-honouring control, the interoperability-interface control) are actually in operation; the 8.3 operational SoA documents the Consent Manager integrity control evidence.
The penalty exposure underscores the weight. Section 33 + the Schedule set the maxima: up to two hundred and fifty crore rupees for section 8(5) failure (reasonable security safeguards, the modify-option control surface), up to two hundred crore for section 8(6) failure (breach notification, the operational breach-response control), up to two hundred crore for section 9 failure (children's data, the avoid-option discipline for prohibited processing), up to one hundred and fifty crore for section 10 failure (SDF obligations, the SDF DPIA findings log and the algorithmic-software review as a treatment control). The operational SoA must surface these obligations; the operational treatment must implement the controls that satisfy each; the effectiveness evaluation must test whether the controls actually hold.
The lineage is the wedge. K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (judgment delivered 24 August 2017 by a nine-judge Bench of the Supreme Court) declared the right to privacy, including informational privacy, a fundamental right under Articles 14, 19 and 21 of the Constitution. The Aadhaar judgment (2019) 1 SCC 1 set the proportionality test, the modify option must be proportionate (the least intrusive means to the legitimate aim). The DPDP Act was enacted 11 August 2023. The DPDP Rules 2025 were notified 13 November 2025 with phased commencement. ISO/IEC 27701:2025 was published 14 October 2025, twelve days before the DPDP Rules were notified. The two instruments were, in effect, made for each other; the operational SoA is where the legal landscape enters the PIMS, every day, on every applicable control.
The dual-clock pattern is the uniquely Indian 8.3-relevant operational control. A single personal-data-breach event triggers two parallel reporting clocks under two parallel regimes: the CERT-In six-hour clock (CERT-In Directions 20(3)/2022-CERT-In of 28 April 2022, the ICT-incident angle) and the DPDP breach clock (intimation without delay, then a seventy-two-hour report; DPDP Act section 8(6) read with DPDP Rules 2025 Rule 7, the personal-data angle). For BFSI and listed entities, a third clock applies (RBI six hours; SEBI six hours; IRDAI twenty-four to seventy-two hours). The breach-response control under 8.3, the operational implementation of Annex A.3.12 (response to information security incidents), must handle all applicable clocks in parallel from the same awareness event. The effectiveness evaluation must test this dual-clock control periodically.
The cost of non-compliance
The cost of a Clause 8.3 failure breaks down into four bands. Direct DPDP penalty exposure for an organisation whose operational SoA documents controls as applicable where the implementation is future-state (e.g. the consent-withdrawal control marked applicable but the withdrawal workflow not actually implemented; the breach-notification control marked applicable but the dual-clock workflow not actually operating) can run to the Schedule maxima, up to two hundred and fifty crore for section 8(5), two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10. Indirect regulatory consequences are larger and slower, an operational SoA failure that produces an incorrect residual-risk projection, an ineffective treatment, or an unsigned acceptance cascades through every other Clause 8 sub-clause. The Data Protection Board of India, after a complaint or a breach, will request the operational SoA, the residual-risk register, and the effectiveness evaluation; an absence or a defect is the post-incident equivalent of a major nonconformity. Commercial cost is significant, the Indian privacy incidents most cited in board rooms (Juspay approximately thirty-five million records in 2021, publicly acknowledged; BigBasket approximately twenty million records alleged in 2020; Air India / SITA approximately four-and-a-half million customers affected by the SITA breach disclosed in 2021; MobiKwik contested allegations, denied by the company) all carried post-incident examinations that tested whether the operational controls were actually operating, whether the residual-risk acceptance was actually signed, whether the effectiveness evaluation was actually done. Recoverable; entirely avoidable with a workable operational discipline.
Scope and Applicability
By organisation size
Growing companies (50 to 250 staff). A compact operational artefact set: a single Operational Privacy Risk Treatment Procedure of fifteen to twenty-five pages, an operational SoA covering the full Annex A.1 / A.2 / A.3 set (with the controller-side applicable for most growing companies, the processor-side applicable where the organisation acts as a processor, the security-side applicable across the board), an operational residual-risk register of thirty to eighty entries, residual-risk acceptance records for the risks above the threshold (typically five to fifteen in the first cycle), and the first effectiveness evaluation cycle covering the top ten to fifteen material treatment decisions. The first cycle is deliverable in six to twelve weeks of internal effort plus external advisory.
Mid-sized (250 to 2,000 staff). A more granular artefact set: an Operational Procedure of twenty-five to forty pages, an operational SoA with the integrated-with-distinction posture (the Annex A.3 evidence shared with the ISMS SoA), an operational residual-risk register of eighty to two hundred and fifty entries, residual-risk acceptance records for risks above the threshold (typically fifteen to forty), the effectiveness evaluation cycle covering the top thirty to fifty material treatment decisions, and for SDFs the SDF DPIA findings log and the algorithmic-software review pipeline. The first cycle typically takes twelve to twenty weeks and requires board-cycle alignment for the acceptance decisions at the higher threshold.
Multi-entity enterprise (2,000+ staff or multi-jurisdiction). A layered operational architecture: a group Operational Procedure plus entity-level operational SoA annexes plus jurisdiction-specific acceptance streams; an effectiveness evaluation programme (the systematic, repeatable evaluation cycle); the SDF DPIA findings log integrated with the DPIA pipeline from 8.2; the algorithmic-software review integrated with the MLOps pipeline; for SDFs, the full section 10 cadence (DPO based in India, SDF DPIA every 12 months, periodic independent data audit, algorithmic-software review). Typically six to ten months for the first cycle, with an embedded privacy-treatment function.
By PIMS role
PII controller (Data Fiduciary) primary. The operational SoA leads with the Annex A.1 controls, the consent-quality controls (A.1.2.3, A.1.2.4, A.1.2.5), the notice-quality controls (A.1.3.3, A.1.3.4), the rights-handling controls (A.1.3.5 to A.1.3.10), the privacy-by-design controls (A.1.4.2 to A.1.4.10), the cross-border-transfer controls (A.1.5.2 to A.1.5.5). The operational residual-risk register leads with the controller-side risks; the acceptance records are signed by the business-process owners of the controller-side processing activities.
PII processor (Data Processor) primary. The operational SoA leads with the Annex A.2 controls, the customer-agreement control (A.2.2.2), the infringing-instruction control (A.2.2.5), the customer-obligations control (A.2.2.6), the sub-processor controls (A.2.5.7 to A.2.5.9). The operational residual-risk register leads with the processor-side risks; the acceptance records are signed by the customer-account owners or the service-delivery owners.
Both controller and processor. The most common shape for Indian growing companies. The operational SoA covers both Annex A.1 and Annex A.2 controls; the residual-risk register addresses both risk sets and the boundary between them, which risks are controller-side (the organisation's own principals), which are processor-side (the customer's principals reached through the organisation's processing), where the boundary is contested (joint-controller arrangements under Annex A.1.2.8 / GDPR Article 26).
By sector
Sector-specific overlays are addressed in Section 21 (BFSI, Healthcare, IT-ITeS, E-commerce, Edtech, Manufacturing), along with the cross-sector patterns (processor-side scale, dual-regulator exposure, AI-driven profiling) that recur regardless of industry.
Key Definitions and Terminology
Operational privacy risk treatment. The implementation of the 6.1.3 planning-layer treatment decisions in the live PIMS environment, the production and maintenance of the operational Statement of Applicability, the operational residual-risk acceptance, and the evaluation of treatment effectiveness. The 8.3 artefact set is the operational SoA, the operational residual-risk register, the residual-risk acceptance records, the treatment effectiveness evaluation records, and the SDF DPIA findings log (for SDFs).
Operational Statement of Applicability (operational SoA). The current-state, version-controlled, reconciled document cross-walking every Annex A.1, A.2 and A.3 control to (a) its applicability status (applicable / not applicable), (b) its justification (the risk or requirement it treats), (c) its implementation state (current-state, evidenced, never future-state), and (d) its exclusion reasoning where not applicable. "Operational" means the implementation column reflects the state of the control in production today, not the design intent.
Operational residual-risk register. The current-state view of every material risk with its treatment option, the controls applied, the residual-risk rating, the risk-owner acceptance record, the review date and the effectiveness-evaluation cross-reference. Reconciled with the 8.2 live Privacy Risk Register (every 8.2 risk has a corresponding 8.3 treatment state).
Residual-risk acceptance record. The signed artefact that documents the organisation's informed decision to operate with a residual risk above the acceptance threshold. Includes the risk ID, the residual-risk rating, the treatment option, the rationale, the conditions, the risk-owner signature with date, the DPO countersignature (for higher thresholds), the top management sign-off (for the highest threshold), and the review date.
Treatment effectiveness evaluation. The periodic and event-triggered evaluation that tests, for each material treatment decision, whether the residual-risk projection held, whether the controls operated as designed, whether the DPIA conclusion remained valid, and whether new risks emerged. The evaluation produces an effectiveness conclusion (effective / partially effective / ineffective) and a treatment revision (confirmed / adjusted / re-engineered).
Treatment option. The four options inherited from ISO 31000:2018 and ISO/IEC 27005:2022: modify (apply controls), retain (accept the residual risk), avoid (terminate the processing activity), share (transfer part of the risk through insurance or contractual allocation). The 8.3 operational execution implements the option selected under 6.1.3.
Risk owner. The named person with the authority and accountability to manage a risk, including signing the residual-risk acceptance record. Risk ownership follows processing-activity ownership, the business-process owner is the canonical risk owner.
Risk-acceptance threshold. The documented level above which a residual risk requires a signed acceptance record. Set at the planning layer (6.1.3); applied at the operational layer (8.3). Typically: low and medium residual risks do not require an acceptance record; high and critical residual risks require an acceptance record signed by the business-process owner; critical residual risks affecting a material principal population additionally require DPO countersignature and top management sign-off.
SDF DPIA findings log. For Indian Significant Data Fiduciaries under DPDP section 10, the operational artefact that records each SDF DPIA finding (from the 8.2 DPIA Register), the treatment option selected under 8.3, the operational implementation, the residual-risk acceptance (where applicable), and the effectiveness evaluation. The SDF DPIA findings log drives the operational treatment cycle for SDFs.
Algorithmic-software review (as a treatment control). For AI-driven processing activities, the algorithmic-software review (under DPDP section 10 for SDFs; recommended for non-SDFs) operates as a treatment control, the modify option that reduces the principal-impact on the non-discrimination dimension. The review assesses the model for bias, discrimination, transparency, explainability and adversarial strength.
Consent Manager integrity controls. For organisations using a Consent Manager under DPDP section 2(1)(g) and section 6, the operational controls that protect the consent record, honour the withdrawal signal, and maintain the interoperability interface. The Consent Manager is the Indian mechanism for satisfying Annex A.1.2.3 (when and how consent), A.1.2.4 (obtain and record consent), A.1.3.5 (withdrawal mechanism) and A.1.4 (privacy by design) operationally.
Current-state implementation. The discipline that the operational SoA's implementation column reflects the state of the control in production today, not the design intent or a future-state plan. The three sub-rules: no future-state ("in progress", "planned", "rolling out next quarter"); no hypothetical-future-applicability (the control is not applicable until the triggering relationship exists); justified exclusions only (every not-applicable control has a specific, defensible reason).
Integrated-with-distinction posture. The recommended posture for the operational SoA: a single risk-register backbone shared with the ISMS risk register (ISO/IEC 27001:2022 Clause 8.3 information security risk treatment), two distinct impact axes (principal-impact and organisational-impact), two distinct control surfaces (Annex A.1 / A.2 privacy controls and ISO/IEC 27002:2022 security controls), and a single operational SoA covering both surfaces with a clear cross-walk between the privacy controls and the security controls. The Annex A.3 controls are the bridge.
Relationship to Other Clauses and Frameworks
Inside ISO/IEC 27701:2025
- 4.1 (context): the issues drive the risk landscape; changes in context trigger treatment-effectiveness re-evaluation.
- 4.2 (interested parties): the requirements register is the canonical treatment target, every applicable control in the operational SoA treats a risk or satisfies a requirement.
- 4.3 (scope): defines the operational treatment boundary; scope changes trigger operational SoA re-scoping.
- 4.4 (the PIMS): run through 8.3 operationally.
- 5.1, 5.2, 5.3 (leadership, policy, roles): the policy commits to risk-based privacy; the roles include the named risk owners who sign the acceptance records.
- 6.1 (the planning-layer risk methodology): 6.1.3 produces the planning-layer treatment decisions; 8.3 implements them operationally. The 6.1.3 / 8.3 demarcation is load-bearing.
- 6.2 (objectives): calibrated to the residual-risk trajectory the 8.3 effectiveness evaluation produces.
- 6.3 (changes): every material change triggers an 8.3 treatment revision. The 6.3 change-control loop feeds the operational SoA update.
- 7.2 (competence): the operational treatment methodology competence is a 7.2 requirement.
- 7.3 (awareness): staff trained on the operational controls the 8.3 SoA documents.
- 7.4 (communication): internal and external communication about treatment, the board, the regulator, the principals.
- 7.5 (Documented Information): the operational SoA, the residual-risk register, the acceptance records, the effectiveness evaluation.
- 8.1 (operational planning and control): the umbrella over the seven core PIMS processes; 8.3 is the treatment engine inside 8.1.
- 8.2 (operational privacy risk assessment): produces the live Privacy Risk Register and DPIA Register that 8.3 treats.
- 9.1 (monitoring): tests the residual-risk trajectory and the control-operation effectiveness that 8.3 produces.
- 9.2, 9.3 (audit, review): test the operational SoA, the residual-risk register, the acceptance records, the effectiveness evaluation.
- 10.1, 10.2 (improvement, corrective action): respond when the effectiveness evaluation shows the treatment did not hold; improve the operational treatment discipline.
- Annex A.1 (controllers), A.2 (processors), A.3 (security): the controls implemented operationally under 8.3; the operational SoA documents the implementation state of each.
Cross-framework
- ISO/IEC 27001:2022 Clause 8.3 (information security risk treatment). The ISMS analogue of the 8.3 operational treatment. The integrated-with-distinction posture uses the shared structure, the operational PIMS SoA and the operational ISMS SoA share the Annex A.3 / ISO/IEC 27002:2022 evidence.
- ISO/IEC 27005:2022 (Information security risk management). The methodological reference for the four-treatment-option taxonomy (modify / retain / avoid / share).
- ISO 31000:2018 (Risk management). The umbrella vocabulary and the four-treatment-option source.
- ISO/IEC 29134:2017 (Guidelines for privacy impact assessment). The methodological reference for the DPIA tradition; the 8.3 effectiveness evaluation tests whether the DPIA conclusions remained valid.
- ISO/IEC 29100:2011 (Privacy framework). The 11 privacy principles that the Annex A.1 / A.2 controls operationalise.
- GDPR Article 24 (controller responsibility) and Article 32 (security of processing). The external anchors for the modify-option control surface. Article 5(2) accountability anchors the operational SoA.
- NIST Privacy Framework v1.0, Control-P function (Data-processing management, Disassociated processing, Data-flow management, Privacy testing). The US-flavoured structural analogue of the 8.3 operational treatment.
- NIST SP 800-37 Rev. 2 (Risk Management Framework), Continuous Monitoring step. The US federal continuous-monitoring tradition that informs the 8.3 effectiveness evaluation.
- SOC 2 (AICPA TSC 2017, with 2022 update), CC3.3 (Risk response), CC4.1 / CC4.2 (Monitoring). The SOC 2 view of the treatment and monitoring discipline. The Privacy category P-criteria depend on the treatment.
- ISO/IEC 42001:2023 (AI Management System). The algorithmic-software review is a treatment control on AI-driven processing activities; ISO/IEC 42001 is the structural reference for the algorithmic-fairness management discipline.
- DPDP Act 2023, section 8(5) reasonable security safeguards (the modify-option control surface); section 8(6) breach notification (the operational breach-response control); section 9 children (the avoid-option trigger for prohibited processing); section 10 SDF (DPIA findings log drives the operational treatment); section 2(1)(g) + section 6 Consent Manager (the integrity controls that protect the consent record); section 11 rights (the rights-handling controls); section 13 grievance; section 16 transfer (the transfer-impact-assessment controls); section 18 the Data Protection Board; section 33 + Schedule penalties. The DPDP is the load-bearing regulatory input to the Indian operational SoA.
Inside the harmonized structure, what 8.3 inherits
The harmonized structure (HS, formerly Annex SL) is the shared skeleton ISO uses for management-system standards. 27701:2025, 27001:2022, 22301:2019, 9001:2015, 14001:2015, 45001:2018, 42001:2023 all use it. For 8.3, this means the operational treatment discipline is structurally aligned with the infosec risk-treatment discipline, the business-continuity risk-treatment discipline, and the AI-system risk-treatment discipline. An organisation running an integrated 27001 + 27701 + 42001 programme can run a single combined operational treatment cycle with sub-sections for each discipline, a single operational SoA covering all three control surfaces, a single residual-risk register, a single effectiveness evaluation cycle.
Detailed Implementation Guidance, The Six Operational Moves
Figure · Process
What Clause 8.3 asks you to do
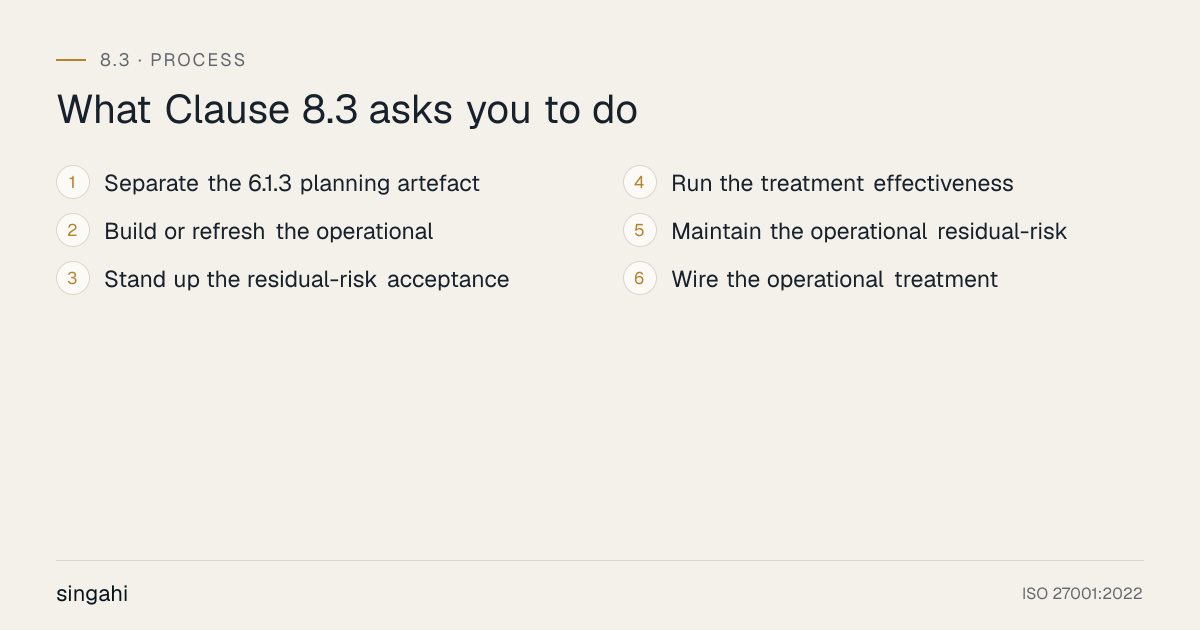
Move 1, Separate the 6.1.3 planning artefact from the 8.3 operational artefact
The first move is to physically separate the planning-layer Risk Treatment Plan from the operational-layer Operational Privacy Risk Treatment Procedure. The 6.1.3 RTP records the decisions: for each material risk, the treatment option selected, the controls selected, the implementation owner, the target date, the resource estimate, the residual-risk projection. The 6.1.3 planning-layer SoA records the design intent: which Annex A.1 / A.2 / A.3 controls are applicable and why. The 6.1.3 artefacts are stable, reviewed annually, amended when the framework shifts, signed by top management.
The 8.3 Operational Privacy Risk Treatment Procedure is a different artefact. It records the operational discipline that implements the decisions: the operational SoA maintenance rules (who updates, when, with what evidence), the residual-risk acceptance workflow (the signature chain, the thresholds, the conditions), the effectiveness evaluation cycle (the planned-interval cadence, the event-trigger re-evaluation, the per-decision evaluation structure), the operational residual-risk register maintenance rules, the integration with the 8.2 live register, the SDF DPIA findings log maintenance (for SDFs), the Consent Manager integrity control evidence (where applicable), the roles operationally, the Documented Information control. It is a living document, updated when the operational discipline shifts, signed by the DPO with sponsor authority.
The two documents cross-reference each other. The 6.1.3 RTP explicitly references the 8.3 Operational Procedure as the operational expression of the decisions; the 8.3 Operational Procedure explicitly references the 6.1.3 RTP as the decisions it implements. The two documents reconcile on the operational residual-risk register, every 8.3 entry traces back to a 6.1.3 decision, and every 6.1.3 decision has a corresponding 8.3 implementation state.
The Singahi Operational Privacy Risk Treatment Procedure template (toolkit doc 02) provides the structure with all 11 operational sections pre-populated for customisation.
Move 2, Build or refresh the operational Statement of Applicability
The operational SoA is the load-bearing 8.3 artefact. The discipline is current-state currency, not annual ceremony. The Singahi operational SoA template (toolkit doc 03) provides the structure with all 78 Annex A controls pre-populated (31 controllers + 18 processors + approximately 29 security, per the 2025-edition enumeration from the official PDF). The four columns per control:
- Applicability status, applicable / not applicable. The applicability test: does the organisation act in the role (controller for A.1, processor for A.2, either for A.3) AND does the control treat a material risk in the 8.2 live register OR satisfy a material requirement in the 4.2 requirements register?
- Justification, for applicable, the risk ID(s) or the requirement ID(s). For not-applicable, the documented exclusion reason (the organisation does not act in the role; the control does not treat a material risk and does not satisfy a material requirement).
- Implementation state (current-state, evidenced), the current-state evidence: the procedure reference, the system reference, the records reference, the owner, the last review date. Never future-state ("in progress", "planned", "rolling out next quarter").
- Exclusion reasoning (for not-applicable), specific and defensible. Not boilerplate.
The reconciliation discipline: the operational SoA reconciles with the planning-layer SoA (6.1.3), the two should agree on applicability, with the operational SoA adding the implementation column. The operational SoA also reconciles with the ISMS SoA (ISO/IEC 27001:2022 Clause 6.1.3 / 8.3) for the Annex A.3 controls, the integrated-with-distinction posture.
The currency discipline: the operational SoA is updated on every risk-register change, every DPIA completion, every new or amended requirement, every 6.3 change, and at the planned-interval cycle. An operational SoA whose last-update date matches the last surveillance audit is the canonical 8.3 red flag.
Move 3, Stand up the residual-risk acceptance workflow
The residual-risk acceptance workflow is the discipline most organisations miss. For every risk above the risk-acceptance threshold, the named risk owner signs a residual-risk acceptance record. The Singahi residual-risk acceptance record template (toolkit doc 05) provides the structure.
The workflow:
- Trigger, a risk in the 8.2 live register is rated above the acceptance threshold after the operational treatment (modify or share, with the residual risk remaining above the threshold), OR the retain option is selected.
- Acceptance record preparation, the DPO prepares the record with the risk ID, the residual-risk rating, the treatment option, the rationale (the specific reason the residual risk is acceptable), the conditions (the mitigation commitments, the monitoring requirements, the review date).
- Risk-owner signature, the named risk owner (the business-process owner for the processing activity that generates the risk) signs the record with date. The signature is the load-bearing element, the organisation's informed decision to operate with the residual risk.
- DPO countersignature, for risks above a higher threshold (e.g. critical, or section 10 SDF DPIA-related for SDFs), the DPO countersigns.
- Top management sign-off, for risks at the highest threshold (e.g. critical risks affecting a material principal population, or risks with section 33 penalty exposure), top management signs off at the management review (Clause 9.3).
- Filing and reporting, the acceptance record is filed in the operational residual-risk register; the open acceptance record count is reported to the management review.
- Review, the acceptance is reviewed at the planned interval (annual; quarterly for SDFs and listed entities) or on material change. The review re-tests whether the residual risk remains acceptable; if not, the acceptance is withdrawn and the treatment cycle re-opens.
The acceptance-record coverage discipline: every risk above the threshold has a signed acceptance. A risk above the threshold without a signed acceptance is a major nonconformity.
Move 4, Run the treatment effectiveness evaluation cycle
The effectiveness evaluation is the operational loop that closes the PIMS. The Singahi treatment effectiveness evaluation template (toolkit doc 06) provides the per-decision structure. The cycle runs at the planned interval (annual minimum; semi-annual for SDFs and listed entities; quarterly for high-volatility sectors) and on material change.
For each material treatment decision:
- Projected residual risk, from the 6.1.3 RTP (what the planning layer projected).
- Actual residual risk, observed in operation after the treatment cycle.
- Control-operation evidence, the control-testing results, the log reviews, the metrics, the incident records, the audit findings.
- DPIA conclusion currency, did the DPIA conclusion remain valid? If the DPIA was re-run under 8.2, did the residual-risk projection change?
- Emerging-risk review, the threat-intelligence feed, the regulator-engagement feed, the post-incident review feed.
- Effectiveness conclusion, effective / partially effective / ineffective.
- Treatment revision, confirmed / adjusted / re-engineered.
The evaluation feeds back into:
- The 8.2 re-assessment cycle for ineffective treatments.
- The 8.3 treatment revision for partially effective treatments (additional controls, modified conditions, revised review date).
- The 6.1.3 RTP update for treatments where the projection was systematically wrong (the planning-layer methodology is revised under Clause 10.1).
- The continual improvement cycle (10.1) for systemic effectiveness-evaluation findings.
Move 5, Maintain the operational residual-risk register
The operational residual-risk register is the current-state view of every material risk with its treatment state. The Singahi residual-risk register template (toolkit doc 07) provides the structure. Each entry records:
- Risk ID, cross-referenced to the 8.2 live Privacy Risk Register.
- Processing activity, the ROPA entry that generates the risk.
- Treatment option, modify / retain / avoid / share.
- Controls applied, the Annex A.1 / A.2 / A.3 controls (cross-referenced to the operational SoA rows).
- Residual-risk rating, the rating after the operational treatment.
- Risk owner, the named individual.
- Acceptance record, signed if residual risk is above the threshold; cross-referenced to the acceptance record.
- Review date, the next scheduled review.
- Effectiveness evaluation, the latest evaluation conclusion (effective / partially effective / ineffective); cross-referenced to the effectiveness evaluation record.
- Last-update date, when the entry was last reviewed.
- Last-update reason, the event that drove the update (planned-interval cycle, trigger event, treatment implementation, effectiveness evaluation finding).
The reconciliation discipline: the operational residual-risk register is reconciled against the 8.2 live register (every 8.2 risk has a corresponding 8.3 treatment state), the ROPA (every processing activity has a corresponding risk-treatment set), the requirements register (every material requirement is satisfied by a control in the operational SoA), the contract inventory (every processor-side risk has a corresponding DPA entry), the change log (every material change has a corresponding treatment revision), and the breach register (every breach realises a previously accepted residual risk, or surfaces a missing one).
Typical register sizes for Indian growing companies: thirty to eighty entries (fifty to two hundred and fifty staff); eighty to two hundred and fifty (mid-sized); two hundred and fifty to fifteen hundred or more (enterprise / SDF).
Move 6, Wire the operational treatment into the management review and the 8.2 → 8.3 loop
The operational treatment discipline is incomplete if it does not drive the management review and feed back into the 8.2 assessment cycle. The DPO presents to the management review (Clause 9.3): the operational residual-risk trajectory (high-and-critical count, quarter-on-quarter trend); the open residual-risk acceptance record count; the operational SoA currency (last-update date; the count of controls whose implementation state changed since the last review); the effectiveness evaluation results (effective / partially effective / ineffective counts; the treatment revisions arising); the SDF DPIA findings log status (for SDFs; findings open, treated, effectiveness-evaluated); the Consent Manager integrity control status (where applicable); the trigger events since the last review and the resulting treatment revisions. The management review is the forum where top management tests the operational treatment discipline, and where the certification auditor will sample the management-review minutes for evidence that the operational discipline is real.
The 8.2 → 8.3 loop is wired bi-directionally. 8.2 → 8.3: every risk in the 8.2 live register produces a treatment decision under 8.3; the 8.2 DPIA conclusions drive the 8.3 SDF DPIA findings log for SDFs. 8.3 → 8.2: the effectiveness evaluation findings drive the 8.2 re-assessment cycle for ineffective treatments; the operational residual-risk trajectory drives the 8.2 trigger events (a residual risk that climbs above the threshold triggers a re-assessment). The loop is operational, not annual. A material change breaks the steady state, 8.2 re-runs, 8.3 revises, the effectiveness evaluation re-baselines. A breach, a complaint, an audit finding, a regulator engagement, each is a trigger that re-opens the loop.
Worked example, Tarang Fintech operationalises the 8.3 treatment loop
To make the six moves concrete, consider Tarang Fintech (a fictional Bengaluru-based wealth-management platform with two thousand one hundred staff; the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation). Tarang's 8.3 build: Move 1 separated the 6.1.3 RTP (28 pages) from the 8.3 Operational Procedure (24 pages). Move 2 built the operational SoA covering the full Annex A set, sixty-two applicable controls, sixteen not-applicable with documented exclusion reasons (e.g. A.1.2.8 joint controller not applicable because no current arrangement; A.2.2.4 marketing not applicable because the processor-side business does not use customer PII for the processor's own marketing). Move 3 produced twenty-three residual-risk acceptance records: eighteen signed by the business-process owner (high risks); four with DPO countersignature (critical risks); one with additional top-management sign-off (the AI-driven portfolio-recommendation engine affecting a material principal population). Move 4 evaluated thirty-eight material treatment decisions, thirty-one effective, five partially effective (additional controls committed), two ineffective (consent-withdrawal latency exceeded the projected SLA; the cross-border TIA was stale on a UAE flow), with the two ineffective findings triggering corrective action under Clause 10.2 and re-assessment under 8.2. Move 5 maintained a 158-entry operational residual-risk register reconciled with the 8.2 live register (173 entries; the fifteen-risk delta was below the operational treatment threshold), the ROPA (forty-one processing activities), the requirements register (fifty-two entries), the contract inventory (forty-seven processors), and the change log (nineteen trigger events since the last review). Move 6 wired the trajectory into the management review, high-and-critical count down from twenty-three at cycle start to fourteen at cycle end, open acceptance record count of twenty-three (three due for review in the next quarter), operational SoA currency within thirty days, eleven controls whose implementation state changed since the last review.
The first-cycle effort: sixteen weeks of internal time plus external advisory; the resulting artefact set passed the 27701:2025 transition surveillance audit at first attempt; the operational discipline positioned Tarang for the SDF designation analysis and the algorithmic-software review (operationalised as a per-model release gate on the portfolio-recommendation engine).
The operational treatment discipline in more depth
The operational treatment is only as good as its currency. Three patterns dominate operationally. Pattern A, Annual update only (the canonical 8.3 failure): the operational SoA is updated in the thirty days before the surveillance audit; the residual-risk acceptance records are produced the night before; the effectiveness evaluation is a tick-box exercise. The rest of the year the operational treatment is dark, the single most common 8.3 finding in the Indian growing-company segment. Pattern B, Event-trigger update (the discipline most organisations should run): the operational SoA is updated whenever a material event fires (the seven-trigger catalog); the DPO maintains the change log and convenes the treatment-revision workshop on trigger. Pattern C, Continuous monitoring (the discipline for SDFs, listed entities, and large enterprises): the operational treatment is monitored continuously through a GRC platform, a threat-intelligence subscription, a processor-change feed, a regulatory-intelligence feed, and a stakeholder-engagement programme; the effectiveness evaluation runs on a continuous basis with quarterly deep-dives.
Tools, Technologies, and Solutions
The tool categories
Privacy GRC platforms. Modules that record the operational SoA, the operational residual-risk register, the residual-risk acceptance records, and the treatment effectiveness evaluation records. Generic descriptions: a GRC platform with a privacy-treatment module that supports the integrated-with-distinction posture and the event-trigger intake; an operational-SoA automation tool that pre-populates the implementation column from the ROPA and the control evidence library.
Operational SoA automation tools. Specialised platforms that operationalise the SoA maintenance discipline, the 78 Annex A controls pre-populated, the four-column structure, the currency alerts, the reconciliation with the planning-layer SoA and the ISMS SoA.
Residual-risk acceptance workflow tools. Modules that route the acceptance record to the named risk owner, capture the signature, file the record in the residual-risk register, and report the open count to the management review. Often a feature of the GRC platform rather than a standalone tool. Cost: typically bundled.
Effectiveness evaluation tools. Platforms that operationalise the per-decision evaluation structure, the projected residual risk, the actual residual risk, the control-operation evidence, the conclusion, the treatment revision. Often a feature of the GRC platform. Cost: typically bundled.
DPIA workflow tools. Specialised platforms that operationalise the 29134 / Article 35(7) structure with templates, routing, and the SDF DPIA findings log (for SDFs).
Consent and Consent Manager platforms. Operational tools that implement the consent controls (Annex A.1.2.3 / .4 / .5; A.1.3.5) and the Consent Manager integrity controls (DPDP section 2(1)(g) and section 6).
Continuous monitoring tools. Threat-intelligence feeds, processor-change feeds, regulatory-intelligence feeds, the inputs that feed the effectiveness evaluation's emerging-risk review.
Algorithmic-fairness tooling. For SDFs under DPDP section 10, tooling that assesses AI models for bias and discrimination, the technical expression of the algorithmic-software review as a treatment control.
Selection criteria
Select on: India-DPDP coverage (most global platforms are GDPR-heavy and DPDP-thin); integrated-with-distinction support (the ability to maintain the operational PIMS SoA alongside the ISMS SoA in a single platform); operational-SoA automation depth (the 78 Annex A controls as a first-class artefact, not a free-form text field); acceptance-workflow support (the signature chain and the threshold-based routing); effectiveness-evaluation support (the per-decision structure as a first-class artefact); SDF DPIA findings log support (for SDFs); algorithmic-software integration (for AI-driven processing activities); Consent Manager interoperability (where the Consent Manager ecosystem is in use); alert quality (low false-positive rate); and cost-to-value for the Indian growing-company segment.
Build vs buy
Most growing companies should buy the GRC platform and build the operational treatment methodology in-house with external advisory for the first cycle. The methodology is too organisation-specific to outsource end-to-end; the tooling is too time-intensive to build internally. The algorithmic-fairness tooling is the specialist decision, for SDFs, buy is typically more cost-effective than build, given the depth of statistical and machine-learning expertise required.
Policy and Procedure Templates
Operational Privacy Risk Treatment Policy (sample of our own drafting)
The organisation maintains an operational privacy risk treatment discipline that implements the Clause 6.1.3 planning-layer Risk Treatment Plan in the live PIMS environment. The DPO owns the Operational Procedure; the CISO co-owns the integrated-with-distinction interface for Annex A.3; the business-process owners own the residual-risk acceptance records for their processing activities. The operational SoA cross-walks every Annex A.1, A.2 and A.3 control to its applicability, justification, current-state implementation evidence, and exclusion reasoning. The operational residual-risk register reconciles with the 8.2 live Privacy Risk Register, the ROPA, the requirements register, the contract inventory, the change log and the breach register. Every risk above the risk-acceptance threshold has a signed residual-risk acceptance record. The treatment effectiveness evaluation runs at the planned interval and on material change. For Indian Significant Data Fiduciaries, the SDF DPIA findings log drives the operational treatment cycle, the algorithmic-software review operates as a treatment control on AI-driven processing activities, and the Consent Manager integrity controls are evidenced where a Consent Manager is in use. The operational residual-risk trajectory is reported to the management review (Clause 9.3).
Operational Privacy Risk Treatment Procedure (sample of our own drafting, summarised)
- Scope and inputs, every material risk in the 8.2 live Privacy Risk Register; the inputs are the 6.1.3 RTP, the 8.2 live register, the DPIA Register, the requirements register, the contract inventory, the change log, the threat-intelligence feed.
- Operational SoA maintenance, the four-column discipline; the reconciliation against the planning-layer SoA and the ISMS SoA; the currency alerts.
- Operational residual-risk register maintenance, the reconciliation discipline.
- Residual-risk acceptance workflow, the trigger; the record preparation; the signature chain (risk owner, DPO countersignature, top management sign-off at the highest threshold); the filing; the reporting; the review cadence.
- Treatment effectiveness evaluation cycle, the planned interval; the event-trigger re-evaluation; the per-decision structure.
- 8.2 → 8.3 loop wiring, the bi-directional integration.
- SDF DPIA findings log maintenance (for SDFs), the integration with the 8.2 DPIA Register; the per-finding treatment record; the effectiveness evaluation per finding.
- Consent Manager integrity controls (where applicable), the consent-record integrity control; the withdrawal-signal-honouring control; the interoperability-interface control.
- Algorithmic-software review as a treatment control (for AI-driven processing activities), the per-model release gate; the integration with the MLOps pipeline.
- Roles and responsibilities, the DPO, the CISO, the Legal, the business-process owners, the Internal Audit, the Change Advisory Board.
- Documented Information control, the Procedure, the operational SoA, the operational residual-risk register, the acceptance records, the effectiveness evaluation records; controlled per Clause 7.5.
Statement of Applicability Policy (sample of our own drafting)
The organisation maintains an operational Statement of Applicability as a living Documented Information artefact that cross-walks every Annex A.1, A.2 and A.3 control to its applicability status, its justification, its current-state implementation evidence, and its exclusion reasoning where not applicable. The operational SoA is updated on every risk-register change, every DPIA completion, every new or amended requirement, every Clause 6.3 change, and at the planned-interval cycle. The current-state discipline is enforced: a control marked applicable where the implementation is planned but not in operation is a nonconformity. The justified-exclusion discipline is enforced. The no-hypothetical-future-applicability discipline is enforced.
Integrated-with-Distinction Operating Statement (sample of our own drafting)
The organisation operates the operational PIMS SoA and the operational ISMS SoA (under ISO/IEC 27001:2022 Clause 6.1.3 / 8.3) under a single risk-register backbone with two distinct impact axes (principal-impact and organisational-impact) and two distinct control surfaces (Annex A.1 / A.2 for privacy controls; Annex A.3 and ISO/IEC 27002:2022 Annex A for security controls). Where the two SoAs cover the same security control (e.g. Annex A.3.23 secure authentication and ISO/IEC 27002:2022 control 8.5), the evidence is shared.
Residual-Risk Acceptance Statement (sample of our own drafting)
The organisation accepts the residual risk identified in Risk ID
<R-XXX>for processing activity<PA-XXX>with the residual-risk rating<high / critical>. The treatment option selected is<modify / retain / share>with the residual risk remaining above the acceptance threshold. The rationale:<the specific reason>. The conditions:<the mitigation commitments, the monitoring requirements>. The review date:<DD-Mon-YYYY>. The named risk owner<name, title>signs this acceptance. The DPO<name>countersigns. For risks at the highest threshold, top management sign-off is recorded in the management-review minutes.
Treatment Effectiveness Evaluation Statement (sample of our own drafting)
For the treatment decision on Risk ID
<R-XXX>: the projected residual risk was<rating>; the actual residual risk observed was<rating>. The control-operation evidence:<the testing results, the log reviews, the metrics, the incident records>. The DPIA conclusion<remained valid / was re-run with the revised projection>. The emerging-risk review identified<no new risks / the following new risks>. The effectiveness conclusion:<effective / partially effective / ineffective>. The treatment revision:<confirmed / adjusted / re-engineered>.
SDF DPIA Findings Log Operating Statement (sample of our own drafting)
As a Significant Data Fiduciary designated under DPDP Act 2023 section 10, the organisation maintains the SDF DPIA findings log as the operational expression of the SDF DPIA programme. The SDF DPIA is performed every 12 months under the Clause 8.2 operational discipline; the findings are recorded in the log. For each finding, the operational treatment under Clause 8.3 is recorded (the treatment option, the controls applied, the operational implementation, the residual-risk acceptance where applicable, the effectiveness evaluation). The algorithmic-software review operates as a treatment control on AI-driven processing activities. The Consent Manager integrity controls (DPDP section 2(1)(g) and section 6) are evidenced where a Consent Manager is in use. The DPO based in India is accountable to the Board for the SDF DPIA findings log.
Operational Risk Treatment and Effectiveness
This section is the operational core of Clause 8.3. It expands on the operational discipline introduced in Section 7 and provides the worked detail for the four treatment options, the operational SoA discipline, the residual-risk acceptance record, and the effectiveness evaluation.
The four treatment options, the operational cycle
The four treatment options inherited from ISO 31000:2018 / ISO/IEC 27005:2022 are operationalised as follows:
Option 1, Modify (apply controls). The canonical option for most privacy risks. The modify option selects controls from Annex A.1 (controller), A.2 (processor) and A.3 (security) to reduce the likelihood or the principal-impact / organisational-impact. The operational implementation discipline: the controls are actually operating in production (the operational SoA documents the current-state evidence); the residual-risk projection (from the 6.1.3 RTP) is tested by the effectiveness evaluation; the controls are revised when the effectiveness evaluation shows the projection did not hold. Worked examples: a marketing-lead scoring engine that triggers the WP248 "evaluation or scoring" criterion is modified by A.1.4.5 (PII minimisation) and A.1.4.10 (PII transmission controls) plus the algorithmic-software review (for SDFs under DPDP section 10), operational evidence is the data-minimisation review record, the algorithmic-software review report, the model-release gate sign-off; a cross-border analytics flow is modified by A.1.5.2 (basis for PII transfer), supplementary measures (encryption, pseudonymisation), the standard contractual clauses, and the transfer-impact assessment, operational evidence is the executed SCCs, the TIA, the supplementary-measures deployment record, the transfer register; an AI-driven fraud-detection model is modified by the algorithmic-software review, A.1.3.11 (automated decision-making, the principal's right to contest), and the transparency control, operational evidence is the algorithmic-software review report, the contest-handling workflow, the transparency notice.
Option 2, Retain (accept the residual risk). The option for residual risks above the acceptance threshold where modify is not cost-effective or avoid is not commercially viable. Requires a signed residual-risk acceptance record by the named risk owner (Move 3 above). The retain option is operationally disciplined: the acceptance record includes the rationale, the conditions and the review date; the effectiveness evaluation tests whether the residual risk remains within the accepted envelope; the acceptance is withdrawn if the residual risk climbs above the accepted rating. Worked examples: an employee-monitoring tool with a residual-medium rating is retained pending the works-council consultation, with the HR lead as the risk owner signing the acceptance record with a six-month review date; a legacy HR information system with a residual-high rating on the data-minimisation dimension is retained pending the system replacement scheduled in eighteen months, with the HR lead signing the acceptance record with an eighteen-month review date and the replacement-schedule mitigation commitment.
Option 3, Avoid (terminate the processing activity). The option for risks that exceed the risk appetite and cannot be modified. Worked examples: a behavioural-monitoring feature on a K-12 platform triggers the DPDP section 9 prohibition on behavioural monitoring of children, the only defensible treatment is avoid, and the feature is terminated (operational evidence is the feature-decommissioning record, the user-notification record, the data-deletion record); a cross-border analytics flow to a destination added to the DPDP section 16 negative list, the only defensible treatment is avoid unless an exception applies, and the flow is terminated.
Option 4, Share (transfer part of the risk). The option to transfer part of the risk through insurance (cyber-insurance with privacy-liability coverage) or through contractual allocation (the processor agreement's indemnity, the sub-processor's liability cap, the joint-controller arrangement's responsibility allocation). Share does not eliminate the risk; it allocates the financial consequence. The principal-impact is not transferable, the organisation remains accountable to the principal regardless of the contractual allocation. Worked examples: a residual-high risk on a payment-processing flow is shared through cyber-insurance with privacy-liability coverage; a processor-side risk on a customer-data processing activity is shared through the customer DPA's indemnity clause.
The operational Statement of Applicability, the worked detail
The operational SoA is the load-bearing 8.3 artefact. The Singahi operational SoA template (toolkit doc 03) provides the structure with all 78 Annex A controls pre-populated. The SoA fields per control:
- Control ID, e.g. A.1.2.4.
- Control title (paraphrased), e.g. "Obtain and record consent".
- Applicability, applicable / not applicable.
- Justification, for applicable, the risk ID(s) and / or the requirement ID(s). For not-applicable, the documented exclusion reason.
- Implementation state (current-state, evidenced), the procedure reference, the system reference, the records reference, the owner, the last review date.
- Exclusion reasoning (for not-applicable), specific and defensible.
- Last-update date, when the row was last reviewed.
- Last-update reason, the event that drove the update (planned-interval cycle, trigger event, treatment implementation, effectiveness evaluation finding).
The three discipline rules (current-state only, justified exclusions, no hypothetical-future-applicability) are enforced per row. The reconciliation discipline: the operational SoA reconciles with the planning-layer SoA (6.1.3) on applicability; the operational SoA adds the implementation column. The operational SoA reconciles with the ISMS SoA (ISO/IEC 27001:2022 Clause 6.1.3 / 8.3) on the Annex A.3 controls.
The residual-risk acceptance record, the worked detail
The residual-risk acceptance record is the discipline most organisations miss. The Singahi residual-risk acceptance record template (toolkit doc 05) provides the structure. The fields per record:
- Acceptance ID, unique identifier.
- Risk ID, cross-referenced to the 8.2 live Privacy Risk Register.
- Risk description, the harm scenario and the affected PII principal class.
- Residual-risk rating, the rating after the operational treatment (high / critical, low and medium do not require an acceptance record).
- Treatment option selected, modify (with the residual risk remaining above the threshold), retain, share.
- Rationale, the specific reason the residual risk is acceptable. Not boilerplate.
- Conditions, the mitigation commitments, the monitoring requirements.
- Review date, the next scheduled review (annual; quarterly for SDFs and listed entities).
- Risk-owner signature, name, title, signature, date.
- DPO countersignature, for risks above a higher threshold.
- Top management sign-off, for risks at the highest threshold (recorded in the management-review minutes).
- Status, open / withdrawn / closed.
The acceptance-record coverage discipline: every risk above the threshold has a signed acceptance. The reporting discipline: the open acceptance record count is reported to the management review. The review discipline: the acceptance is reviewed at the planned interval and on material change; the review re-tests whether the residual risk remains acceptable.
The treatment effectiveness evaluation, the worked detail
The effectiveness evaluation is the operational loop that closes the PIMS. The Singahi treatment effectiveness evaluation template (toolkit doc 06) provides the per-decision structure. The evaluation runs at the planned interval and on material change. The fields per evaluation:
- Evaluation ID, unique identifier.
- Risk ID, cross-referenced to the 8.2 live Privacy Risk Register and the 8.3 operational residual-risk register.
- Treatment decision under evaluation, the treatment option, the controls applied.
- Projected residual risk, from the 6.1.3 RTP.
- Actual residual risk, observed in operation after the treatment cycle.
- Control-operation evidence, the control-testing results, the log reviews, the metrics, the incident records, the audit findings.
- DPIA conclusion currency, did the conclusion remain valid? If re-run under 8.2, the revised projection.
- Emerging-risk review, the threat-intelligence feed, the regulator-engagement feed, the post-incident review feed.
- Effectiveness conclusion, effective / partially effective / ineffective.
- Treatment revision, confirmed / adjusted / re-engineered.
- Cross-references, to the 8.2 re-assessment cycle for ineffective treatments; to the 6.1.3 RTP update for systematically wrong projections; to the Clause 10.2 corrective action for control-operation failures; to the Clause 10.1 continual improvement for systemic findings.
- Evaluator signature, name, title, date.
- DPO sign-off, date.
The operational treatment register (the consolidated view)
| Risk | Source | Treatment option | Controls applied | Residual risk | Acceptance | Effectiveness |
|---|---|---|---|---|---|---|
| Algorithmic-bias in the credit-scoring engine | AI-driven profiling on protected-class-adjacent features | Modify + Retain | A.1.3.11 (ADM); A.1.4.5 (minimisation); algorithmic-software review | High (non-discrimination) | Signed by analytics lead + DPO countersign + top management | Effective after the second review cycle |
| Cross-border analytics flow without TIA | US sub-processor; non-adequacy destination | Modify | A.1.5.2; SCCs + supplementary measures + TIA | Medium | n/a | Effective |
| Children's-data exposure in K-12 platform | Behavioural monitoring; no verifiable parental consent | Avoid | Feature terminated under DPDP s.9 | n/a | n/a | n/a |
| Infringing-instruction from controller customer | Customer pressure to breach DPDP | Modify | A.2.2.5 process | Medium | n/a | Effective |
| Breach-notification clock missed | Unclear ownership; unclear clock per data set | Modify | A.3.12; dual-clock playbook | Medium | n/a | Partially effective, additional controls committed |
| Consent-quality failure (withdrawal asymmetry) | 14-day withdrawal vs one-click give | Modify | A.1.2.3 + A.1.3.5; Consent Manager integration | Medium | n/a | Effective after Consent Manager integration |
| Employee-monitoring overreach | Surveillance beyond legitimate purpose | Modify + Retain | A.1.4.2; A.1.4.3 | High (dignity) | Signed by HR lead | Partially effective, works-council consultation pending |
| Joint-controller arrangement undocumented | Co-branded product; loyalty programme | Modify | A.1.2.8 contract | Medium | n/a | Effective |
| Operational SoA future-state rows | Controls marked applicable where implementation planned | Modify | Operational SoA refresh | Low after refresh | n/a | Effective |
| Unsigned residual-risk acceptance records | Acceptance records missing | Modify | Acceptance workflow | Low after workflow | n/a | Effective |
The high-impact, high-likelihood operational treatments to get right first are: the operational SoA currency (no future-state rows); the residual-risk acceptance coverage (every above-threshold risk signed); the effectiveness evaluation depth (not a tick-box exercise); the SDF DPIA findings log (for SDFs); the Consent Manager integrity controls (where applicable). These five account for most of the 8.3 audit nonconformities in the Indian growing-company segment.
Audit and Compliance Checklist
The 28 questions below cover the audit-evidence surface for Clause 8.3. Expected evidence and red flags noted. Most can be answered from the toolkit doc 04 audit-evidence checklist.
- Is there an Operational Privacy Risk Treatment Procedure (the 8.3 artefact)? Expected: dated, version-controlled, signed by the DPO with sponsor authority. Red flag: missing.
- Is the Operational Procedure distinct from the 6.1.3 planning-layer RTP? Red flag: single document (the canonical conflation).
- Does the Operational Procedure document the operational SoA maintenance rules (who updates, when, with what evidence; the reconciliation discipline)?
- Does the Operational Procedure document the residual-risk acceptance workflow (the signature chain, the thresholds, the conditions)?
- Does the Operational Procedure document the treatment effectiveness evaluation cycle (the planned interval, the event-trigger re-evaluation, the per-decision structure)?
- Does the Operational Procedure document the operational residual-risk register maintenance rules (the reconciliation against the 8.2 live register, the ROPA, the requirements register, the contract inventory, the change log, the breach register)?
- Does the Operational Procedure document the SDF DPIA findings log maintenance for SDFs (DPDP section 10)?
- Does the Operational Procedure document the Consent Manager integrity controls (DPDP section 2(1)(g) and section 6)?
- Is there an operational Statement of Applicability cross-walking every Annex A.1 / A.2 / A.3 control? Expected: dated, version-controlled.
- What is the last-update date of the operational SoA? Red flag: same as the last surveillance audit.
- For each applicable control, is the justification documented (the risk ID or the requirement ID)?
- For each not-applicable control, is the exclusion reasoning specific and defensible? Red flag: boilerplate ("not relevant") or missing.
- Does each applicable control reflect current-state implementation (not future-state)? Red flag: any control marked applicable where the implementation is "in progress" or "planned".
- Are any controls marked applicable on a hypothetical future relationship? Red flag: A.1.2.8 joint controller marked applicable because "we may enter an arrangement next year".
- Is the operational SoA reconciled with the 6.1.3 planning-layer SoA on applicability? With the ISMS SoA on Annex A.3?
- Is there an operational residual-risk register with every material risk recorded?
- Does each register entry record the treatment option, the controls applied (cross-referenced to the SoA rows), the residual risk, the risk owner, the acceptance record (where applicable), the review date, the effectiveness-evaluation cross-reference?
- Is every risk above the acceptance threshold covered by a signed residual-risk acceptance record? Red flag: above-threshold risks without a signed acceptance.
- Does each acceptance record include the rationale (specific, not boilerplate), the conditions, the review date, the risk-owner signature?
- For risks at the higher threshold, is the DPO countersignature present? For risks at the highest threshold, is the top management sign-off recorded in the management-review minutes?
- Is there a treatment effectiveness evaluation per material treatment decision?
- Does each effectiveness evaluation record the projected residual risk, the actual residual risk, the control-operation evidence, the DPIA conclusion currency, the emerging-risk review, the conclusion, the treatment revision?
- For ineffective treatments, was corrective action taken under Clause 10.2 and a re-assessment under 8.2?
- For Indian SDFs, is the SDF DPIA findings log maintained with each finding treated under 8.3?
- For AI-driven processing activities, is the algorithmic-software review operating as a treatment control? For SDFs, is it integrated with the MLOps pipeline?
- For organisations using a Consent Manager, are the Consent Manager integrity controls evidenced (the consent-record integrity control, the withdrawal-signal-honouring control, the interoperability-interface control)?
- Is the operational residual-risk register reconciled with the 8.2 live register, the ROPA, the requirements register, the contract inventory, the change log, the breach register?
- Has the operational residual-risk trajectory been reported to the management review (Clause 9.3), the high-and-critical count, the open acceptance count, the operational SoA currency, the effectiveness evaluation results, the SDF DPIA findings log status, the Consent Manager integrity control status?
Evidence the auditor will physically request
- The dated and signed Operational Privacy Risk Treatment Procedure.
- The 6.1.3 planning-layer RTP (for the demarcation test).
- The operational Statement of Applicability (with the four-column discipline enforced).
- The operational residual-risk register (with the acceptance-record cross-reference populated for above-threshold risks).
- The residual-risk acceptance records (signed by the named risk owners; with the DPO countersignatures and the top-management sign-offs where applicable).
- The treatment effectiveness evaluation records (with the per-decision structure populated).
- The management-review minutes showing the operational residual-risk trajectory input.
- Sample reconciliations: the operational SoA row for one sampled Annex A.1 / A.2 control cross-referenced to the matching risk in the 8.2 live register, the matching ROPA entry, the matching requirements-register entry, the matching operational residual-risk register entry, the matching acceptance record, the matching effectiveness evaluation.
- The SDF-specific evidence (where applicable): the SDF DPIA findings log; the algorithmic-software review reports; the Consent Manager integrity control evidence; the independent data audit report.
- The integrated-with-distinction evidence: the operational PIMS SoA and the operational ISMS SoA (ISO/IEC 27001:2022 Clause 6.1.3 / 8.3) reconciled on the Annex A.3 / ISO/IEC 27002:2022 controls.
Common Stage-1 nonconformities the auditor will write up
- NC 1: Operational Procedure does not exist; only the 6.1.3 RTP is in the evidence set. Major NC. Remediation: write the Operational Procedure, four to eight weeks.
- NC 2: 6.1.3 / 8.3 conflation, single document covering both. Major NC on 8.3 (and frequently on 6.1.3 as well). Remediation: separate the artefacts, four to eight weeks.
- NC 3: Operational SoA documents future-state controls. Major NC. Remediation: operational SoA refresh, four to twelve weeks depending on the count.
- NC 4: Operational SoA has unjustified exclusions. Minor or major NC. Remediation: exclusion-reasoning discipline, two to four weeks.
- NC 5: Operational SoA has hypothetical-future-applicability rows. Major NC. Remediation: downgrade to not-applicable with a documented exclusion reason; revisit on material change.
- NC 6: Above-threshold risks without signed residual-risk acceptance records. Major NC. Remediation: stand up the acceptance workflow, four to eight weeks.
- NC 7: Effectiveness evaluation missing or a tick-box exercise. Minor or major NC. Remediation: stand up the cycle, six to twelve weeks.
- NC 8: Operational SoA last-update date matches the last surveillance audit. Major NC. Remediation: stand up the event-trigger update discipline, six to twelve weeks.
Metrics and KPIs
Figure · Measures
The measures that show Clause 8.3 is working
- Operational SoA currency100%Periodic
- Operational SoA future-state rowszeroPeriodic
- Operational SoA unjustified exclusionszeroPeriodic
- Operational SoAzeroPeriodic
- Operational residual-risk register coverage100%Periodic
- Operational SoA currency, percentage of applicable controls whose implementation state was reviewed within the last twelve months (or the planned interval). Target: 100%.
- Operational SoA future-state rows, count of controls marked applicable where the implementation is "in progress" or "planned". Target: zero. Red flag: any non-zero count indicates nonconformity risk.
- Operational SoA unjustified exclusions, count of not-applicable controls with missing or boilerplate exclusion reasoning. Target: zero.
- Operational SoA hypothetical-future-applicability rows, count of controls marked applicable on a hypothetical future relationship. Target: zero.
- Operational residual-risk register coverage, percentage of risks in the 8.2 live register with a corresponding entry in the 8.3 operational register. Target: 100% (or 100% of risks above the operational treatment threshold).
- Residual-risk acceptance coverage, percentage of risks above the threshold with a signed acceptance record. Target: 100%.
- Open acceptance record count, the count of risks currently accepted above the threshold. Target: downward trend; spikes investigated at the management review.
- Acceptance record review currency, percentage of open acceptance records reviewed within the planned interval. Target: 100%.
- Effectiveness evaluation coverage, percentage of material treatment decisions with a current effectiveness evaluation. Target: 100%.
- Effectiveness evaluation conclusion distribution, the percentage split between effective, partially effective, ineffective. Target: majority effective; partially effective and ineffective investigated.
- Ineffective treatment corrective-action latency, median time from ineffective conclusion to corrective action under Clause 10.2. Target: under thirty days.
- Operational residual-risk trajectory, quarter-on-quarter change in the count of high and critical residual risks. Target: downward trend.
- Operational residual-risk register reconciliation, percentage of risks reconciled with the 8.2 live register, the ROPA, the requirements register, the contract inventory, the change log, the breach register. Target: 100%.
- SDF DPIA findings log coverage, for SDFs, percentage of SDF DPIA findings with a treatment record under 8.3. Target: 100%.
- Algorithmic-software review cadence, for AI-driven processing activities, percentage with a current algorithmic-software review report operating as a treatment control. Target: 100% (mandatory for SDFs under DPDP section 10).
Common Pitfalls and Audit Failures
Pitfall 1, The 6.1.3 / 8.3 conflation. A single document covers both the planning-layer RTP and the operational-layer execution. The operational artefact set (the operational SoA, the residual-risk register, the acceptance records, the effectiveness evaluation) is missing. The single most common 8.3 finding. Treatment: Move 1 separation (the Operational Procedure as a distinct artefact).
Pitfall 2, The future-state SoA. The operational SoA documents controls as applicable where the implementation is "in progress", "planned", or "rolling out next quarter". The canonical 6.1.3 / 8.3 audit failure flagged in tier-1 practitioner commentary. Treatment: Move 2 operational SoA refresh, downgrade to not-applicable with a documented exclusion reason, or commit to a remediation target date and remove the row from the audit-evidence set until the control is live.
Pitfall 3, The unjustified-exclusion SoA. Not-applicable controls have missing or boilerplate exclusion reasoning. Treatment: the exclusion-reasoning discipline, every not-applicable control has a specific, defensible reason.
Pitfall 4, The hypothetical-future-applicability SoA. Controls marked applicable on a hypothetical future relationship (the A.1.2.8 joint-controller example is the canonical case). Treatment: downgrade to not-applicable; revisit on material change.
Pitfall 5, The unsigned residual-risk acceptance. Risks above the threshold are listed but not signed by the named risk owner. The acceptance-record discipline is missing. Treatment: Move 3 acceptance workflow.
Pitfall 6, The tick-box effectiveness evaluation. The effectiveness evaluation exists but is a tick-box exercise without the control-operation evidence. Treatment: Move 4 effectiveness evaluation depth, the per-decision structure populated with the projected vs actual residual risk, the control-operation evidence, the DPIA currency, the emerging-risk review.
Pitfall 7, The annual-only operational SoA. The operational SoA is updated in the thirty days before the surveillance audit; the rest of the year the SoA is dark. Treatment: the event-trigger update discipline (Move 2), wire the seven-trigger catalog from the Clause 6.3 guide into the operational SoA update workflow.
Pitfall 8, The operational-SoA-without-reconciliation. The operational SoA exists but does not reconcile with the 6.1.3 planning-layer SoA, the ISMS SoA, or the operational residual-risk register. Treatment: the reconciliation discipline (Move 5).
Pitfall 9, The SDF-oblivion. The organisation crosses the SDF threshold (DPDP section 10) without realising it; the SDF DPIA findings log is missing; the algorithmic-software review is not done. Treatment: SDF-designation analysis in the annual review; the SDF DPIA findings log on standby.
Pitfall 10, The algorithmic-software review gap. AI-driven processing activities without the algorithmic-software review as a treatment control. Section 10 exposure for SDFs; reputational risk for all. Treatment: algorithmic-software review pipeline; the integration with the MLOps pipeline.
Pitfall 11, The Consent Manager integrity control gap. The organisation uses a Consent Manager under DPDP section 2(1)(g) and section 6 but the integrity controls (consent-record integrity, withdrawal-signal-honouring, interoperability-interface) are not evidenced in the operational SoA. Treatment: the Consent Manager integrity control evidence discipline.
Pitfall 12, The treatment-without-implementation. The 6.1.3 RTP selects the modify option with specific controls, but the controls are not actually implemented in the operational processes (the operational SoA documents them as applicable but the implementation evidence is missing). Treatment: implementation discipline; evidence in the operational SoA implementation column.
Pitfall 13, The methodology-without-competence. The Operational Procedure exists but the DPO, the CISO and the process owners are not trained on it. Treatment: training programme under Clause 7.2.
Pitfall 14, The board-invisible operational treatment. The operational residual-risk trajectory is not reported to the board / Risk Management Committee (for listed entities and SDFs). Treatment: board-on-a-page summary every cycle; the management review (Clause 9.3).
Pitfall 15, The effectiveness-evaluation-without-feedback. The effectiveness evaluation exists but the findings do not feed back into the 8.2 re-assessment cycle or the 6.1.3 RTP update. Treatment: the bi-directional 8.2 → 8.3 loop wiring (Move 6).
Pitfall 16, The acceptance-record-without-review. The residual-risk acceptance records exist but are never reviewed at the planned interval. Treatment: the acceptance-record review discipline (Move 3 step 7).
Pitfall 17, The share-option-misunderstanding. The share option (insurance, contractual allocation) is treated as risk elimination rather than risk transfer. The principal-impact is not transferable. Treatment: the share-option discipline, the organisation remains accountable to the principal regardless of the contractual allocation.
Pitfall 18, The avoid-option-avoidance. The avoid option is not exercised for risks that exceed the risk appetite and cannot be modified (e.g. DPDP section 9 children's-data behavioural monitoring). The organisation continues the processing under a retain or modify treatment that does not address the section 9 prohibition. Treatment: the avoid-option discipline, terminate the processing activity that generates the risk.
Illustrative Scenario 1: Failure, Public-Health Contact-Tracing Healthtech and the Future-State SoA Behind an Algorithmic Triage Engine (Illustrative)
Illustrative scenario, a composite example for guidance, not a specific Singahi engagement or a verified outcome. It is set after 13 May 2027, when the DPDP Act's duties and the Board's inquiry and penalty powers take effect.
Illustrative scenario. Aarogya-style healthtech in this scenario is a fictional Bengaluru-based secondary-care network offering telemedicine, inpatient coordination, and an AI-driven triage engine; the name is descriptive only and the facts are composite from publicly reported sector patterns. Nothing here should be attributed to any real organisation, including any government-deployed application with a similar-sounding name.
The healthtech built its PIMS in 2024 ahead of an ISO/IEC 27701:2019 certification push. The 6.1.3 Risk Treatment Plan was a 24-page document covering the planning-layer treatment decisions; the operational SoA was a separate document but it had been drafted ahead of the Stage 2 audit and not refreshed since. Of the 78 Annex A controls, sixty-eight were marked applicable. The operational SoA's implementation column for twenty-three of those sixty-eight controls read "in progress" or "planned Q1 2028", the future-state failure. The residual-risk acceptance records for the eleven risks above the threshold existed but were signed by the DPO rather than the named business-process owners, the wrong-signatory failure. The effectiveness evaluation was a single-page tick-box exercise, the tick-box failure.
The AI-driven triage engine was launched in late 2024 with a DPIA that predated the model's third-generation upgrade by fourteen months. The DPIA was never refreshed. The 6.3 change-control loop did not flag the model upgrade as a trigger event; the operational SoA was not updated; the effectiveness evaluation was not re-baselined. The algorithmic-software review was not done.
In February 2028 a published investigation alleged that the third-generation triage engine was systematically under-triaging patients from a particular demographic cohort, with a measurable adverse effect on the time-to-treatment for the under-triaged cohort. The principal-impact was severe on the non-discrimination and safety dimensions. The Data Protection Board of India preliminary inquiry (under section 18) identified the defective operational treatment discipline as the root cause, the operational SoA had not been updated since the certification audit, the controls cited as treating the algorithmic-bias risk (A.1.3.11 automated decision-making; A.1.4.5 PII minimisation; the algorithmic-software review) were documented as "in progress" in the operational SoA at the time of the model upgrade, and the effectiveness evaluation had not been re-baselined.
The certification body issued a major nonconformity on Clause 8.3 at the next surveillance audit, cascading into nonconformities on 6.1.3 (the planning-layer RTP and the operational SoA diverged), 6.3 (the model upgrade did not trigger a treatment revision), 8.2 (the DPIA was stale), 9.1 (the continuous monitoring did not surface the bias), 9.3 (the management review did not test the operational treatment), 10.2 (the corrective action was reactive), Annex A.1.3.11 (the ADM control was not operating), A.1.4.5 (the minimisation control was not operating), and Annex A.1.2.6 (the DPIA was stale). The certificate was suspended pending remediation.
The remediation re-engineered the operational treatment discipline (the 6.1.3 / 8.3 separation, the operational SoA refreshed with zero future-state rows, the residual-risk acceptance workflow with the named-business-process-owner signature chain, the effectiveness evaluation cycle with the per-decision depth, the algorithmic-software review pipeline integrated with the MLOps release gate).
The lessons: the operational SoA is only as good as its currency; the residual-risk acceptance is only as good as the named-owner signature; the effectiveness evaluation is only as good as the control-operation evidence; the future-state row is a nonconformity waiting to be written; the algorithmic-software review is not optional for AI-driven processing activities; the seven-trigger catalog from the Clause 6.3 guide must be wired into the operational SoA update workflow.
Illustrative Scenario 2: Success, Tarang Fintech Operationalises the 8.3 Treatment Loop (Illustrative)
Illustrative scenario. Tarang Fintech is a fictional Bengaluru-based wealth-management platform with two thousand one hundred staff, a SEBI-registered investment-advisory subsidiary, and approximately one-point-eight million retail-investor accounts; the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation.
Tarang Fintech ran an integrated ISO/IEC 27001:2022 + ISO/IEC 27701:2019 programme with a single risk register inherited from the ISMS. The operational SoA existed but had been last updated for the 2019 certification cycle; thirty-one of the seventy-three applicable controls had future-state implementation columns. The residual-risk acceptance records existed for four risks; eleven risks above the threshold were unsigned. The effectiveness evaluation was a one-page annual exercise. The 6.1.3 / 8.3 demarcation was not made.
In Q4 2025 the DPO commissioned an 8.3 refresh ahead of the 27701:2025 transition. The workshop surfaced six material shifts (worked example in Section 7.7 details the operational shape): the 6.1.3 / 8.3 separation made; the operational SoA refreshed to zero future-state rows (eleven downgraded to not-applicable with documented exclusion reasons; twenty committed to remediation target dates and removed from the audit-evidence set until the controls were live); the integrated-with-distinction posture formalised with the operational PIMS SoA reconciled with the operational ISMS SoA on the Annex A.3 / ISO/IEC 27002:2022 controls; the residual-risk acceptance workflow stood up with twenty-three signed records; the treatment effectiveness evaluation cycle operationalised across thirty-eight material treatment decisions (thirty-one effective; five partially effective; two ineffective, triggering corrective action and 8.2 re-assessment); and the Consent Manager integrity controls evidenced for the consent-capture flow migrating to a Consent Manager under DPDP section 2(1)(g) and section 6.
The outcome: the integrated-with-distinction posture cut parallel-pattern reconciliation overhead; the operational SoA refresh (zero future-state rows) avoided Stage 1 nonconformity remediation cost; the residual-risk acceptance workflow avoided the canonical 8.3 audit failure (estimated eight to twelve lakh rupees and four to eight weeks of timeline); the effectiveness evaluation cycle surfaced the two ineffective treatments early enough to remediate before public exposure (avoiding DPDP section 8(5) penalty exposure and reputational damage on the retail-investor onboarding flow); the Consent Manager integrity control evidence positioned Tarang for the Consent Manager integration go-live without an additional remediation cycle.
The lessons: the 6.1.3 / 8.3 separation is the highest-use operational decision for most Indian growing companies; the operational SoA refresh (zero future-state rows) is the cheapest remediation move; the residual-risk acceptance workflow (named-owner signature chain) is the discipline most organisations miss; the effectiveness evaluation cycle (per-decision depth) closes the operational loop; the Consent Manager integrity control evidence is the 2026 / 2027 maturity dimension as the Consent Manager ecosystem emerges.
Multi-Framework Mapping
| 27701:2025 8.3 theme | GDPR article | DPDP Act (India) section | NIST Privacy Framework | SOC 2 TSC | ISO 27001:2022 / 27005 / 31000 / 29134 | ISO 29100 principle |
|---|---|---|---|---|---|---|
| Operational treatment cycle (modify / retain / avoid / share) | Art 24 (controller responsibility); Art 32 (security) | s.8(5) safeguards (modify); s.17 exemptions (avoid) | Control-P (Data-processing management; risk response) | CC3.3 (Risk response) | ISO 31000:2018; 27005:2022 (the four-option taxonomy) | Accountability; Security safeguards |
| Operational Statement of Applicability (current-state) | Art 5(2) accountability; Art 24(1) | s.8(5) safeguards (implemented) | Govern-P (Risk-management strategy); Control-P | CC3.3 (Risk response) | 27001 Clause 8.3 (infosec risk treatment) | Accountability |
| Operational SoA reconciliation with ISMS SoA (Annex A.3) | Art 32 (security of processing) | s.8(5) reasonable security safeguards | Govern-P + Protect-P | CC3.3 + CC6 (Security) | 27001 Clause 8.3 + 27002:2022 | Security safeguards |
| Residual-risk acceptance record (signed by named owner) | Art 5(2) accountability; Art 24(1) | s.8 accountability (board-level); s.10 SDF | Govern-P (Risk-management strategy) | CC3.3 + CC4.2 (Monitoring) | ISO 31000:2018 (risk acceptance) | Accountability |
| Treatment effectiveness evaluation | Art 24(1) (review and update); Art 32(1)(d) (regular testing) | s.8(5) safeguards (regular review); s.10 SDF independent audit | Control-P (Privacy testing) + Identify-P (Risk Assessment review) | CC4.1 / CC4.2 (Monitoring) | 27001 Clause 9.1 + Clause 8.3; 27005:2022 | Accountability; Security safeguards |
| Algorithmic-software review as a treatment control | Art 22 ADM; Art 35(3)(a) DPIA mandatory | Rule 13(3) algorithmic-software review | Control-P (Disassociated processing, ADM) | CC3.3 + P8.0 (Monitoring) | 27005:2022 + ISO/IEC 42001:2023 | Non-discrimination (emerging) |
| Consent Manager integrity controls (DPDP-specific) | (no direct EU analogue) | s.2(1)(g) + s.6 Consent Manager | Control-P (Consent management) | CC6 + P-criteria | 29134:2017 + 27018:2019 | Consent & choice |
| SDF DPIA findings log (SDF overlay) | (no direct EU SDF analogue) | s.10 SDF DPIA every 12 months | Govern-P + Control-P | CC3.3 + CC4 | 29134:2017 + 27006 / 27706 (cert scheme) | Accountability |
| 8.2 → 8.3 operational loop (assess-treat-verify) | Art 24 (planning) + Art 32 (operation) + Art 35(11) (DPIA review) | s.4 (grounds) + s.8(5) + s.10 (SDF DPIA) | Identify-P + Control-P + Govern-P (闭环) | CC3 (planning) + CC3.3 (response) + CC4 (monitoring) | 27001 Clause 6.1.2 / 8.2 + Clause 8.3 + Clause 9.1 | Accountability |
| 6.1.3 / 8.3 demarcation (the second-most-confused pair) | Art 24 (planning) vs Art 32 + Art 35(11) (operation) | s.4 (grounds) vs s.8(5) + s.10 (operation) | Identify-P (Govern) vs Control-P | CC3 (planning) vs CC3 + CC4 (operation) | 27001 Clause 6.1.3 vs Clause 8.3 | Accountability |
| Avoid option for prohibited processing (DPDP s.9 children) | Art 8 child consent; Art 22 ADM | s.9 children & persons with disability (prohibition) | Control-P (Disassociated processing) | CC3.3 | 27005:2022 | Consent & choice; Use limitation |
| Share option (insurance / contractual allocation) | Art 32 (security, does not transfer accountability) | s.8(5) safeguards (does not transfer accountability); contractual allocation under s.7 | Govern-P (Risk-management strategy) | CC3.3 + CC9 (Risk mitigation) | ISO 31000:2018 | Accountability |
| Breach-response control (dual-clock pattern) | Art 33 (72h to SA); Art 34 (to data subjects) | s.8(6) (without delay to Board; detailed report within 72 hours) + CERT-In 6h | Identify-P + Protect-P (recovery) | CC7.3 + CC7.4 | 27002 5.24–5.27; 27001 Clause 8.3 (incident-response control implementation) | Security safeguards |
The densest cross-framework mappings are at the operational-SoA row (GDPR Article 5(2) accountability; DPDP section 8(5); NIST PF Govern-P / Control-P; ISO/IEC 27001:2022 Clause 8.3), the residual-risk-acceptance row (GDPR Article 5(2); DPDP section 8; ISO 31000:2018), and the effectiveness-evaluation row (GDPR Article 24(1) and 32(1)(d); DPDP section 8(5) regular review; ISO/IEC 27001:2022 Clause 9.1 + Clause 8.3). The unique-to-India rows are the Consent Manager integrity controls (DPDP section 2(1)(g) + section 6) and the SDF DPIA findings log (DPDP section 10), no direct GDPR analogue exists at the Consent Manager level or the SDF designation level.
Implementation Roadmap
30 days
- Decide the 6.1.3 / 8.3 separation (Move 1). Issue or refresh the Operational Procedure as a distinct artefact.
- Run the operational-SoA reconciliation workshop (Move 2). Identify the future-state rows; downgrade or commit to remediation target dates.
- Document the residual-risk acceptance workflow (Move 3). Identify the above-threshold risks without signed acceptance records.
- Document the treatment effectiveness evaluation cycle (Move 4). Identify the material treatment decisions due for evaluation.
90 days
- Complete the operational SoA refresh with zero future-state rows (Move 2). Every applicable control has current-state evidence; every not-applicable control has a specific exclusion reason.
- Complete the residual-risk acceptance records for every above-threshold risk (Move 3). The signature chain operationalised; the first cycle of acceptance records filed.
- Run the first treatment effectiveness evaluation cycle (Move 4). The per-decision structure populated for the top ten to fifteen material treatment decisions.
- For SDFs, stand up the SDF DPIA findings log (Move 5). Wire it into the 8.2 DPIA Register.
- For organisations using a Consent Manager, document the Consent Manager integrity controls (Move 5).
180 days
- Complete the operational residual-risk register (Move 5). The register reconciled with the 8.2 live register, the ROPA, the requirements register, the contract inventory, the change log.
- Run the second effectiveness evaluation cycle. Apply the treatment revisions from the first cycle's partially-effective and ineffective findings.
- Wire the operational residual-risk trajectory into the management review (Clause 9.3). The DPO presents the high-and-critical residual-risk count, the open acceptance record count, the operational SoA currency, the effectiveness evaluation results.
- Update the awareness programme to reference the operational controls (Clause 7.3) and the training programme on the operational treatment methodology (Clause 7.2).
- For SDFs, complete the algorithmic-software review on the AI-driven processing activities and integrate it with the MLOps pipeline.
12 months
- Run the first full annual review at the management review (Clause 9.3).
- Update the operational SoA to reflect the year's risk-register changes, DPIA completions, new or amended requirements, and Clause 6.3 changes.
- Run an internal-audit test against the Section 11 checklist (Clause 9.2).
- Calibrate the metrics against the Section 12 targets.
- For SDFs, complete the first SDF DPIA findings log annual review and the algorithmic-software review annual cycle.
FAQ
Q1. We already have an ISO/IEC 27001:2022 ISMS Statement of Applicability. Can we reuse it for 27701 8.3?
Yes, with the integrated-with-distinction posture. The ISMS SoA covers the ISO/IEC 27002:2022 Annex A controls; the PIMS operational SoA adds the privacy-specific controls, the Annex A.1 (controllers) and A.2 (processors). The Annex A.3 controls are the bridge, the security controls shared between the two SoAs. Most Indian growing companies run a single combined SoA with two clearly labelled control surfaces (privacy and security) and a clear cross-walk between them.
Q2. Our operational SoA is in a spreadsheet. Is that enough?
A spreadsheet is acceptable for the first cycle. The test is whether the operational SoA is current-state, justified, and reconciled, not the medium. The 8.3 audit asks "what is the last-update date?" and "show me the operational evidence for this applicable control". A spreadsheet that does all of that outperforms a GRC platform that does none of those things.
Q3. We have a 6.1.3 planning-layer Risk Treatment Plan. Do we need a separate 8.3 Operational Procedure?
Yes. The 6.1.3 / 8.3 separation is the load-bearing demarcation (Move 1). The 6.1.3 RTP is the decision; the 8.3 Operational Procedure is the operational execution. A single document covering both is the canonical 8.3 audit failure.
Q4. How often should we update the operational SoA?
At the planned-interval cycle (annual minimum; semi-annual for SDFs and listed entities; quarterly for high-volatility sectors) plus on every event trigger (the seven-trigger catalog wired into Clause 6.3: new or changed processing purpose; new data type; new processor or sub-processor; new jurisdiction or cross-border transfer; new technology (especially AI); regulatory change; SDF re-scoping). An operational SoA whose last-update date matches the last surveillance audit is the canonical 8.3 red flag.
Q5. We have several controls documented as applicable where the implementation is "in progress" or "planned". Is that a problem?
Yes. A control marked applicable where the implementation is future-state is the canonical 6.1.3 / 8.3 audit failure. Either downgrade the control to not-applicable with a documented exclusion reason, or commit to a remediation target date and remove the row from the audit-evidence set until the control is live.
Q6. What happens if the treatment effectiveness evaluation concludes that a treatment is ineffective?
The finding triggers corrective action under Clause 10.2 (root-cause analysis and corrective action on the control that did not operate as designed) and a re-assessment under 8.2 (re-running the risk assessment for the affected processing activity). The treatment is then revised under 8.3, additional controls, modified conditions, or a new treatment option. The ineffectiveness finding is reported to the management review (Clause 9.3).
Q7. We are not yet designated an SDF. Do we need the SDF DPIA findings log under DPDP section 10?
The SDF DPIA findings log applies to Significant Data Fiduciaries. The discipline is to run the SDF-designation analysis annually (data volume, sensitivity, risk to principals, sovereignty impact); if the thresholds are approachable, build the SDF DPIA findings log operating model ahead of the designation. The ISO/IEC 27701:2025 operational treatment discipline is the natural single framework that satisfies both the PIMS obligation and (when designated) the section 10 obligations.
Q8. Who signs the residual-risk acceptance record?
The named risk owner, the business-process owner for the processing activity that generates the risk. The DPO does not sign in place of the risk owner; the DPO countersigns for risks above a higher threshold (e.g. critical, or section 10 SDF DPIA-related for SDFs). For risks at the highest threshold (critical risks affecting a material principal population, or risks with section 33 penalty exposure), top management signs off at the management review.
Q9. What is the relationship between 8.2 and 8.3?
8.2 produces the live Privacy Risk Register and the DPIA Register; 8.3 implements the operational treatment cycle on that register. 8.2 is the assess step; 8.3 is the treat and verify steps. The two clauses form the operational assess-treat-verify engine. 8.2 without 8.3 is a register without action; 8.3 without 8.2 is action without basis.
Q10. How is 8.3 different from 6.1.3?
6.1.3 is the planning-layer treatment decisions, the treatment option selected per risk, the planning-layer SoA that documents the design intent, the planning-layer RTP that records per-risk the option and the controls. 8.3 is the operational-layer execution, the operational SoA that documents the current-state implementation, the operational residual-risk register that records the current treatment state, the residual-risk acceptance records that are signed operationally, the treatment effectiveness evaluation that closes the loop. 6.1.3 produces the plan; 8.3 implements it.
Q11. Do we need to do algorithmic-software review on every AI-driven processing activity?
For SDFs under DPDP section 10, yes, the algorithmic-software review is a mandatory treatment control. For non-SDFs, the algorithmic-software review is recommended (not mandatory under DPDP) but the GDPR Article 22 ADM risk and the WP248 "evaluation or scoring" + "automated decision-making" criteria together make the review effectively mandatory where those criteria fire.
Q12. Our breach playbook handles the DPDP breach clock (intimation without delay; seventy-two-hour report). Is that enough?
No. A personal-data breach triggers two parallel clocks in India: the CERT-In six-hour clock (CERT-In Directions 28 April 2022) and the DPDP breach clock (intimation without delay, then a seventy-two-hour report; DPDP Act section 8(6) read with DPDP Rules 2025 Rule 7). For BFSI and listed entities, a third clock applies (RBI six hours; SEBI six hours; IRDAI twenty-four to seventy-two hours). The breach-response control under 8.3, the operational implementation of Annex A.3.12, must handle all applicable clocks in parallel from the same awareness event.
Q13. We use a Consent Manager under DPDP section 2(1)(g). What does 8.3 require?
The Consent Manager integrity controls must be evidenced in the operational SoA. Three controls: the consent-record integrity control (the consent record is tamper-evident, time-stamped, retrievable); the withdrawal-signal-honouring control (the withdrawal signal is honoured within the SLA and propagated to downstream systems); the interoperability-interface control (the Consent Manager interface is interoperable per the registration conditions, so the principal can move between Consent Managers). The three controls operationalise Annex A.1.2.3, A.1.2.4, A.1.3.5 and A.1.4 (privacy by design).
Q14. Can we outsource the operational treatment entirely?
The artefact construction can be outsourced (with external advisory); the live maintenance cannot be outsourced because it requires continuous organisational knowledge of the processing activities, the controls in operation, and the trigger events. The DPO owns the artefact; the workshop attendees (the business-process owners) own the input and the residual-risk acceptance signatures.
Q15. How often should the effectiveness evaluation be re-run?
At the planned-interval cycle (annual minimum; semi-annual for SDFs and listed entities; quarterly for high-volatility sectors) and on material change (the seven-trigger catalog from the Clause 6.3 guide). For each material treatment decision, the effectiveness evaluation produces an effectiveness conclusion (effective / partially effective / ineffective) and a treatment revision (confirmed / adjusted / re-engineered).
Industry-Specific Requirements
BFSI
Banks, NBFCs, payment aggregators, payment gateways, insurers. The BFSI operational SoA carries the heaviest regulatory load: the DPDP section 8(5) safeguards, the section 8(6) breach notification (intimation without delay and a seventy-two-hour report), the section 10 SDF obligations (most large BFSI players are likely SDFs), the RBI Storage of Payment System Data directive (6 April 2018), the RBI Digital Lending Guidelines (2 September 2022, borrower-consent, device-data minimisation, privacy-by-design for lending apps), the RBI Tokenisation circular (22 September 2021), the RBI Cybersecurity Directions 2026 (31 July 2026; incident reporting within six hours), the SEBI Cybersecurity and Cyber Resilience Framework (20 August 2024), the IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023). The operational SoA must surface the dual-clock pattern (CERT-In six hours, DPDP without delay plus a seventy-two-hour detailed report, RBI and SEBI six hours, IRDAI per its own guidelines) and the BFSI-specific harm scenarios (financial fraud, identity theft, credit-discrimination). The algorithmic-software review is critical for credit-scoring, fraud-detection and collections engines, the operational treatment implements the review as a per-model release gate. The residual-risk acceptance records for the credit-scoring engine and the cross-border affiliate flows are typically the highest-threshold records (DPO countersignature plus top-management sign-off).
Healthcare
Hospitals, telemedicine platforms, healthtech, insurers processing health data. The operational SoA must flag the heightened sensitivity of health data (the DPDP section 9 analog for vulnerable data subjects; the SPDI Rules' explicit inclusion of health data; clinical-data-confidentiality expectations; the IRDAI framework where insurance is involved). The DPIA threshold is low, most material processing activities require DPIA treatment under 8.2; the 8.3 operational treatment therefore covers most processing activities. The principal-impact "safety" dimension is load-bearing for clinical-data risks; the modify-option controls (A.1.4.4 accuracy; A.1.4.5 minimisation; A.1.4.8 retention) are densest. The role declaration is complex, hospitals are controllers for patient data, processors for some insurance-claim data, joint controllers with referring physicians in some cases (A.1.2.8). The algorithmic-software review is critical for AI-driven diagnostic and triage engines, the operational treatment implements the review as a release gate and the A.1.3.11 right-to-contest control as a patient-facing workflow.
IT-ITeS and SaaS
IT services firms, BPOs, SaaS providers, cloud processors. The operational SoA is almost always "both", the Annex A.1 controls for the organisation's own employees, marketing-lead contacts and beta-test users (controller-side); the Annex A.2 controls for the customer's principals reached through the organisation's processing (processor-side). The A.2.2.5 infringing-instruction control is the marquee processor-side operational control, the process for handling a customer instruction that would breach DPDP. The sub-processor controls (A.2.5.7 to A.2.5.9) are operationally dense for SaaS providers with multi-layer sub-processor ecosystems. The standalone-PIMS scoping decision lets SaaS firms scope a PIMS to the customer-data plane only, separate from the ISMS-scoped engineering plane. The cross-border transfer issue is central, most ITeS firms process data of overseas principals under GDPR / CCPA jurisdiction; the operational treatment implements the TIA control and the standard-contractual-clauses control densely.
E-commerce and Retail
D2C brands, marketplaces, e-commerce platforms, omni-channel retailers. The operational SoA must address consumer-privacy expectations at scale, the children's-data regime where minors are in the user base (DPDP section 9), the marketing-lead consent regime, the supplier-ecosystem processor chains, the payment-data overlays (RBI Tokenisation, the Payment Aggregator obligations). The operational treatment typically covers the recommendation engine (the algorithmic-software review as a treatment control), the marketing-lead scoring (the A.1.4.5 minimisation control and the WP248 "evaluation or scoring" trigger), the cross-border analytics (the A.1.5.2 transfer-impact-assessment control), the loyalty programme (often a joint-controller arrangement under A.1.2.8, the operational SoA marks A.1.2.8 applicable only when the arrangement is in place). The Consent Manager integration (DPDP section 2(1)(g)) is particularly relevant for consumer-facing firms, the operational treatment implements the Consent Manager integrity controls densely; the consent-quality risk (consent not as-easy-to-withdraw) is a frequent finding.
Edtech
K-12 platforms, higher-edtech, skilling platforms, test-prep. The children's-data regime (DPDP section 9) is the central operational-treatment issue, the principal is a minor, the consent dynamic is parental, and the section 9 verifiable-parental-consent + no-behavioural-monitoring-or-targeted-advertising regime is load-bearing. The avoid option is the canonical treatment for any processing activity that would breach section 9, behavioural monitoring features, targeted advertising features, recommendation engines that process minor-principal data without verifiable parental consent. The operational SoA marks A.1.2.4 (consent capture) and A.1.3.5 (withdrawal mechanism) applicable with the verifiable-parental-consent implementation evidenced. The DPIA threshold is low, most material processing activities require DPIA treatment under 8.2; the 8.3 operational treatment therefore covers most processing activities. The principal-impact "safety" and "dignity" dimensions are load-bearing for minor-principal risks; the residual-risk acceptance records for the adaptive-learning features (if any survive the section 9 screen) are the highest-threshold records.
Manufacturing
Discrete and process manufacturing, automotive, chemicals, pharma manufacturing. The operational SoA must address the OT-IT convergence (operational technology systems increasingly connected, with PII exposure in HR, contractor and visitor data), the supply-chain processor ecosystem, the geopolitical context for cross-border manufacturing data flows. The principal set includes employees, contractors, visitors, customers (where the manufacturer operates a direct-to-customer channel), and patients (for pharma manufacturing with patient-level pharmacovigilance data). The operational treatment typically covers the employee-monitoring tools (OT-IT convergence, the modify-option controls A.1.4.2 limit collection and A.1.4.3 limit processing), the contractor-management systems, the pharmacovigilance reporting (for pharma, the modify-option control A.1.5.4 records of disclosure). The role declaration is typically simpler than in consumer-facing sectors. The operational SoA is often lighter on the Annex A.1 / A.2 controls and heavier on the Annex A.3 security controls.
Cross-sector patterns
Three patterns recur across sectors and are worth flagging in any 8.3 operational treatment regardless of industry.
The processor-side scale pattern. Indian ITeS, BPO, SaaS and cloud-processor firms typically process personal data at volumes that easily cross the DPDP SDF thresholds even though their consumer brand is small. The principal-as-affected-population runs into millions; the SDF-designation analysis must use the volume of data processed (not the headcount) as the threshold proxy. For SDF-designated processor-side firms, the SDF DPIA findings log under DPDP section 10 drives the operational treatment cycle.
The dual-regulator pattern. BFSI and listed entities carry dual-regulator exposure, DPDP via the Data Protection Board plus the sector regulator (RBI, SEBI, IRDAI). The operational SoA must capture both regulatory streams and the dual-clock pattern they create (CERT-In six hours, DPDP without delay plus a seventy-two-hour detailed report, sector six hours).
The AI-driven profiling pattern. AI-driven processing activities (credit-scoring, marketing-lead scoring, recommendation engines, fraud detection, adaptive learning, algorithmic hiring) require the algorithmic-software review as a treatment control. The operational SoA surfaces these activities explicitly and the operational treatment implements the review as a release gate.
Maturity Model
Figure · Tiers
Maturity levels for privacy risk treatment
- OptimisedContinuous operational-treatment-monito…
- ManagedAn operationally treatment-literate
- DefinedA structured Operational Procedure
- ReactiveAn Operational Procedure exists
- InitialNo Operational Privacy Risk Treatment
| Level | Description |
|---|---|
| L1, Initial | No Operational Privacy Risk Treatment Procedure, or a single document conflated with the 6.1.3 RTP. Operational SoA updated only in the thirty days before the surveillance audit. Multiple future-state rows. Residual-risk acceptance records missing or unsigned. No effectiveness evaluation. No SDF DPIA findings log (for SDFs). |
| L2, Reactive | An Operational Procedure exists but is dated. Operational SoA mostly current with some future-state rows and some unjustified exclusions. Residual-risk acceptance records exist for some above-threshold risks but unsigned or signed by the wrong party. Effectiveness evaluation exists but is a tick-box exercise. |
| L3, Defined | A structured Operational Procedure distinct from the 6.1.3 RTP. Operational SoA current-state with documented exclusions; zero or near-zero future-state rows. Residual-risk acceptance records signed by the named risk owner for every above-threshold risk. Effectiveness evaluation cycle operational with the per-decision structure. SDF DPIA findings log operational (for SDFs). Consent Manager integrity controls evidenced (where applicable). Annual planned-interval cycle wired into the management review. |
| L4, Managed | An operationally treatment-literate PIMS. Operational SoA event-driven current; reconciliation with the ISMS SoA on Annex A.3; integrated-with-distinction posture. Effectiveness evaluation cycle drives treatment revisions and feeds back into 8.2 and 6.1.3. Algorithmic-software review integrated with the MLOps pipeline for AI-driven activities. Board-visible operational residual-risk trajectory for SDFs and listed entities. Cross-framework reconciliation (DPDP / GDPR / NIST / SOC 2 / ISO 27001 / 27005 / 31000 / 29134 / 42001). For SDFs, the SDF DPIA findings log / independent-audit / algorithmic-software review cadence is fully operational. |
| L5, Optimised | Continuous operational-treatment-monitoring capability. GRC platform with operational SoA automation; effectiveness evaluation continuous with quarterly deep-dives. ROPA-discovery tool feeds the operational treatment automatically. Algorithmic-software review integrated with the MLOps pipeline. Consent Manager interoperability fully operational. Operational residual-risk register reconciled in real-time with the operational control evidence. The operational treatment discipline demonstrably drives every downstream Clause 8 sub-clause. For SDFs, the SDF DPIA findings log / independent-audit / algorithmic-software review cadence is fully operational and continuously improved. |
Emerging Trends
AI-driven processing and the algorithmic-fairness axis. The Rule 13(3) algorithmic-software review, the 2025 edition's callout of AI-driven profiling and automated decision-making, and the parallel development of ISO/IEC 42001:2023 (AI Management System) are reshaping the 8.3 operational treatment landscape. For organisations using AI / ML on personal data, the algorithmic-software review is the highest-use modify-option control; the operational treatment implements the review as a per-model release gate, and the effectiveness evaluation tests the review's bias / discrimination / transparency / explainability / strength findings periodically.
DPDP SDF designations and the SDF DPIA findings log. The Central Government is expected to designate the first wave of SDFs through 2026 and 2027 as the DPDP Rules 2025 phased commencement completes. Designated SDFs must operationalise the SDF DPIA findings log under DPDP section 10. The 8.3 operational treatment discipline is the natural framework for the SDF DPIA findings log; the ISO/IEC 27701:2025 PIMS is the natural single system that satisfies both the management-system obligation and the section 10 obligations.
DPBI operational emergence. The Data Protection Board of India, constituted under DPDP section 18, is emerging through 2026 and 2027. Its early orders, its interpretation of the Schedule penalty maxima, its engagement patterns on treatment effectiveness (did the operational treatment actually hold?), and its precedent on the breach-notification clock will reshape the 8.3 operational treatment landscape for every Indian Data Fiduciary.
Consent Manager ecosystem emergence. The DPDP Rules 2025 prescribe Consent Manager registration conditions; the first Consent Managers are expected to be registered through 2026 and 2027. As the ecosystem emerges, the Consent Manager integrity controls (DPDP section 2(1)(g) and section 6) become a first-class operational-treatment dimension for consumer-facing firms, the consent-record integrity, the withdrawal-signal-honouring, the interoperability-interface.
Cross-border transfer regime evolution. The DPDP negative list under section 16, the EU-US Data Privacy Framework adequacy decision (10 July 2023), the UK IDTA / Addendum, the China PIPL cross-border mechanisms, and the geopolitical risk environment are all in flux. The operational SoA's A.1.5.2 / A.2.5.2 (basis for PII transfer) controls must monitor this dimension continuously; the effectiveness evaluation tests the TIA currency periodically.
Integrated management systems. The harmonized structure enables integrated 27001 + 27701 + 42001 + 22301 governance. The operational treatment discipline is the natural point of integration, a single combined operational treatment cycle that serves all four management systems with clearly labelled sub-sections; a single operational SoA covering all four control surfaces (Annex A.1 / A.2 / A.3 privacy; ISO/IEC 27002:2022 security; ISO/IEC 42001:2023 AI; ISO 22301:2019 business-continuity).
Generative AI in PIMS operations themselves. The use of generative AI inside the PIMS function (for operational SoA automation, effectiveness evaluation drafting, breach-notification drafting) is an 8.3 risk in its own right, the principal-impact axis must consider the generative-AI-specific harm scenarios (training-data leakage, prompt-injection-driven disclosure, model hallucination on principal-rights requests). The operational treatment implements the generative-AI-specific modify-option controls (data-handling restrictions, output review, prompt-injection-hardening).
Sector-regulator convergence on privacy treatment. RBI, SEBI and IRDAI are each tightening their privacy-adjacent rules (RBI Digital Lending, SEBI CSCRF, IRDAI ICS 2023). The DPDP Act sits as a horizontal layer above these sectoral instruments; the operational SoA must monitor both the horizontal and the sectoral streams because they can diverge in their specific obligations even when they share the underlying privacy principle.
Climate-related privacy risks. The 2025 edition's climate-change amendment (to Clauses 4.1 and 4.2) intersects with 8.3, climate-driven disruption of PII processing (climate-exposed data centres, climate-driven supply-chain failures affecting processors, climate-driven migration affecting principal populations) is an emerging operational-treatment dimension for climate-exposed sectors.
References and Further Reading
Primary instruments (India). Digital Personal Data Protection Act, 2023 (Act No. 22 of 2023, enacted 11 August 2023), MeitY, in particular sections 8(5), 8(6), 9, 10 (SDF, DPO, SDF DPIA, independent data audit, algorithmic-software review), 11 to 14, 16, 18, 33 + Schedule (penalty maxima up to two hundred and fifty crore rupees for section 8(5) failure; two hundred crore for sections 8(6) and 9; one hundred and fifty crore for section 10). Digital Personal Data Protection Rules, 2025 (notified 13 November 2025), MeitY, Rule 7 (breach intimation without delay, the seventy-two-hour detailed report and format); SDF thresholds; Consent Manager registration conditions. Information Technology Act, 2000, sections 43A, 72A, 70B. IT (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011 (notified 11 April 2011). CERT-In Directions 20(3)/2022-CERT-In (28 April 2022), the six-hour clock. RBI Storage of Payment System Data (6 April 2018); RBI Digital Lending Guidelines (2 September 2022); RBI Tokenisation (22 September 2021); RBI Cybersecurity Directions 2026 (31 July 2026). SEBI Cybersecurity and Cyber Resilience Framework (20 August 2024). IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023). Companies Act 2013, sections 134(3)(n), 177; SEBI LODR Regulation 21.
Primary jurisprudence (India). K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (nine-judge Bench, 24 August 2017). Justice K.S. Puttaswamy (Retd.) v. Union of India (Aadhaar), (2019) 1 SCC 1 (five-judge Bench, 26 September 2018).
Primary instruments (global). Regulation (EU) 2016/679 (GDPR), OJ L 119, 4.5.2016, p. 1; application from 25 May 2018, Articles 5(2), 24 (controller responsibility, review and update of treatment), 32 (security of processing, regular testing and evaluation), 35 (DPIA), 35(11) (DPIA review on change), 36 (prior consultation). NIST Privacy Framework v1.0, NIST.CSWP.01162020, 16 January 2020, the Control-P function (Data-processing management; Disassociated processing; Data-flow management; Privacy testing). NIST SP 800-37 Rev. 2 (Risk Management Framework), Continuous Monitoring step. AICPA, 2017 Trust Services Criteria (with 2022 Points of Focus update), CC3.3, CC4.1, CC4.2, CC7, CC8. Brazil LGPD, Lei nº 13.709/2018. China PIPL, Article 55 (mandatory PIA).
ISO/IEC standards. ISO/IEC 27701:2025 (2nd ed., published 14 October 2025), Clause 8.3 (operational privacy risk treatment); Clause 6.1.3 (planning-layer privacy risk treatment, the load-bearing demarcation); Clause 8.2 (operational privacy risk assessment, the assess step in the 8.2 / 8.3 loop); Clause 8.1 (operational planning and control, the umbrella); Clause 9.1 (monitoring, the continuous-monitoring spine); Annex A.1 / A.2 / A.3 (the operational SoA control surface); Annex B (normative in 2025). ISO/IEC 27701:2019 (1st ed., for transition reference, Annex F risk-treatment guidance). ISO/IEC 27001:2022 Clause 8.3 (infosec risk treatment, the integrated-with-distinction partner). ISO/IEC 27002:2022, only 5.34 is PII-specific. ISO/IEC 27005:2022 (infosec risk management, the four-treatment-option source). ISO 31000:2018 (risk management, the four-treatment-option taxonomy). ISO/IEC 29134:2017 (DPIA guidelines, the effectiveness evaluation tests DPIA conclusion currency). ISO/IEC 27557 (impact assessment). ISO/IEC 29100:2011 (privacy framework, 11 principles). ISO/IEC 27018:2019 (cloud PII processor); ISO/IEC 27017:2015 (cloud security); ISO/IEC 29151 (PII protection code). ISO/IEC 42001:2023 (AI Management System, algorithmic-software review as a treatment control). ISO/IEC 27706:2025 (PIMS cert-scheme competence). ISO/IEC 27001:2022 Amendment 1:2024 (climate-change addition to 4.1; mirrored in 27701:2025 for 4.1/4.2, intersects with 8.3 operational treatment for climate-exposed sectors).
Edition-transition sources (practitioner commentary used as research input). ANAB Heads Up #550 (transition timeline). The 2025 edition's structure, control counts (31 + 18 + 29 = 78 consensus; one tier-1 cert-body source reports an outlier count of 86), the operational SoA discipline (current-state implementation; justified exclusions; no hypothetical-future-applicability), the four-treatment-option taxonomy, the effectiveness evaluation requirement, the normative-Annex-B change, and the climate-change amendment are confirmed from the official 2025 PDF (OCR) and corroborated by tier-1 practitioner commentary. The common-nonconformity patterns (the 6.1.3 / 8.3 conflation; the future-state SoA; the unsigned residual-risk acceptance; the tick-box effectiveness evaluation; the operational SoA last-update date matching the last surveillance audit; the SDF-oblivion) are drawn from tier-1 cert-body practitioner commentary. All clause text in this guide is paraphrased; the official text is copyrighted by ISO/IEC and has not been reproduced.
This guide is published by Singahi. The ISO/IEC 27701:2025 clause text is copyrighted by ISO/IEC and has not been reproduced; all requirements are paraphrased. Brand names of competitors, cert bodies, and reference books are intentionally omitted. Scenarios are illustrative and should not be attributed to any real organisation.