On this page
- Quick Reference (60 Seconds)
- What the Standard Actually Requires
- Why This Control Matters
- Scope and Applicability
- Key Definitions and Terminology
- Relationship to Other Clauses and Frameworks
- Detailed Implementation Guidance, The Eight Leadership Moves
- Tools, Technologies, and Solutions
- Policy and Procedure Templates
- Risk Assessment and Treatment
- Audit and Compliance Checklist
- Metrics and KPIs
- Common Pitfalls and Audit Failures
- Illustrative Scenario 1: Failure, Pragati FinServ NBFC (Illustrative)
- Illustrative Scenario 2: Success, Anaya SaaS (Illustrative, with ROI)
- Multi-Framework Mapping
- Implementation Roadmap
- FAQ
- Industry-Specific Requirements
- Maturity Model
- Emerging Trends
- References and Further Reading
Quick Reference (60 Seconds)
| Attribute | Detail |
|---|---|
| Clause | ISO/IEC 27701:2025 Clause 5.1, Leadership and Commitment (the apex leadership clause of the PIMS, structurally aligned to the Harmonized Structure shared by ISO/IEC 27001:2022 Clause 5.1, ISO 22301:2019 Clause 5.1, ISO 9001:2015 Clause 5.1, and ISO/IEC 42001:2023 Clause 5.1). The 2025 edition moved 27701 from the 2019 "extension to 27001/27002" framing to a standalone PIMS on the harmonized structure; Clause 5.1 inherits the standalone framing in full. |
| What it asks for (paraphrase) | ISO/IEC 27701:2025 Clause 5.1 asks organizations to have top management visibly lead the PIMS and integrate privacy into business processes. Four ideas do the work in that paraphrase. Top management is a defined term, the person or group that directs and controls the organisation at the highest level. Visibly lead means demonstrable, evidenced leadership conduct, not a paper designation. The PIMS is the privacy information management system the organisation establishes under Clause 4.4. Integrate privacy into business processes means the PIMS is woven into product, sales, HR, vendor, finance, M&A and governance processes, not run as a parallel programme. |
| The marquee insight competitors miss | Leadership of the PIMS is a conduct obligation of top management, not a delegation to the DPO. The DPO runs the programme; top management owns the system. Under the harmonized structure, Clause 5.1 is the only clause that uses the phrase "top management shall" repeatedly and the only clause that prevents the PIMS from degenerating into "the DPO's project". In India this insight has statutory weight that goes far beyond the ISO standard itself: DPDP Act 2023 section 8 makes the Data Fiduciary's obligations non-delegable duties of the entity itself; section 10 makes the Significant Data Fiduciary's DPO accountable to the Board of Directors; the Companies Act 2013 section 134(3)(n) places the risk-management statement in the Board's Report; SEBI LODR Regulation 21 places privacy within the Risk Management Committee mandate. An Indian Top Management that treats Clause 5.1 as a DPO paperwork exercise is simultaneously failing an ISO requirement, a statutory duty, a board-governance duty and (for listed entities or SDFs) a markets-disclosure duty. This guide treats 5.1 as one unified board-level obligation across all four regimes. |
| Domain | Leadership (Clause 5). Clause 5.1 sits above Clause 5.2 (Privacy Policy) and Clause 5.3 (Roles, Responsibilities, Authorities). Where 5.2 tests the substance of the privacy policy and 5.3 tests the assignment of roles, 5.1 tests conduct, does top management demonstrate, through observable decisions and behaviours over time, that it leads the PIMS? Without 5.1 the rest of the PIMS is unsponsored. Without 5.1 the policy under 5.2 has no sponsor and the roles under 5.3 have no authority. |
| What you must produce | (a) A privacy governance structure with a named executive sponsor at top-management level, a DPO or Privacy Lead with a defined reporting line, a PIMS Steering Committee or equivalent forum, and (for SDFs and listed entities) a board or board-committee reporting channel; (b) a sponsor commitment statement signed by top management that names the privacy commitments and the resource plan; (c) business-process integration gates, privacy checkpoints embedded in product launch, vendor onboarding, M&A diligence, HR onboarding, marketing campaign approval, and software-development gates; (d) a privacy objective cascade that connects top-management direction to process-owner objectives and individual performance management; (e) a top-management reporting cadence (monthly sponsor review, quarterly steering committee, annual management review, board noting at prescribed intervals); (f) an incident-escalation chain that activates top management on the dual-clock (DPDP 72 hours and CERT-In 6 hours) and on regulator engagement; (g) demonstrable leadership evidence in the form of meeting minutes, decision logs, signed artefacts, calendar holds, budget approvals, town-hall records and the sponsor's audit-interview fluency; (h) the management-review ownership chain that ties Clause 5.1 to Clause 9.3. |
| Typical owner | Top management (CEO, MD, Managing Director, or the top-management team) owns Clause 5.1, it cannot be delegated. The named executive sponsor (typically the CEO, COO or a Top-Management Privacy Champion) is the single point of accountability for the PIMS at the top-management table. The DPO or Privacy Lead runs the programme day-to-day (and, under DPDP section 10, the SDF DPO is an India-based statutory role accountable to the board). The PIMS Steering Committee is the cross-functional forum. The Board or Risk Management Committee receives reports at planned intervals (mandatory under DPDP section 10 for SDFs, and under the Companies Act 2013 / SEBI LODR for listed entities). Internal Audit reports to the Audit Committee on PIMS conformance. |
| Minimum viable actions | (1) Name the executive sponsor and the DPO/Privacy Lead at the top-management table; (2) stand up the PIMS Steering Committee with a quarterly cadence and a documented charter; (3) author and sign the sponsor commitment statement (one page, on letterhead, dated, version-controlled); (4) wire privacy gates into product launch, vendor onboarding, M&A diligence and the software-development lifecycle; (5) allocate a privacy budget line and a headcount line for the DPO function and the awareness programme; (6) set the privacy objective cascade into process-owner performance management; (7) set the reporting cadence (monthly sponsor-DPO, quarterly steering committee, annual management review, board cycle); (8) design the incident-escalation chain with the dual-clock countdowns; (9) brief top management at the awareness programme and rehearse the sponsor for the certification audit interview; (10) capture all of the above in the Clause 5.1 evidence file for the certification auditor. |
| Maturity floor (L1) | A "delegated-and-forgotten" PIMS: top management has named the DPO and signed the policy at certification launch, then disengaged. No steering committee; no calendar holds; no budget line beyond the certification fee; no business-process integration; no sponsor audit fluency; no board visibility. The single most common Clause 5.1 nonconformity in the Indian growing-company segment, and the single most common pattern underlying a DPDP penalty exposure where the entity cannot demonstrate adequate safeguards under section 8(5). |
| Maturity target (L4 to L5) | A "leadership-owned" PIMS: the executive sponsor is fluent in the four commitment statements and the dual-clock breach commitment; the steering committee meets quarterly with documented decisions; the privacy budget is a board-noted line; business-process gates produce monthly privacy-by-design reviews; the sponsor and the DPO jointly host the privacy town-hall; the board Risk Management Committee receives a privacy pack quarterly; the SDF section 10 DPO is in post and reporting to the board; the certification audit interview is a sponsor strength; the leadership evidence file passes the auditor's traceability test on the first pass. |
| Quick win | Run a two-hour top-management privacy workshop with the executive sponsor, the CEO, the DPO, the CISO, the Head of Legal, the Head of Product and the Head of HR. Use the eight leadership moves in Section 7 as the agenda. Produce the signed sponsor commitment statement (one page), the named governance structure (one page), the quarterly calendar holds, and the budget line. It is the single intervention most likely to convert a Stage 1 major nonconformity on Clause 5.1 into a Stage 1 pass, and it is the single intervention most likely to avoid a DPDP section 8(5) "adequate safeguards" finding against the entity. |
| Time to implement (first cycle) | Growing companies (50 to 250 staff): 4 to 8 weeks for the first leadership-cycle setup (sponsor statement, governance structure, calendar, budget, integration gates, awareness programme). Mid-market (250 to 2,000): 8 to 14 weeks, usually requiring board-cycle alignment, SDF-readiness work for likely-SDF entities, and integration with the existing Risk Management Committee. Multi-entity enterprise: 4 to 9 months, integrated with group governance taxonomy, board reporting architecture, and the multi-jurisdiction regulator landscape. |
| Related clauses | 4.1 (context informs the leadership agenda), 4.2 (regulators and PII principals are interested parties the leadership commitment must address), 4.3 (scope defines what top management leads), 4.4 (the PIMS is what leadership leads), 5.2 (the privacy policy top management establishes, see the companion Singahi guide), 5.3 (the privacy roles top management assigns, the DPO/Privacy Lead, the SDF section 10 DPO, the PIMS Steering Committee), 6.1 (leadership owns the privacy risk decision), 6.2 (leadership sets the framework for privacy objectives), 6.3 (leadership owns planned PIMS changes), 7.1 (leadership provides resources), 7.2 (leadership ensures competence), 7.3 (leadership drives awareness), 7.4 (leadership owns the communication discipline), 7.5 (leadership ensures Documented Information is controlled), 8.1 to 8.3 (leadership owns the operational processes, especially the privacy risk treatment), Annex A.1.2.x (controller conditions for collection and processing, leadership owns the lawful-basis decision), Annex A.1.2.5 (privacy impact assessment, leadership owns the DPIA trigger decision), Annex A.1.4.x (privacy by design, leadership owns the integration into product development), Annex A.2.x (processor controls, leadership owns the processor-relationship framework), Annex A.3 (security, leadership owns the SoA sign-off), 9.1 to 9.3 (leadership owns the management review), 10.2 to 10.1 (leadership owns the corrective-action and continual-improvement discipline). 5.1 is the spine every other clause hangs from. |
| Critical Indian leadership clocks the sponsor must own | DPDP breach notice within 72 hours to the Data Protection Board of India and to affected Data Principals (DPDP Act 2023 section 8(6) + DPDP Rules 2025 Rule 7, notified 13 November 2025); CERT-In incident report within 6 hours of noticing a prescribed cyber incident (CERT-In Directions 20(3)/2022-CERT-In, 28 April 2022); RBI incident report within six hours for banks and NBFCs (RBI Cybersecurity Directions 2026, 31 July 2026); SEBI Regulated Entity incident report within 6 hours (SEBI CSCRF, 20 August 2024); IRDAI incident report per IRDAI guidelines (IRDAI ICS 2023, 24 April 2023); grievance redressal response within the period prescribed under the DPDP Rules (DPDP Act section 13); SDF DPO accountability-to-board at planned intervals (DPDP Act section 10). The leadership commitment must name these clocks and bind the organisation to maintain the capability that meets them. The dual-clock breach reality (CERT-In 6 hours and DPDP 72 hours running in parallel from the same awareness event) is the marquee test of whether leadership has integrated privacy into the organisation's incident-response capability, and the most common Clause 5.1 audit-failure signal after the sponsor-interview question. |
If you only read one thing: Clause 5.1 is where the PIMS stops being a programme and becomes the organisation's own institution. A 5.1-conformant PIMS is one in which top management demonstrably directs the privacy agenda, integrates privacy into business processes, resources the DPO function, owns the dual-clock breach commitment, hosts the management review, and is fluent in the year's privacy risks and objectives, not one in which top management signed the policy at launch and disengaged. The certification auditor will test this distinction in the sponsor interview; the Data Protection Board of India will test it after a breach; the board will test it in the section 134(3)(n) risk-management statement. Get 5.1 wrong and every other clause becomes harder because no one at the top owns the system. Get it right and the rest of the PIMS becomes a matter of execution.
What the Standard Actually Requires
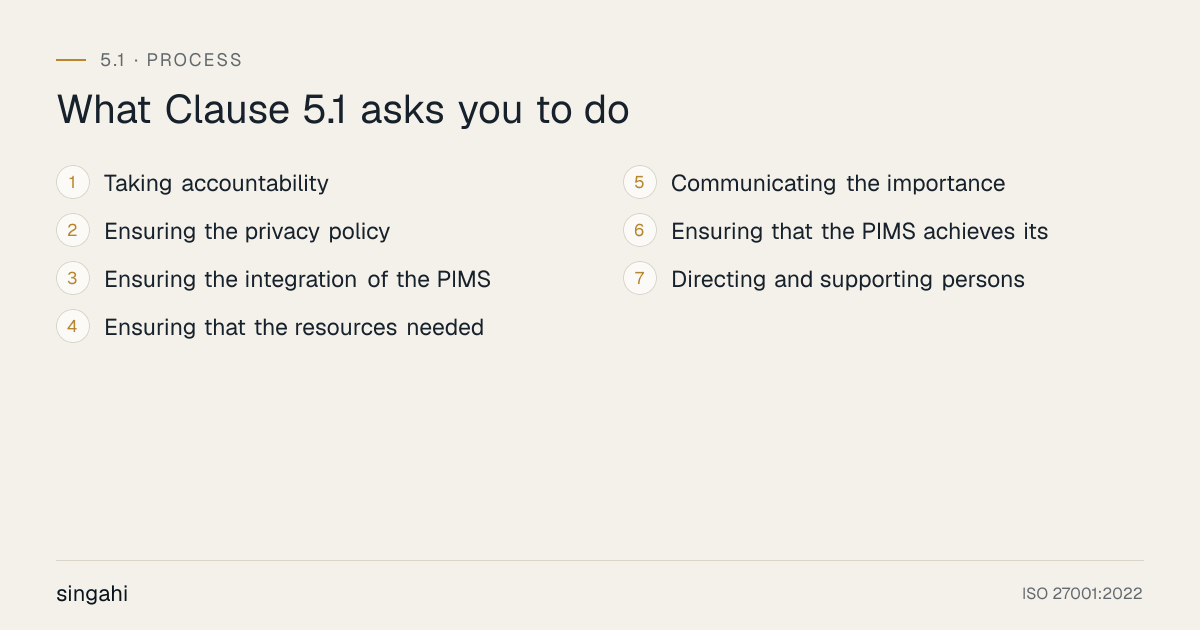
Figure · Process
What Clause 5.1 asks you to do
The paraphrased requirement
ISO/IEC 27701:2025 Clause 5.1 asks organizations to have top management visibly lead the PIMS and integrate privacy into business processes. Four ideas do the work in that paraphrase.
Top management is a defined term in the harmonized structure. It is the person or group of people who direct and control an organisation at the highest level. In an Indian growing company this is typically the CEO or MD, the founding partners, the top-management team, or, for a board-managed entity, the Board itself acting through delegated authority. Top management is not the DPO, the CISO, the Head of Legal or the Head of Compliance. Those are management roles. Top management is the level above them.
Visibly lead is the load-bearing word. The harmonized structure deliberately uses "demonstrates leadership", visible, evidenced, conduct-based leadership. The standard does not accept a paper designation. Top management must demonstrate, through observable decisions and behaviours over time, that it leads the PIMS. The decisions and behaviours the standard names are the leadership moves that Section 7 of this guide organises into the eight-move framework: establishing the privacy policy and objectives; ensuring the PIMS is integrated into business processes; ensuring the resources the PIMS needs; communicating the importance of effective privacy management and of conforming to the PIMS requirements; ensuring the PIMS achieves its intended outcomes; directing and supporting persons to contribute to the PIMS effectiveness; promoting continual improvement; and supporting other relevant managerial roles to demonstrate leadership in their areas of control.
The PIMS is the privacy information management system the organisation establishes, implements, maintains and continually improves under Clause 4.4. The PIMS is not a single document or a single role; it is the system of policies, processes, controls, resources and people that the organisation uses to manage privacy. Top management leads the system; it does not run the system day-to-day. Running is delegated; leading is not.
Integrate privacy into business processes is the marquee integration requirement. The PIMS is not a parallel programme; it is woven into the organisation's business processes. This is the requirement that, in practice, most distinguishes a 5.1-conformant PIMS from a "compliance-only" PIMS. The integration happens at the operational gates: the product-launch gate, the vendor-onboarding gate, the M&A diligence gate, the software-development gate, the marketing-campaign approval gate, the HR onboarding gate. Top management's job is to ensure those gates exist, that they include privacy checks, and that they are operated. The DPO and the Privacy Lead run the checks; top management ensures the checks are part of the business.
The harmonized-structure leadership set
ISO/IEC 27701:2025 Clause 5.1 inherits the harmonized-structure leadership set. The wording below is Singahi's paraphrase; the standard's own formulation is not reproduced.
Top management shall demonstrate leadership and commitment with respect to the PIMS by:
-
Taking accountability for the effectiveness of the PIMS. This is the apex commitment. Top management owns whether the PIMS works. Not the DPO, not the consultant, not the certifying body. The auditor's sponsor-interview question, "who owns whether the PIMS works?", must be answered with a name at top-management level.
-
Ensuring the privacy policy and privacy objectives are established and are compatible with the strategic direction of the organisation. Clause 5.2 (policy) and Clause 6.2 (objectives) are downstream of this commitment. The privacy policy must align with the organisation's strategy, a privacy policy that is incompatible with the strategic direction (for example, a data-minimisation commitment incompatible with a data-monetisation strategy) is a 5.1 failure on this limb.
-
Ensuring the integration of the PIMS requirements into the organisation's business processes. This is the integration limb, the marquee integration requirement described above.
-
Ensuring that the resources needed for the PIMS are available. Clause 7.1 (Resources) is downstream of this commitment. Top management owns the privacy budget, the DPO headcount, the awareness programme investment, the consent-management infrastructure, the platform investments.
-
Communicating the importance of effective privacy management and of conforming to the PIMS requirements. Clause 7.3 (Awareness) and Clause 7.4 (Communication) are downstream of this commitment. Top management is the most effective communicator of the PIMS, the sponsor's town-hall, the board message, the all-hands email, the visible enforcement of privacy expectations against violations.
-
Ensuring that the PIMS achieves its intended outcome(s). The PIMS has intended outcomes, lawful processing, honoured rights, breach resilience, regulator-ready artefacts, customer trust. Top management owns whether those outcomes are achieved.
-
Directing and supporting persons to contribute to the effectiveness of the PIMS. This is the management-direction limb. Top management directs process owners, engineers, vendor managers, HR, marketing, finance to do their part; it supports them with resources, training and authority.
-
Promoting continual improvement. Clauses 9.1, 9.2, 9.3, 10.2, 10.1 are downstream of this commitment. Top management owns the improvement cycle.
-
Supporting other relevant managerial roles to demonstrate their leadership as it applies to their areas of responsibility. This is the cascaded-leadership limb. Top management does not lead privacy alone; it supports the CISO, the Head of Legal, the Head of Product, the Head of HR to demonstrate their own leadership in their areas.
The standard's Clause 5.1 list is short; the method lives in the now-normative Annex B (Implementation Guidance for PII Controllers and Processors), a load-bearing 2025 change. In ISO/IEC 27701:2019 the equivalent material sat in informative Annex F; auditors could treat it as guidance. In ISO/IEC 27701:2025, Annex B is normative, auditors will test against it. For Clause 5.1 specifically, the Annex B guidance (numbered B.5.1 to mirror the clause) explains how leadership commitment should be evidenced, what the governance forum should look like, how the integration into business processes is operationalised, and what the reporting cadence should be. The Annex B guidance should be treated as testable, not optional.
The DPDP overlay, where Indian leadership becomes a statutory duty
In India, four statutory overlays make Clause 5.1 conduct a matter of board-level legal duty, not just a management-system preference. The four overlays are independent but reinforcing.
DPDP Act 2023 section 8 (general obligations of Data Fiduciary). Section 8 makes the obligations of a Data Fiduciary, including reasonable security safeguards under section 8(5), breach notification under section 8(6), and erasure under section 8(7), duties of the entity itself. They are non-delegable. A Data Fiduciary cannot contract out of them by appointing a DPO or engaging a consultant. The Data Fiduciary's top management owns these obligations. Under the Schedule, failure on section 8(5) safeguards can attract a Board-imposed penalty of up to 250 crore rupees; failure on section 8(6) notification can attract up to 200 crore rupees. The Data Protection Board's analysis of "adequate safeguards" under section 8(5) and "adequate notification" under section 8(6) tests leadership conduct directly, what budget did the entity allocate, what awareness programme did it run, what integration gates did it operate, what was the sponsor's fluency in the breach playbook.
DPDP Act 2023 section 10 (Significant Data Fiduciary). For SDFs, the leadership duty is sharper. The SDF must appoint a DPO based in India, accountable to the Board of Directors or governing body (the explicit statutory phrase); perform a Data Protection Impact Assessment (DPIP) for each new processing activity; perform periodic independent data audits; and conduct an algorithmic-AI fairness review where relevant. The DPO-accountability-to-board requirement is the densest overlap with ISO/IEC 27701:2025 Clause 5.1, section 10 effectively makes a Clause 5.1 reporting channel a statutory requirement for SDFs. Failure on the section 10 additional obligations can attract up to 150 crore rupees.
Companies Act 2013 section 134(3)(n). The Board's Report must include a statement on the development and implementation of a risk management policy for the company, including identification of elements of risk that may threaten the existence of the company. Privacy risk is one of those elements. The Board of an Indian company, whether or not it is an SDF, whether or not it is listed, has a statutory obligation to address privacy risk in its risk-management policy statement. The statement is the natural board-visible artefact of Clause 5.1 conduct.
Companies Act 2013 section 177 (Audit Committee) and SEBI LODR Regulation 21 (Risk Management Committee). For listed entities, the Audit Committee and the Risk Management Committee are the board committees that oversee risk, including privacy and cyber risk. The RMC mandate under Regulation 21 explicitly includes cyber security, operational risk, and (in practice) privacy risk. The RMC is the natural recipient of the privacy pack that operationalises Clause 5.1 at board level. For BFSI entities, the RBI Cybersecurity Directions 2026 (31 July 2026) and the IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023) impose parallel board-approval and board-reporting obligations. For SEBI Regulated Entities, the SEBI CSCRF (20 August 2024) requires a board-approved cyber-resilience policy.
The four overlays together produce a single conclusion: in India, top-management leadership of the PIMS is the statutory and governance duty of the entity's own board and top management, not a delegated compliance task. ISO/IEC 27701:2025 Clause 5.1 is the management-system lens through which an Indian organisation can demonstrably evidence that duty to the Data Protection Board, the sector regulator, the board's own Audit Committee, the markets regulator and (after a breach) the courts. This is the marquee commercial argument for pursuing ISO/IEC 27701:2025 certification in India, it converts the DPDP / Companies Act / SEBI LODR / RBI / IRDAI leadership duties from a defensive posture into a structured, auditable, board-grade discipline.
What the standard does NOT require (the demarcation competitors miss)
Clause 5.1 is widely misread as "the sponsor signs the policy and shows up at the audit". That misreading produces the most common 5.1 nonconformity in the Indian growing-company segment. Being explicit about what 5.1 does not require protects against two failure modes: under-investing (treating leadership as a signature) and over-reaching (treating leadership as micro-management of every privacy decision).
- 5.1 does not require top management to run the PIMS day-to-day. Top management leads; the DPO and the Privacy Lead run. The auditor will test whether the sponsor knows the difference. A sponsor who describes the consent-record schema in detail is over-reaching (and is probably interfering with the DPO); a sponsor who cannot describe the year's top three privacy risks is under-investing.
- 5.1 does not require a specific governance structure. The standard does not mandate a Privacy Committee, a Chief Privacy Officer, or any particular named forum. It requires that the integration, the resources and the communication happen; how they happen is the organisation's choice. DPDP section 10 (for SDFs) does require a DPO based in India accountable to the board, but that is a regulatory overlay, not a baseline 5.1 requirement.
- 5.1 does not require board approval of every privacy decision. Top management delegates operational privacy decisions to the DPO and the Privacy Lead. Board visibility is required at planned intervals (annually at minimum; quarterly for SDFs and listed entities) and on event trigger, not on every consent-record decision.
- 5.1 does not require a Chief Privacy Officer. The DPO function can be discharged by a Privacy Lead, a part-time DPO, an external DPO-as-a-service, or (for smaller entities) a senior manager wearing the privacy hat. The test is whether the function has the authority, the resources and the reporting line, not whether the title exists.
- 5.1 does not require the sponsor to be the CEO. The sponsor can be the CEO, the COO, the MD, a Whole-Time Director, or, for large groups, a Group Privacy Champion at the top-management table. The test is whether the sponsor is at the top-management level and has the authority to direct resources and integration.
- 5.1 does not require the sponsor to be a privacy expert. The sponsor must be fluent in the year's top privacy risks and the dual-clock breach commitment. The sponsor is not required to be a CIPM or a CIPP/E. The DPO is the expert; the sponsor is the leader.
- 5.1 does not require variable-pay linkage to privacy performance. Pay linkage is a leading-practice signal of L4 to L5 maturity, not a standard requirement.
- 5.1 does not require public reporting on leadership conduct. The leadership evidence is internal; it is shared with the certification auditor and (on event) with the regulator. Public reporting on privacy leadership is a brand choice (the customer trust portal route), not a 5.1 requirement.
- 5.1 does not require the privacy budget to be a separate line item. The test is whether the resources are available, not whether they sit in a separately labelled budget code. Many Indian growing companies bundle privacy spend into the IT, Legal or Compliance budget; this is acceptable as long as the spend is identifiable and adequate.
- 5.1 does not require a separate "PIMS sponsor role" distinct from the ISMS sponsor role. If the organisation runs an integrated ISMS+PIMS, a single sponsor at top-management level can satisfy both ISO/IEC 27001:2022 Clause 5.1 and ISO/IEC 27701:2025 Clause 5.1. The test is whether the sponsor leads both systems.
What auditors actually check
The certification auditor's Clause 5.1 examination has eight predictable moves. Preparing for them is the most efficient way to convert a Stage 1 visit into a Stage 1 pass.
First, the sponsor interview. The auditor asks for a 30- to 60-minute interview with the named executive sponsor. The questions are predictable: who owns whether the PIMS works; what are the four commitment statements; what are this year's top three privacy risks and how were they treated; what is the dual-clock breach commitment; when was the last steering committee; when was the last board pack; what is the privacy budget; what is the sponsor's role in the management review. If the sponsor cannot answer fluently, the audit is effectively over on Clause 5.1, major nonconformity, regardless of how technically excellent the rest of the PIMS is.
Second, the governance-structure check. The auditor asks to see the documented governance structure: the named sponsor, the named DPO, the PIMS Steering Committee charter, the reporting line to the board or RMC. The auditor checks that the structure is real, meeting minutes, attendance, decisions documented.
Third, the integration check. The auditor samples business processes for privacy integration. Pick a recently launched product, was there a privacy gate in the launch? Pick a recently onboarded vendor, was there a privacy gate in onboarding? Pick a recently approved marketing campaign, was there a privacy check? Pick a recently merged or acquired entity, was there a privacy diligence? If the gates exist on paper but no decisions are documented, the integration is decoration. The auditor will find this.
Fourth, the resource check. The auditor asks to see the privacy budget line, the DPO headcount, the awareness programme investment, the platform investments. The test is whether the resources are adequate for the PIMS scope.
Fifth, the communication check. The auditor samples staff. "Have you heard from leadership about privacy this year? Who is the executive sponsor? What did they say?" Five randomly-sampled staff in different functions and locations. If three out of five cannot answer, the communication commitment is failed, minor nonconformity. If four out of five cannot answer, major nonconformity.
Sixth, the management-review check. The auditor reviews the last management review (Clause 9.3), was the sponsor present, did the sponsor chair, are the privacy decisions documented, are the corrective actions tracked to closure. A management review without the sponsor present is a 5.1 finding.
Seventh, the incident-escalation check. The auditor asks for the last breach tabletop exercise record, who attended from top management, were both clocks met, what was the decision tree. If no tabletop has been run, or if top management did not participate, the incident-escalation limb is weak.
Eighth, the leadership evidence file. The auditor asks to see the bundle: the signed sponsor commitment statement, the steering committee charter, the steering committee minutes (typically four per year), the board pack (typically two to four per year for SDFs and listed entities), the privacy budget approval, the awareness programme calendar, the integration gate log, the management review minute, the tabletop exercise record. This bundle is the leadership evidence, without it, the sponsor interview is uncorroborated testimony.
Why This Control Matters
The leadership spine of the PIMS
Every other clause and annex of ISO/IEC 27701:2025 inherits its legitimacy from Clause 5.1. The privacy policy (Clause 5.2) is justified because top management establishes it. The privacy roles (Clause 5.3) are justified because top management assigns them. The privacy risk assessment (Clause 6.1.2 and 8.2) is justified because top management directs the risk decision. The ROPA (Clause 8 and Annex A.1.2.x) is justified because top management ensures the integration. The DPIA (Annex A.1.2.5) is justified because top management ensures the trigger mechanism. The data-principal-rights workflow (Annex A.1.3.x) is justified because top management ensures the resources. The processor DPA regime (Annex A.2) is justified because top management sets the processor-relationship framework. The breach playbook (Clause 8 and Annex A.3) is justified because top management owns the dual-clock commitment. The internal audits (Clause 9.2) and management review (Clause 9.3) are justified because top management owns the improvement cycle.
Without 5.1, the rest of the PIMS is unsponsored effort. With a strong 5.1, every other clause has a defensible origin. This is not a stylistic observation. It is the operational reality that the certification auditor and the Data Protection Board of India converge on. A PIMS without demonstrable top-management leadership is, in auditor language, a "system without top-management authorisation", the most serious structural nonconformity a PIMS can carry. A PIMS without demonstrable top-management leadership is, in DPDP language, a Data Fiduciary unable to evidence the "adequate safeguards" analysis under section 8(5), exposing the entity to penalties up to 250 crore rupees per the Schedule.
The Indian regulatory weight behind 5.1
In India, Clause 5.1 has a regulatory weight that goes far beyond the ISO standard itself. The lineage is the same lineage that anchors the companion Clause 5.2 guide: K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 declared informational privacy a fundamental right; the Aadhaar judgment, (2019) 1 SCC 1 set the proportionality test; the DPDP Act 2023 (enacted 11 August 2023) operationalised the right; the DPDP Rules 2025 (notified 13 November 2025, with phased commencement) operationalised the Act; and ISO/IEC 27701:2025 (published 14 October 2025) is the management-system lens through which an Indian Data Fiduciary can demonstrably satisfy the DPDP obligations. Clause 5.1 is the lens for the leadership dimension specifically.
The DPDP Act and the Companies Act bear on Clause 5.1 across at least eight provisions.
DPDP section 8(5), reasonable security safeguards. The Data Fiduciary must implement reasonable security safeguards to maintain the integrity, confidentiality and availability of personal data. "Reasonable" is informed by the resources allocated, the awareness programme run, the integration gates operated, the breach capability maintained, all Clause 5.1 conduct. The Schedule ceiling for failure on section 8(5) is 250 crore rupees.
DPDP section 8(6), breach notification. The Data Fiduciary must notify the Board and each affected Data Principal in the form and manner prescribed. The DPDP Rules 2025 Rule 7 prescribes 72 hours of becoming aware, with the prescribed intimation content. Top management owns the dual-clock capability (CERT-In 6 hours and DPDP 72 hours, running in parallel). Failure on section 8(6) can attract up to 200 crore rupees.
DPDP section 10, Significant Data Fiduciary. The SDF must appoint a DPO based in India accountable to the Board of Directors or governing body, perform a DPIP for each new processing activity, perform periodic independent data audits, and conduct an algorithmic-AI fairness review. The section 10 DPO-accountability-to-board requirement is the densest overlap with ISO/IEC 27701:2025 Clause 5.1. Failure on the section 10 obligations can attract up to 150 crore rupees.
DPDP section 11 to 14, rights of Data Principals. The Data Fiduciary must operate the rights-handling workflow (access, correction and erasure, grievance redressal, nomination). Top management owns whether the workflow is resourced. Section 13 grievance redressal has a prescribed response period, a leadership-reporting KPI.
DPDP section 33 and the Schedule, penalties. The Schedule maxima run to 250 crore rupees. The Board's analysis of penalty quantum tests leadership conduct directly.
Companies Act 2013 section 134(3)(n). The Board's Report must include the risk-management policy statement. Privacy risk is in scope. The board statement is the natural board-visible artefact of Clause 5.1 conduct.
Companies Act 2013 section 177 and SEBI LODR Regulation 21. The Audit Committee and the Risk Management Committee oversee privacy and cyber risk for listed entities. The RMC is the natural recipient of the privacy pack.
CERT-In Directions 20(3)/2022-CERT-In (28 April 2022). The 6-hour cyber-incident-report clock. The DPDP 72-hour Board-notification clock. The dual clock is the marquee test of whether top management has integrated privacy into the organisation's incident-response capability.
In aggregate: in India, top-management leadership of the PIMS is not optional, it is a multi-regulator duty with monetary penalties attached (DPDP up to 250 crore rupees; RBI enforcement; SEBI penalties; IRDAI direction; CERT-In action). ISO/IEC 27701:2025 Clause 5.1 is the natural single framework through which an Indian organisation can demonstrably evidence this duty, which is one of the strongest commercial arguments for pursuing ISO/IEC 27701:2025 certification in the Indian market.
The cost of non-compliance
The cost of a Clause 5.1 failure breaks down into four bands.
Direct DPDP penalty exposure is the most visible. The Schedule maxima run to 250 crore rupees for failure on section 8(5) safeguards and 200 crore rupees for failure on breach notification or children's data, and 150 crore rupees for failure on the SDF obligations. But the Schedule is the headline ceiling, and the leadership-conduct quality directly informs the Board's "adequate safeguards" analysis under section 8(5) and the "adequate notification" analysis under section 8(6). A Data Fiduciary whose top management cannot demonstrate the eight leadership moves is unlikely to make an adequate-safeguards case.
Indirect regulatory consequences are larger and slower. A leadership failure that produces a privacy incident can support a finding of unfair trade practice under the Consumer Protection Act 2019, a section 43A compensation claim, and parallel proceedings by sector regulators (RBI ombudsman scheme, SEBI investor grievance mechanism, IRDAI grievance redressal). For listed entities, a material privacy failure triggers disclosure obligations under SEBI LODR and may constitute a price-sensitive event.
Commercial cost is the largest single category. The Indian incidents most cited in board rooms, MobiKwik 2021 (contested allegations of approximately 3.5 million to approximately 110 million records exposed; the company denied the breach; subsequently substantiated by independent verification), Juspay (approximately 35 million records in 2021, publicly acknowledged), BigBasket (approximately 20 million records alleged in 2020), Air India / SITA (approximately 4.5 million customers affected, disclosed February-May 2021), AIIMS Delhi ransomware (23 November 2022), all carried commercial costs in churn, brand damage, customer-acquisition drag, and regulatory scrutiny. None was a Clause 5.1 failure in isolation, but in every case the post-incident regulatory and litigation examination tested whether leadership had visibly led the privacy programme.
Certification cost is the most immediate for ISO/IEC 27701:2025 candidates. The remediation is leadership-attention time, which is the most expensive kind, the bottleneck is almost always sponsor availability for the workshop and the interview rehearsal. A Clause 5.1 minor nonconformity at Stage 2 delays the certificate issue by 4 to 12 weeks. Both are recoverable; both are entirely avoidable with the discipline this guide sets out.
The board-level angle
For Indian listed companies and BFSI, and for any organisation designated or likely to be designated as a Significant Data Fiduciary under DPDP section 10, the privacy leadership discipline is increasingly a board-level matter, not a management matter. Section 134(3)(n) of the Companies Act 2013 places the risk-management statement in the Board's Report; SEBI LODR Regulation 21 places privacy within the Risk Management Committee mandate; DPDP section 10 makes the SDF DPO accountable to the Board; the RBI Cybersecurity Directions 2026 (31 July 2026) require board-approved IT policies for regulated entities; the SEBI CSCRF (20 August 2024) requires a board-approved cyber-resilience policy; the IRDAI ICS 2023 (24 April 2023) requires board-approved information and cyber security policy. The board-level angle is not theoretical: a privacy leadership discipline the board has not directed, or has not reviewed, is a governance gap a regulator will name in any post-incident proceeding.
The practical implication for the DPO and the executive sponsor: the privacy pack presented to the board must be board-grade. That means short (typically a 4 to 8 page pack with a one-page executive summary), well-structured (the year's risks, the year's objectives, the year's incidents, the year's KPIs, the year's resource ask, the year's regulator interactions), free of jargon, dated, version-controlled, and accompanied by a sponsor briefing that prepares board members to ask informed questions. The DPO prepares the pack; the sponsor presents it; the board or RMC notes and directs. The pack is the board-visible artefact of Clause 5.1 conduct, and it is the single artefact most likely to convert a defensive privacy posture into a governance-grade one.
Scope and Applicability
By organisation size
Growing companies (50 to 250 staff). A single executive sponsor (typically the CEO, MD or COO) and a single DPO or Privacy Lead (often wearing multiple hats) cover the whole organisation. The PIMS Steering Committee is typically a quarterly 90-minute meeting of the sponsor, the DPO, the CISO (if separate), the Head of Legal, the Head of Product, and the Head of HR. The board visibility for a non-listed growing company is typically annual at the management review; listed growing companies add a board RMC noting. The integration gates are lightweight, a privacy check in the product-launch checklist, a privacy check in the vendor-onboarding checklist, a privacy check in the marketing-campaign approval. The first cycle (sponsor statement, governance structure, calendar, budget, gates, awareness) is deliverable in 4 to 8 weeks of internal effort plus optional external advisory.
Mid-market (250 to 2,000 staff). The sponsor is typically a Whole-Time Director or the CEO; the DPO is typically a dedicated role reporting to the sponsor or to the top-management team. The PIMS Steering Committee meets quarterly with documented decisions and a standing agenda; sub-forums (a privacy-by-design working group, a vendor-privacy working group, an incident-response committee) feed into it. For likely-SDF entities, the SDF-readiness work begins in this band, the DPO-accountability-to-board reporting line is stood up, the DPIP register is initiated, the independent-audit cadence is planned. Integration gates are formalised in the product life cycle, the vendor life cycle and the M&A diligence process.
Multi-entity enterprise (2,000-plus staff or multi-site). A group privacy function typically sits at the group level, with entity-level DPOs or Privacy Leads and a defined parent-subsidiary reporting hierarchy. The group executive sponsor is typically the Group CEO, the Group COO, or a Group Chief Privacy Officer at the top-management table. The group PIMS Steering Committee is typically a monthly forum with quarterly entity-level reporting. The board / RMC pack is produced quarterly; for SDFs, the section 10 DPO-accountability-to-board pack is produced at the cadence the Board prescribes. Integration gates are formalised across the group; the M&A privacy diligence is a dedicated workstream. For SDFs (DPDP section 10), this band is the typical floor, the SDF DPO, DPIP and audit obligations add cost on top.
By controller/processor role
PII controller only. Top management leads the full Annex A.1 control set; the leadership commitment covers the principal-facing obligations (notice, consent, rights, retention, breach notification to principals). DPDP section 8 duties apply directly; the Schedule ceiling of 250 crore rupees applies.
PII processor only. Top management leads the Annex A.2 control set (the processor-side controls, about 18 controls in the 2025 consensus count); the leadership commitment covers the processor-facing obligations (the DPA terms, the sub-processor list, the breach-notification SLA to controllers, the infringing-instruction process, the cross-border transfer handling). The DPDP section 8 duties apply through the controller relationship; the processor's leadership commitment is to operate the controller's instructions lawfully and to maintain the capability to do so.
Both controller and processor. Most Indian growing companies of any scale are both, controller for employee data, customer CRM data, finance data; processor for the customer data they handle under SaaS or BPO contracts. Top management leads both control sets; the leadership commitment is dual. The Statement of Applicability (Clause 6.1.3 e), the risk assessment scope (Clause 6.1.2) and the audit programme (Clause 9.2) all reflect both roles.
By industry (summary, full detail in Section 21)
| Industry | Distinctive 5.1 emphasis |
|---|---|
| BFSI (banks, NBFCs, insurers, payment systems, MIIs) | Board oversight of information and cyber risk is mandated by RBI Cybersecurity Directions 2026 (31 July 2026), SEBI CSCRF (20 August 2024) and IRDAI ICS 2023; privacy leadership builds on it. The board / RMC pack is quarterly. The SDF overlay applies to most large BFSI entities. The dual-clock breach commitment (DPDP 72 hours plus CERT-In 6 hours) is supplemented by RBI six-hour and SEBI 6-hour clocks. |
| Healthcare (hospitals, pharma, devices, diagnostics, telemedicine) | Patient data is sensitive. Likely SDF designation for large healthtech platforms. Leadership owns the consent-to-treat versus consent-to-process integration and the AI diagnostic-assist algorithmic-fairness overlay. Section 9 children's dimension requires leadership-owned verifiable-parental-consent capability. |
| IT / ITeS and SaaS | The processor track is critical. Leadership owns the customer DPA framework, the sub-processor governance, the infringing-instruction process (Annex A.2.2.5), the cross-border transfer impact assessment. Customer trust portal publication is a leadership-owned sales asset. |
| E-commerce / Retail | Notice quality, consent for marketing, cookie/SDK consent, behavioural advertising opt-out, children's-data safeguards (section 9) dominate. Leadership owns the marketplace-versus-seller role declaration and the loyalty-programme data flows. |
| Edtech | Children's data (DPDP section 9) is the marquee challenge. Leadership owns the verifiable-parental-consent capability and the no-behavioural-monitoring / no-targeted-advertising commitment. These are section 9 hard requirements, with direct 200-crore-rupee Schedule exposure. |
| Manufacturing | Employee data, vendor data, OT/IT convergence, biometric access control, CCTV. Leadership owns the workplace-data dimension and the cross-border group-company data flows. |
By geographic footprint
Single-state Indian operations. Top management leads against the DPDP Act + DPDP Rules, IT Act/SPDI, sectoral regulation if any, and the relevant state-level instruments. The board pack is in English plus the state language.
Pan-India operations. Top management leads against DPDP Act + Rules, IT Act/SPDI, CERT-In Directions, sectoral regulation (RBI/SEBI/IRDAI as applicable), with multilingual board-pack content where the board composition requires it.
India-plus-overseas operations. Top management leads against the global regulator regime, GDPR for EU/EEA data subjects, UK GDPR for UK data subjects, CCPA/CPRA for California, LGPD for Brazil, PIPL for China, PDPA for Singapore and other APAC instruments. The Indian parent leadership commitment typically commits to meeting the most stringent of these; entity-level leadership operationalises locally. The Annex A.1.5.2 / A.2.5.2 cross-border transfer controls require top-management sign-off on the documented transfer basis.
Key Definitions and Terminology
Clause 5.1 uses a small number of terms precisely. The harmonized structure vocabulary (ISO/IEC Directives Annex SL), the ISO/IEC 27000 family vocabulary, and the ISO/IEC 29100:2011 privacy framework definitions are the international sources; the DPDP Act 2023 section 2 definitions are the Indian source.
Top management
In harmonized-structure usage, top management is the person or group of people who direct and control an organisation at the highest level. In an Indian growing company this is typically the CEO, MD, the founding partners, the Board, or the top-management team. Top management is not the DPO, the CISO, the Head of Legal or the Head of Compliance, those are management roles. Top management is the level above them. The Clause 5.1 commitment is made at this level and is non-delegable in substance (even where operational delivery is delegated).
Executive sponsor
The executive sponsor is the named individual at top-management level who is the single point of accountability for the PIMS. The sponsor is typically the CEO, COO, a Whole-Time Director, or a designated Top-Management Privacy Champion. The sponsor signs the sponsor commitment statement; chairs or co-chairs the PIMS Steering Committee; hosts the privacy town-hall; presents the privacy pack to the board or RMC; sits the certification audit interview; owns the dual-clock breach commitment. The sponsor's name and signature are the load-bearing evidence of Clause 5.1 conduct.
DPO / Privacy Lead
The Data Protection Officer or Privacy Lead is the management role responsible for running the PIMS day-to-day. Under DPDP Act 2023 section 10, an SDF's DPO is a statutory role: based in India, accountable to the Board of Directors or governing body. The DPO drafts the privacy policy and notice (Clause 5.2); maintains the ROPA (Clause 8 / Annex A.1.2.x); runs the DPIA process (Annex A.1.2.5); operates the rights-handling workflow (Annex A.1.3.x); runs the awareness programme (Clause 7.3); prepares the management review (Clause 9.3); and is the natural incident-response commander for privacy incidents. The DPO is the expert; the sponsor is the leader.
PIMS Steering Committee
The PIMS Steering Committee (sometimes called the Privacy Committee or the Privacy Governance Forum) is the cross-functional top-management-level forum that oversees the PIMS between board pack cycles. Typical membership: the sponsor (chair), the DPO (secretary), the CISO, the Head of Legal, the Head of Product, the Head of HR, the Head of Vendor Management, the Head of Marketing. Typical cadence: quarterly, with monthly sub-forums. The committee's charter, minutes and decisions are the load-bearing evidence of Clause 5.1's "directing and supporting persons" limb.
Data Fiduciary
Under DPDP Act 2023 section 2(1)(i), the Data Fiduciary is the entity that, alone or in conjunction with others, determines the purpose and means of processing personal data. The DPDP analogue of the ISO/IEC 29100 "PII controller" and the GDPR Article 4(7) "controller". The Data Fiduciary carries the principal-facing obligations under sections 4 to 14, the reasonable-security-safeguards duty under section 8(5), the breach-notification duty under section 8(6), and the bulk of the Schedule penalty exposure. The Data Fiduciary's top management owns Clause 5.1 conduct as a statutory duty, not just a management-system preference.
Significant Data Fiduciary (SDF)
Under DPDP Act 2023 section 10, a Significant Data Fiduciary is a Data Fiduciary designated by the Central Government on the basis of prescribed thresholds (volume and sensitivity of personal data processed, risk to data principals, impact on sovereignty, integrity and electoral democracy, etc.). The SDF must appoint a DPO based in India accountable to the board; perform a DPIP for each new processing activity; perform periodic independent data audits; and conduct an algorithmic-AI fairness review where relevant. The SDF overlay is the densest overlap with ISO/IEC 27701:2025 (Clauses 5.1, 5.3, 6.1.2, 8.2, Annex A.1.2.5).
Data Protection Board of India (DPBI / the Board)
Under DPDP Act 2023 section 18, the Board is the independent regulatory authority established by the Central Government, the DPDP analogue of a GDPR supervisory authority. The Board adjudicates, imposes penalties up to the Schedule maxima, and is the recipient of the 72-hour breach notification under section 8(6) and Rule 7. The Board is an interested party under Clause 4.2; top management owns the regulator-engagement capability (the leadership commitment includes "what happens when the Board calls").
Privacy leadership evidence
Privacy leadership evidence is the bundle of artefacts that evidences Clause 5.1 conduct. It includes: the signed sponsor commitment statement; the governance-structure document; the PIMS Steering Committee charter, membership, and minutes (typically four per year); the board / RMC pack (typically two to four per year for SDFs and listed entities); the privacy budget approval; the awareness programme calendar and materials; the integration-gate log (privacy checks in product, vendor, M&A, marketing, SDLC); the management review minute (Clause 9.3); the breach tabletop exercise record; the sponsor's certification audit interview preparation notes. The leadership evidence file is what the auditor reviews alongside the sponsor interview.
Business-process integration
Business-process integration is the marquee Clause 5.1 requirement that the PIMS requirements be woven into the organisation's business processes. Operationally, this means privacy checkpoints at: product launch, vendor onboarding, M&A diligence, marketing campaign approval, software-development lifecycle gates, HR onboarding, data-sharing agreement approval, cross-border transfer approval, AI/deployment approval. Each gate has a privacy check, a documented decision and an escalation route to the DPO and (where material) the sponsor.
Dual-clock breach commitment
The dual-clock breach commitment is the leadership-owned undertaking that the organisation will maintain the capability to intimate the Data Protection Board of India without delay on becoming aware of a personal data breach and file the detailed report within 72 hours (DPDP section 8(6) + DPDP Rules 2025 Rule 7) and to notify CERT-In within 6 hours of noticing a prescribed cyber incident (CERT-In Directions 20(3)/2022-CERT-In). For BFSI: add the RBI six-hour clock and the SEBI RE 6-hour clock. The dual clock runs in parallel from the same awareness event. The commitment is the marquee test of whether top management has integrated privacy into the organisation's incident-response capability.
Management review
Under Clause 9.3, the management review is the planned-interval top-management review of the PIMS. Top management owns it. The review agenda includes: the status of actions from previous management reviews; changes in external and internal issues; information on PIMS performance (audit results, compliance, objective achievement, incident performance, corrective actions, performance of other parties); resource adequacy; effectiveness of actions taken to address risks and opportunities; opportunities for improvement. The sponsor chairs or co-chairs; the DPO prepares; the board / RMC receives the outcome. The management review is the apex Clause 5.1 forum.
Risk Management Committee (RMC)
Under SEBI LODR Regulation 21, the Risk Management Committee is the board committee (for listed entities) mandated to oversee risk, including cyber, operational and privacy risk. The RMC is the natural board-level recipient of the privacy pack for listed entities. The Companies Act 2013 section 177 Audit Committee has a parallel oversight role for financial-reporting risks, which increasingly includes privacy-related provisions and contingencies.
Relationship to Other Clauses and Frameworks
Relationship to other ISO/IEC 27701:2025 clauses
Clause 5.1 is the apex leadership clause of the PIMS. Its relationships to the other clauses are the spine of the system.
- Clause 4.1 (Context). Top management directs the PIMS to address the internal and external issues identified under Clause 4.1, including the organisation's role as PII controller and/or processor.
- Clause 4.2 (Interested parties). Top management ensures the PIMS addresses the needs of interested parties, PII principals, regulators (DPBI, RBI, SEBI, IRDAI, CERT-In, EDPB national DPAs), customers, processors, sub-processors, employees.
- Clause 4.3 (Scope). Top management approves the PIMS scope.
- Clause 4.4 (PIMS). Top management establishes, implements, maintains and continually improves the PIMS.
- Clause 5.2 (Privacy Policy). Top management establishes the privacy policy (see the companion Singahi Clause 5.2 guide).
- Clause 5.3 (Roles, Responsibilities, Authorities). Top management assigns the privacy roles, the DPO/Privacy Lead, the SDF section 10 DPO, the PIMS Steering Committee, the data owners.
- Clause 6.1 (Risks and opportunities). Top management owns the privacy risk decision, the SoA sign-off, the risk-treatment direction, the risk-appetite statement.
- Clause 6.2 (Privacy objectives). Top management sets the framework for privacy objectives and ensures the objectives are compatible with the strategic direction.
- Clause 6.3 (Change). Top management owns planned PIMS changes.
- Clause 7.1 (Resources). Top management ensures the resources are available, the privacy budget, the DPO headcount, the awareness programme investment, the platform investments.
- Clause 7.2 (Competence). Top management ensures competence, the DPO's CIPM/CIPP/E credentials, the engineers' privacy-by-design training, the HR team's consent-handling competence.
- Clause 7.3 (Awareness). Top management communicates the importance of effective privacy management, the sponsor's town-hall, the all-hands, the visible enforcement.
- Clause 7.4 (Communication). Top management owns the communication discipline.
- Clause 7.5 (Documented Information). Top management ensures Documented Information is controlled, the policy, the ROPA, the DPIA register, the consent records, the breach playbook.
- Clause 8.1 (Operational planning and control). Top management ensures the operational processes run.
- Clause 8.2 (Privacy risk assessment). Top management owns the detailed privacy risk assessment and the DPIP process.
- Clause 8.3 (Privacy risk treatment). Top management owns the treatment decisions, including the SoA.
- Annex A.1 (PII controllers). Top management owns the controller obligations, the conditions for processing, the notice, the consent framework, the rights-handling capability, the privacy-by-design integration, the cross-border transfer framework, the disclosures framework.
- Annex A.2 (PII processors). Top management owns the processor framework, the DPA terms, the sub-processor governance, the infringing-instruction process, the cross-border handling.
- Annex A.3 (Information security controls). Top management owns the SoA sign-off and the resourcing of the security controls.
- Clause 9.1 (Monitoring and measurement). Top management owns the monitoring and measurement discipline.
- Clause 9.2 (Internal audit). Top management ensures the audit programme is independent, resourced, and reported to the Audit Committee.
- Clause 9.3 (Management review). Top management chairs the management review, the apex Clause 5.1 forum.
- Clauses 10.2 and 10.1 (Improvement). Top management owns the corrective-action and continual-improvement discipline.
Relationship to other ISO management-system standards
ISO/IEC 27701:2025 uses the Harmonized Structure shared by ISO/IEC 27001:2022, ISO 22301:2019, ISO 9001:2015, ISO/IEC 42001:2023, and others. Clause 5.1 in each is the leadership clause. An organisation running more than one of these systems has an integration opportunity: a single sponsor or a tightly-aligned sponsor set can satisfy all of them.
- ISO/IEC 27001:2022 Clause 5.1, the ISMS leadership clause. Structurally identical. Common Indian integration: a single sponsor leading an integrated ISMS+PIMS. ISO/IEC 27002:2022 control 5.34 (Privacy and protection of PII) is the only PII-specific control in 27002, the bridge between the ISMS and the PIMS leadership.
- ISO 22301:2019 Clause 5.1, the BCMS leadership clause. The intersection with the PIMS is the DPDP section 8(5) availability duty, the BCMS leadership commits to continuity of processing; the PIMS leadership commits to availability of personal data.
- ISO/IEC 42001:2023 Clause 5.1, the AIMS (AI management system) leadership clause. The intersection with the PIMS is the DPDP section 10 SDF algorithmic-AI fairness review, the AIMS leadership commits to AI governance; the PIMS leadership commits to AI fairness.
- ISO 9001:2015 Clause 5.1, the QMS leadership clause. For Indian manufacturers running ISO 9001, integrated QMS+PIMS leadership is increasingly common where the data dimension is light.
- ISO/IEC 20000-1:2018 Clause 5.1, the SMS (service management) leadership clause. Integration opportunity for IT-service firms.
The full multi-framework mapping (Clause 5.1 row)
The detailed mapping with marquee IDs and dates is in Section 16. The headline cross-framework anchors for Clause 5.1 are:
- ISO/IEC 27701:2025 Clause 5.1, the requirement itself.
- Annex B (normative) section B.5.1, the implementation guidance auditors test against.
- ISO/IEC 27001:2022 Clause 5.1 and control 5.34, the ISMS leadership clause and the PII-protection control.
- ISO/IEC 27002:2022 control 5.34, the only PII-specific control in 27002.
- ISO/IEC 29100:2011, the accountability privacy principle (the leadership principle).
- ISO/IEC 29134:2017, the DPIA methodology that top management resourcing enables.
- ISO/IEC 27018:2019, the cloud-processor code that top management processor governance aligns with.
- GDPR Article 5(2) (accountability), Article 24 (controller responsibility, the densest GDPR analogue of Clause 5.1), Article 25 (data protection by design and by default, leadership owns the integration), Article 28(3) (DPA mandatory clauses, leadership owns the processor framework), Article 32 (security of processing, leadership owns the resourcing), Articles 33 to 34 (breach notification, leadership owns the dual-clock commitment), Articles 35 to 36 (DPIA and prior consultation, leadership owns the trigger decision), Articles 37 to 39 (DPO, leadership owns the appointment), Article 83 (fines).
- NIST Privacy Framework v1.0 (NIST.CSWP.01162020, 16 January 2020), Govern-P function (governance structure, privacy roles, risk-management strategy, policy, the US-flavoured structural analogue of Clause 5.1).
- SOC 2 (AICPA TSC 2017, with 2022 PoF update), P8.0 (Monitoring and enforcement) and the Common Criteria CC1 (Control Environment / Tone at the Top). CC1.1 through CC1.5 are the closest SOC 2 analogue of Clause 5.1, the board and management commitment to the system.
- DPDP Act 2023, sections 8(5), 8(6), 10 (SDF DPO accountability-to-board), 33 + Schedule.
- DPDP Rules 2025, Rule 7 (breach 72 hours); the SDF rules; the section 13 grievance rules.
- Companies Act 2013, section 134(3)(n) (risk-management statement); section 177 (Audit Committee).
- SEBI LODR, Regulation 21 (Risk Management Committee).
- RBI Cybersecurity Directions 2026 (31 July 2026), board-approved IT policy for REs.
- SEBI CSCRF (20 August 2024), board-approved cyber-resilience policy.
- IRDAI ICS 2023 (24 April 2023), board-approved information and cyber security policy.
- CERT-In Directions 20(3)/2022-CERT-In (28 April 2022), 6-hour incident report; Point of Contact appointment.
Detailed Implementation Guidance, The Eight Leadership Moves
This section sets out the eight leadership moves a growing company in India must execute to satisfy Clause 5.1 in a form that survives both an IAF-accredited certification audit under the new ISO/IEC 27706:2025 scheme and a post-incident regulatory inspection by the Data Protection Board of India. Each move has an input, an output, an owner, an indicative effort, and a list of common failure modes. Treat them as a sequence for the first cycle and as a parallel cadence thereafter.
Move 1, Stand up the privacy governance structure
Input. The Clause 4.1 context register, the Clause 4.2 interested-party register, the Clause 4.3 scope statement, the controller/processor role declaration, the existing governance map (board, board committees, top-management team, management forums), the regulatory landscape, and the executive sponsor's strategic narrative.
Output. A documented privacy governance structure with five components.
-
The named executive sponsor at top-management level. One individual. Named, with title, signed sponsor commitment statement (Move 2). For SDFs and listed entities, the sponsor is typically a Whole-Time Director or the CEO; for non-listed growing companies, the sponsor is typically the CEO or MD.
-
The named DPO or Privacy Lead. For SDFs under DPDP section 10, an India-based DPO accountable to the board. For non-SDF growing companies, a Privacy Lead (often wearing multiple hats). The reporting line to the sponsor is documented.
-
The PIMS Steering Committee with a documented charter, named membership (typically the sponsor as chair, the DPO as secretary, the CISO, Head of Legal, Head of Product, Head of HR, Head of Vendor Management, Head of Marketing), quarterly cadence, and a standing agenda (the year's risks, the year's objectives, the year's incidents, the year's KPIs, the year's regulator interactions, the year's resource ask, integration-gate decisions, audit findings).
-
The board or RMC reporting channel. For SDFs and listed entities, a defined cadence (typically quarterly for SDFs, half-yearly for listed non-SDF entities) and a board-grade pack format. For non-listed growing companies, an annual noting at the management review.
-
The sub-forums that feed the Steering Committee, typically a privacy-by-design working group (Product, Engineering, DPO), a vendor-privacy working group (Procurement, Legal, DPO), an incident-response committee (sponsor, DPO, CISO, Legal, Communications), and a data-principal-rights review forum (DPO, Customer Success, Legal).
Owner. Executive sponsor appoints the DPO and chairs the Steering Committee; Company Secretary schedules board / RMC noting; DPO drafts the charter and the standing agenda.
Indicative effort. Two to four weeks of calendar time for the structure design and the charter; one half-day workshop to launch.
Common failure modes. (a) Sponsor named but no DPO appointed, fails the Clause 5.3 test. (b) Steering Committee exists on paper but never meets, fails the audit evidence test. (c) Board / RMC channel not defined for SDFs and listed entities, fails the DPDP section 10 / SEBI LODR / Companies Act test. (d) Sub-forums not defined, the Steering Committee becomes a bottleneck; decisions are not prepared. (e) Charter not documented, the auditor cannot test the structure. (f) Reporting line of the DPO to the sponsor unclear, fails the accountability test. (g) DPO reports to Legal or Compliance without a top-management line, fails the independence-of-the-DPO test (GDPR Article 38; DPDP section 10 spirit).
Move 2, Make and evidence the executive sponsor's commitment
Input. The governance structure from Move 1; the strategic narrative from the board or top-management team; the privacy risk assessment (Clause 6.1.2); the regulatory landscape; the privacy budget envelope.
Output. A signed one-page sponsor commitment statement that names:
- The sponsor's name, role, and signature (on letterhead, dated, version-controlled).
- The four commitment statements (paraphrased from the harmonized structure): accountability for the effectiveness of the PIMS; ensuring the privacy policy and objectives are established and compatible with the strategic direction; ensuring the integration of the PIMS requirements into the organisation's business processes; ensuring the resources the PIMS needs.
- The privacy-specific commitments: lawful, fair and transparent processing; purpose limitation; data minimisation; accuracy; storage limitation; integrity, confidentiality and availability (DPDP section 8(5)); accountability (GDPR Article 5(2)); privacy by design and by default; lawful cross-border transfer; data principal rights and grievance redressal (DPDP sections 11 to 14); protection of children's and vulnerable persons' data (DPDP section 9); breach notification capability (the dual-clock commitment, DPDP section 8(6) 72 hours and CERT-In 6 hours).
- The resource commitment: the privacy budget line for the year (an indicative figure, not a detailed breakdown); the DPO headcount; the awareness programme investment; the platform investments planned.
- The reporting commitment: the Steering Committee cadence; the board / RMC cadence; the management review cadence; the certification audit participation commitment.
- The escalation commitment: the sponsor's availability on the incident-escalation chain; the sponsor's commitment to chair or co-chair the management review; the sponsor's commitment to sit the certification audit interview.
- The next review date.
The sponsor commitment statement is the single most load-bearing artefact of Clause 5.1 conduct. The auditor will ask for it first; the regulator will ask for it first after an incident; the board / RMC will note it. It is short, signed, dated, version-controlled.
Owner. Executive sponsor signs; DPO prepares; Company Secretary schedules board noting if applicable.
Indicative effort. One workshop day to draft; one sponsor iteration cycle; signature.
Common failure modes. (a) Statement signed but undated, fails the Documented Information test. (b) Statement generic ("we comply with applicable privacy laws"), fails the substantive commitment test. (c) Statement signed by the DPO instead of the sponsor, fails the top-management accountability test. (d) Resource commitment absent, fails the Clause 7.1 resourcing test. (e) Reporting commitment absent, fails the Clause 9.3 management-review test. (f) Escalation commitment absent, fails the dual-clock breach commitment test. (g) Statement not refreshed on event trigger (sponsor change, SDF designation, breach, regulatory change), fails the Documented Information currency test.
Move 3, Integrate privacy into business processes
Input. The organisation's existing business-process map (product lifecycle, vendor lifecycle, M&A process, marketing approval, software-development lifecycle, HR onboarding, data-sharing approval, cross-border transfer approval, AI/deployment approval); the privacy requirements (Annex A.1 conditions, A.1.4 privacy by design, A.2 processor conditions); the DPO's capacity to run the gates.
Output. Documented privacy integration gates at eight points in the business.
-
Product launch gate. Every new product or material product change passes a privacy review before launch. The review covers the lawful basis, the notice, the consent flow, the data-sharing relationships, the cross-border transfers, the retention, the children's-data dimension, the AI/ADM dimension, the privacy-by-design controls. The review is documented; the decision is signed by the DPO; material decisions are escalated to the Steering Committee.
-
Vendor onboarding gate. Every new processor or sub-processor passes a privacy due diligence before contract. The due diligence covers the DPA terms (Annex A.2.2.x and A.2.5.x), the sub-processor list, the breach-notification SLA, the infringing-instruction process, the cross-border transfers, the security controls (Annex A.3), the deletion-on-termination commitment. The due diligence is documented; the decision is signed by Procurement and the DPO.
-
M&A diligence gate. Every material acquisition, divestiture or partnership passes a privacy diligence. The diligence covers the target's privacy posture, the data-sharing implications, the consent implications for the inherited data principal base, the regulatory exposure, the integration risks. The diligence is documented; material findings are escalated to the sponsor and the board / RMC.
-
Marketing campaign approval gate. Every marketing campaign that involves personal data (email, SMS, push, behavioural advertising, profiling) passes a privacy check. The check covers the consent basis, the suppression list, the cross-border dimension, the children's-data dimension, the behavioural-advertising opt-out.
-
Software-development gate. Every material software change passes a privacy check at the design stage (privacy by design, Annex A.1.4 / A.2.4) and at the deployment stage. The check covers the data flows, the consent integration, the data-subject-rights surface, the retention implementation, the security controls (Annex A.3), the AI/ADM logic where applicable.
-
HR onboarding gate. Every new joiner receives the privacy policy-on-a-page (Move 5 awareness programme), acknowledges the internal policy, and is briefed on the reporting channels (the grievance officer, the breach-reporting channel, the whistleblower channel).
-
Data-sharing agreement approval gate. Every new data-sharing relationship with a controller, joint controller, or processor passes a privacy review and a DPA check.
-
Cross-border transfer approval gate. Every new cross-border transfer passes a negative-list screen (DPDP section 16) and, for non-adequate destinations under GDPR, a Schrems-II-aware transfer impact assessment.
Owner. DPO runs the gates; process owners (Product, Procurement, M&A, Marketing, Engineering, HR) operate them; sponsor ensures they exist and are operated.
Indicative effort. One-time setup of 4 to 8 person-weeks across the DPO and the process owners; ongoing 1 to 3 person-days per gate invocation.
Common failure modes. (a) Gates exist on paper but no decisions documented, fails the integration evidence test. (b) Gates too heavyweight, process owners route around them; fails the "integrated into business processes" test. (c) Gates too lightweight, privacy decisions are rubber-stamped; fails the substantive-integration test. (d) DPO bottleneck, gates queue up and the business loses patience; fails the resourcing test. (e) Gates not wired into existing tooling (the issue-tracker, the IT-service-management platform, the procurement system), fails the operationalisation test. (f) Material gates not escalated to the Steering Committee, fails the leadership-direction test.
Move 4, Set the privacy objective cascade and resource the PIMS
Input. The strategic direction of the organisation; the privacy risk assessment outputs; the regulatory landscape; the previous year's performance; the sponsor commitment statement.
Output. Three artefacts.
-
The privacy objective cascade. Top management sets the framework for privacy objectives (Clause 6.2). The objectives are SMART (Specific, Measurable, Achievable, Relevant, Time-bound); they cover the dimensions that matter for the organisation (consent-record completeness, DSAR turnaround, grievance resolution time, breach-detection-to-notification time, DPIA coverage, training completion, third-party privacy assessment scores, retention-deletion compliance); they cascade to process-owner performance management; they are reviewed at the management review.
-
The competence plan. Top management ensures competence (Clause 7.2). The plan covers the DPO's credentials (typically CIPM, CIPP/E, CIPT, the IAPP credentials); the engineers' privacy-by-design training; the HR team's consent-handling training; the customer-success team's data-principal-rights training; the leadership team's privacy fluency (typically a half-day annual sponsor and top-management briefing).
Owner. Top management sets the framework; DPO drafts the objectives; HR and Finance operationalise the budget and the competence plan.
Indicative effort. One-time setup of 2 to 4 person-weeks; annual refresh of 1 to 2 person-weeks.
Common failure modes. (a) Objectives set but not cascaded to performance management, fails the "directing and supporting persons" test. (b) Budget absent or bundled into IT without identification, fails the resourcing test. (c) Competence plan absent, fails the Clause 7.2 test. (d) Objectives not SMART, fails the Clause 6.2 test. (e) Objectives not reviewed at the management review, fails the Clause 9.3 test.
Move 5, Communicate the importance (the awareness discipline top management owns)
Input. The sponsor commitment statement; the privacy policy (Clause 5.2); the awareness programme plan (Clause 7.3); the year's incidents and learnings.
Output. A five-strand communication programme.
-
The sponsor's privacy town-hall. Annual (or semi-annual). The sponsor hosts, the DPO supports. The town-hall covers the year's privacy risks, the year's objectives, the year's incidents and learnings, the year's regulatory changes, the sponsor's expectations of staff. Recorded for field sites and absent staff.
-
The new-joiner induction. Every new joiner receives the privacy policy-on-a-page, the reporting channels, and the breach-reporting duty in their first 30 days. Acknowledgement captured (Move 6).
-
The annual awareness refresh. Every staff member acknowledges the privacy policy annually; the DPO runs a 30- to 45-minute refresh session.
-
The process-owner and engineer briefing. Process owners, product managers and engineers receive a deeper briefing on privacy by design, the integration gates, the DPIA process, the consent-flow design.
-
The top-management and board briefing. The sponsor, the top-management team, and the board / RMC receive an annual privacy briefing, the year's risks, the year's regulatory landscape, the year's incidents, the year's resource ask, the management review outcome. The board briefing is the board pack delivery (Move 7).
Owner. Sponsor hosts the town-hall; DPO runs the refresh and the process-owner briefing; HR runs the new-joiner induction; Company Secretary schedules the board briefing.
Indicative effort. Ongoing, typically 2 to 3 person-weeks per quarter for the DPO; 1 to 2 person-days per year for the sponsor.
Common failure modes. (a) Town-hall absent or recorded-but-never-watched, fails the "communicating the importance" test. (b) No new-joiner induction component, staff onboarded in the gap between annual refreshes are missed. (c) No acknowledgement mechanism, the auditor cannot evidence communication. (d) Sponsor not hosting, fails the leadership-visibility test. (e) Board briefing absent, fails the board-oversight test for SDFs and listed entities.
Move 6, Capture and maintain the leadership evidence base
Input. The sponsor commitment statement; the governance structure; the Steering Committee minutes; the board / RMC packs; the budget approval; the awareness programme calendar and attendance; the integration-gate log; the management review minute; the breach tabletop record; the sponsor's audit-interview preparation notes.
Output. The leadership evidence file, a controlled, dated, version-managed bundle that the auditor reviews alongside the sponsor interview. The bundle is organised into eight sections (one per leadership move). Each artefact is dated, signed where applicable, and cross-referenced to the relevant clause.
Owner. DPO maintains the file; sponsor reviews annually; Internal Audit tests pre-certification.
Indicative effort. One-time setup of 1 to 2 person-weeks; ongoing 1 to 2 person-days per month to keep current.
Common failure modes. (a) Artefacts scattered across SharePoint folders with no index, fails the traceability test. (b) Minutes undated or unsigned, fails the Documented Information test. (c) Board / RMC packs missing, fails the board-oversight test. (d) Integration-gate log absent, fails the integration evidence test. (e) Tabletop record absent, fails the incident-escalation evidence test. (f) Sponsor interview not rehearsed, fails the sponsor-fluency test.
Move 7, Wire leadership into the management review and the audit programme
Input. The leadership evidence file; the management review agenda (Clause 9.3); the internal audit programme (Clause 9.2); the audit-finding log.
Output. Three integration points.
-
The management review (Clause 9.3). Top management chairs. The agenda includes the status of previous actions, changes in context, PIMS performance, audit results, compliance, objective achievement, incident performance, corrective actions, performance of other parties, resource adequacy, effectiveness of risk treatment, opportunities for improvement. The minute records decisions; the board / RMC receives the outcome.
-
The internal audit programme (Clause 9.2). Top management ensures the audit programme is independent (audit reports to the Audit Committee or the board), resourced, and covers all PIMS clauses and Annex A controls. Audit findings are tracked to closure; material findings are escalated to the sponsor.
-
The audit-finding escalation route. Material findings (majors; recurring minors; findings on Clauses 5.1, 5.2, 5.3; findings on Annex A.1.2.x or A.2.2.x controls) are escalated to the sponsor within a defined SLA (typically 5 to 10 working days). The sponsor directs the corrective action; the DPO runs it; the Steering Committee reviews closure.
Owner. Top management chairs the management review; Internal Audit runs the programme; DPO tracks findings to closure.
Indicative effort. Annual cycle, 1 to 2 person-weeks of DPO preparation for the management review; 2 to 4 person-weeks of Internal Audit per cycle.
Common failure modes. (a) Sponsor absent from the management review, fails the 5.1 chair test. (b) Management review agenda generic (the standard's recommended agenda items not addressed), fails the 9.3 test. (c) Audit programme not independent, fails the 9.2 independence test. (d) Findings not tracked to closure, fails the 10.2 test. (e) Material findings not escalated to the sponsor, fails the leadership-direction test.
Move 8, Demonstrate leadership during events and incidents
Input. The breach-response playbook (Clause 8 and Annex A.3 incident controls); the incident-escalation chain; the regulator-engagement protocol; the dual-clock commitment; the tabletop exercise schedule.
Output. The leadership dimension of the incident capability.
-
The incident-escalation chain. A documented chain that activates the sponsor on detection of a personal-data breach, with a 30-minute SLA for sponsor notification. The chain names the incident commander (typically the DPO), the deputy (typically the CISO), the communications lead, the legal lead, and the sponsor's role in decision-making (especially the breach-notification decisions).
-
The dual-clock rehearsal. A semi-annual breach tabletop exercise (KPI in Section 12) that rehearses the dual-clock commitment, CERT-In 6 hours, DPDP 72 hours, plus sectoral clocks as applicable. The sponsor participates; the tabletop record is part of the leadership evidence file.
-
The regulator-engagement protocol. A documented protocol for engaging the Data Protection Board of India, CERT-In, the sector regulator (RBI / SEBI / IRDAI), and overseas regulators (GDPR supervisory authorities). The protocol names the spokesperson, the legal support, the sponsor's role in regulatory interviews.
-
The SDF-designation response. For likely-SDF entities, a documented plan for responding to a section 10 designation, the DPO appointment (or re-confirmation), the board accountability mechanism, the DPIP cadence, the independent-audit cadence, the algorithmic-fairness review.
-
The M&A trigger response. A documented plan for activating privacy diligence on a material acquisition, divestiture or partnership, the Move 3 M&A gate.
Owner. Sponsor owns the activation; DPO runs the response; Communications and Legal support.
Indicative effort. One-time setup of 2 to 4 person-weeks for the chain, the protocol, the response plans; semi-annual tabletop of 0.5 to 1 person-week each.
Common failure modes. (a) Escalation chain exists on paper but the sponsor is not reachable in the tabletop, fails the dual-clock commitment test. (b) Tabletop never run, fails the incident-escalation evidence test. (c) Regulator-engagement protocol absent, fails the interested-party engagement test. (d) Sponsor defers notification decisions to the DPO, fails the top-management accountability test. (e) SDF designation arrives without a plan, fails the section 10 readiness test.
The eight moves in aggregate
The eight moves together convert a "delegated-and-forgotten" PIMS into a "leadership-owned" PIMS. The first cycle (Moves 1 to 8) takes 8 to 16 weeks for a typical Indian growing company; the steady-state cycle (Moves 4 to 8 in recurrence plus Moves 1 to 3 on event trigger) is a continuous management discipline that produces the leadership evidence base the certification auditor, the Data Protection Board, the board / RMC and overseas regulators all want to see. The Singahi toolkit for Clause 5.1 contains 17 ready-to-customise documents that operationalise each move.
Tools, Technologies, and Solutions
Clause 5.1 is a leadership-and-governance clause rather than a technical-control clause. Tooling falls into five categories that support the leadership discipline. The tooling discussion below uses category-level descriptors only; no vendor is named or endorsed. All third-party pricing is indicative and must be verified against candidate providers' official domains at the time of selection.
Governance, Risk and Compliance (GRC) platforms with PIMS modules
For organisations running integrated management systems (27001 + 27701 + 22301 + 42001), an integrated GRC platform with a PIMS module hosts the leadership evidence base alongside the ISMS, BCMS and AIMS evidence. Required capabilities: a steering-committee meeting and minutes module; a board-pack builder; a budget and resourcing tracker; an integration-gate log; an objective cascade; a KPI dashboard; a corrective-action tracker with escalation to sponsor; a policy and Documented Information register; an audit-programme module; an incident-escalation chain with the dual-clock countdown; a regulator-engagement log; a tabletop exercise module. The Indian market is served by global GRC vendors with substantial Indian delivery footprints, by global SaaS GRC vendors selling through partner networks, and by India-HQ GRC vendors.
Implementation is typically 16 to 40 weeks depending on scope and integration complexity.
The selection question for a Clause 5.1 buyer is whether the platform supports: the leadership evidence file structure (organised by the eight leadership moves); the sponsor commitment statement template and the workflow that signs and versions it; the steering-committee cadence and minutes; the board-pack builder with the version control and the Companies Act section 134(3)(n) alignment; the integration-gate log wired into the existing product, vendor, M&A, marketing, SDLC, HR, data-sharing and cross-border workflows; the KPI dashboard (Section 12) with the sponsor-grade one-page view; the incident-escalation chain with the dual-clock countdown and the sponsor-notification SLA; the tabletop exercise module with the dual-clock rehearsal; the audit-programme module with the Clause 5.1 sponsor-interview rehearsal script.
Privacy management platforms / enterprise privacy software
For Mid-market and enterprise, dedicated enterprise privacy platforms combine ROPA management, DPIA workflows, data-principal-rights request handling, consent vaulting, processor and sub-processor management, cross-border transfer tracking, breach incident response, awareness delivery, and policy and notice workflow. The leadership dimension of these platforms is the dashboard and reporting capability that produces the board-grade pack.
Pricing is per-fulfiller-user (DPO, privacy analysts, legal, processor-relationship managers); data-principal-facing surfaces are typically priced by record volume or by active-principal count.
Meeting and board-portal software
For the steering-committee cadence and the board-pack delivery, board-portal software and meeting-management software support the documented-decision evidence base. Required capabilities: agenda and minutes templates; signature workflow; version control; secure distribution to board members; attendance and acknowledgement tracking; archive and retrieval; secure tablet / smartphone access for board members.
Awareness and training platforms
For the Move 5 communication programme, awareness and training platforms with leadership-message modules are the standard Indian stack. Required capabilities: assign the sponsor town-hall to all staff with attendance tracking; assign the policy acknowledgement; deliver the process-owner briefing; deliver the new-joiner induction; deliver the annual refresh with comprehension check; deliver the leadership-team fluency briefing; generate the audit reports.
Incident-response and tabletop tooling
For the Move 8 incident-escalation chain and the dual-clock rehearsal, incident-response tooling supports the chain activation, the countdown timers, the regulator-notification templates, the principal-notification templates, and the tabletop exercise delivery. The dual-clock rehearsal is the marquee tabletop scenario.
Indicative cost bands for the Clause 5.1 leadership stack
| Size segment | Stack |
|---|---|
| Growing company (50 to 250) | Existing Microsoft 365 / Google Workspace (SharePoint / Drive for the evidence file; Teams for the steering committee; Forms for the acknowledgement) + email-based escalation + IR retainer (optional) + ad-hoc tabletop |
| Mid-market (250 to 2,000) | DMS + dedicated GRC-with-PIMS module or privacy platform + board-portal for the board pack + awareness platform + IR retainer + semi-annual tabletop |
| Enterprise (2,000-plus) or SDF | DMS + full GRC platform with PIMS module + privacy management platform + board-portal + awareness platform + IR retainer + dedicated privacy content team + quarterly tabletop |
These bands are indicative. Actual costs depend on existing stack, integration complexity, number of board members, number of fulfilment users, principal-record volume, and vendor selection. The Singahi advisory team can assist with vendor-neutral selection tailored to the organisation's stack and scale.
Policy and Procedure Templates
This section previews the apex Clause 5.1 templates. The full ready-to-customise templates are in the Clause 5.1 toolkit (17 documents).
Executive sponsor commitment statement (preview, full template in toolkit doc 01)
[EXECUTIVE SPONSOR COMMITMENT STATEMENT — PIMS]
[Organisation Name]
Version: [X.Y] | Issue Date: [DD Month YYYY] | Next Review: [DD Month YYYY]
Sponsor: [Name, Role, Signature]
DPO / Privacy Lead: [Name, Co-signature]
Classification: Internal / Confidential

1. Accountability
   I, [Name], in my role as [Role], am accountable to top management and
   the Board for the effectiveness of the Privacy Information Management
   System (PIMS) established under ISO/IEC 27701:2025.

2. The four commitment statements
   2.1 I will ensure the privacy policy (Clause 5.2) and privacy objectives
       (Clause 6.2) are established and compatible with the strategic
       direction of [Organisation].
   2.2 I will ensure the PIMS requirements are integrated into the
       organisation's business processes (Move 3 integration gates).
   2.3 I will ensure the resources the PIMS needs are available (Clause 7.1
       — see Section 4 budget).
   2.4 I will communicate the importance of effective privacy management
       (Move 5 awareness programme).

3. Privacy-specific commitments
   The organisation commits to lawful, fair and transparent processing;
   purpose limitation; data minimisation; accuracy; storage limitation;
   integrity, confidentiality and availability of personal data (DPDP Act
   2023 section 8(5)); accountability (GDPR Article 5(2)); privacy by
   design and by default; lawful cross-border transfer (DPDP section 16
   negative-list; GDPR Chapter V); data principal rights (DPDP sections
   11 to 14); protection of children's data (DPDP section 9); breach
   notification within the dual-clock commitment (DPDP section 8(6) +
   Rule 7, 72 hours to the Board; CERT-In Directions 20(3)/2022-CERT-In,
   6 hours).

4. Resource commitment
   The privacy budget line for FY [YYYY] is INR [X lakh / crore],
   covering the DPO function (headcount [N]), the awareness programme,
   the consent-management infrastructure, the privacy-management platform,
   the DPIA / DPIP process, the breach-response capability, the
   independent data audit (SDF section 10), and the algorithmic-fairness
   review (SDF section 10).

5. Reporting commitment
   5.1 Steering Committee: quarterly, chaired by me.
   5.2 Board / Risk Management Committee: [quarterly / half-yearly] noting
       for [SDF / listed entity / BFSI] entities; annual noting otherwise.
   5.3 Management Review (Clause 9.3): annual, chaired by me.
   5.4 Certification audit participation: I will sit the sponsor interview.

6. Escalation commitment
   I will be reachable on the incident-escalation chain within 30 minutes
   of a personal-data breach detection (Move 8). I will chair or co-chair
   the breach-response decision-making for material breaches. I will
   participate in the semi-annual dual-clock tabletop exercise.

7. Next review
   This statement will be reviewed at the management review (Clause 9.3)
   and on event trigger (sponsor change, SDF designation, breach,
   regulatory change, scope change, audit nonconformity).
PIMS Steering Committee charter (preview, full template in toolkit doc 01)
[PIMS STEERING COMMITTEE CHARTER]
[Organisation Name]
Version: [X.Y] | Issue Date: [DD Month YYYY] | Next Review: [DD Month YYYY]
Approved by: [Sponsor Name, Role, Signature]

1. Purpose
   The PIMS Steering Committee is the cross-functional top-management-
   level forum that oversees the PIMS between board pack cycles.

2. Membership
   Chair: [Sponsor — CEO / MD / Whole-Time Director].
   Secretary: [DPO / Privacy Lead].
   Members: [CISO; Head of Legal; Head of Product; Head of HR; Head of
   Vendor Management; Head of Marketing; Head of Customer Success;
   others as required].

3. Cadence
   Quarterly [or monthly for SDFs / large enterprise], 90 to 120 minutes.

4. Standing agenda
   4.1 Year's privacy risks and treatment status (Clause 6.1.2 / 8.2 / 8.3).
   4.2 Year's privacy objectives and progress (Clause 6.2).
   4.3 Integration-gate decisions (Move 3) — product, vendor, M&A,
       marketing, SDLC, HR, data-sharing, cross-border.
   4.4 Incidents, breaches, tabletop exercises (Clause 8 / Annex A.3;
       Move 8).
   4.5 KPI dashboard (Section 12 of the guide).
   4.6 Audit findings and corrective actions (Clauses 9.2, 10.2).
   4.7 Regulatory interactions (DPBI, CERT-In, RBI, SEBI, IRDAI,
       overseas regulators).
   4.8 Resource adequacy (Clause 7.1).
   4.9 Management review preparation (Clause 9.3).
   4.10 Board / RMC pack preparation.

5. Decision authority
   The Committee decides on: privacy-risk treatment (Clause 8.3);
   privacy-objective approval (Clause 6.2); integration-gate escalations;
   corrective-action direction (Clause 10.2); minor scope changes
   (Clause 4.3); budget re-allocation within the approved envelope.
   The Committee recommends to the Board / RMC: the privacy policy
   (Clause 5.2); major scope changes; the annual budget; SDF-specific
   commitments; the algorithmic-fairness review outcome.

6. Quorum and minutes
   Quorum: the Chair (or delegate) plus the DPO plus three members.
   Minutes: drafted by the DPO within 5 working days; circulated within
   10 working days; signed by the Chair; archived per Documented
   Information controls (Clause 7.5).
Risk Assessment and Treatment
Clause 5.1 is itself a control on leadership conduct; the risks that bear on it are risks to that conduct. The Singahi Clause 5.1 risk register seeds 15 risks. Each risk is scored on a 1-to-5 likelihood and 1-to-5 impact scale (1 = negligible; 5 = severe), with the product giving a 1-to-25 inherent risk score. Treatment options follow the ISO 31000 hierarchy (avoid, reduce, transfer, accept).
| # | Risk | Likelihood | Impact | Inherent | Treatment |
|---|---|---|---|---|---|
| R1 | Sponsor named on paper only; no actual leadership conduct | 4 | 5 | 20 | Move 1 + Move 2 (signed sponsor commitment statement; calendar holds; budget line) |
| R2 | Sponsor cannot answer the audit-interview questions fluently | 4 | 5 | 20 | Move 6 (sponsor interview rehearsal); annual top-management briefing |
| R3 | Steering Committee exists on paper but never meets | 3 | 5 | 15 | Move 1 charter with cadence; Move 6 minutes as evidence |
| R4 | Integration gates absent or rubber-stamped | 4 | 4 | 16 | Move 3 documented gates with DPO sign-off; escalation to Steering Committee |
| R5 | Privacy budget inadequate for the PIMS scope | 3 | 5 | 15 | Move 4 budget line; annual review at the management review |
| R6 | Dual-clock breach commitment not operationalised (DPDP 72h + CERT-In 6h) | 3 | 5 | 15 | Move 8 incident-escalation chain; semi-annual tabletop |
| R7 | DPO reports to Legal/Compliance without top-management line | 4 | 4 | 16 | Move 1 reporting line documented; for SDFs, section 10 DPO-accountability-to-board |
| R8 | Board / RMC pack absent (SDFs and listed entities) | 3 | 5 | 15 | Move 1 board channel; Move 7 management review; Companies Act 134(3)(n) statement |
| R9 | Management review not chaired by the sponsor | 3 | 5 | 15 | Move 7 sponsor chairs; agenda per Clause 9.3 |
| R10 | Awareness programme absent; staff cannot identify the sponsor | 4 | 3 | 12 | Move 5 town-hall; new-joiner induction; acknowledgement record |
| R11 | Tabletop never run or sponsor absent | 4 | 4 | 16 | Move 8 semi-annual tabletop; KPI A2 |
| R12 | Privacy objectives set but not cascaded to performance management | 3 | 3 | 9 | Move 4 cascade; HR performance management integration |
| R13 | SDF section 10 designation arrives without a readiness plan | 2 | 5 | 10 | Move 8 SDF-designation response; DPIP register; DPO appointment in place |
| R14 | Sponsor turnover without transition | 2 | 5 | 10 | Move 2 sponsor statement refreshed on event trigger; Move 6 version control |
| R15 | Leadership evidence file scattered; auditor cannot trace | 4 | 4 | 16 | Move 6 organised file; Internal Audit pre-certification test |
The risks above are the seed register. The full risk-assessment template (toolkit doc 09) includes sector-specific risks (BFSI: RBI board-approval failure risk; Healthcare: AI diagnostic-assist algorithmic-fairness failure risk; SaaS: customer DPA framework failure risk; Edtech: section 9 children's-data capability failure risk).
Audit and Compliance Checklist
The Clause 5.1 audit checklist below contains 28 questions across the eight leadership moves. Each question lists the evidence the auditor will request and a red flag indicating the failure mode. The full checklist (with the sponsor interview script, the sampled-staff script, and the integration-gate trace worksheet) is in toolkit doc 04.
Stage 1, Document and leadership-evidence review
| # | Question | Expected evidence | Red flag |
|---|---|---|---|
| 1 | Is the executive sponsor named, at top-management level, with a signed sponsor commitment statement? | Signed statement on letterhead, dated, version-controlled | Statement missing; signed by DPO not sponsor; undated |
| 2 | Does the sponsor commitment statement name the four commitments and the privacy-specific commitments? | Statement sections 2 and 3 | Generic "comply with laws" wording; commitments missing |
| 3 | Does the sponsor commitment statement name the dual-clock breach commitment (DPDP 72h + CERT-In 6h)? | Statement section 3 | One clock named; no commitment at all |
| 4 | Is the DPO or Privacy Lead named, with a documented reporting line to the sponsor? | Governance structure document; DPO appointment letter | No DPO; DPO reports to Legal without top-management line |
| 5 | For SDFs (DPDP section 10): is the DPO based in India and accountable to the board? | Board minute noting the DPO appointment and accountability | No board noting; DPO not India-based |
| 6 | Is the PIMS Steering Committee chartered, with named members and a quarterly cadence? | Charter document; membership list; meeting calendar | No charter; never meets |
| 7 | Are there four Steering Committee minutes in the last 12 months? | Minutes dated, signed, archived | Fewer than four; undated; missing decisions |
| 8 | For listed entities: is there a board / RMC privacy pack at the regulated cadence? | Board / RMC packs; board minutes referencing the pack | No pack; pack absent from board minutes |
| 9 | Does the leadership evidence file cover all eight leadership moves? | The organised bundle | Scattered artefacts; no index |
| 10 | Is the privacy budget identifiable, with the DPO function, awareness, platform and breach-response lines? | Budget approval; CFO sign-off | Bundled into IT without identification; no DPO line |
Stage 2, Sponsor interview and operating effectiveness
| # | Question | Expected evidence | Red flag |
|---|---|---|---|
| 11 | Can the sponsor describe the four commitment statements? | Sponsor interview | Cannot articulate; "the DPO handles it" |
| 12 | Can the sponsor name the year's top three privacy risks and how they were treated? | Sponsor interview; Clause 8.2 risk register | Cannot name three; no treatment |
| 13 | Can the sponsor describe the dual-clock breach commitment and the last tabletop? | Sponsor interview; tabletop record | Cannot name both clocks; no tabletop; sponsor absent from tabletop |
| 14 | Can the sponsor name the date of the last Steering Committee and the last management review? | Sponsor interview; minutes | Cannot recall; "the DPO schedules those" |
| 15 | Can the sponsor describe the integration gates (product, vendor, M&A, marketing, SDLC)? | Sponsor interview; Move 3 gate log | Cannot describe any gate; gates exist on paper only |
| 16 | Can the sponsor describe the privacy budget and whether it is adequate? | Sponsor interview; budget approval | Cannot name the figure; "Finance handles it" |
| 17 | Can the sponsor describe the board / RMC reporting cadence (for SDFs and listed entities)? | Sponsor interview; board packs | Cannot name the cadence; "Company Secretary handles it" |
| 18 | For SDFs: can the sponsor describe the section 10 DPO accountability and the DPIP cadence? | Sponsor interview; DPIP register | Cannot describe; no DPIP register |
| 19 | Do sampled staff (5 across functions and locations) know who the sponsor is and what they have communicated? | Sampled-staff interview | 3 of 5 cannot answer |
| 20 | Has the management review been chaired by the sponsor in the last 12 months? | Management review minute | Sponsor absent; DPO chairs; no minute |
| 21 | Does the management review address the Clause 9.3 agenda items (context changes, performance, audits, incidents, improvement)? | Management review agenda and minute | Generic agenda; items missing |
| 22 | Are integration gates operational, sampled product launches, vendor onboardings, M&A events with documented privacy checks? | Integration-gate log; sampled decisions | Gates exist on paper but no decisions documented |
| 23 | Is the incident-escalation chain documented with a 30-minute sponsor SLA? | Chain document; tabletop record | No chain; sponsor not reachable in tabletop |
| 24 | Has the semi-annual dual-clock tabletop been run with sponsor participation? | Tabletop record; attendance | No tabletop; sponsor absent; only one clock rehearsed |
| 25 | Are material audit findings escalated to the sponsor within the SLA? | Audit-finding log; escalation record | Findings sit with the DPO; sponsor unaware |
| 26 | Is the privacy objective cascade wired into process-owner performance management? | HR performance management records | Objectives set but not cascaded |
| 27 | For SDFs: is the DPO board-accountable, the DPIP cadence operated, the independent audit done, the algorithmic-fairness review done? | DPO board reports; DPIP register; audit report; algorithmic-fairness report | Any of the four absent |
| 28 | Has the sponsor commitment statement been refreshed on the 27701:2019 to 27701:2025 transition (standalone PIMS, normative Annex B, harmonized structure)? | Statement version history | Still on 2019 framing; no transition plan |
Metrics and KPIs
Figure · Measures
The measures that show Clause 5.1 is working
- Steering Committee meetings held vs planned100%Annual
- Steering Committee decisions closed vs≥90% within t…Per meeting
- Sponsor town-hall held vs planned100%Annual
- Sponsor availability≤30 minutesQuarterly test
- Top-management privacy briefing held100% annualAnnual
The Clause 5.1 KPI set spans process metrics (is the leadership work being done?), outcome metrics (is the leadership work producing the right result?), and assurance metrics (are we confident the leadership will hold up under audit?). The Singahi Clause 5.1 dashboard (toolkit doc 11) operationalises 15 KPIs.
Process KPIs
| # | KPI | Formula | Target | Frequency |
|---|---|---|---|---|
| P1 | Steering Committee meetings held vs planned | Held / planned | 100% (4 of 4 per year) | Annual |
| P2 | Steering Committee decisions closed vs raised | Closed / raised | ≥90% within the next meeting | Per meeting |
| P3 | Sponsor town-hall held vs planned | Held / planned | 100% (1 to 2 per year) | Annual |
| P4 | Sponsor availability on the incident-escalation chain | Minutes to sponsor engagement in tests | ≤30 minutes | Quarterly test |
| P5 | Top-management privacy briefing held | Held / planned | 100% annual | Annual |
| P6 | Integration-gate decisions documented vs invoked | Documented / invoked | 100% | Monthly |
| P7 | Material audit findings escalated to sponsor within SLA | Within SLA / total | 100% | Per finding |
Outcome KPIs
| # | KPI | Formula | Target | Frequency |
|---|---|---|---|---|
| O1 | Staff awareness: % who can name the sponsor | Sampled staff who can name / total sampled | ≥90% | Annual |
| O2 | Privacy objective achievement | Objectives achieved / total set | ≥85% | Annual |
| O3 | Process-owner objective cascade completion | Process owners with privacy objectives / total | 100% | Annual |
| O4 | Privacy budget execution vs approved | Spent / approved | 90 to 110% | Annual |
Assurance KPIs
| # | KPI | Formula | Target | Frequency |
|---|---|---|---|---|
| A1 | Sponsor audit-interview rehearsal score | Rehearsal rubric score | ≥80% pre-audit | Per certification cycle |
| A2 | Dual-clock tabletop: both clocks met | Tabletops meeting both clocks / total | 100% | Semi-annual |
| A3 | Internal audit nonconformities on Clause 5.1 | NCs per cycle | 0 major; ≤1 minor | Per audit cycle |
| A4 | Board / RMC pack delivery on cadence (for SDFs and listed entities) | Packs delivered on time / planned | 100% | Per pack cycle |
The dashboard rolls into the management review (Clause 9.3) pack. The DPO presents the metrics; the sponsor and the board / RMC review trends and approve any corrective actions. Failure patterns to watch: P1 below 100% (Steering Committee cadence slipping); O1 below 70% (sponsor visibility weak); A2 below 100% (dual-clock commitment not met in rehearsal, the marquee audit-failure signal).
Common Pitfalls and Audit Failures
Eight named anti-patterns account for the bulk of Clause 5.1 nonconformities observed in the Indian growing-company segment. Each is named, described, traced to the audit move it fails, and paired with a treatment.
Pitfall 1, The named-only sponsor. Top management named a sponsor at the certification launch event, signed the policy, and disengaged. The sponsor commitment statement is absent. The Steering Committee has not met. The budget is bundled into IT. The sponsor cannot answer the audit-interview questions. Fails Move 1 and Move 2; audit questions 1, 2, 11 to 14. Treatment: stand up the governance structure (Move 1); author and sign the sponsor commitment statement (Move 2); rehearse the sponsor (Move 6).
Pitfall 2, The delegated PIMS. Top management treats privacy as "the DPO's job". The DPO reports to Legal or Compliance without a top-management line. The sponsor is unsure who owns whether the PIMS works. Decisions queue up at the DPO without escalation. Fails Move 1; audit questions 4, 11. Treatment: document the DPO-to-sponsor reporting line; for SDFs, stand up the section 10 DPO-accountability-to-board; cascade leadership direction through the Steering Committee.
Pitfall 3, The parallel-programme PIMS. The PIMS exists as a separate initiative, not integrated into the business. Privacy gates are absent; product launches happen without a privacy review; vendor contracts are signed without a DPA; M&A deals close without privacy diligence. Fails Move 3; audit questions 15, 22. Treatment: design and operate the eight integration gates; document decisions; escalate material gates to the Steering Committee.
Pitfall 4, The compliance-budget PIMS. The privacy budget is the certification fee plus a small DPO line. There is no awareness budget, no platform budget, no breach-response retainer, no Consent Manager integration budget. The budget is inadequate for the PIMS scope. Fails Move 4; audit question 10, 16. Treatment: build the privacy budget line with the eight components (DPO, awareness, platform, DPIA, breach response, audit, algorithmic-fairness review, customer trust portal); CFO sign-off; annual review.
Pitfall 5, The unbriefed sponsor. Top management signed the sponsor commitment statement but did not internalise it. The sponsor cannot name the four commitments, the dual-clock commitment, the year's top risks, the integration gates, or the budget. The audit interview is a failure. Fails Move 6; audit questions 11 to 18. Treatment: run the annual top-management briefing; rehearse the sponsor interview; capture the rehearsal record in the leadership evidence file.
Pitfall 6, The single-clock breach commitment. The sponsor commitment statement names the DPDP 72-hour clock but not the CERT-In 6-hour clock (or vice versa). In a real breach, the organisation misses one of the two. The tabletop reveals the gap, if the tabletop is run. Fails Move 2 and Move 8; audit questions 3, 13, 23, 24. Treatment: name both clocks in the sponsor commitment statement; design the escalation chain with parallel countdowns; semi-annual tabletop (KPI A2).
Pitfall 7, The board-invisible PIMS (SDFs and listed entities). For SDFs under DPDP section 10 and for listed entities under SEBI LODR / Companies Act section 134(3)(n), the privacy leadership discipline is a board-level matter. A PIMS where the board has not reviewed the privacy pack, or where the section 10 DPO has not been formally accounted to the board, is a governance gap. Fails Move 1 and Move 7; audit questions 5, 8, 18, 27. Treatment: stand up the board / RMC channel; produce the board pack at the regulated cadence; for SDFs, formalise the DPO board-accountability minute.
Pitfall 8, The scattered evidence file. The leadership artefacts exist but are scattered across SharePoint, email, individual laptops and shared drives with no index, no version control and no Documented Information discipline. The auditor cannot trace leadership conduct; the sponsor cannot prepare for the interview; after an incident the regulator cannot be served a clean evidence bundle. Fails Move 6; audit question 9. Treatment: stand up the organised leadership evidence file under Clause 7.5 Documented Information controls; Internal Audit tests pre-certification.
Illustrative Scenario 1: Failure, Pragati FinServ NBFC (Illustrative)
Illustrative scenario, a composite example for guidance, not a specific Singahi engagement or a verified outcome.
Disclaimer. Pragati FinServ is a fictional composite of multiple real Indian NBFC, digital-lender and growing financial-services firms observed in the market between 2023 and 2026, drawing on the public researcher and media disclosures around Indian fintech and NBFC cyber events, the SEBI and RBI enforcement pattern, and the DPDP Act 2023 / DPDP Rules 2025 commencement window. It is illustrative; any resemblance to a specific named firm is coincidental. Numbers are illustrative for teaching purposes and do not assert any contested figure as fact.
The organisation
The firm was regulated by the Reserve Bank of India under the RBI Act 1934 and ran a digital-lending vertical (originating loans via a mobile app and through Lending Service Provider arrangements) that accounted for approximately 38 percent of new originations. Pragati was pursuing ISO/IEC 27701:2025 certification (transitioning from the 2019 edition which it had certified in late 2022) and had self-declared as a Data Fiduciary under the DPDP Act 2023. The firm was widely expected to be designated a Significant Data Fiduciary under DPDP section 10 once the SDF thresholds were operationalised.
The leadership failure
Pragati's ISO/IEC 27701:2019 certification, obtained in November 2022, had been driven by a customer-contract requirement (a large private bank's procurement clause). The certification push was run by the Head of Compliance (a Deputy General Manager reporting to the Chief Risk Officer). The CEO had signed the ISMS and PIMS policies at the launch event in October 2022 and had not engaged with the PIMS since. The named executive sponsor on the certification file was the Chief Risk Officer, who had himself not been briefed on the role and was surprised to be named in the Stage 1 audit opening meeting. There was no PIMS Steering Committee; there was no documented privacy budget line; there was no integration of privacy checks into the digital-lending product lifecycle (a new loan product launched in 2024 had no privacy review, no DPIA, and no reassessment of the consent flow); the awareness programme was an annual click-through e-learning module.
The DPO function was nominally held by the Head of Compliance, with no India-based dedicated DPO appointed for the SDF transition. The board's Risk Management Committee had not received a privacy pack in 2024 or 2025; the Companies Act section 134(3)(n) risk-management statement in the FY 2024-25 Board's Report mentioned cyber risk generically but did not mention privacy risk or DPDP. The Move 3 integration gates were absent. The Move 8 incident-escalation chain was a paper document in the Incident Response policy that had not been tested; no breach tabletop had been run.
The external advisory firm that had helped with the 2019 certification had been retained for the 2025 transition surveillance; their gap assessment in October 2025 rated Clause 5.1 at L1 (delegated-and-forgotten) and recommended a leadership-cycle rebuild. The recommendation was not actioned because the Head of Compliance did not escalate it to the CRO or the CEO; the budget envelope did not include a leadership-cycle line; the certification was treated as a Compliance renewal event.
The disruption
On 17 February 2026, the digital-lending vertical's loan-origination platform suffered a misconfiguration in a third-party analytics sub-processor's environment. The sub-processor (a Bengaluru-based analytics vendor engaged in 2024 without a Move 3 vendor-onboarding privacy gate) had exposed an S3 bucket containing approximately 1.8 million borrower records, KYC data (PAN, Aadhaar masked but partially visible in some record formats), loan-application data, bank-account details, employer information, and credit-decision outputs, for approximately 19 days before a security researcher disclosed the exposure to the Indian Computer Emergency Response Team.
The dual clock began running from the moment of Pragati's awareness (the researcher's disclosure reached Pragati via CERT-In on the morning of 18 February 2026):
- CERT-In 6-hour clock. The CERT-In Point of Contact (a junior IT manager) attempted to reach the Head of IT, who was travelling. The prescribed cyber incident report was filed 14 hours after awareness, 8 hours late.
- DPDP 72-hour clock. The Head of Compliance (the nominal DPO) prepared a draft section 8(6) notification to the Board but could not reach the CEO (in a board meeting of a group company) or the CRO (on leave). The notification was filed 78 hours after awareness, 6 hours late. Affected Data Principals were notified over the following 21 days in batches.
The incident-escalation chain failed at the first step: the CEO was not engaged within the 30-minute SLA; the CRO was engaged only on day 2; the board's Risk Management Committee was briefed on day 5 (well after both clocks had been missed).
The regulatory inspection
The Data Protection Board of India opened a proceeding on 26 February 2026 under DPDP section 18 read with section 33. The Board's first request was the leadership evidence file: the sponsor commitment statement, the Steering Committee charter and minutes, the board / RMC packs, the privacy budget, the integration-gate log, the tabletop record, the management review minute. Pragati produced a partial file with significant gaps. The Board's findings, in summary:
- No named executive sponsor with a signed sponsor commitment statement. Material non-conformance with the top-management accountability requirement under the DPDP Act 2023 section 8 read with ISO/IEC 27701:2025 Clause 5.1.
- No PIMS Steering Committee. Material non-conformance with the "directing and supporting persons" limb.
- No integration of privacy into the digital-lending product lifecycle; the 2024 loan product launched without a privacy review. Material non-conformance with the section 8(5) safeguards analysis and with the section 9 children's-data dimension (a small fraction of borrowers were 18 to 21 and the product had no age-gate).
- No documented DPO accountability-to-board; the firm had not prepared for the expected SDF designation. Material non-conformance with section 10 readiness.
- No board / RMC privacy pack in 2024 or 2025; the section 134(3)(n) risk-management statement did not address privacy. Material non-conformance with the Companies Act 2013 section 134(3)(n) and (for the listed parent) SEBI LODR.
- Both clocks missed (CERT-In 6-hour by 8 hours; DPDP 72-hour by 6 hours). Material non-conformance with section 8(6) read with the CERT-In Directions.
- Vendor (the analytics sub-processor) onboarded without a privacy due-diligence gate. Material non-conformance with the processor-management obligations and the section 8(5) safeguards analysis.
RBI opened a parallel supervisory review under the RBI Master Direction on IT Governance (7 November 2023, since replaced by the Cybersecurity Directions 2026) and the RBI Master Direction on Digital Lending (2 September 2022), the borrower-data dimension and the LSP-relationship governance were both material. SEBI opened a disclosure-proceedings review against the listed parent for the section 134(3)(n) gap and the potential price-sensitivity of the incident.
The consequence
The Data Protection Board of India imposed a penalty of approximately 65 crore rupees on Pragati under section 33 read with the Schedule, with the headline finding articulated as failure to take reasonable security safeguards under section 8(5) and failure to notify the breach within the prescribed timeline under section 8(6), with the leadership-conduct failures cited as aggravating factors in the "adequate safeguards" and "adequate notification" analyses. CERT-In imposed a separate monetary penalty under the IT Act for the 8-hour reporting delay. RBI referred the matter to its supervisory ladder, requiring Pragati to commission an external IT audit, remediate the digital-lending privacy gaps, restrict new digital originations for 90 days, and report quarterly to the Senior Supervisory Manager for 12 months. SEBI required the listed parent to make a corrective disclosure.
Pragati's ISO/IEC 27701:2025 transition surveillance audit (reclassified as a special audit) produced a major nonconformity on Clause 5.1 (no sponsor commitment statement; no Steering Committee; no integration gates; no tabletop) plus further majors on Clause 5.2 (policy stale; no DPDP/DPDP Rules refresh, see the companion guide), Clause 5.3 (no DPO with top-management line), Clause 7.1 (no identifiable privacy budget), Clause 9.3 (no sponsor-chaired management review), and Annex A.2.2.x (processor controls, the analytics sub-processor without a DPA). The certificate was suspended.
The commercial cost was larger. Pragati's digital-lending origination volume dropped 42 percent over the following two quarters (the RBI restriction plus customer-acquisition drag). The Pragati share price (listed parent) dropped 11 percent over the two weeks following the incident. A class-action proceeding was filed under the Consumer Protection Act 2019.
The lessons
- A signed policy is not leadership conduct. The CEO's 2022 launch-event signature was the start of the leadership commitment; the absence of any subsequent conduct was the failure. The eight leadership moves are not optional.
- The sponsor must be the sponsor. Naming a CRO who had not been briefed was worse than naming no sponsor, it produced a false assurance. Move 1 requires the named sponsor to be engaged and briefed.
- The dual-clock commitment is the marquee test. Missing both clocks by hours was a direct consequence of the absent Move 8 escalation chain. A semi-annual tabletop would have caught the gap.
- Integration gates protect the section 8(5) safeguards analysis. The 2024 loan product launched without a privacy review; the 2024 analytics vendor onboarded without a privacy due diligence. Both failures flowed from the absent Move 3 integration discipline.
- The SDF-readiness window is now. Pragati's failure to stand up the section 10 DPO-accountability-to-board ahead of the expected SDF designation compounded every other finding.
- The cost of a 5.1 failure dwarfs the cost of 5.1 conformance. Pragati's 65-crore-rupee DPDP penalty plus the CERT-In penalty plus the RBI supervisory action plus the customer churn plus the share-price drop plus the class action, versus a 4 to 8 lakh rupee external advisory cost for a proper Clause 5.1 leadership-cycle rebuild. The asymmetry is several orders of magnitude.
Illustrative Scenario 2: Success, Anaya SaaS (Illustrative, with ROI)
Disclaimer. Anaya SaaS is a fictional composite of multiple real Indian B2B SaaS and ITeS firms that have invested in privacy leadership and obtained ISO/IEC 27701:2025 certification. It is illustrative; any resemblance to a specific named firm is coincidental. Numbers are illustrative for teaching purposes.
The organisation
Anaya's platform handled customer HR data, payroll data, performance data and (for some customers) biometric attendance data, making Anaya a PII processor for most of its customers' data and a PII controller for its own employee, candidate and customer-relationship data. Anaya was pursuing ISO/IEC 27701:2025 certification as a commercial differentiator in enterprise sales cycles (where ISO 27701 was increasingly a procurement qualifier) and as the management-system lens for its DPDP, GDPR and PDPA Singapore obligations.
The challenge
In April 2026, Anaya's CEO (the executive sponsor for the certification programme) commissioned a Clause 5.1 leadership-cycle build ahead of the certification Stage 1 audit planned for September 2026. The existing leadership posture was L2 on most dimensions: the CEO had signed the ISMS policy in 2023 (Anaya was already ISO/IEC 27001:2022 certified), the CISO doubled as the Privacy Lead, there was a quarterly information-security steering group, but there was no dedicated privacy steering committee, no documented sponsor commitment statement for privacy, no integration of privacy gates into the product or vendor lifecycle, no dual-clock breach tabletop, no board-level privacy pack (Anaya's parent was listed), and no Consent Manager integration planning. An internal gap assessment (using the toolkit doc 12 template) rated Clause 5.1 at L2.
The phased remediation
The CEO sponsored a 12-week leadership-cycle build, supported by external advisory.
Weeks 1 to 2: Move 1 (stand up the governance structure). The CEO appointed the existing CISO as the dedicated DPO (with a CIPM credential sponsored by the firm) and named a Whole-Time Director of the parent as the section 10 DPO-board-accountable executive in anticipation of an SDF-equivalent designation. The PIMS Steering Committee was chartered with the CEO as chair, the DPO as secretary, the CTO, the Head of Legal, the Head of Product, the Head of HR, the Head of Customer Success and the Head of Vendor Management as members, with a quarterly cadence and the standing agenda from Section 7 Move 1. A Move 1 sub-forum structure was stood up: a privacy-by-design working group (Product, Engineering, DPO); a vendor-privacy working group (Procurement, Legal, DPO); an incident-response committee (CEO, DPO, CTO, Head of Legal, Head of Communications).
Weeks 3 to 4: Move 2 (sponsor commitment statement). A two-hour workshop with the CEO, the DPO, the CTO and the Head of Legal produced the one-page sponsor commitment statement on Anaya letterhead, signed by the CEO, dated, with the next review date set to the management review in March 2027. The statement named the four commitment statements, the privacy-specific commitments (including the dual-clock breach commitment for Anaya's India, EU and Singapore operations, DPDP 72 hours, GDPR 72 hours, PDPA 72 hours, CERT-In 6 hours), the privacy budget line for FY 2026-27 (180 lakh rupees covering the DPO function, the awareness programme, the consent-management platform, the privacy-management module, the breach-response retainer, the independent data audit, and the customer trust portal), the reporting cadence (Steering Committee quarterly; board / RMC half-yearly; management review annually), and the escalation commitment (CEO reachable on the chain within 30 minutes).
Weeks 5 to 7: Move 3 (integrate privacy into business processes). Anaya wired privacy gates into eight points in the business. The product-launch gate was added to the existing product-management lifecycle (a privacy review at the design stage and at the deployment stage, with documented sign-off). The vendor-onboarding gate was added to the procurement workflow (a privacy due-diligence questionnaire, a DPA template, a sub-processor disclosure, signed off by Procurement and the DPO). The M&A diligence gate was added to the corporate-development playbook. The marketing-campaign approval gate was added to the marketing-automation workflow. The software-development gate was added to the engineering Definition of Done. The HR onboarding gate was added to the new-joiner workflow. The data-sharing agreement approval gate and the cross-border transfer approval gate were added to the legal workflow. The first month of operation produced 14 documented gate decisions, three of which escalated to the Steering Committee.
Weeks 8 to 9: Move 4 (objective cascade and resourcing). The CEO and the DPO set six SMART privacy objectives for FY 2026-27 (consent-record completeness 99 percent; DSAR turnaround 21 days; breach-detection-to-tabletop-notification 4 hours; DPIA coverage 100 percent of new high-risk processing; training completion 95 percent; sub-processor change-notification SLA 98 percent). The objectives were cascaded into the performance management of the relevant process owners (Product, Customer Success, Engineering, Procurement). The DPO's CIPM credential and three privacy-engineering certifications for the engineering leads were funded.
Weeks 10 to 11: Move 5 (awareness programme). The CEO hosted the inaugural privacy town-hall (-recorded; available to field sites); 96 percent of staff attended live. The new-joiner induction was updated to include the privacy policy-on-a-page, the reporting channels and the breach-reporting duty. The annual awareness refresh was scheduled. The process-owner briefing was run for the 38 process owners across Product, Engineering, Customer Success, Procurement and HR. The top-management briefing was run for the CEO, the CTO, the CFO, the Whole-Time Director and the board / RMC members.
Week 12: Move 6 (leadership evidence file), Move 7 (management review) and Move 8 (tabletop). The leadership evidence file was organised under the eight-moves structure with Documented Information controls (Clause 7.5). The first management review under the new structure was chaired by the CEO, with the DPO as secretary; the agenda addressed all Clause 9.3 items; the minute recorded the decisions and the corrective actions. The first dual-clock tabletop was run with the CEO, the DPO, the CTO, the Head of Legal, the Head of Communications and the IR retainer, both clocks met (CERT-In 5 hours 20 minutes; DPDP 68 hours; PDPA 64 hours; GDPR 60 hours). The board / RMC pack was produced and delivered at the next sitting.
The quantified results
-
ISO/IEC 27701:2025 Stage 1 audit (September 2026). Zero major nonconformities on Clause 5.1; one minor nonconformity (a Documented Information metadata gap in the integration-gate log, fixed in 48 hours). The certifying body's auditor noted the leadership-cycle build as a benchmark example for the Indian B2B SaaS segment.
-
ISO/IEC 27701:2025 Stage 2 audit (November 2026). Zero nonconformities on Clause 5.1. Certification recommended.
-
Internal culture. The annual staff engagement survey showed a 22-point improvement in the "I understand how we protect customer data" item and a 16-point improvement in the "Leadership communicates the importance of privacy" item, attributable (per the survey commentary) to the town-hall, the awareness programme and the visible integration gates.
-
Board engagement. The board / RMC, which had previously not engaged with privacy, became an active forum, asking informed questions, directing reviews of the AI roadmap's privacy implications, and commissioning an independent privacy assessment ahead of a planned acquisition.
-
Regulator engagement. When a sub-processor experienced a minor incident (no customer data affected, but a notifiable event under the sub-processor's DPA), Anaya's incident-escalation chain activated within the 30-minute sponsor SLA, both clocks were evaluated within 4 hours, the decision was made (notify the affected controllers; not a DPDP section 8(6) reportable event), and the documentation was clean. The event demonstrated the leadership capability in operation.
The ROI
The Year-1 ROI on a purely financial basis (insurance saving alone) is under 1x, modest. The ROI on insurance plus the sales-cycle saving is 14x. The expected-value ROI (including revenue wins and avoided penalty exposure) is several orders of magnitude higher. The revenue wins are the upside of treating privacy leadership as a commercial differentiator, Anaya's customer trust portal publication is now referenced in its enterprise sales proposals as a primary trust artefact.
The lessons
- Privacy leadership is commercially valuable for B2B SaaS. It is not just a compliance artefact; it is a sales asset, an insurance asset, a regulator-relations asset, and a brand asset.
- The eight moves are sequential and deliverable in 12 weeks for a B2B SaaS firm. Most of the work is workshop time, governance design and integration-gate standing-up, not capital expenditure.
- The customer trust portal publication of the leadership evidence is the under-exploited Indian market opportunity. Most Indian growing companies treat the customer trust portal as an afterthought; Anaya treated it as a sales asset and won enterprise business as a result.
- The board briefing converts the board from passive to active. Anaya's board moved from "not engaging with privacy" to "directing reviews of the AI roadmap", a material governance uplift directly attributable to the Move 5 board briefing.
- The integration gates catch real issues. In the first month, three of 14 gate decisions escalated to the Steering Committee, including a vendor that failed the privacy due diligence and was not onboarded, and a marketing campaign that required a consent redesign.
- The ROI frame is the executive sponsor's frame. The CEO commissioned the programme because the financial plus expected-value case was compelling; the compliance frame alone would have produced a slower decision.
- The dual-clock tabletop produces confidence. When the sub-processor incident occurred, the chain activated cleanly, the clocks were evaluated, and the documentation was clean, because the tabletop had rehearsed exactly that scenario.
Multi-Framework Mapping
This section maps ISO/IEC 27701:2025 Clause 5.1 to the relevant controls, articles and sections in the major global and Indian frameworks. The mapping is structured to support a single integrated leadership discipline that satisfies multiple regimes simultaneously, which is the marquee commercial argument for ISO/IEC 27701:2025 in the Indian market.
Mapping table
| Framework | Reference | What it requires (paraphrased) | How the 5.1 leadership discipline satisfies it |
|---|---|---|---|
| ISO/IEC 27701:2025 | Clause 5.1 | Top management visibly leads the PIMS and integrates privacy into business processes | The eight leadership moves are the artefact |
| ISO/IEC 27701:2025 | Annex B (normative) section B.5.1 | Implementation guidance, auditors test against it | The eight-move framework reflects Annex B |
| ISO/IEC 27001:2022 | Clause 5.1 | ISMS leadership | An integrated sponsor or aligned sponsor set satisfies both |
| ISO/IEC 27002:2022 | Control 5.34 | Privacy and protection of PII (the only PII-specific control) | The leadership discipline operationalises 5.34 at the management-system level |
| ISO/IEC 29100:2011 | The accountability principle | The organisation is accountable for PII under its control | The sponsor commitment statement is the accountability artefact |
| ISO/IEC 29134:2017 | DPIA guidelines | Privacy impact assessment methodology | Top-management resourcing enables the DPIP / DPIA capability |
| ISO/IEC 27018:2019 | Code of practice for PII protection in public clouds acting as PII processor | Cloud-processor-specific controls | Top-management processor governance aligns with 27018 |
| GDPR | Article 5(2) | Accountability, controller is responsible for and able to demonstrate compliance | The leadership evidence file is the accountability demonstration |
| GDPR | Article 24 | Controller responsibility, appropriate technical and organisational measures | The eight leadership moves are the organisational measures |
| GDPR | Article 25 | Data protection by design and by default | Top management owns the Move 3 integration gates that operationalise Article 25 |
| GDPR | Article 28(3) | Mandatory DPA clauses | Top management owns the processor-relationship framework |
| GDPR | Article 32 | Security of processing | Top management owns the resourcing of the security controls |
| GDPR | Articles 33-34 | Breach notification (72h to SA; to data subjects without undue delay) | The Move 8 dual-clock commitment |
| GDPR | Articles 35-36 | DPIA and prior consultation | Top management owns the trigger decision |
| GDPR | Articles 37-39 | DPO | Top management owns the appointment; DPO reports to top management |
| GDPR | Article 83 | Fines | The leadership discipline reduces exposure |
| NIST Privacy Framework v1.0 (NIST.CSWP.01162020, 16 Jan 2020) | Govern-P | Governance structure, privacy roles, risk-management strategy, policy | The PIMS governance structure is the Govern-P artefact |
| SOC 2 (AICPA TSC 2017, 2022 PoF update) | CC1.1 to CC1.5 (Control Environment / Tone at the Top) | Board and management commitment to the system | The sponsor commitment statement and Steering Committee are the CC1 artefacts |
| SOC 2 (AICPA TSC 2017, 2022 PoF update) | P8.0 (Monitoring and enforcement) | Monitoring and enforcement of privacy commitments | The KPI dashboard (Section 12) and the integration-gate log are the P8.0 artefacts |
| DPDP Act 2023 (Act 22 of 2023) | Section 8(5) | Reasonable security safeguards | The leadership discipline is informed by Move 3, Move 4 and Move 8 |
| DPDP Act 2023 | Section 8(6) | Breach notification (72h via Rules) | The Move 8 dual-clock commitment |
| DPDP Act 2023 | Section 10 (Significant Data Fiduciary) | DPO based in India accountable to the board; DPIP; independent audit; algorithmic-fairness review | Move 1 DPO-accountability-to-board; the Move 4 resourcing of the DPIP and audit; the Move 3 algorithmic-fairness review gate |
| DPDP Act 2023 | Sections 11-14 | Data principal rights | Top management owns the rights-handling capability resourcing |
| DPDP Act 2023 | Section 33 + Schedule | Penalties (up to ₹250 cr) | The leadership discipline is the marquee "adequate safeguards" defence |
| DPDP Rules 2025 (notified 13 Nov 2025) | Rule 7 | Breach 72-hour clock to the Board | Move 8 dual-clock commitment |
| Companies Act 2013 | Section 134(3)(n) | Risk-management statement in the Board's Report | The board / RMC pack is the input to the section 134(3)(n) statement |
| Companies Act 2013 | Section 177 | Audit Committee | Audit Committee oversight of audit findings; privacy-related provisions and contingencies |
| SEBI LODR | Regulation 21 | Risk Management Committee mandate includes cyber, operational, privacy risk | The board / RMC pack is delivered to the RMC for listed entities |
| RBI Cybersecurity Directions 2026 (31 July 2026) | Board-approved IT policy | Board-approved IT policy for Regulated Entities | The sponsor commitment statement and the board-approved IT policy align |
| RBI Master Direction Digital Lending (2 Sep 2022) | Borrower consent; device-data restriction; privacy policy | Privacy-by-design for digital lending | Move 3 integration gates operationalise Digital Lending for REs lending digitally |
| SEBI CSCRF (20 Aug 2024) | Board-approved cyber-resilience policy; incident reporting 6h | Cyber resilience | The Move 8 dual-clock commitment reflects CSCRF for SEBI REs |
| IRDAI Information and Cyber Security Guidelines 2023 (24 Apr 2023) | Board-approved information and cyber security policy; CISO | Insurance-sector privacy | The leadership discipline reflects IRDAI ICS for insurers |
| CERT-In Directions 20(3)/2022-CERT-In (28 Apr 2022) | 6-hour incident report; Point of Contact | Horizontal incident baseline | The Move 8 dual-clock commitment reflects CERT-In |
| CCPA / CPRA (California) | Cal. Civ. Code 1798.100 et seq. | Business responsibility | The leadership discipline extends to CCPA-covered processing for California residents |
| LGPD (Brazil) | Lei 13.709/2018 | Controller responsibility | The leadership discipline extends to LGPD-covered processing |
| PIPL (China) | PRC PIPL Articles 13, 23, 29, 39 | Separate consent; cross-border; sensitive PI; ADM | The Move 3 integration gates operationalise PIPL for China-data subjects |
| PDPA (Singapore) | PDPA 2012 + 2020 amendment | Breach notification 72h to PDPC | The Move 8 dual-clock extends to the PDPA clock |
The densest overlaps
The densest, cleanest one-to-one mappings for Clause 5.1 are at four points. GDPR Article 24 (controller responsibility) and Article 5(2) (accountability) together are the EU analogue of Clause 5.1; the EU supervisory authorities test "appropriate technical and organisational measures" the same way the ISO 27701 auditor tests the eight leadership moves. NIST Privacy Framework Govern-P is the US-flavoured structural analogue of Clause 5.1; the Govern-P function is where leadership, governance and risk-tolerance strategy live. SOC 2 CC1 (Control Environment / Tone at the Top) is the attestation-equivalent of Clause 5.1; CC1.1 through CC1.5 test board and management commitment to the system. DPDP Act 2023 section 10 (SDF DPO accountability-to-board) is the densest Indian analogue, section 10 effectively makes a Clause 5.1 reporting channel a statutory requirement for SDFs. An Indian organisation implementing the eight leadership moves satisfies substantial portions of all four frameworks simultaneously.
The section 134(3)(n) bridge, Clause 5.1 evidence in the Board's Report
A uniquely Indian angle: the leadership evidence produced under Clause 5.1 is the natural input to the section 134(3)(n) risk-management statement in the Board's Report. The board statement is a statutory disclosure; the leadership evidence is the management-system discipline behind it. Forward-looking Indian firms use the section 134(3)(n) statement to disclose, at a high level, the privacy leadership structure (the named sponsor, the DPO, the board / RMC oversight) and the year's privacy-risk posture, converting the Clause 5.1 evidence into a public-facing governance disclosure. This is an L4-to-L5 maturity signal.
Implementation Roadmap
This is the 30 / 90 / 180 / 365-day roadmap for a typical Indian growing company pursuing Clause 5.1 conformance from a cold start. The full version with milestones, owners and deliverables is in toolkit doc 05.
Days 0 to 30, Foundation
Week 1. Confirm the executive sponsor and the DPO/Privacy Lead at the top-management table. Open the Clause 5.1 workstream. Pull the Clause 4.1, 4.2, 4.3, the privacy risk assessment (6.1.2), and the strategic-narrative inputs.
Weeks 2 to 3 (Move 1). Stand up the privacy governance structure. Charter the PIMS Steering Committee. Schedule the inaugural sitting. For SDFs and listed entities, schedule the board / RMC noting.
Week 4 (Move 2). Author and sign the sponsor commitment statement. Workshop with the sponsor, the DPO, Legal and Product; Legal and Compliance review; sponsor signature; board / RMC noting for SDFs and listed entities.
Days 31 to 90, Integration and resourcing
Weeks 5 to 8 (Move 3). Wire the eight integration gates into the existing business processes. Document the gates; train the process owners; run the first gate decisions.
Weeks 9 to 10 (Move 4). Set the privacy objective cascade. Approve the privacy budget line. Fund the competence plan (DPO credentials, engineer training).
Weeks 11 to 12 (Move 5). Run the inaugural sponsor town-hall. Update the new-joiner induction. Schedule the annual awareness refresh. Run the process-owner briefing. Run the top-management briefing.
Week 13 (Move 6). Organise the leadership evidence file under the eight-moves structure with Documented Information controls (Clause 7.5).
Days 91 to 180, Review, audit and integration
Weeks 14 to 16 (Move 7). Run the first sponsor-chaired management review (Clause 9.3). Stand up the internal-audit Clause 5.1 test. Run the first internal audit; close findings.
Weeks 17 to 20 (Move 8). Design the incident-escalation chain. Run the first dual-clock tabletop. Stand up the regulator-engagement protocol. For likely-SDF entities, document the SDF-designation response plan.
Weeks 21 to 24. Traceability test: confirm the policy (Clause 5.2) is authored and signed; the roles (Clause 5.3) are assigned; the privacy risk assessment (6.1.2) is informed by the integration-gate findings; the awareness programme (7.3) records attendance; the management review (9.3) reflects Clause 5.1; the corrective-action log (10.2) closes against leadership commitments. Remediate any inconsistencies.
Days 181 to 365, Steady state and certification
Months 7 to 9. Run the awareness programme quarterly cycle. Monitor the leadership KPIs (Section 12). Maintain the Documented Information controls. Run the second dual-clock tabletop. Prepare the certification audit pack.
Months 10 to 12. Stage 1 audit. Rehearse the sponsor interview (Move 6 evidence file is the rehearsal script). Close any minor nonconformities. Stage 2 audit. Receive certification (or, for entities already certified on 27701:2019, complete the :2025 transition with the 5.1 finding closed before the 31 October 2028 organisation transition deadline).
Continuous. Quarterly Steering Committee. Annual sponsor town-hall. Annual sponsor-chaired management review. Semi-annual dual-clock tabletop. Board / RMC pack on the regulated cadence (SDFs and listed entities). Refresh the sponsor commitment statement on event trigger (sponsor change, SDF designation, breach, regulatory change, scope change, audit nonconformity).
FAQ
Q1. Our CEO signed the privacy policy at certification launch. Isn't that Clause 5.1 done?
No. A signature at launch is the start, not the substance, of Clause 5.1. The standard asks for visible leadership over time, the eight leadership moves are the substance. The certification auditor will test this in the sponsor interview; the Data Protection Board of India will test it after a breach.
Q2. Can the DPO be the executive sponsor?
No. The DPO is a management role. The sponsor must be at top-management level, the CEO, MD, a Whole-Time Director, or a Top-Management Privacy Champion. The DPO can co-sign the sponsor commitment statement but cannot replace the sponsor. For SDFs, the section 10 DPO is accountable to the board, the DPO reports to and is overseen by top management, not the reverse.
Q3. Does Clause 5.1 require a Privacy Committee?
The standard does not mandate a Privacy Committee. It requires that the integration, the resources and the communication happen, most organisations discharge this through a PIMS Steering Committee, but the structure is the organisation's choice. The test is whether the forum meets, documents decisions, and escalates to top management.
Q4. We are already ISO/IEC 27001:2022 certified. Does our ISMS sponsor cover Clause 5.1?
Yes, if the sponsor leads both systems. An integrated ISMS+PIMS sponsor at top-management level can satisfy both Clause 5.1 commitments. The test is whether the sponsor's commitment explicitly covers the privacy dimension (the privacy-specific commitments, the dual-clock breach commitment, the privacy integration gates) and not just the security dimension.
Q5. How often should the PIMS Steering Committee meet?
Quarterly for most organisations. Monthly for SDFs, large enterprises, or entities in a transformation programme. The test is cadence-with-decisions: a forum that meets but does not document decisions is a 5.1 failure.
Q6. How often should the board / RMC receive a privacy pack?
For SDFs under DPDP section 10 and for listed entities: quarterly or half-yearly, on the regulated cadence. For non-listed growing companies: annual noting at the management review. The board pack is a 4 to 8 page document with a one-page executive summary.
Q7. What is the dual-clock breach commitment and who owns it?
The organisation maintains the capability to intimate the Data Protection Board of India without delay on becoming aware of a personal data breach and file the detailed report within 72 hours (DPDP section 8(6) + Rule 7) and to notify CERT-In within 6 hours of noticing a prescribed cyber incident (CERT-In Directions 20(3)/2022-CERT-In). The two clocks run in parallel from the same awareness event. For BFSI, add the RBI six-hour clock and the SEBI RE 6-hour clock. Top management owns the capability; the DPO runs the response; the sponsor chairs the breach-response decision-making for material breaches.
Q8. What is the privacy budget line and how do we build it?
The privacy budget line covers the DPO function (headcount, training, credentials), the awareness programme, the consent-management infrastructure, the privacy-management platform or GRC-with-PIMS module, the DPIA / DPIP process, the breach-response capability (retainer, tabletops), the independent data audit (for SDFs), the algorithmic-fairness review (for SDFs using AI), the customer trust portal, and the legal advisory. Build it with the DPO and the CFO; review annually at the management review.
Q9. How do we run the integration gates without the DPO becoming a bottleneck?
Three ways. First, scale the DPO function (a dedicated Privacy Lead, a privacy analyst, or an external DPO-as-a-service). Second, wire the gates into existing tooling (the issue-tracker, the IT-service-management platform, the procurement system) so the workflow routes automatically. Third, train process owners to do the first-pass privacy check, with the DPO doing the second-pass review and sign-off, a "privacy champion network" model.
Q10. What if our sponsor leaves?
Sponsor change is an event trigger. Refresh the sponsor commitment statement within 30 days of the new sponsor's appointment; the new sponsor co-signs (version update); the Steering Committee re-endorses; for SDFs, the section 10 DPO-accountability-to-board is re-confirmed at the next board sitting; the leadership evidence file is updated; the certification body is notified if the change occurs during a surveillance cycle.
Q11. Does Clause 5.1 require variable-pay linkage to privacy performance?
No. Pay linkage is a leading-practice signal of L4 to L5 maturity, not a standard requirement. Many L3 organisations meet Clause 5.1 without pay linkage.
Q12. Can we use an external DPO?
Yes, for non-SDF organisations. Under DPDP section 10, an SDF's DPO must be based in India and accountable to the board, an external DPO can satisfy this if the engagement terms meet the accountability requirement. The DPO-as-a-service model is a common choice for growing companies.
Q13. How do we evidence the sponsor's fluency for the audit interview?
Run a two-hour sponsor interview rehearsal using the certification audit script. Cover: the four commitment statements; the dual-clock commitment; the year's top three privacy risks and how they were treated; the integration gates; the privacy budget; the board / RMC cadence; the management review; the last tabletop. Capture the rehearsal record in the leadership evidence file.
Q14. What is the relationship between Clause 5.1 and Clause 9.3 (management review)?
Clause 5.1 produces the leadership conduct; Clause 9.3 reviews it. The sponsor chairs the management review; the DPO prepares; the board / RMC receives the outcome. A management review without the sponsor present is a 5.1 finding; a 5.1 evidence base without a sponsor-chaired management review is a 9.3 finding. The two clauses are paired.
Q15. We are a small growing company (60 staff). Is the eight-moves framework too heavy?
No, it scales. For a 60-staff firm, the Steering Committee is three people (the CEO, the DPO, the Head of Product); the integration gates are lightweight checklists; the tabletop is a 90-minute exercise. The eight moves are the structure; the depth is the organisation's choice. Most of the work is workshop time and governance design, not capital expenditure.
Industry-Specific Requirements
BFSI (banks, NBFCs, insurers, payment systems, MIIs)
BFSI is the most regulator-heavy Indian sector for Clause 5.1. The leadership discipline must reference and integrate with:
- DPDP Act 2023 + DPDP Rules 2025, the horizontal overlay. BFSI entities are typically Data Fiduciaries for customer data and processors for partner-bank or partner-insurer data. Many large BFSI entities are likely SDF designees.
- RBI Cybersecurity, Technology: Risk, Resilience and Assurance Framework Directions, 2026 (31 July 2026), board-approved IT and cyber-security policies; Cyber Crisis Management Plan; incident reporting within six hours; data-locality expectations; ICT outsourcing oversight. The sponsor commitment statement references the Cybersecurity Directions 2026 on the security and availability dimension, and the Move 8 escalation chain names the RBI clock.
- RBI Master Direction on Digital Lending (2 September 2022), India's most prescriptive sectoral privacy-by-design rule. Move 3 integration gates operationalise Digital Lending for REs lending digitally: borrower-consent check; device-data access check; data-minimisation check; storage-and-sharing check at every lending-product launch.
- RBI Tokenisation circular (22 September 2021; full effect 1 October 2022), consent for tokenisation; no raw card data storage.
- RBI Storage of Payment System Data (6 April 2018), end-to-end storage of payment data in India only.
- RBI Managing Risks in Outsourcing Directions, 2025 (28 November 2025), outsourced/cloud-provider privacy and security inheritance.
- SEBI CSCRF (20 August 2024), board-approved cyber-resilience policy; incident reporting within 6 hours to SEBI and CERT-In.
- SEBI KRA Regulations 2011 (as amended 2024), KYC data handling.
- IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023), board-approved Information and Cyber Security Policy including BCP/DR; CISO; 180-day log retention; DR drills; data locality for policyholder data; ICT outsourcing oversight; annual compliance reporting within 90 days of FY end.
The BFSI sponsor commitment statement typically includes an explicit "regulatory reporting clocks" commitment (CERT-In 6 hours; RBI six hours; SEBI RE 6 hours; IRDAI per guidelines; DPDP 72 hours). The board / RMC noting is mandatory. The Move 8 incident-escalation chain rehearses all the clocks semi-annually.
Healthcare (hospitals, pharma, devices, diagnostics, telemedicine)
Healthcare is the sector where the section 9 children's dimension, the consent-to-treat-versus-consent-to-process distinction, and the AI diagnostic-assist algorithmic-fairness overlay all intersect most acutely. The leadership discipline must address:
- DPDP Act 2023 + DPDP Rules 2025, health data is sensitive; section 9 children's dimension applies to pediatric patients (verifiable parental consent; no behavioural monitoring; no targeted advertising).
- The consent-to-treat-versus-consent-to-process distinction. The Move 3 product-launch gate must ensure the consent-flow design distinguishes the two.
- AI diagnostic-assist disclosure. Move 3 integration gate for AI deployment; Move 8 algorithmic-fairness review (DPDP section 10 SDF; GDPR Article 22).
- Cross-border transfer of health data. Telemedicine serving NRI patients; radiology-image sub-processing for AI model training. Move 3 cross-border gate.
- The Digital Information Security in Healthcare Act (DISHA) draft remains in limbo, DPDP is the operative instrument.
- Clinical trial data adds the ICH-GCP / New Drugs and Clinical Trials Rules 2019 layer, trial consent is separate from DPDP consent; the leadership discipline ensures the trial-specific governance.
- The Medical Council of India telemedicine guidelines (2020) govern the doctor-patient relationship in telemedicine; the Move 3 gate reflects the telemedicine-specific disclosures.
For healthcare SDFs (likely designation for large healthtech platforms), the section 10 DPO-accountability-to-board is a board-visible commitment; the DPIP cadence covers every new processing activity; the independent-audit cadence is annual; the algorithmic-fairness review covers the AI diagnostic-assist roadmap.
IT / ITeS and SaaS
IT/ITeS and SaaS firms typically act as PII processors for their customers' data and as PII controllers for their own employee and customer-relationship data. The processor track is critical to the leadership discipline.
- The Move 3 vendor-onboarding gate ensures every customer DPA has the Article 28(3)-style mandatory clauses (subject, duration, nature/purpose, type of data, categories of subjects, obligations) and every sub-processor is disclosed and change-notified.
- The infringing-instruction process (Annex A.2.2.5), what the processor does when a controller instructs processing that infringes DPDP, GDPR or another law. Leadership owns the process and the escalation.
- The cross-border transfer impact assessment for Schrems-II-aware transfers to non-adequate destinations. The Move 3 cross-border gate.
- The customer trust portal publication of the processor-facing artefact set is a leadership-owned sales asset.
- DPDP section 8(5) availability, for SaaS handling personal data, availability is a statutory obligation; the leadership discipline ensures the BCMS leadership (ISO 22301:2019 Clause 5.1) and the PIMS leadership (ISO 27701:2025 Clause 5.1) are integrated.
- The integrated 27001 + 27701 leadership is the marquee opportunity for Indian SaaS firms serving enterprise customers, a single sponsor at top-management level satisfies both, with the customer trust portal publication as the commercial asset.
E-commerce and Retail
- Notice quality and consent for marketing, DPDP section 6 specific consent for marketing communications; Move 3 marketing-campaign approval gate.
- Cookie and SDK consent, granular per-purpose consent; Move 3 marketing gate.
- Behavioural advertising opt-out, and, where AI-based profiling produces legal/significant effects, the disclosure of the logic (DPDP section 10; GDPR Article 22).
- Children's data (DPDP section 9), verification mechanisms for age-restricted products; verifiable parental consent for minors' accounts.
- The marketplace-versus-seller roles, the leadership discipline ensures the role declaration is precise per processing activity; the Move 3 gate tests the role before launch.
- Payment-data handling, RBI Tokenisation; RBI Storage of Payment System Data; the payment-aggregator relationship. Leadership owns the payment-data framework.
- Loyalty-programme data flows, separate consent for loyalty enrolment; cross-programme data sharing.
- The Consumer Protection (E-Commerce) Rules 2020, mandatory privacy policy and grievance redressal mechanism.
Edtech
Edtech is the sector where DPDP section 9 (children) is the marquee challenge. The leadership discipline must address:
- Verifiable parental consent under DPDP section 9 and the DPDP Rules 2025, the Move 3 product-launch gate ensures the verifiable-parental-consent flow is designed before any new Edtech product reaches the market.
- Child-readable notice layer, age-appropriate language, simple icons, audio versions.
- No behavioural monitoring, no targeted advertising, no tracking of children, section 9 hard requirements, not aspirational commitments. The sponsor commitment statement names them; the Move 3 marketing-campaign approval gate enforces them.
- The school-versus-Edtech processor relationship, many Edtech firms act as processors for schools. The role declaration must be precise per processing activity.
- The Protection of Children from Sexual Offences (POCSO) Act 2012, reporting obligations intersect with privacy obligations for child-safety disclosures. The Move 8 incident-escalation chain includes the POCSO reporting route.
For Edtech SDFs (likely designation for large platforms), the section 10 DPO-accountability-to-board covers the children's-data dimension explicitly.
Manufacturing
- Employee data, biometric access control, CCTV, vehicle and asset tracking, health-and-safety data. The Move 3 HR-onboarding gate and the employee-notice discipline (Clause 5.2) cover this.
- Vendor and contractor data, KYC, supplier-portal data, the vendor privacy schedule. The Move 3 vendor-onboarding gate.
- OT/IT convergence, operational-technology data that may identify individuals (operator logs, shift data).
- The Factories Act 1948 and state-level factory rules, health-and-safety data, accident records, the workplace privacy overlay.
- The Rights of Persons with Disabilities Act 2016, accessibility requirements extend to the leadership communication.
- Cross-border transfer for multi-site manufacturing groups, group-company data flows; the Move 3 cross-border gate and the negative-list screen.
Maturity Model
The L1 to L5 maturity model for Clause 5.1. Each level is described by observable characteristics, indicative Indian-segment investment to achieve and sustain the level, and the typical audit outcome.
Level 1, Delegated-and-forgotten
Characteristics. Top management signed the policy at certification launch and disengaged. The sponsor is named on paper but cannot describe the role. No Steering Committee; no documented budget; no integration gates; no tabletop; no board pack (for SDFs and listed entities). The DPO is in Compliance or Legal without a top-management line. The classic decoration.
Audit outcome. Major nonconformity on Clause 5.1 at Stage 1. Direct DPDP penalty exposure on sections 8(5), 8(6), 9 and 10 as applicable, the "adequate safeguards" defence is not available.
Level 2, Authored but not lived
Characteristics. The sponsor commitment statement is signed; the Steering Committee is chartered but meets irregularly; the budget is identifiable but not detailed; some integration gates exist on paper but decisions are not documented; the tabletop has not been run; the board pack is occasional. The DPO reports to Legal without a strong top-management line. The sponsor can name the four commitment statements but cannot name the year's top three privacy risks.
Audit outcome. Typically a minor nonconformity at Stage 1; closeable before Stage 2. Some DPDP exposure on the safeguards and notification dimensions.
Level 3, Leadership-owned
Characteristics. The sponsor commitment statement is signed through the correct governance chain (including board / RMC noting for SDFs, BFSI, listed entities); the Steering Committee meets quarterly with documented decisions; the eight integration gates are operational with documented decisions; the privacy budget line is identifiable and adequate; the awareness programme runs; the sponsor town-hall is annual; the first dual-clock tabletop has been run; the management review is sponsor-chaired; the leadership evidence file is organised under Clause 7.5 Documented Information controls; the sponsor can answer the audit-interview questions fluently; for SDFs, the section 10 DPO-accountability-to-board is operational.
Audit outcome. Stage 1 pass; Stage 2 pass with zero or one minor nonconformity on 5.1.
Level 4, Integrated and platform-hosted
Characteristics. All L3 characteristics plus: the leadership discipline is hosted on a GRC platform with PIMS module; the integration gates are wired into the existing product, vendor, M&A, marketing, SDLC, HR, data-sharing and cross-border tooling; the steering-committee cadence produces a quarterly KPI dashboard that drives decisions; the sponsor's audit-interview rehearsal is part of the annual cycle; the board / RMC pack is a benchmark document; the customer trust portal publication of the leadership evidence (redacted) is a sales asset; the sponsor commitment statement is refreshed on event trigger via a documented workflow; the dual-clock tabletop is run semi-annually with sponsor participation and the record is part of the evidence file; for SDFs, the DPIP register, the independent-audit report and the algorithmic-fairness review are board-visible.
Audit outcome. Stage 2 pass with zero nonconformities on 5.1; typically supervisor-grade (the certifying body treats the leadership discipline as a benchmark).
Level 5, Predictive and benchmark
Characteristics. All L4 characteristics plus: the leadership discipline is sectoral benchmark (the firm shares its architecture with industry bodies, regulators, and standards committees); the leadership discipline is predictive (event triggers are monitored via horizon-scanning for regulatory change, DPDP Rules amendments, GDPR developments, new overseas instruments, and via peer-incident learning); the leadership discipline is part of the firm's commercial proposition (the customer trust portal publication is a sales asset; the architecture is referenced in tender proposals); the firm's architecture is referenced by other firms; the algorithmic-fairness review is mature for SDFs; the firm participates in DPDP-rule-making consultation through industry bodies; the section 134(3)(n) risk-management statement publicly discloses the privacy leadership structure.
Audit outcome. Continual Stage 2 pass; the leadership discipline is the certifying body's reference architecture for the sector.
Maturity progression
Most Indian growing companies start at L1 and aim for L3 within the first certification cycle. L4 is the typical target for the second surveillance cycle (year 2 to 3 after certification) or for SDFs from the outset. L5 is achieved by a small minority of firms and is a multi-year investment. The Singahi toolkit and advisory are scoped to take a firm from L1 to L3 in 8 to 16 weeks and from L3 to L4 in 6 to 12 months.
Emerging Trends
Seven trends are reshaping Clause 5.1 practice in India and globally over the 2025 to 2028 horizon.
The DPDP Rules 2025 full-enforceability window
The DPDP Rules 2025 were notified on 13 November 2025 with phased commencement. The core data-fiduciary/processor obligations are widely read as reaching full enforceability approximately 18 months from notification, around May 2027 (confirm the exact date in the notified commencement rule). The window between notification and full enforceability is the implementation window. Indian growing companies that use this window to build the Clause 5.1 leadership discipline will be ready; those that wait will face the Data Protection Board's first wave of proceedings. ISO/IEC 27701:2025 Clause 5.1 is the management-system lens through which the DPDP Rules operationalisation is most defensible.
The SDF overlay and the section 10 board-accountability discipline
DPDP section 10 SDF designation is the densest overlap with Clause 5.1. As the Central Government designates the first wave of SDFs (expected through 2026 and 2027 as the SDF threshold rules are operationalised), the section 10 DPO-accountability-to-board, the DPIP cadence, the independent-audit cadence and the algorithmic-fairness review become statutory duties. The Move 1 governance structure, the Move 4 resourcing, and the Move 7 board-pack discipline are the management-system lens through which an SDF satisfies section 10. Forward-looking firms stand up the SDF-readiness programme ahead of designation.
The algorithmic-fairness review as a board-visible artefact
DPDP section 10 makes algorithmic-AI fairness review a statutory obligation for SDFs. Combined with GDPR Article 22 (automated decision-making), the EU AI Act (Regulation (EU) 2024/1689, in force 1 February 2025), and the NIST AI Risk Management Framework (1.0, 26 January 2023), the algorithmic-fairness overlay creates a new category of governance, the algorithmic-fairness review becomes a board-visible artefact. Indian firms designated as SDFs, and any firm using AI for credit, hiring, content moderation, healthcare diagnostic assist, or marketing, should stand up the algorithmic-fairness review under the Move 3 AI-deployment integration gate and report the outcome to the board / RMC. Singahi's AI-governance advisory helps firms anticipate this, in conjunction with ISO/IEC 42001:2023 (AI management system).
The integrated 27001 + 27701 + 42001 leadership discipline
The ISO harmonized structure (HS / Annex SL) makes integrated leadership of ISO/IEC 27001:2022 (ISMS), ISO/IEC 27701:2025 (PIMS), and ISO/IEC 42001:2023 (AIMS) a practical reality. The three Clause 5.1 sponsor commitments can be authored as a coordinated set with shared scope, integrated risk register, joint management review, and integrated audit. Indian firms pursuing multiple certifications, particularly SaaS firms serving enterprise customers, increasingly adopt the integrated approach to reduce total cost of ownership and improve governance coherence. Singahi's integrated-management-systems advisory is built around this convergence.
The board-pack as a public-disclosure asset
The section 134(3)(n) risk-management statement is the natural bridge between the internal leadership discipline and the public-disclosure regime. Forward-looking Indian firms use the section 134(3)(n) statement to disclose, at a high level, the privacy leadership structure (the named sponsor, the DPO, the board / RMC oversight) and the year's privacy-risk posture, converting the Clause 5.1 evidence into a public-facing governance disclosure. This is an L4-to-L5 maturity signal that is increasingly rewarded by investors and proxy advisors.
The customer trust portal as a commercial asset
For B2B SaaS, ITeS, BFSI and healthcare firms, the customer trust portal publication of the redacted leadership evidence (the sponsor commitment statement, the governance structure, the integration-gate summary, the board-pack summary, the tabletop record) is increasingly a sales asset. Enterprise security and privacy questionnaires ask for it; procurement teams reward it; the publication shortens the diligence cycle. Forward-looking firms treat the customer trust portal as a leadership-owned commercial asset, not an afterthought.
Privacy leadership as a director-duty discipline
The Companies Act 2013 section 166 (directors' duties) requires directors to act in the best interests of the company, with reasonable care, skill and diligence, and to avoid conflicts of interest. Privacy risk is increasingly recognised as a material risk that engages directors' duties, particularly for SDFs, BFSI, healthcare and listed entities. The Move 1 board / RMC channel, the Move 7 management review, and the Move 8 incident-escalation chain are the management-system lens through which directors discharge their section 166 duties on privacy risk. Forward-looking boards are educating themselves on privacy leadership (the Move 5 board briefing) and treating privacy as a board-level governance discipline, not a management compliance task. This trend is reinforced by the Securities and Exchange Board of India's ongoing emphasis on cyber-resilience and the Reserve Bank of India's supervisory focus on IT governance.
References and Further Reading
This guide draws on primary instruments (Tier 1), the ISO/IEC 27xxx family of standards, Indian regulatory instruments, and established global privacy frameworks. The standards' own clause text is not reproduced; the paraphrases are Singahi's own drafting, attributed per the manifest.
ISO/IEC standards and companions
- ISO/IEC 27701:2025 Information security, cybersecurity and privacy protection, Privacy information management systems, Requirements and guidance (2nd edition, published 14 October 2025; the standard). ISO/IEC JTC 1/SC 27. The Annex B implementation guidance (B.5.1 for Clause 5.1) is normative in 2025.
- ISO/IEC 27701:2019 (1st edition), the predecessor; the official 2019-to-2025 correspondence is in 27701:2025 Annex F.
- ISO/IEC 27001:2022 Information security management systems, Requirements (5th edition; Clause 5.1; control 5.34 in the Annex A reference controls).
- ISO/IEC 27002:2022 Information security controls (6th edition; control 5.34, Privacy and protection of PII, is the only PII-specific control).
- ISO/IEC 29100:2011 Information technology, Security techniques, Privacy framework (the 11 privacy principles, including accountability; a newer edition may exist, verify on iso.org).
- ISO/IEC 29134:2017 Information technology, Security techniques, Guidelines for privacy impact assessment.
- ISO/IEC 27018:2019 Information technology, Security techniques, Code of practice for protection of personally identifiable information (PII) in public clouds acting as PII processors (2nd edition).
- ISO/IEC 27017:2015 Code of practice for information security controls based on ISO/IEC 27002 for cloud services.
- ISO/IEC 29151 Code of practice for personally identifiable information protection.
- ISO/IEC 27706:2025 Requirements for bodies providing audit and certification of privacy information management systems (1st edition; the new PIMS cert-scheme standard; publication date 2025, confirm the exact date on iso.org).
- ISO/IEC 42001:2023 Information technology, Artificial intelligence, Management system (the AIMS Clause 5.1 sibling).
- ISO 22301:2019 Security and resilience, Business continuity management systems (the BCMS Clause 5.1 sibling).
- ISO 9001:2015 Quality management systems (the QMS Clause 5.1 sibling).
- ISO/IEC 20000-1:2018 Information technology, Service management (the SMS Clause 5.1 sibling).
- ISO/IEC 27000 family vocabulary.
- ISO 31000 Risk management.
Indian regulatory instruments
- Digital Personal Data Protection Act 2023 (Act No. 22 of 2023, enacted 11 August 2023; eGazette notification 247847). meity.gov.in.
- Digital Personal Data Protection Rules 2025 (draft 3 January 2025; final notified 13 to 14 November 2025; phased commencement). meity.gov.in.
- Information Technology Act 2000 (Act 21 of 2000; amended 2008), sections 43, 43A, 72A. indiacode.nic.in.
- Information Technology (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules 2011 (notified 11 April 2011). meity.gov.in.
- Indian Computer Emergency Response Team, Directions under section 70B(6) of the IT Act 2000 (No. 20(3)/2022-CERT-In, 28 April 2022). cert-in.org.in.
- Reserve Bank of India, Cybersecurity, Technology: Risk, Resilience and Assurance Framework Directions, 2026 (31 July 2026). rbi.org.in.
- Reserve Bank of India, Master Direction on Digital Lending (DOID.CO.PPG.SEC.09/14.14.001/2022-23, 2 September 2022). rbi.org.in.
- Reserve Bank of India, Tokenisation of card transactions (DPSS.CO.RPPD.No.S-35/07.01.005/2021-22, 22 September 2021; full effect 1 October 2022). rbi.org.in.
- Reserve Bank of India, Storage of Payment System Data (DPSS.CO.OD.No.1098/06.08.005/2017-18, 6 April 2018). rbi.org.in.
- Reserve Bank of India, Managing Risks in Outsourcing Directions, 2025 (28 November 2025). rbi.org.in.
- Securities and Exchange Board of India, Cybersecurity and Cyber Resilience Framework (CSCRF) for SEBI Regulated Entities (SEBI/HO/ITD-1/ITD_CSC_EXT/P/CIR/2024/113, 20 August 2024). sebi.gov.in.
- Securities and Exchange Board of India, KYC Registration Agencies Regulations 2011 (as amended; Master Circular May 2024). sebi.gov.in.
- Insurance Regulatory and Development Authority of India, Information and Cyber Security Guidelines 2023 (24 April 2023). irdai.gov.in.
- Companies Act 2013 (Act 18 of 2013), section 134(3)(n) (risk-management statement), section 166 (directors' duties), section 177 (Audit Committee); SEBI LODR Regulation 21 (Risk Management Committee). mca.gov.in; sebi.gov.in.
- Consumer Protection (E-Commerce) Rules 2020 (notified under the Consumer Protection Act 2019).
- Rights of Persons with Disabilities Act 2016.
- Protection of Children from Sexual Offences (POCSO) Act 2012.
- Medical Council of India telemedicine guidelines (2020).
- New Drugs and Clinical Trials Rules 2019.
Constitutional and jurisprudential foundations
- K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (nine-judge Bench, judgment delivered 24 August 2017), the right to privacy as a fundamental right under Articles 14, 19, 21.
- Justice K.S. Puttaswamy (Retd.) v. Union of India (Aadhaar), (2019) 1 SCC 1 (five-judge Bench, judgment delivered 26 September 2018), upholding Aadhaar in large part; striking down section 57; the proportionality test.
Global frameworks
- Regulation (EU) 2016/679 (General Data Protection Regulation, GDPR). OJ L 119, 4.5.2016, p. 1; applies from 25 May 2018. eur-lex.europa.eu.
- Regulation (EU) 2024/1689 (EU AI Act). eur-lex.europa.eu; in force 1 February 2025.
- Commission Implementing Decision (EU) 2021/914 (modernised Standard Contractual Clauses). eur-lex.europa.eu.
- European Commission, EU-US Data Privacy Framework adequacy decision (10 July 2023).
- Case C-311/18, Data Protection Commissioner v. Facebook Ireland and Maximillian Schrems (Schrems II), CJEU Grand Chamber, judgment 16 July 2020.
- European Data Protection Board, Guidelines 4/2019 on Article 25; Guidelines 05/2020 on consent; Guidelines 9/2022 on personal data breach notification.
- NIST Privacy Framework v1.0, A Tool for Improving Privacy Through Enterprise Risk Management (NIST.CSWP.01162020, 16 January 2020). nist.gov/privacy-framework.
- NIST AI Risk Management Framework 1.0 (26 January 2023). nist.gov.
- AICPA, 2017 Trust Services Criteria for Security, Availability, Processing Integrity, Confidentiality and Privacy (TSC 2017, with 2022 points-of-focus update); the Common Criteria CC1 (Control Environment). aicpa.org.
- California Consumer Privacy Act / California Privacy Rights Act, Cal. Civ. Code 1798.100 et seq.
- Brazil, Lei 13.709/2018 (LGPD).
- Canada, Personal Information Protection and Electronic Documents Act, S.C. 2000, c. 5.
- China, Personal Information Protection Law (PIPL), effective 1 November 2021.
- Singapore, Personal Data Protection Act 2012 (No. 26 of 2012) + 2020 amendment.
- UK GDPR; Data Protection Act 2018 (c. 12).
Citable incident anchors (primary-sourced)
These are referenced in the guide for the lessons they teach. The reader is encouraged to consult the primary sources.
- MobiKwik 2021 event, researcher disclosure of approximately 3.5 million records (with larger contested figures); initially denied by the company; subsequently substantiated by independent verification.
- Juspay 18 January 2021 event, approximately 35 million records; publicly acknowledged by the company.
- BigBasket 2020 event, approximately 20 million records alleged; reported in mainstream media.
- Air India / SITA breach (disclosed February-May 2021), approximately 4.5 million customers affected; reported in Reuters and the company's regulatory notifications.
- AIIMS Delhi ransomware (23 November 2022), healthcare-sector anchor.
- Infosys McCamish Systems LockBit (October 2023), approximately 6 million individuals affected; reported 17.5 million US dollar class-action settlement.
A reading note on contested attribution and unverified claims
In keeping with the accuracy rules in the standards-factory authoring contract: the MobiKwik 2021 event figures are contested (the company disputes the researcher's disclosure); the Pragati FinServ illustrative scenario in Section 14 is illustrative and does not assert any contested figure as fact. Most Indian-firm rupee-loss figures are not publicly disclosed; specific numbers in this guide are attributed to primary sources (regulator orders, SEC filings, peer-reviewed studies, company disclosures) or marked illustrative. The Singahi authoring principle is to mark anything second-hand "reported" or "illustrative" and to present both positions where attribution is contested.