
On this page
- Quick Reference (60 Seconds)
- What the Standard Actually Requires
- Why This Control Matters
- Scope and Applicability
- Key Definitions and Terminology
- Relationship to Other Clauses and Frameworks
- Detailed Implementation Guidance, The Seven Documented-Information Moves
- Tools, Technologies, and Solutions
- Policy and Procedure Templates
- Risk Assessment and Treatment
- Audit and Compliance Checklist
- Metrics and KPIs
- Common Pitfalls and Audit Failures
- Illustrative Scenario 1: Failure, Karuna Insurance Loses the Breach Record (Illustrative)
- Illustrative Scenario 2: Success, Tarini Commerce Builds a ROPA-Anchored Documented-Information Discipline (Illustrative)
- Multi-Framework Mapping
- Implementation Roadmap
- FAQ
- Industry-Specific Requirements
- Maturity Model
- Emerging Trends
- References and Further Reading
Quick Reference (60 Seconds)
| Attribute | Detail |
|---|---|
| Clause | ISO/IEC 27701:2025 Clause 7.5, Documented Information. The closing sub-clause of the PIMS Support block (7.1 Resources, 7.2 Competence, 7.3 Awareness, 7.4 Communication, 7.5 Documented Information), structurally aligned to the Harmonized Structure shared by ISO/IEC 27001:2022 Clause 7.5, ISO 22301:2019 Clause 7.5, ISO 9001:2015 Clause 7.5, ISO/IEC 42001:2023 Clause 7.5. The 2025 edition pushes the documented-information obligation beyond generic ISMS document control into privacy-specific record-keeping: the PIMS documented-information set includes the records that prove the organisation is meeting its privacy obligations to PII principals and to the regulator, not merely the policies and procedures that describe the system. |
| What it asks for (paraphrase) | ISO/IEC 27701:2025 Clause 7.5 asks organizations to create, update, and control PIMS documented information. The organisation's PIMS must include the documented information required by the standard and the documented information the organisation determines as necessary for the effectiveness of the PIMS, a floor (the records ISO/IEC 27701:2025 names across its clauses) plus a ceiling (whatever additional records the organisation needs to demonstrate that the PIMS works). When the organisation creates and updates documented information, it must ensure appropriate identification and format, appropriate review and approval (a defined authority signs off before the document enters service), and appropriate change control. The organisation must control its documented information so that it is available where and when needed, adequately protected (including against privacy-confidentiality-integrity-availability compromise), under version and change control, retained for the period the regulator and the organisation require, and disposed of in a defined and evidenced manner at end-of-life. |
| The marquee insight competitors miss | Three facts make 7.5 the most consequential record-keeping clause in the 2025 edition for a PIMS. First, PIMS documented information is not ISMS documented information with a privacy label, the dominant competitor pattern is to extend the ISO/IEC 27001:2022 Clause 7.5 document-control register with a few privacy entries. That pattern fails the PIMS audit because the privacy-specific record load is substantively different: a ROPA that mirrors the regulator's required fields, consent records that satisfy the DPDP section 6 free-specific-informed-unconditional-unambiguous test and the GDPR Article 7(1) demonstrate-of-consent duty, DPIA records that capture the Article 35(7) content, processor and sub-processor DPA records with the Article 28(3) mandatory clauses, breach records that anchor both the CERT-In 6-hour clock and the DPDP breach clock (intimation without delay; 72-hour report), DSAR and rights-handling logs, transfer records with the section 16 negative-list screen, and the SoA that ties the Annex A.1/A.2/A.3 controls to the risk register. Second, the 7.5-versus-8.x demarcation is the most-misunderstood structural point in the Support block, Clause 7.5 governs how documented information is controlled (the version, the access, the retention, the disposal, the change); the operational records themselves are produced by their owning clauses in Clause 8 and 9 and 7.5 controls them as documented information. Third, the ROPA is the master record of the PIMS, the single document that links processing activities to purposes, lawful bases, retention periods, recipients, transfers, controls and risks. The Data Protection Board of India, the supervisory authority, the certification auditor and the customer assessor will all begin their examination with the ROPA. |
| Domain | Support (Clause 7), Information stack. 7.5 sits after 7.4 (communication) and closes the Support block before Clause 8 (Operation). Where 7.1 to 7.4 build the resources, the competence, the awareness and the communication flows the PIMS needs to operate, 7.5 builds the record-keeping discipline that makes the PIMS demonstrable, every commitment, risk, objective, competence, awareness touch, communication, operational record, audit, review, nonconformity and improvement is controlled Documented Information under 7.5. |
| What you must produce | (a) A Documented Information Policy (the governance artefact) setting out the seven-family inventory, the four control dimensions, the format and identification rules, the review-and-approval matrix, the access control model, the retention schedule, the disposal discipline, the change control workflow; (b) a Document Control Procedure (the methodology artefact) covering the document lifecycle, the identification-and-format standard, the approval matrix, the access control matrix, the version control standard, the change-control workflow, the retention schedule implementation, the disposal log; (c) the PIMS Documented Information Inventory (the master register) listing every document and record in the PIMS scope with its family, owner, version, location, classification, retention period, disposal method, and linkage to the controlling clause; (d) the ROPA (the load-bearing privacy artefact); (e) the Retention Schedule (the privacy-specific overlay mapping each record family to its DPDP, sector-regulator and organisational retention period); (f) the Document Disposal Log; (g) the Version and Approval Matrix; (h) the Access Control Matrix (with the privacy-classification overlay). |
| Typical owner | Top management owns the documented information commitment (Clause 5.1 + 5.2). The DPO / Privacy Lead owns the Inventory, the ROPA, the Retention Schedule, the Policy, and the privacy-side of the Document Control Procedure. The CISO / Security Lead is the integration partner for the integrated-with-distinction posture. The Quality / ISMS representative owns the underlying Document Control Procedure and the document-management platform. Legal and Compliance co-owns the Retention Schedule (legal-retention obligations) and the disposal discipline (legal-hold workflow). Business process owners (engineering, support, marketing, HR) own the operational records produced by their function under Clause 8, they are the authors; the DPO is the controller. Internal Audit tests the Inventory, the retention discipline, the access control and the disposal log at the internal audit (Clause 9.2). |
| Minimum viable actions | (1) Adopt the Documented Information Policy (Clause 5.2 link) and the seven-family inventory; (2) stand up the PIMS Documented Information Inventory from day one (a spreadsheet is acceptable, a GRC module is better); (3) build or extend the Document Control Procedure to cover the four control dimensions; (4) build or commission the ROPA, the master record; (5) build the Retention Schedule with the DPDP, CERT-In, RBI/SEBI/IRDAI and organisational layers; (6) define the approval and access control matrices with the privacy-classification overlay; (7) run the first inventory reconciliation against the operational systems; (8) wire the document-disposal discipline into the records platform; (9) measure (inventory currency, overdue-retention entries, version-currency, ROPA reconciliation rate, breach-record completeness, DSAR-log completeness); (10) wire the 7.5 discipline into the management review (Clause 9.3) and the corrective-action pathway (Clause 10.2). |
| Maturity floor (L1) | A "filing-cabinet" practice: documents scattered across shared drives, individual mailboxes, contractor laptops and shadow-IT repositories; no Inventory; a ROPA that exists as a one-off compliance artefact produced for the last audit; no Retention Schedule; no disposal discipline; version control by filename convention ("_final_v3_USE_THIS"); access control by directory permissions with no privacy overlay. The single most common Clause 7.5 audit nonconformity in the Indian growing-company segment. |
| Maturity target (L4 to L5) | A "demonstrable" discipline: the Inventory reconciles to the operational systems; the four control dimensions are operational and evidenced; the Retention Schedule covers every record family with DPDP, CERT-In and sector-regulator periods; the disposal log is current; the access-control matrix applies the privacy classification; the ROPA is the master record that anchors every audit, every DPIA, every DSAR response, every breach investigation and every regulator engagement. |
| Audit red flag | An Inventory that does not reconcile with the operational systems. The 7.5 audit test is always the same: the auditor picks three to five named records (a processing activity in the ROPA, a vendor contract in the DPA register, a breach incident in the breach log, a rights request in the DSAR log, a consent record for a sampled principal) and traces each one through its full lifecycle, created under an owning clause, controlled under 7.5, retained per the schedule, retrievable on demand, disposed at end-of-life. The second-most-common red flag is the 7.5-versus-8.x collapse, the Inventory tries to be the operational system. The third is the ROPA-as-compliance-artefact pattern, the ROPA exists as a static document produced for the last audit. |
| Quick win | Run a 90-minute documented-information-mapping workshop with the DPO, the CISO (or ISMS representative), the Legal Head, and one representative each from engineering, support, marketing and procurement. Use the Singahi Documented Information Inventory template (toolkit doc 02) on a whiteboard. Walk the seven families with the privacy policy (5.2) and the ROPA draft open. For each family, decide: what records exist, where they live, who owns them, what version they are, what classification they carry, what retention period applies, what disposal method applies. Most Indian growing companies complete the Inventory and stand up the Retention Schedule in 6 to 12 weeks at 3 to 8 lakh rupees of internal effort. |
| Time to implement (first cycle) | Growing companies (50 to 250 staff): 8 to 16 weeks for the first Programme pass (Policy, Procedure, Inventory, ROPA, Retention Schedule, approval and access matrices, disposal log, first reconciliation). Mid-sized (250 to 2,000): 14 to 22 weeks, usually requiring the full seven-family Inventory, the privacy-classification overlay, the GRC-platform integration, the integrated-with-distinction posture, and the sector-regulator retention overlays. Multi-entity enterprise: 5 to 9 months, integrated with enterprise content management, multi-geography localisation (DPDP for India, GDPR for EU/EEA, PIPL for China, CCPA/CPRA for California), the contractor-ecosystem records, and the SDF audit-evidence records. |
| Related clauses | 4.1 (context drives the documented-information landscape); 4.2 (interested-party requirements drive the record-keeping duties); 4.3 (the PIMS scope statement is the foundational artefact); 4.4 (PIMS sustained by the documented-information discipline); 5.1 (top management owns the commitment); 5.2 (privacy policy is the load-bearing strategic artefact); 5.3 (roles, the approval and access matrix maps to the role register); 6.1 (privacy risk register and SoA are core PIMS documented information); 6.2 (objectives are documented information); 6.3 (every PIMS change triggers a document-control event); 7.1 (resources, the document-control platform is a 7.1 line item); 7.2 (competence evidence); 7.3 (awareness evidence); 7.4 (communication records); 7.5 (this clause, the control framework); 8.1 to 8.3 (operational records, the ROPA, the consent records, the DPIA library, the DPA register, the breach log, the DSAR log, the transfer records, produced by Clause 8, controlled by 7.5); 9.1 (monitoring evidence); 9.2 (internal audit results); 9.3 (management review results); 10.2 (nonconformity and corrective-action records); 10.1 (improvement records). Annex A.1.2.x (conditions, ROPA, consent records, DPIA library); A.1.3 (principal obligations, DSAR log, grievance log); A.1.5.x (transfer, disclosure records); A.2.2.x (processor, DPA records, infringing-instruction records); A.3.21 (secure disposal); A.3.25 (logging); A.3.26 (cryptography, applies to documented information at rest). |
| Critical Indian context-bearing instruments the documented-information discipline must reflect | DPDP Act 2023 (Act 22/2023, enacted 11 August 2023), in particular section 4 grounds (lawful-basis records), section 5 notice, section 6 consent (free, specific, informed, unconditional, unambiguous, withdrawable as easily as given, via the Consent Manager), section 8 (records of compliance with 8(5) safeguards, 8(6) breach records, the breach-clock record (intimation and 72-hour report), 8(7) erasure records, the retention schedule operationalised), section 9 children (verifiable-parental-consent records), section 10 SDF (DPIA records, independent-data-audit records, algorithmic-software review records), sections 11 to 14 (rights records, access, correction/erasure, grievance within the prescribed period, nomination), section 16 cross-border (negative-list-screen records), section 18 DPBI (regulator-correspondence records), section 33 + Schedule (penalty-exposure records); DPDP Rules 2025 (notified 13 November 2025), Rule 7 (the breach-notification record format and the breach clock evidence (intimation without delay; 72-hour report)); the verifiable-parental-consent mechanism; the SDF designation thresholds and the SDF DPIA/audit cadence; the data-retention and erasure timelines including the 48-hour pre-erasure notice; the Consent Manager registration conditions; the grievance-redressal response periods; section 2(1)(g) Consent Manager records (give, manage, review, withdrawal, interoperable, revocable, retained for the prescribed period); Puttaswamy (2017) 10 SCC 1 and the Aadhaar judgment (2019) 1 SCC 1; CERT-In Directions 20(3)/2022-CERT-In of 28 April 2022 (the 6-hour clock record and the 180-day log-retention duty within Indian jurisdiction, the most-overlapped Indian retention obligation on PIMS records); RBI Storage of Payment System Data (6 April 2018); RBI Digital Lending Guidelines (2 September 2022); SEBI CSCRF (20 August 2024); IRDAI Information and Cyber Security Guidelines (24 April 2023); the IT Act 2000 sections 43A and 72A and the SPDI Rules 2011 (the legacy privacy records). The discipline must name these instruments, map each to a record family, and evidence that the record is being created, controlled, retained and disposed of per the obligation. |
If you only read one thing: Clause 7.5 is where the PIMS stops being a collection of well-intentioned policies and becomes a demonstrable discipline. A 7.5-conformant PIMS is one in which every record the regulator, the auditor, the customer-assessor and the principal can ask for, the scope, the policy, the risk register, the SoA, the ROPA, the consent records, the DPIA library, the DPA register, the breach log, the DSAR log, the transfer records, the awareness Evidence Register, the audit results, the management-review minutes, the corrective-action records, exists, is current, is controlled, is retrievable on demand, is retained for the period the regulator requires, and is disposed of in an evidenced manner at end-of-life. Not a shared-drive folder structure nobody trusts; not a one-off compliance artefact produced for the last audit; not a version-control convention honoured in the breach. The certification auditor will sample named records and trace each one through its full lifecycle, and the Data Protection Board of India will, after a complaint or a breach, ask whether the record the organisation needed to start the clock, to honour the right, to report the breach, to demonstrate the consent, to justify the transfer, actually existed, was current and was retrievable. Get 7.5 wrong, a scattered shared-drive practice, a ROPA that exists only as a compliance artefact, no Retention Schedule, no disposal discipline, the 7.5-versus-8.x collapse, the ISMS-reskin failure, and however strong the policies and the procedures are on paper, the PIMS will fail at the moment a single missing or stale record is needed. Get it right, and the privacy programme scales with the records that prove it.
What the Standard Actually Requires
The paraphrased requirement
ISO/IEC 27701:2025 Clause 7.5 asks organizations to create, update, and control PIMS documented information. The clause is short in words and disproportionately wide in surface. Three load-bearing obligations sit inside that paraphrase, and auditors test each separately.
The organisation's PIMS documented information must include the records the standard requires plus the records the organisation itself determines are necessary for effectiveness. The "required by the standard" floor sweeps in every record the harmonized-structure clauses and the Annex A.1/A.2/A.3 controls name, the scope (4.3), the privacy policy (5.2), the role register (5.3), the privacy risk register and the SoA (6.1), the objectives (6.2), the change records (6.3), the competence evidence (7.2), the awareness Evidence Register (7.3), the communication records (7.4), the operational records (Clause 8, the ROPA, the consent records, the DPIA library, the DPA register, the breach log, the DSAR log, the transfer records), the internal audit results (9.2), the management review minutes (9.3), the nonconformity and corrective-action records (10.2), the improvement records (10.1). The "necessary for effectiveness" ceiling is where the organisation exercises judgement. A growing company will typically have 80 to 200 distinct record types in the Inventory; a growing firm 200 to 600; an enterprise 600 to 2,000-plus across jurisdictions.
When the organisation creates and updates documented information, three creation disciplines apply. Appropriate identification and format, every document carries a unique identifier, a version, a date, an owner, a classification, and a format legible to its audience. Appropriate review and approval, a defined authority signs off before the document enters service (the Version-and-Approval Matrix maps document types to approving authorities; the privacy policy to top management; the procedures to the DPO; the ROPA to the DPO with the process owners; the breach log entries to the incident-response lead; the DPIA records to the DPO with the project owner). Appropriate change control, every change is identified, recorded, version-controlled, communicated to the affected audience, and subject to re-approval where material.
The organisation must control its documented information so that seven control attributes hold. The records must be available and fit for use where and when needed. The records must be adequately stored and protected, including against compromise of confidentiality, integrity and availability, with the privacy-classification overlay applied (a ROPA entry identifying a vulnerable principal's health data carries a higher protection bar than a marketing-lead capture). The records must be preserved for the period the regulator and the organisation require (the Retention Schedule operationalises this). The records must be under change control so that the current version is unambiguously identifiable. The records must be retained in a manner that preserves their integrity over the retention period. The records must be disposed of in a defined and evidenced manner at end-of-life (the Disposal Log records the method, crypto-shredding for digital, cross-cut shredding for paper, certificate of destruction for outsourced disposal, and the date and the witnessing authority). And the records must be subject to access control that aligns with the privacy classification.
The seven documented-information families, the load-bearing framework
The most useful conceptual move in Clause 7.5 is recognising that the documented-information landscape divides into seven families with different production disciplines, different retention drivers and different disposal methods. The Singahi seven-family inventory (toolkit doc 02 Section 4) operationalises this and is the load-bearing framework for the rest of the guide.
Family 1, Strategic and governance records. The scope statement (Clause 4.3), the privacy policy (Clause 5.2), the role register and the RACI (Clause 5.3), the privacy objectives and the planning-to-achieve-them (Clause 6.2). Production discipline: top-management or DPO-authored; formally approved; version-controlled; re-approved on every material change; communicated organisation-wide; reviewed at minimum annually. Retention driver: organisational (permanently, superseded versions retained to evidence the historical baseline). Disposal method: archival at end-of-life.
Family 2, Risk and treatment records. The privacy risk register (Clause 6.1), the Statement of Applicability (Clause 6.1), the privacy risk treatment plan, the risk-acceptance records, the change-plan records (Clause 6.3). Production discipline: DPO-authored with process owners; reviewed quarterly and on every material change; re-approved by the risk-acceptance authority. Retention driver: organisational plus regulatory (10 years for the historical risk-treatment record; longer for sector-regulator exposure). Disposal method: archival at end-of-life.
Family 3, Operational privacy records (the PIMS-specific load). The ROPA (Clause 8.1 / 8.2, the master record), the consent records (Annex A.1.2.3/.4), the DPIA library (Clause 8.2 / Annex A.1.2.5), the processor and sub-processor DPA register (Annex A.1.5 / A.2.5), the breach log and the breach investigation files (Clause 8.x and 9.1), the DSAR and rights-handling log (Annex A.1.3), the cross-border transfer records and the transfer-impact assessments (Annex A.1.5.2), the grievance log (DPDP section 13). Production discipline: business-process-owned (engineering, support, marketing, HR, operations produce the records; the DPO controls them); generated continuously through the operational processes; reconciled against the operational systems. Retention driver: DPDP (the section 8(7) erasure obligation runs against this family, the retention period cannot exceed the purpose period); sector-regulator overlays (CERT-In 180-day logs; RBI payment-data; SEBI CSCRF; IRDAI policyholder data); GDPR (Article 30 ROPA kept up to date; Article 5(2) accountability records). Disposal method: secure deletion with the 48-hour pre-erasure notice to the Data Principal where DPDP Rules apply; crypto-shredding for cloud-stored records; certificate of destruction for outsourced disposal.
Family 4, Support evidence. The competence matrix and the qualifications evidence (Clause 7.2), the awareness Evidence Register (Clause 7.3), the communication records and the communication plan (Clause 7.4), the resources and budget records (Clause 7.1). Production discipline: HR / DPO / Communications-owned; generated by the underlying programmes; reconciled against the HR roster and the contractor inventory. Retention driver: organisational plus regulatory (employment-law overlays; certification-body retention expectations). Disposal method: secure deletion at end-of-employment plus the archival copy for the certification retention period.
Family 5, Evaluation evidence. The internal audit programme, the audit reports, the audit-evidence working papers (Clause 9.2), the management review minutes and the input/output records (Clause 9.3), the monitoring and measurement records (Clause 9.1). Production discipline: Internal Audit and top management-owned; produced on the audit and review cadence; retained for the certification-body-required retention period. Retention driver: certification-scheme (typically three certification cycles, nine years, for the audit reports and management-review minutes). Disposal method: archival at end-of-life.
Family 6, Improvement evidence. The nonconformity register, the corrective-action records, the root-cause analyses, the effectiveness reviews (Clause 10.2), the improvement records and the lessons-learned (Clause 10.1). Production discipline: DPO / Quality-owned; produced on event-trigger (nonconformity surfaced) and on improvement-cycle (annual lessons-learned). Retention driver: organisational plus regulatory (three to five years for the corrective-action record; longer if linked to a regulatory finding). Disposal method: archival at end-of-life.
Family 7, Sector and regulatory records (the India overlay). The CERT-In incident reports and the 180-day log retention (CERT-In Directions 28 April 2022), the RBI incident reports (RBI Cybersecurity Directions 2026), the SEBI incident reports (SEBI CSCRF 20 August 2024), the IRDAI incident reports and the policyholder-data records (IRDAI Information and Cyber Security Guidelines 2023), the DPDP section 8(6) breach notifications to the Board, the DPDP section 13 grievance records, the DPDP section 10 SDF audit-evidence records and the algorithmic-software review records, the Consent Manager records (DPDP section 2(1)(g) read with section 6), the cross-border negative-list screening records (DPDP section 16), the regulator-correspondence register (DPBI, RBI, SEBI, IRDAI, CERT-In, MeitY). Production discipline: DPO / Legal / Compliance-owned; produced on regulatory cadence and on event-trigger; retained for the regulator-specified period. Retention driver: sector-regulator-specific (CERT-In 180 days for logs; RBI/SEBI/IRDAI two to ten years for incident records; DPDP Rules-prescribed periods for breach, grievance and SDF records; the Consent Manager registration conditions prescribe the consent-record retention). Disposal method: secure deletion per the regulator-specified end-of-life.
The seven-family inventory is the operational structure the auditor will use to walk through the PIMS. It is not a static document, every Clause 6.3 change to the processing activities, technology, geography, vendor base or regulatory landscape triggers an Inventory refresh.
The ROPA as the master record
The Records of Processing Activities is the master record of the PIMS. It is the single document that links processing activities to purposes, lawful bases, retention periods, recipients, transfers, controls and risks. Almost every other clause in ISO/IEC 27701:2025, and almost every DPDP obligation, hangs off a current and reconciled ROPA.
The ROPA is the Article 30 of GDPR analogue (controller ROPA content in Article 30(1); processor ROPA content in Article 30(2)). In the DPDP ecosystem, the ROPA is the section 8 records-of-compliance artefact the Data Fiduciary must maintain to demonstrate adherence to the section 4 grounds, the section 5 notice, the section 6 consent, the section 8(5) safeguards, the section 8(7) erasure discipline, the section 9 children's regime, the section 10 SDF obligations, the section 16 transfer screen. In ISO/IEC 27701:2025 the ROPA is the operational record that anchors Clause 8.1 (operational planning and control), Clause 8.2 (privacy risk assessment), Clause 8.3 (privacy risk treatment), Annex A.1.2.2 (identify and document purpose), A.1.2.3 (identify lawful basis), A.1.5.x (records of disclosure and transfer), and the SoA at Clause 6.1.
A PIMS-conformant ROPA entry contains, at minimum: the processing activity name and description; the controller role (Data Fiduciary in DPDP terms); the processor(s) involved (including sub-processors); the categories of principals (Data Principals); the categories of personal data; the purpose(s) of processing; the lawful basis (DPDP section 4 / 7; GDPR Article 6); the consent record reference where consent is the basis; the recipients (internal and external); the cross-border transfer destination(s) and the transfer mechanism (DPDP section 16 negative-list screen; GDPR Article 45/46/49); the retention period; the technical and organisational controls applied; the residual risk rating; the link to the DPIA where one was conducted; the link to the SoA entries; the link to the breach log where the activity was involved in an incident; the link to the DSAR log where the activity has been the subject of a rights request.
The ROPA is not a one-off compliance artefact. It is a living record. Every new processing activity triggers a ROPA entry; every change to an existing activity (new purpose, new processor, new geography, new technology) triggers a ROPA update; every DPIA surfaces ROPA updates; every breach surfaces a ROPA review; every Clause 6.3 PIMS change surfaces a ROPA refresh. The ROPA reconciliation against the application landscape (every application processing personal data has a corresponding ROPA entry) is the canonical audit-evidence test. A ROPA that does not reconcile with the application landscape is the single most common Clause 7.5 audit finding in the Indian growing-company segment.
The 7.5-versus-8.x demarcation, the most-misunderstood structural point
The relationship between Clause 7.5 (documented information control) and Clause 8 (operational processes that produce records) is the single most-misunderstood structural point in the Support block. Three patterns dominate the failure modes.
Pattern A, 7.5 collapses into Clause 8. The Inventory tries to be the operational system. Every ROPA entry, every consent record, every breach record, every DSAR log entry is reproduced inside the documented-information inventory as a "controlled document". The Inventory balloons to thousands of entries; the document-control overhead drowns the operational team; the version-control discipline breaks; the access-control overlay becomes impossible to maintain. The auditor cannot tell what is a document-control record and what is an operational record; the certification finding is almost guaranteed.
Pattern B, Clause 8 collapses out of 7.5's control. The Inventory covers the strategic, governance, risk and support-evidence families (Families 1, 2 and 4) but does not extend to the operational records (Family 3) or the sector-regulatory records (Family 7). The ROPA exists as an operational artefact in the privacy team's SharePoint but is not under document control; the consent records live in the consent-management platform with no version, no approval, no retention schedule, no disposal log; the breach log lives in the incident-response platform with no linkage to the 7.5 discipline. The auditor cannot trace the operational record through the 7.5 lifecycle; the certification finding is almost guaranteed.
Pattern C, The integrated-without-distinction failure. The Inventory extends to every operational record but does not differentiate the four control dimensions across record families. The ROPA is treated like the privacy policy (manually versioned, manually approved); the consent records are treated like the strategic documents (annually reviewed); the breach log is treated like the governance policies (top-management approved). The discipline is uniform but inappropriate, every record type needs its own discipline matched to its production pattern.
The Singahi recommended posture is the demarcation-with-linkage pattern. Clause 7.5 governs how documented information is controlled (the version, the access, the retention, the disposal, the change), the four control dimensions apply to every record family. Clause 8 (and the operational clauses) produces the records themselves. The Inventory links to the operational system (the ROPA-as-master-record in the privacy platform; the consent records in the consent platform; the breach log in the incident-response platform) without reproducing the operational entries. The control dimensions are tuned per family: the strategic records are manually versioned, manually approved, annually reviewed; the operational records are system-versioned, process-approved, event-refreshed; the sector-regulatory records follow the regulator-specified cadence.
The four control dimensions, the operational discipline
The four control dimensions are the load-bearing 7.5 operational discipline. The Singahi Document Control Procedure (toolkit doc 02) operationalises each dimension across the seven families.
Dimension 1, Create and update. Every record has a documented creation event (the trigger, the author, the date, the approval) and a documented update discipline (the trigger for refresh, the authority for the change, the version-control rule, the re-approval rule where material). The creation event for a strategic record is a top-management or DPO decision; for a risk record a risk-assessment cycle; for an operational record an operational process event (a new processing activity, a new consent capture, a new breach occurrence); for a support-evidence record a programme event (a training delivery, an audit completion); for an evaluation record a calendar event (the audit cycle, the review cadence); for an improvement record a nonconformity event; for a sector-regulatory record a regulatory trigger.
Dimension 2, Identification and format. Every record carries an identifier (a unique document ID), a version (semantic versioning, major.minor for documents, monotonic versioning for records), a date (effective date for documents; production timestamp for records), an owner (the role responsible for the content), a classification (public, internal, confidential, restricted, privileged), a format (the tool and the file type), and a location (the system of record). The identification standard is uniform across the Inventory; the format varies by family (a policy is a structured document; a log is a structured data table; a notice is a principal-facing artefact; a record is a system-generated artefact).
Dimension 3, Review and approval. Every record has a defined approving authority. The Version and Approval Matrix (toolkit doc 04) maps each record type to the approving role: the privacy policy to top management; the procedures to the DPO; the ROPA to the DPO with the relevant process owners; the DPIA records to the DPO with the project owner; the breach log entries to the incident-response lead with the DPO; the DSAR log entries to the DSAR handler; the consent records to the consent-record owner (the marketing lead for marketing consent; the product lead for product consent; the HR lead for employee consent); the DPA records to the Legal Head with the DPO; the audit reports to the lead auditor; the management-review minutes to top management; the nonconformity records to the DPO; the corrective-action records to the corrective-action owner.
Dimension 4, Distribution, access, storage, retention, disposal and change. Every record has a distribution discipline (who receives the published version), an access control (who can read, who can edit, who can administer), a storage location and protection level (the system of record, the backup discipline, the encryption-at-rest, the encryption-in-transit), a retention period (per the Retention Schedule), a disposal method (per the Disposal Log), and a change-control rule (the version increment, the re-approval requirement, the communication to the affected audience).
The four dimensions are the audit-evidence surface. The auditor will sample records and walk each one through the four dimensions, was it created with the right discipline, identified with the right metadata, approved by the right authority, distributed-accessed-stored-retained-disposed-of-changed with the right control?
The retention schedule, the privacy-specific overlay
The Retention Schedule is the load-bearing privacy-specific overlay on the document-control discipline. Every record family carries a retention driver, DPDP, sector-regulator, GDPR (for organisations processing EU/EEA principals' data), organisational. The Retention Schedule maps each record type to the applicable retention driver and the applicable retention period. The Singahi Retention Schedule (toolkit doc 06) provides the structure.
The retention drivers for an Indian Data Fiduciary:
- DPDP Act 2023 + DPDP Rules 2025, section 8(7) erasure obligation (retention cannot exceed the purpose period); section 8(6) breach records (the Rules prescribe the retention period for the breach-notification records); section 9 children's-data records (the Rules prescribe the retention-and-erasure discipline for verifiable-parental-consent records); section 10 SDF records (the SDF DPIA, the independent-data-audit reports, the algorithmic-software review records, the Rules prescribe the retention); section 13 grievance records (the Rules prescribe the response-period and the retention); the Consent Manager registration conditions prescribe the consent-record retention. The DPDP Rules 2025 include the 48-hour pre-erasure notice to the Data Principal before erasure under section 8(7), the retention schedule must operationalise this notice discipline.
- CERT-In Directions 20(3)/2022-CERT-In of 28 April 2022, the 180-day log-retention duty within Indian jurisdiction (the most-overlapped retention obligation on PIMS records, especially for ICT-system logs that surface privacy-relevant events); the five-year KYC retention for VPN/data-centre/cloud/anonymous-service customers.
- RBI, the Storage of Payment System Data directive (6 April 2018) implies payment-data residency and an organisational retention; the Digital Lending Guidelines (2 September 2022) prescribe borrower-data retention; the Cybersecurity Directions 2026 (31 July 2026) require incident reporting within six hours (para 182), so keep the incident and reporting records that show the clock was met.
- SEBI, the CSCRF (20 August 2024) prescribes incident-record retention for SEBI Regulated Entities; the KRA Regulations prescribe KYC-data retention.
- IRDAI, the Information and Cyber Security Guidelines 2023 (24 April 2023) prescribe policyholder-data retention and ICT-outsourcing-data retention.
- GDPR (for organisations processing EU/EEA principals' data), Article 30 ROPA (kept up to date; retained for the controller/processor lifecycle); Article 5(2) accountability records (retained for the demonstration of compliance); Article 33 to 34 breach records (retained per the supervisory-authority guidance).
- IT Act 2000 / SPDI Rules 2011 (the legacy), section 43A reasonable-security-practices records; the SPDI Rules' body-corporate obligations. Largely superseded by the DPDP but still cited where the DPDP does not expressly occupy the field.
The retention schedule is the operational discipline that prevents two opposite failure modes. The first failure is over-retention, the organisation retains records beyond the period the regulator permits, exposing itself to a section 8(7) erasure-obligation breach. The second failure is under-retention, the organisation disposes of records before the period the regulator requires, exposing itself to a CERT-In or RBI or SEBI or IRDAI retention-duty breach. The Retention Schedule operationalises the right period per record type and the right disposal method at end-of-life.
What the standard does NOT require (the demarcation)
- 7.5 does not require a specific document-management technology. A shared drive with a strong discipline, a purpose-built document-management system, a GRC platform, an enterprise content management system, all are acceptable if the four control dimensions hold.
- 7.5 does not require the Inventory to reproduce every operational record. The Inventory links to the operational systems without reproducing their content. The 7.5-versus-8.x demarcation is load-bearing.
- 7.5 does not require every record to have the same retention period. The Retention Schedule is tuned per record family and per retention driver.
- 7.5 does not require manual approval for system-generated records. Consent records, DSAR log entries, breach log entries are approved by the operational process that produces them; the manual approval discipline applies to the strategic, governance and risk records.
- 7.5 does not require the PIMS Inventory to be separate from the ISMS Inventory. The integrated-with-distinction posture, one Inventory with discipline columns, is the recommended default for organisations running an integrated 27001 + 27701 programme.
- 7.5 does not require paper records to be digitised. Where the operational reality produces paper records (signed consent forms, signed DPA originals, printed notices in physical branches), the Inventory records the paper artefact and its physical storage location.
- 7.5 does not require retention to be the longest applicable period. Where multiple drivers apply (e.g., DPDP plus CERT-In plus RBI), the Retention Schedule reconciles the periods and selects the appropriate period per record type, typically the longest, but with documented justification where a shorter period is selected.
The companion guidance, Annex B is normative in 2025
In 27701:2019 the implementation guidance lived in informative Annex F. In 27701:2025 the guidance lives in Annex B (Implementation Guidance for PII Controllers and Processors), and Annex B is normative. For Clause 7.5 specifically, the Annex B guidance (numbered to mirror the clause) explains how the documented-information inventory should be structured across the controller and processor roles, how the ROPA should be reconciled with the application landscape, how the retention schedule should accommodate multi-jurisdiction processing, and how the disposal discipline should preserve the evidence chain. Auditors will test against Annex B, not just against the clause text.
Five external anchors are most relevant for Clause 7.5.
- ISO/IEC 27001:2022 Clause 7.5 (Documented Information, the infosec sibling) is structurally identical. The integrated-with-distinction posture uses the shared structure and the shared document-control discipline.
- ISO/IEC 27002:2022 control 5.33 (Protection of records) is the operational reference for the storage-and-protection dimension; the privacy programme inherits the protection discipline and adds the privacy-classification overlay.
- ISO/IEC 27002:2022 control 8.10 (Information deletion) is the operational reference for the disposal discipline; the privacy programme inherits the secure-deletion discipline and adds the DPDP section 8(7) erasure overlay.
- GDPR Article 30 (Records of processing activities) is the anchor for the ROPA content and the controller-versus-processor ROPA split.
- NIST Privacy Framework v1.0, Identify-P function (data mapping, business environment) is the US-flavoured structural analogue for the data-mapping discipline that the ROPA operationalises.
What auditors actually check
The certification auditor's Clause 7.5 examination has seven predictable moves.
First, the auditor opens the Documented Information Policy and the Document Control Procedure. Are they dated, version-controlled, signed by top management or the DPO with sponsor authority? Do they document the seven-family inventory, the four control dimensions, the format-and-identification standard, the review-and-approval matrix, the access-control matrix, the version-control standard, the change-control workflow, the Retention Schedule, and the disposal discipline? If any of these fails, minor nonconformity. If the documents do not exist, major nonconformity.
Second, the auditor opens the PIMS Documented Information Inventory. Does it cover all seven families? Does it reconcile with the operational systems, the application landscape (every application processing personal data has a corresponding ROPA entry), the procurement system (every processor has a corresponding DPA entry), the incident-response system (every breach has a corresponding breach-log entry), the support-ticketing system (every DSAR has a corresponding DSAR-log entry), the contract repository (every DPA has a corresponding Inventory entry)? Are the owner, version, classification, retention period and disposal method populated for every entry?
Third, the auditor tests the ROPA. Is it current? Does it reconcile with the application landscape? Does each entry carry the required content (purpose, lawful basis, recipients, retention, controls, residual risk, links to the DPIA, the SoA, the breach log, the DSAR log)? Has it been refreshed in the last 12 months and on every material change? The ROPA-as-compliance-artefact pattern (the ROPA that exists as a one-off document produced for the last audit) is the canonical 7.5 finding.
Fourth, the auditor tests the Retention Schedule. Does it cover every record family? Does it accommodate the DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR and organisational drivers? Does it operationalise the section 8(7) erasure discipline and the 48-hour pre-erasure notice? Are the disposal methods specified? Is the Disposal Log current?
Fifth, the auditor tests the version-and-approval and access-control matrices. Does every document type have a defined approving authority? Does every record type have a defined access-control rule with the privacy-classification overlay? Are the matrices current?
Sixth, the auditor traces sampled records through the four control dimensions. Three to five named records, typically a processing activity in the ROPA, a vendor contract in the DPA register, a breach incident in the breach log, a rights request in the DSAR log, a consent record for a sampled principal. Each one is traced through create-and-update, identification-and-format, review-and-approval, distribution-access-storage-retention-disposal-change. If any of those traces is hollow, the PIMS has a 7.5 finding regardless of how complete the Inventory looks on paper.
Seventh, the auditor checks the 7.5-to-10.2 pipeline. When a documented-information gap surfaced (from an internal audit, a regulator engagement, a customer assessment, an operational incident), did it feed the Clause 10.2 corrective-action pathway? Is there a record of gap-closure verification?
Why This Control Matters
The record-keeping layer as the foundation of every other clause
Every other clause and annex of ISO/IEC 27701:2025 is, in audit terms, demonstrated through records. The privacy policy (5.2) is itself a record and is interpreted through records; the roles (5.3) are evidenced through records; the privacy risk register (6.1) is a record; the objectives (6.2) are evidenced through records; the changes (6.3) are recorded; the operational processes (Clause 8), the consent capture, the notice issuance, the DSAR handling, the grievance redressal, the processor management, the cross-border transfer screening, the breach reporting, all produce records; the controls (Annex A.1 / A.2 / A.3) are evidenced through records; the internal audit (9.2) and the management review (9.3) are recorded; the corrective actions (10.2) and the improvements (10.1) are recorded.
Without 7.5, the entire PIMS is a paper architecture that cannot be demonstrated. The most carefully drafted privacy policy fails the moment the auditor asks for the version that was in force when a sampled principal was onboarded and the document control cannot retrieve it. The most carefully designed ROPA fails the moment a sampled processing activity cannot be reconciled against the application landscape. The most carefully drafted breach playbook fails the moment the breach log cannot demonstrate that the DPDP clock (intimation without delay; 72-hour report) and the 6-hour CERT-In clock were both started in time. The most carefully drafted DPA fails the moment the Inventory cannot produce the executed counter-signed copy of the processor agreement for a sampled vendor.
The certification auditor and the Data Protection Board of India converge on the same operational reality. A PIMS built on a scattered shared-drive practice is, in auditor language, a "system without record reliability", a structural finding that cascades into every operational clause because the records cannot demonstrate the controls. A PIMS built on a disciplined documented-information practice is defensible end-to-end.
The Indian regulatory weight behind 7.5
In India, Clause 7.5 has a regulatory weight that goes beyond the ISO standard itself. The DPDP Act 2023 (Act 22 of 2023, enacted 11 August 2023) and the DPDP Rules 2025 (notified 13 November 2025) make record-keeping the operational pivot on which several statutory obligations turn.
The most load-bearing 7.5-relevant DPDP provision is section 8(6), the breach-notification clock. The breach clock (intimation without delay; 72-hour report) to the Data Protection Board of India must be supported by a contemporaneous breach record, the moment the Data Fiduciary became aware, the form and manner of the notification (the Rule 7 intimation content), the correspondence with the Board, the affected-principal notifications. Without a 7.5-conformant breach log, the Data Fiduciary cannot demonstrate compliance with the clock, and the section 33 + Schedule penalty exposure (up to 200 crore rupees for a section 8(6) failure) becomes operational. The breach log is the canonical Family 3 / Family 7 record.
The second most load-bearing provision is section 10, the Significant Data Fiduciary obligations. A designated SDF must operate the DPO / SDF DPIA / independent-data-audit / algorithmic-software review machinery; each produces records that must be controlled under 7.5. The SDF DPIA library (Family 3) is the Article 35(7) analogue; the independent-data-audit reports (Family 5) are the audit-evidence records; the algorithmic-software review records (Family 3 and Family 7) are the new AI-driven record-keeping duty. The SDF record-keeping duty is operationally inseparable from the section 10 obligations.
The third is section 13, the grievance-redressal duty. The Data Fiduciary and the Consent Manager must maintain the grievance records, the receipt, the response within the prescribed period, the resolution or escalation. The grievance log is the canonical Family 3 record; the 7.5 retention schedule must operationalise the prescribed retention.
The fourth is section 2(1)(g) read with section 6, the Consent Manager. A Consent Manager must enable the principal to give, manage, review and withdraw consent across multiple Data Fiduciaries. The Consent Manager must maintain the consent records (give, manage, review, withdrawal) in an interoperable format, retained for the prescribed period, and made available to the principal and to the Board on demand. The consent-record-keeping duty is operationally inseparable from the Consent Manager function; the 7.5 retention schedule must operationalise the Consent Manager registration conditions.
The fifth is the dual-clock pattern. A single personal-data-breach event produces two parallel reporting records under two parallel regimes, the CERT-In 6-hour record (CERT-In Directions 20(3)/2022-CERT-In of 28 April 2022, the ICT-incident record and the 180-day log retention) and the DPDP record (intimation without delay, then a 72-hour report; DPDP Act section 8(6) read with DPDP Rules 2025 Rule 7, the personal-data-breach record). For BFSI and listed entities, a third record applies (RBI six hours; SEBI 6 hours; IRDAI 24 to 72 hours). The 7.5 discipline must ensure the same breach event produces the right records under each regime, retained for the right period, retrievable on demand by the right regulator.
The lineage is the wedge. K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (judgment delivered 24 August 2017 by a nine-judge Bench of the Supreme Court) declared the right to informational privacy a fundamental right under Articles 14, 19 and 21. The Aadhaar judgment, Justice K.S. Puttaswamy (Retd.) v. Union of India, (2019) 1 SCC 1 set the proportionality test that every privacy-relevant processing must meet, a test that requires the processing to be lawful, legitimate and proportionate, and the lawfulness and the legitimacy and the proportionality to be demonstrable through records. The DPDP Act was enacted on 11 August 2023. The DPDP Rules 2025 were notified on 13 November 2025 with phased commencement. ISO/IEC 27701:2025 was published on 14 October 2025. The documented-information discipline is where the constitutional lineage enters the demonstrable practice of the organisation.
The cost of non-compliance
The cost of a Clause 7.5 failure breaks down into four bands.
Direct DPDP penalty exposure for an organisation whose record-keeping gap produced a missed clock, a missed response, a missed retention duty, or a missed disposal discipline can run to the Schedule maxima, up to 250 crore rupees for section 8(5) failure (reasonable security safeguards, the records are part of the safeguards); 200 crore for section 8(6) failure (breach notification, the breach record is the evidence); 200 crore for section 9 failure (children's data, the verifiable-parental-consent records); 150 crore for section 10 failure (SDF obligations, the SDF DPIA, audit and AI-fairness records).
Indirect regulatory consequences are larger and slower. A record-keeping gap that produces a structural pattern of missing or stale records compounds across the regulator's examination and amplifies the regulatory exposure with every inquiry.
Commercial cost is significant. Indian privacy incidents, Juspay (approximately 35 million records in 2021), BigBasket (approximately 20 million records alleged in 2020), Air India / SITA (approximately 4.5 million customers affected by the SITA breach disclosed in 2021), MobiKwik (contested allegations, denied by the company), all carried post-incident examinations that tested whether the breach log was current, whether the consent records were retrievable, whether the DPA register was complete, whether the ROPA reconciled with the application landscape. A documented-information discipline that cannot retrieve the records on demand amplifies the commercial cost.
Certification cost is the most immediate. Recoverable; entirely avoidable.
Scope and Applicability
By organisation size
Growing companies (50 to 250 staff). A compact documented-information programme: a Documented Information Policy of 6 to 10 pages, a Document Control Procedure of 20 to 30 pages, an Inventory in a structured spreadsheet (one row per record type), a ROPA in a structured spreadsheet (one row per processing activity), a Retention Schedule of 4 to 8 pages, the approval-and-access matrices as spreadsheets, a Disposal Log as a structured spreadsheet. The first cycle is deliverable in 8 to 16 weeks of internal effort plus external advisory.
Mid-sized (250 to 2,000 staff). A more granular programme: a Policy of 8 to 14 pages, a Procedure of 30 to 50 pages, the Inventory in a GRC module or a purpose-built privacy platform, the ROPA in a purpose-built privacy platform, the Retention Schedule of 8 to 14 pages, the matrices as configuration in the GRC platform, a Disposal Log integrated with the records-management system. The first cycle typically takes 14 to 22 weeks.
Multi-entity enterprise (2,000+ staff or multi-jurisdiction). A layered documented-information architecture: group Inventory plus entity-level localisation plus jurisdiction-specific overlays (DPDP for India, GDPR for EU/EEA, PIPL for China, LGPD for Brazil, CCPA/CPRA for California); multi-language records; the contractor-ecosystem records (often thousands of contractors producing records); the SDF-level records (SDF DPIA library, audit-evidence records, algorithmic-software review records). Typically 5 to 9 months for the first cycle, with an embedded records-management function.
By PIMS role
PII controller (Data Fiduciary) primary. The documented-information discipline leads with the controller-side load: the ROPA (the controller-Retained record), the consent records (the controller captures and retains), the notice records (the controller issues), the DSAR log (the controller responds to the rights), the grievance log (the controller's grievance officer handles), the breach log (the controller's breach-notification duty), the DPIA library (the controller's DPIA duty), the transfer records (the controller's transfer basis). The controller-Retained records form the bulk of Family 3.
PII processor (Data Processor) primary. The documented-information discipline leads with the processor-side load: the DPA register (the executed agreements with each controller customer), the sub-processor records (the sub-processor list, the change-notification records, the controller-approval records), the infringing-instruction records (the Annex A.2.2.5 pathway), the breach-notification-to-controller records (the processor's duty to notify the controller without undue delay), the cross-border transfer records (the processor's transfer chain). The processor-Retained records form a distinct sub-set of Family 3.
Both controller and processor. The most common shape for Indian growing companies. The documented-information discipline addresses both loads and the boundary between them, the same record may exist in both the controller and the processor form (a DPA from the controller side is a counter-party DPA from the processor side; the ROPA from the controller side is a processing-activities record from the processor side).
By sector
Sector-specific overlays are addressed in Section 21. The headline sectors, BFSI, Healthcare, IT-ITeS, E-commerce, Edtech, Manufacturing, each carry distinctive documented-information profiles (RBI payment-data retention and incident-reporting for BFSI; clinical-records sensitivity and the patient-data retention for Healthcare; processor-side scale and the multi-jurisdiction ROPA for IT-ITeS; consumer-privacy records at scale and the consent-record discipline for E-commerce; verifiable-parental-consent records and the section 9 regime for Edtech; HR records and the contractor ecosystem for Manufacturing).
Key Definitions and Terminology
Documented information. The harmonized-structure term for the information the organisation must control to make the management system demonstrable. Includes documents (policies, procedures, plans, inventories, created to describe the system) and records (the evidence the system operated, log entries, audit reports, meeting minutes, consent captures, breach notifications). In a PIMS, documented information includes the privacy-specific operational records, not merely the descriptive documents.
Records of Processing Activities (ROPA). The master record of the PIMS, the GDPR Article 30 analogue; the DPDP section 8 records-of-compliance artefact. Links processing activities to purposes, lawful bases, retention periods, recipients, transfers, controls and risks.
Statement of Applicability (SoA). The Clause 6.1 artefact listing the Annex A.1/A.2/A.3 controls applicable, the justification, the implementation status, and the linkage to the risk register. Family 2.
Consent record. Family 3 record evidencing the principal's consent, date, principal identifier, purpose, consent text, affirmative action, channel, Consent Manager reference, withdrawal events. Must satisfy the DPDP section 6 free-specific-informed-unconditional-unambiguous test and the GDPR Article 7(1) demonstrate-of-consent duty.
Data Protection Impact Assessment (DPIA) record. Family 3 record for a high-risk processing activity. GDPR Article 35(7) content analogue; DPDP section 10 SDF DPIA. Includes the processing description, the necessity-and-proportionality assessment, the risks to principals, the mitigation, the residual risk.
Data Processing Agreement (DPA) record. Family 3 record of the controller-processor or processor-sub-processor agreement. GDPR Article 28(3) mandatory clauses; DPDP processor-side flow-down.
Breach record. Family 3 / Family 7 record of the personal-data-breach event, the awareness moment, the form and manner of the notification (CERT-In 6-hour; DPDP Rule 7 intimation without delay and 72-hour report; sector-regulator), the affected-principal notifications, the investigation file, the corrective actions. The canonical 7.5 evidence under the dual-clock pattern.
DSAR log. Family 3 record of the data-principal rights requests, access (section 11 / Article 15), correction and erasure (section 12 / Articles 16 to 17), grievance (section 13), nomination (section 14), consent-withdrawal (section 6 / Article 7(3)). Demonstrates the response within the prescribed period.
Transfer record. Family 3 record of the cross-border transfer, destination country, transfer mechanism (DPDP section 16 negative-list screen; GDPR Article 45/46/49 mechanism), transfer-impact assessment, supplementary measures, records of recipients.
Retention schedule. Family 1 artefact mapping each record type to its retention driver (DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR, organisational) and its retention period. Operationalises the section 8(7) erasure discipline, the CERT-In 180-day log-retention duty, the sector-regulator retention duties, and the organisational retention decisions.
Disposal log. Family 5 / Family 6 artefact recording end-of-life destruction, record type, disposal method (crypto-shredding, cross-cut shredding, certificate of destruction), date, witnessing authority. The evidentiary defence against an under-retention allegation.
Inventory. The master register of every document and record in the PIMS scope. Links to the operational systems without reproducing the operational content. The audit-evidence surface for Clause 7.5.
Version-and-approval matrix. Family 1 artefact mapping each record type to its approving authority.
Access-control matrix. Family 1 artefact mapping each record type to its access rules, read, edit, administer, with the privacy-classification overlay.
Privacy classification overlay. Family 1 method applying a privacy classification (public, internal, confidential, restricted, privileged) to each record type and adjusting the protection, access and disposal disciplines accordingly.
The 7.5-versus-8.x demarcation. Clause 7.5 governs how documented information is controlled (version, access, retention, disposal, change); Clause 8 produces the operational records themselves. The demarcation-with-linkage posture is the Singahi-recommended pattern.
The integrated-with-distinction posture. The PIMS Inventory and the ISMS Inventory share one register with discipline columns, two distinct content tracks (privacy and security), and a unified control discipline. Jointly owned by the DPO and the CISO.
Consent Manager (DPDP section 2(1)(g)). The registered, interoperable, principal-side intermediary through which a Data Principal gives, manages, reviews and withdraws consent across multiple Data Fiduciaries. The records are operationally inseparable from the Consent Manager function.
Significant Data Fiduciary (DPDP section 10). A Data Fiduciary designated by the Central Government on prescribed thresholds. The designation triggers the SDF DPIA, the independent-data-audit, and the algorithmic-software review record-keeping duties.
Relationship to Other Clauses and Frameworks
Inside ISO/IEC 27701:2025
- 4.1 (context): the issues drive the documented-information landscape, the scope of processing, the principal classes, the regulatory landscape the records must reflect.
- 4.2 (interested parties): the requirements register drives the record-keeping duties, every material requirement (regulator, customer, principal) generates a record family.
- 4.3 (scope): the scope statement is the foundational documented-information artefact; the Inventory is bounded by the scope.
- 4.4 (the PIMS): sustained by the documented-information discipline.
- 5.1 (leadership): top management owns the documented-information commitment.
- 5.2 (policy): the privacy policy is the load-bearing strategic documented-information artefact, every Clause 7.5 Inventory references the policy explicitly and the policy-approval cycle fires on every policy revision.
- 5.3 (roles): the version-and-approval and access-control matrices map directly to the role register.
- 6.1 (risks): the privacy risk register and the SoA are core PIMS documented information (Family 2).
- 6.2 (objectives): the objectives and the planning-to-achieve-them are documented information.
- 6.3 (changes): every PIMS change triggers a document-control event under 7.5, the change record, the version increment, the re-approval, the communication to the affected audience.
- 7.1 (resources): the document-control platform, the privacy platform, the GRC module, the records-management system are 7.1 line items.
- 7.2 (competence): the competence matrix and the qualifications evidence are documented information (Family 4).
- 7.3 (awareness): the awareness Evidence Register and the simulation records are documented information (Family 4).
- 7.4 (communication): the communication records and the communication plan are documented information (Family 4).
- 7.5 (this clause, the control framework).
- 8.1 to 8.3 (operation): the operational records, the ROPA, the consent records, the DPIA library, the DPA register, the breach log, the DSAR log, the transfer records, the grievance log, are produced by Clause 8 and controlled by 7.5 (Family 3). The 7.5-versus-8.x demarcation is load-bearing.
- 9.1 (monitoring): the monitoring-and-measurement records are documented information (Family 5).
- 9.2 (internal audit): the audit programme, the audit reports, the audit-evidence working papers are documented information (Family 5).
- 9.3 (management review): the review minutes and the input/output records are documented information (Family 5).
- 10.2 (corrective action): the nonconformity register, the corrective-action records, the root-cause analyses, the effectiveness reviews are documented information (Family 6).
- 10.1 (improvement): the improvement records and the lessons-learned are documented information (Family 6).
- Annex A.1.2.2 to A.1.2.6 (conditions for collection and processing): the ROPA, the consent records, the DPIA library (Family 3).
- Annex A.1.3 (obligations to PII principals): the DSAR log, the grievance log (Family 3).
- Annex A.1.5 (PII sharing, transfer and disclosure): the DPA register, the sub-processor list, the transfer records, the disclosure records (Family 3).
- Annex A.2.2.x (processor conditions): the processor-side DPA records, the infringing-instruction records (Family 3).
- Annex A.3.21 (secure disposal): the disposal discipline (Family 5 / Family 6, the Disposal Log).
- Annex A.3.25 (logging): the system-generated records that feed the operational logs.
- Annex A.3.26 (cryptography): the encryption-at-rest and the encryption-in-transit that protect documented information.
Cross-framework
- ISO/IEC 27001:2022 Clause 7.5 (Documented Information), structurally identical on the infosec side; the integrated-with-distinction posture uses the shared structure and the shared document-control discipline.
- ISO/IEC 27002:2022 control 5.33 (Protection of records), the operational reference for the storage-and-protection dimension.
- ISO/IEC 27002:2022 control 8.10 (Information deletion), the operational reference for the disposal discipline.
- ISO/IEC 27002:2022 control 5.34 (Privacy and protection of PII), the only PII-specific control in 27002; cross-references the documented-information discipline.
- ISO/IEC 29100:2011 (privacy framework, 11 principles), the accountability and the openness/transparency principles are the documented-information foundation.
- GDPR Article 30 (Records of processing activities), the controller ROPA content in Article 30(1); the processor ROPA content in Article 30(2).
- GDPR Article 5(2) (accountability), the controller's responsibility to demonstrate compliance with the Article 5(1) principles; the anchor for the Family 3 records.
- GDPR Article 28(3) (DPA mandatory clauses), the controller-processor DPA content; the anchor for the DPA register content.
- GDPR Article 35(7) (DPIA content), the anchor for the DPIA library content.
- GDPR Articles 33 to 34 (breach notification), the anchor for the breach log content and the 72-hour-clock record.
- NIST Privacy Framework v1.0, Identify-P function (data mapping, business environment), the US-flavoured structural analogue for the data-mapping discipline that the ROPA operationalises.
- NIST Privacy Framework v1.0, Communicate-P function (reporting), the analogue for the reporting records.
- SOC 2 (AICPA TSC 2017), CC2.2 (internal communication), CC6.5 (logical access), CC7.1 (detection), the Privacy category P3.0 (collection), the SOC 2 view of the documented-information discipline.
- DPDP Act 2023, section 4 grounds (lawful-basis records); section 5 notice (notice records); section 6 consent (the consent-record-keeping duty); section 7 legitimate uses (the non-consent-grounds records); section 8 general obligations (records of compliance with 8(5) safeguards, 8(6) breach records, intimation without delay and a 72-hour report record, 8(7) erasure records, the retention schedule operationalised); section 9 children (verifiable-parental-consent records, no-behavioural-tracking records); section 10 SDF (DPIA, audit, AI-fairness records); section 11 access (DSAR records); section 12 correction/erasure (correction-and-erasure records); section 13 grievance (grievance records, within the prescribed period); section 14 nomination (nomination records); section 16 transfer (negative-list screening records); section 18 DPBI (regulator-correspondence records); section 33 + Schedule (penalty-exposure records). The DPDP is the load-bearing regulatory input to the Indian PIMS documented-information discipline.
- DPDP Rules 2025 (notified 13 November 2025), Rule 7 (the breach-notification record format and the breach clock evidence (intimation without delay; 72-hour report)); the verifiable-parental-consent mechanism under section 9; the SDF designation thresholds and the SDF DPIA/audit cadence; the data-retention and erasure timelines including the 48-hour pre-erasure notice; the Consent Manager registration conditions; the grievance-redressal response periods.
Inside the harmonized structure, what 7.5 inherits
The harmonized structure (HS, formerly Annex SL) is the shared skeleton ISO uses for management-system standards. 27701:2025, 27001:2022, 22301:2019, 9001:2015, 14001:2015, 45001:2018, 42001:2023 all use it. For 7.5, this means:
- The clause text is structurally identical across all HS standards, only the subject-matter load differs.
- An organisation running an integrated 27001 + 27701 + 42001 programme can run a single combined documented-information discipline with discipline columns tagging each entry as ISMS-relevant, PIMS-relevant, AIMS-relevant, BCMS-relevant, or shared.
- The seven-family inventory, the four control dimensions, the ROPA-as-master-record concept and the retention-schedule overlay are common across disciplines; the content differs.
- The Inventory can serve multiple management-system clauses with a discipline column tagging each entry.
The Singahi integrated Document Control Procedure (toolkit doc 02) supports the HS-combined pattern: a single Inventory with discipline columns and a single Document Control Procedure with discipline-tagged sections.
Detailed Implementation Guidance, The Seven Documented-Information Moves
Figure · Process
What Clause 7.5 asks you to do
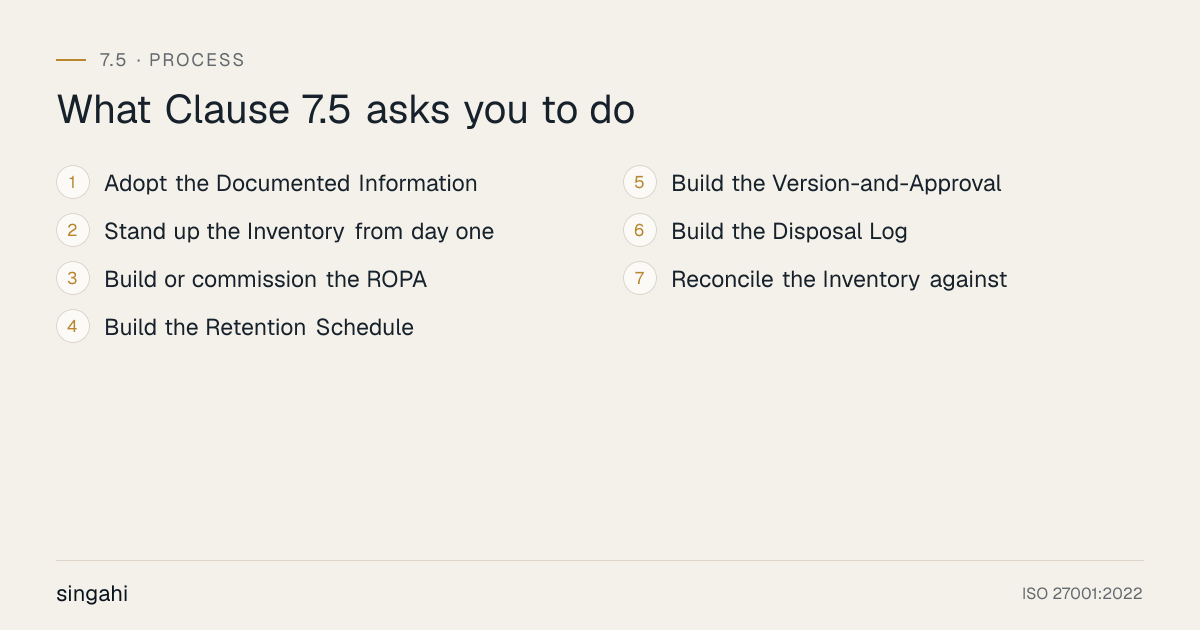
Move 1, Adopt the Documented Information Policy and the seven-family inventory
The first move is the governance artefact and the inventory decision. The Documented Information Policy (toolkit doc 01) commits the organisation to the seven-family inventory, the four control dimensions, the format-and-identification standard, the review-and-approval matrix, the access-control matrix, the version-control standard, the change-control workflow, the Retention Schedule, and the disposal discipline. The Policy is approved by top management (Clause 5.1) and references the privacy policy (Clause 5.2) as the strategic anchor.
The seven-family inventory decision assigns every document and record in the PIMS scope (Clause 4.3) to one of the seven families (Strategic and governance; Risk and treatment; Operational privacy; Support evidence; Evaluation; Improvement; Sector and regulatory). The Singahi Inventory template (toolkit doc 02 annex A) provides the structure. Typical inventory sizes for an Indian growing company: 80 to 200 distinct record types for a 50 to 250-staff firm; 200 to 600 for a growing firm; 600 to 2,000-plus for a multi-entity enterprise.
Move 2, Stand up the Inventory from day one
The Inventory is the load-bearing 7.5 artefact and the discipline that keeps the record-keeping honest. Stand it up from day one, even as a structured spreadsheet before the GRC-platform integration. The Singahi Inventory (toolkit doc 02) records per record type: the family, the document/record name, the description, the owning clause, the owner role, the version, the effective date, the location (system of record), the format, the classification, the approval authority, the access rule, the retention period, the retention driver, the disposal method, the last review date, the next review date, the linkage to the operational system, and the status.
The Inventory updates on every record-creation event and on every Inventory-refresh cycle. The Inventory reconciliation against the operational systems (Move 8) is the operational discipline that keeps the Inventory current.
Move 3, Build or commission the ROPA (the master record)
The ROPA is the master record of the PIMS. Building it is the single highest-use 7.5 investment. The Singahi ROPA template (toolkit doc 03) provides the structure. The ROPA is built in three phases.
Phase A, the application landscape reconciliation. Walk every application processing personal data in the PIMS scope (Clause 4.3) and create a ROPA entry for each. The application landscape is the audit-evidence baseline; every application must reconcile to a ROPA entry.
Phase B, the processing-activity deep dive. For each application, document the processing activities, the purpose, the lawful basis, the categories of principals, the categories of personal data, the recipients, the cross-border transfers, the retention period, the technical and organisational controls, the residual risk rating, the link to the DPIA where one was conducted, the link to the SoA entries.
Phase C, the operational reconciliation. Reconcile the ROPA against the operational systems, the consent records (each consent capture references a ROPA entry), the breach log (each breach references the affected processing activities), the DSAR log (each rights request references the affected processing activities), the DPA register (each processor references the processing activities it supports).
The ROPA is the master record every audit, every DPIA, every DSAR response, every breach investigation and every regulator engagement hangs off. The ROPA reconciliation against the application landscape is the canonical 7.5 audit-evidence test.
Move 4, Build the Retention Schedule
The Retention Schedule (toolkit doc 06) is the privacy-specific overlay on the document-control discipline. Build it in three layers.
Layer 1, the DPDP overlay. Map every Family 3 record type to its DPDP retention driver, section 8(7) erasure obligation, section 8(6) breach records, section 9 children's-data records, section 10 SDF records, section 13 grievance records, the Consent Manager registration conditions. Operationalise the 48-hour pre-erasure notice to the Data Principal under DPDP Rules 2025.
Layer 2, the sector-regulator overlay. Map every record type to its CERT-In (180-day log retention; 5-year KYC for VPN/data-centre/cloud customers), RBI (payment-data residency; digital-lending borrower-data; ICT-incident records; cyber-security-framework incident records), SEBI (CSCRF incident records; KRA KYC data), IRDAI (policyholder data; ICT-outsourcing data) retention driver.
Layer 3, the organisational overlay. Map every record type to its organisational retention decision, the certification-scheme retention (typically three certification cycles for the audit reports and management-review minutes), the employment-law retention (employee records), the contract retention (the DPA originals), the historical-record retention (the prior versions of the strategic records).
The Retention Schedule is the operational discipline that prevents both over-retention (the section 8(7) breach) and under-retention (the CERT-In or RBI or SEBI or IRDAI retention-duty breach).
Move 5, Build the Version-and-Approval and Access-Control matrices
The Version-and-Approval Matrix (toolkit doc 04) maps each record type to its approving authority. The Access-Control Matrix maps each record type to its access rules, who can read, who can edit, who can administer, with the privacy-classification overlay. The two matrices are the operational disciplines that prevent the unapproved-record pattern and the over-access pattern.
The privacy-classification overlay is the privacy-specific load. Every record type carries a classification (public, internal, confidential, restricted, privileged) that adjusts the protection, access and disposal disciplines. A ROPA entry identifying a vulnerable principal's health data carries a "restricted" classification with the access limited to the care team and the DPO; a marketing-lead capture carries an "internal" classification with broader marketing-team access; a breach investigation file carries a "privileged" classification with the DPO, the Legal Head and the incident-response lead.
Move 6, Build the Disposal Log and the change-control workflow
The Disposal Log (toolkit doc 07) records the end-of-life destruction of records, the record type, the disposal method (crypto-shredding for digital, cross-cut shredding for paper, certificate of destruction for outsourced disposal), the date, the witnessing authority, the legal-hold status. The Disposal Log is the evidentiary defence against an under-retention allegation and the operational evidence of the section 8(7) erasure discipline.
The change-control workflow operationalises Dimension 4 (distribution, access, storage, retention, disposal and change). Every document change is identified, recorded, version-controlled, communicated to the affected audience, and subject to re-approval where material. The workflow integrates with the Clause 6.3 PIMS change-control discipline, every material change to the PIMS triggers a document-control event under 7.5.
Move 7, Reconcile the Inventory against the operational systems
The seventh move is the reconciliation discipline that converts the Inventory from a static document into a system. The Singahi reconciliation (toolkit doc 09) reconciles the Inventory against the application landscape (every application processing personal data has a corresponding ROPA entry, surfaces shadow-IT gaps and drift), the procurement system (every processor has a corresponding DPA entry, surfaces vendors onboarded without a DPA), the incident-response system (every breach has a corresponding breach-log entry, surfaces incidents not classified as personal-data breaches), the support-ticketing system (every DSAR has a corresponding DSAR-log entry, surfaces rights requests treated as casual enquiries), the contract repository (every contract with privacy-relevant obligations has a corresponding Inventory entry, surfaces contracts signed without the privacy-flow-down clauses), and the HR system (every employee record with privacy-relevant content has a corresponding Inventory entry, surfaces contractor records missing and employee records past their retention period).
The reconciliation runs on a defined cadence, quarterly for the high-volume reconciliations (the application landscape, the procurement system, the incident-response system, the support-ticketing system) and annually for the lower-volume reconciliations. The reconciliation outcomes feed the Clause 10.2 corrective-action pathway. A reconciliation that surfaces gaps without triggering corrective actions is the canonical 7.5 finding.
The integrated-with-distinction discipline in more depth
The integrated Inventory is only as good as the discipline columns that keep the ISMS and the PIMS tracks distinct. Pattern A, Integrated-with-distinction (the Singahi recommended default): one Inventory with discipline columns tagging each entry as ISMS-relevant, PIMS-relevant, or both; the DPO and the CISO jointly own the Inventory; the four control dimensions apply uniformly; the content tracks are differentiated. Pattern B, Parallel inventories: two inventories maintained in parallel; the DPO owns the PIMS Inventory; the CISO owns the ISMS Inventory; the two are reconciled periodically. Pattern C, Merged-without-distinction (the failure pattern): one Inventory with no discipline columns; the privacy-specific load is invisible. The Pattern C failure is the canonical 7.5 finding in the Indian growing-company segment running an integrated ISMS+PIMS programme. The full Tarini Commerce worked example is in Section 15.
Tools, Technologies, and Solutions
The tool categories
Document Management Systems (DMS) and Enterprise Content Management (ECM). The foundational layer for the document-control discipline. A DMS or ECM provides the version control, the access control, the workflow (review-and-approval), the records-management discipline (retention, disposal, legal hold), the audit trail, and the search. Generic descriptions: a DMS with the document-lifecycle workflow, the version control, the access control, the records-management module; an ECM with the content-services layer, the workflow engine, the records-management module, the eDiscovery module.
Privacy platforms / Privacy Management Software. The purpose-built layer for the Family 3 operational privacy records. A privacy platform provides the ROPA module, the consent-management module, the DPIA module, the DPA-register module, the DSAR-management module, the breach-management module, the transfer-management module, the data-mapping module. Generic descriptions: a privacy platform with the ROPA module and the consent module; a privacy-management software with the DSAR workflow and the breach workflow; a data-mapping platform with the application-landscape reconciliation.
Governance, Risk and Compliance (GRC) platforms. The integrated layer for the Family 2 (risk), Family 4 (support evidence), Family 5 (evaluation) and Family 6 (improvement) records. A GRC platform provides the risk register, the SoA, the control-evidence module, the audit-management module, the corrective-action module, the policy-management module, the training-records module.
Consent Management Platforms (CMP). The operational layer for the consent records (Family 3). A CMP captures, stores, version-controls, and produces consent records on demand. The Consent Manager interoperability (DPDP section 2(1)(g)) is a distinctive Indian requirement, a Consent Manager is a registered, principal-side, interoperable intermediary that the CMP must integrate with.
Incident and breach-response platforms. The operational layer for the breach log (Family 3 and Family 7).
Records-management systems (RMS). The discipline layer for the retention schedule and the disposal log. Some DMS/ECM platforms include an RMS; some organisations run a standalone RMS.
Data Loss Prevention (DLP) and Information Protection platforms. The protection layer for the storage-and-protection dimension. A DLP platform prevents the unauthorised exfiltration of classified records; an information-protection platform applies the encryption, the classification labels, and the access policies.
Selection criteria
Select on: India-DPDP coverage (most global privacy platforms are GDPR-heavy and DPDP-thin); the seven-family inventory support (the ability to record every record type in the PIMS scope); the four-control-dimensions support (create-and-update, identification-and-format, review-and-approval, distribution-access-storage-retention-disposal-change); the ROPA-as-master-record support (the ability to link every operational record to a ROPA entry); the retention-schedule support (the ability to accommodate DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR and organisational retention drivers); the disposal-log support (the ability to record the disposal event with the method, the date, the witnessing authority); the reconciliation support (the ability to reconcile the Inventory against the operational systems); the Consent Manager interoperability (where applicable); and cost-to-value for the Indian growing-company segment.
Build vs buy
Most growing companies should buy the DMS/ECM, the privacy platform, the GRC, and the consent-management platform, and build the documented-information discipline (the seven-family inventory, the four control dimensions, the version-and-approval matrix, the access-control matrix, the retention schedule, the disposal log, the reconciliation cycles) in-house with external advisory for the first cycle. The discipline is too organisation-specific to outsource end-to-end; the tooling is too time-intensive to build internally.
Policy and Procedure Templates
Documented Information Policy (sample of our own drafting)
The organisation maintains a PIMS Documented Information Discipline as the operational expression of the Clause 7.5 commitment. The Discipline is governed by this Policy and operationalised by the Document Control Procedure. Every document and record in the PIMS scope (Clause 4.3) is captured in the PIMS Documented Information Inventory, classified into one of the seven families (Strategic and governance; Risk and treatment; Operational privacy; Support evidence; Evaluation; Improvement; Sector and regulatory), and controlled under the four control dimensions (create-and-update, identification-and-format, review-and-approval, distribution-access-storage-retention-disposal-change). The ROPA is the master record of the PIMS and anchors every operational record. The Retention Schedule operationalises the DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR and organisational retention drivers. The Disposal Log evidences the end-of-life destruction of records. The Discipline is owned by the DPO, co-sponsored by the CISO (integrated-with-distinction posture), the Legal Head and the Quality / ISMS representative, approved by top management, and reviewed annually and on every material change.
Document Control Procedure (sample of our own drafting, summarised)
- Purpose and scope, the Procedure applies to every document and record in the Clause 4.3 PIMS scope; the seven-family inventory (Section 2.2) structures the discipline.
- Seven-family inventory, Family 1 (Strategic and governance); Family 2 (Risk and treatment); Family 3 (Operational privacy); Family 4 (Support evidence); Family 5 (Evaluation); Family 6 (Improvement); Family 7 (Sector and regulatory).
- Document lifecycle, create, review, approve, publish, distribute, use, retain, dispose. Each stage has a defined trigger, a defined authority, a defined evidence record.
- Identification and format standard, every record carries an identifier, a version, a date, an owner, a classification, a format, and a location. The format standard is uniform across the Inventory; the format varies by family.
- Version-and-approval matrix, every record type has a defined approving authority (the matrix; toolkit doc 04).
- Access-control matrix, every record type has defined access rules with the privacy-classification overlay (the matrix; toolkit doc 05).
- Version control standard, semantic versioning for documents (major.minor); monotonic versioning for records.
- Change-control workflow, every change is identified, recorded, version-controlled, communicated, and re-approved where material.
- Retention Schedule, every record type has a defined retention period per the Retention Schedule (toolkit doc 06); the schedule operationalises the DPDP section 8(7) erasure discipline, the CERT-In 180-day log-retention duty, the RBI/SEBI/IRDAI sector-retention duties, and the organisational retention decisions.
- Disposal discipline, every record at end-of-life is disposed of per the Disposal Log (toolkit doc 07); the method, the date, the witnessing authority, the legal-hold status are recorded.
- ROPA as master record, the ROPA (toolkit doc 03) is the master record; every operational record links to a ROPA entry.
- Reconciliation cycles, quarterly for the high-volume reconciliations (the application landscape, the procurement system, the incident-response system, the support-ticketing system); annually for the lower-volume reconciliations.
- Integrated-with-distinction posture, the PIMS Inventory and the ISMS Inventory share one register with discipline columns; the DPO and the CISO jointly own the integrated Inventory.
- Clause 10.2 corrective-action pathway, reconciliation gaps and audit findings feed the corrective-action pathway.
- Documented Information control, the Policy, the Procedure, the Inventory, the ROPA, the Retention Schedule, the Disposal Log, the matrices, and the reconciliation records are themselves controlled per Clause 7.5.
ROPA Policy (sample of our own drafting)
The organisation maintains the Records of Processing Activities (ROPA) as the master record of the PIMS. The ROPA records every processing activity involving personal data in the PIMS scope (Clause 4.3), with each entry capturing the activity name and description, the controller role, the processors and sub-processors, the categories of principals, the categories of personal data, the purpose(s), the lawful basis (DPDP section 4 / 7; GDPR Article 6), the consent-record reference, the recipients, the cross-border transfer destination(s) and mechanism, the retention period, the technical and organisational controls, the residual risk rating, the link to the DPIA, the link to the SoA entries, the link to the breach log, and the link to the DSAR log. The ROPA is reconciled against the application landscape on a quarterly cadence and against the operational systems (consent records, breach log, DSAR log, DPA register) on a quarterly cadence. The ROPA is owned by the DPO and authored with the relevant process owners. The ROPA is reviewed annually and on every material change.
Retention Schedule Policy (sample of our own drafting)
The organisation maintains the Retention Schedule as the privacy-specific overlay on the document-control discipline. The Schedule maps every record type in the Inventory to its retention driver (DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR, organisational) and its retention period. The Schedule operationalises the DPDP section 8(7) erasure obligation, the CERT-In Directions 28 April 2022 (180-day log retention within Indian jurisdiction), the RBI sector retention duties, the SEBI CSCRF incident-record retention, the IRDAI policyholder-data retention, the GDPR Article 30 ROPA-keeping, and the organisational retention decisions. The 48-hour pre-erasure notice to the Data Principal under DPDP Rules 2025 is operationalised. The Disposal Log evidences every end-of-life destruction event with the method, the date, the witnessing authority, and the legal-hold status.
Version-and-Approval Matrix Policy (sample of our own drafting)
Every record type in the Inventory has a defined approving authority per the Version-and-Approval Matrix. The privacy policy (Clause 5.2) is approved by top management; the procedures by the DPO; the ROPA entries by the DPO with the relevant process owners; the DPIA records by the DPO with the project owner; the breach-log entries by the incident-response lead with the DPO; the DSAR-log entries by the DSAR handler; the consent records by the consent-record owner (the marketing lead for marketing consent; the product lead for product consent; the HR lead for employee consent); the DPA records by the Legal Head with the DPO; the audit reports by the lead auditor; the management-review minutes by top management; the nonconformity and corrective-action records by the DPO and the corrective-action owner respectively.
Access-Control Matrix Policy (sample of our own drafting)
Every record type in the Inventory has defined access rules per the Access-Control Matrix, with the privacy-classification overlay applied. The classifications are: public (no restriction), internal (organisation-wide), confidential (need-to-know), restricted (named individuals), privileged (DPO, Legal Head, and counsel). A ROPA entry identifying a vulnerable principal's health data carries a "restricted" classification; a marketing-lead capture carries an "internal" classification; a breach investigation file carries a "privileged" classification. The Matrix is reviewed quarterly and on every material change to the role register (Clause 5.3).
Integrated-with-Distinction Statement (sample of our own drafting)
The organisation runs the PIMS Inventory and the ISMS Inventory (ISO/IEC 27001:2022 Clause 7.5) under a single register with discipline columns tagging each entry as ISMS-relevant, PIMS-relevant, AIMS-relevant, BCMS-relevant, or shared. The DPO and the CISO jointly own the integrated Inventory. The four control dimensions apply uniformly across the disciplines; the content tracks are differentiated. The ROPA is the PIMS-specific master record; the ISMS SoA is the ISMS-specific master record; the two reconcile at the operational-control level.
Risk Assessment and Treatment
This section is the operational core of Clause 7.5. It expands on the documented-information risk dimension introduced in Section 7 and provides the worked detail for the documented-information risk register, the treatment options, and the evidence discipline.
The documented-information risk register (the load-bearing addition)
The documented-information risk register is the operational expression of the documented-information dimension of the Clause 6.1 privacy risk register. Every material risk on the 6.1 register has a documented-information dimension, the record-reliability factor that determines whether the organisation can demonstrate the control when challenged. The Singahi documented-information risk register (toolkit doc 09) records per risk:
- Risk ID (cross-referenced to the 6.1 privacy risk register).
- Risk description, the documented-information failure scenario.
- Record-reliability factor, the records whose existence (or non-existence) determines whether the risk materialises (e.g., the breach log that anchors the DPDP clock (intimation without delay; 72-hour report); the consent record that demonstrates the section 6 consent; the DSAR log that demonstrates the section 11 response window; the ROPA that demonstrates the section 4 lawful basis).
- Treatment control(s), the documented-information control(s) that address the reliability factor (the relevant family discipline, the relevant retention entry, the relevant reconciliation cycle).
- Effectiveness metric, the reconciliation outcome or the audit result that tests whether the treatment is working.
- Residual documented-information risk, the post-treatment rating.
- Risk owner, typically the DPO with the relevant process owner.
Typical documented-information risk register entries for an Indian growing company:
- The breach log incomplete or stale, record-reliability factor: the breach log; treatment: the Family 3 discipline plus the reconciliation against the incident-response system; effectiveness metric: the reconciliation outcome.
- The ROPA does not reconcile with the application landscape, record-reliability factor: the ROPA; treatment: the Move 8 reconciliation; effectiveness metric: the reconciliation rate.
- The consent records cannot be produced on demand, record-reliability factor: the consent records; treatment: the Family 3 discipline plus the consent-platform audit trail; effectiveness metric: the consent-record retrieval test.
- The DSAR log misses the prescribed response window, record-reliability factor: the DSAR log; treatment: the Family 3 discipline plus the reconciliation against the support-ticketing system; effectiveness metric: the response-window compliance rate.
- The DPA register is incomplete, record-reliability factor: the DPA register; treatment: the Family 3 discipline plus the reconciliation against the procurement system; effectiveness metric: the procurement-system reconciliation rate.
- The retention schedule over-retains records past the section 8(7) period, record-reliability factor: the Retention Schedule; treatment: the Move 4 build plus the Disposal Log; effectiveness metric: the over-retention audit.
- The retention schedule under-retains records below the CERT-In 180-day period, record-reliability factor: the Retention Schedule; treatment: the Move 4 build; effectiveness metric: the under-retention audit.
- The Inventory does not reconcile with the operational systems, record-reliability factor: the Inventory; treatment: the Move 8 reconciliation; effectiveness metric: the reconciliation rate.
- The version-and-approval matrix is bypassed in practice, record-reliability factor: the matrix; treatment: the workflow enforcement in the DMS; effectiveness metric: the workflow-compliance rate.
- The access-control matrix over-permits access, record-reliability factor: the matrix; treatment: the privacy-classification overlay and the least-privilege review; effectiveness metric: the over-permission audit.
- The disposal log is incomplete, record-reliability factor: the Disposal Log; treatment: the Move 6 build plus the disposal-workflow enforcement; effectiveness metric: the disposal-log completeness audit.
- The Consent Manager records are not interoperable, record-reliability factor: the consent records (Family 3); treatment: the Consent Manager integration; effectiveness metric: the interoperability test.
The four documented-information treatment options
The four treatment options inherited from the Clause 6.1 methodology apply to the documented-information dimension:
Modify, apply documented-information controls (the Inventory, the ROPA, the Retention Schedule, the matrices, the Disposal Log, the reconciliation cycles) to reduce the record-reliability risk. The canonical option for most documented-information risks.
Retain, accept the residual documented-information risk where modify is not cost-effective or the risk is low-impact. Requires a documented risk-acceptance record by the documented-information risk owner.
Avoid, re-engineer the operational process so the record-reliability factor is removed (e.g., automate the consent-record capture so the manual-discipline risk is removed; automate the DSAR routing so the support-ticket risk is removed). Avoid is the highest-use option where the technology permits.
Share, transfer part of the documented-information risk through contractual allocation (the processor agreement's record-keeping clauses; the contractor-onboarding attestation; the cloud-provider's records-management commitments). Share does not eliminate the risk; it allocates the operational consequence.
The 7.5 risk register (the consolidated view)
| Documented-information risk | Record-reliability factor | Treatment | Effectiveness metric |
|---|---|---|---|
| Breach log incomplete or stale | Breach log (Family 3 / 7) | Modify (Family 3 discipline; reconciliation) | Reconciliation rate |
| ROPA does not reconcile with application landscape | ROPA (Family 3) | Modify (Move 8 reconciliation) | Application-landscape reconciliation rate |
| Consent records cannot be produced on demand | Consent records (Family 3) | Modify (consent-platform audit trail) | Consent-record retrieval test |
| DSAR log misses response window | DSAR log (Family 3) | Modify (reconciliation against ticketing) | Response-window compliance rate |
| DPA register incomplete | DPA register (Family 3) | Modify (reconciliation against procurement) | Procurement reconciliation rate |
| Over-retention (s.8(7) breach) | Retention Schedule (Family 1) | Modify (Move 4 build; Disposal Log) | Over-retention audit |
| Under-retention (CERT-In breach) | Retention Schedule (Family 1) | Modify (Move 4 build) | Under-retention audit |
| Inventory drift | Inventory (Family 1) | Modify (Move 8 reconciliation) | Reconciliation rate |
| Approval matrix bypassed | Approval matrix (Family 1) | Modify (workflow enforcement) | Workflow-compliance rate |
| Access over-permission | Access-control matrix (Family 1) | Modify (least-privilege review) | Over-permission audit |
| Disposal log incomplete | Disposal Log (Family 5 / 6) | Modify (Move 6 build; workflow) | Disposal-log completeness |
| 7.5-versus-8.x collapse | Inventory (Family 1) | Modify (demarcation-with-linkage) | Inventory structure audit |
| ISMS-reskin failure | Inventory (Family 1) | Modify (integrated-with-distinction) | Privacy-content coverage audit |
| ROPA-as-compliance-artefact pattern | ROPA (Family 3) | Modify (Move 3 reconciliation) | ROPA-currency audit |
| SDF records missing | SDF DPIA / audit / AI-fairness (Family 3 / 7) | Modify (Move 1 SDF track) | SDF-records completeness audit |
| Consent Manager records not interoperable | Consent records (Family 3) | Modify (Consent Manager integration) | Interoperability test |
The high-impact, high-likelihood documented-information risks to treat first are: the breach log incomplete or stale; the ROPA does not reconcile with the application landscape; the consent records cannot be produced on demand; the over-retention and the under-retention risks. These five risks account for most of the 7.5 audit nonconformities in the Indian growing-company segment.
Audit and Compliance Checklist
The 28 questions below cover the audit-evidence surface for Clause 7.5. Expected evidence and red flags noted. Most can be answered from the toolkit doc 04 audit-evidence checklist.
- Is there a Documented Information Policy (dated, version-controlled, signed by top management or the DPO with sponsor authority)? Red flag: missing.
- Is there a Document Control Procedure (the methodology artefact) documenting the seven-family inventory, the four control dimensions, the format-and-identification standard, the review-and-approval matrix, the access-control matrix, the version control standard, the change-control workflow, the retention schedule, and the disposal discipline? Red flag: missing or thin.
- Is there a PIMS Documented Information Inventory (the load-bearing artefact) recording every document and record in the PIMS scope with the family, the owner, the version, the effective date, the location, the format, the classification, the retention period, the disposal method, and the linkage to the controlling clause?
- Does the Inventory cover all seven families (Strategic and governance; Risk and treatment; Operational privacy; Support evidence; Evaluation; Improvement; Sector and regulatory)? Red flag: families missing.
- Does the Inventory reconcile with the application landscape (every application processing personal data has a corresponding ROPA entry)? Red flag: the reconciliation has not been performed.
- Does the Inventory reconcile with the procurement system (every processor has a corresponding DPA entry)? Red flag: the reconciliation has not been performed.
- Does the Inventory reconcile with the incident-response system (every breach has a corresponding breach-log entry)? Red flag: the reconciliation has not been performed.
- Does the Inventory reconcile with the support-ticketing system (every DSAR has a corresponding DSAR-log entry)? Red flag: the reconciliation has not been performed.
- Is there a ROPA (the master record) with each entry capturing the activity name and description, the controller role, the processors, the principal categories, the data categories, the purpose, the lawful basis, the consent-record reference, the recipients, the transfer destinations and mechanisms, the retention period, the controls, the residual risk, the DPIA link, the SoA link, the breach-log link, and the DSAR-log link?
- Is the ROPA current (refreshed within the last 12 months and on every material change)? Red flag: the ROPA-as-compliance-artefact pattern.
- Is there a Retention Schedule covering every record family with DPDP, CERT-In, RBI, SEBI, IRDAI, GDPR and organisational drivers?
- Does the Retention Schedule operationalise the DPDP section 8(7) erasure obligation and the 48-hour pre-erasure notice to the Data Principal?
- Does the Retention Schedule operationalise the CERT-In 180-day log-retention duty?
- Is there a Disposal Log recording the end-of-life destruction of records with the method, the date, the witnessing authority, and the legal-hold status? Red flag: missing.
- Is there a Version-and-Approval Matrix mapping each record type to its approving authority?
- Is there an Access-Control Matrix mapping each record type to its access rules with the privacy-classification overlay?
- Are the four control dimensions operational, create-and-update, identification-and-format, review-and-approval, distribution-access-storage-retention-disposal-and-change?
- Is there a reconciliation cycle running on a defined cadence (quarterly for the high-volume reconciliations; annually for the lower-volume reconciliations)?
- Do reconciliation gaps feed the Clause 10.2 corrective-action pathway? Red flag: gaps surfaced without corrective actions.
- Is the 7.5-versus-8.x demarcation in place, the Inventory links to the operational systems without reproducing the operational content?
- Is the integrated-with-distinction posture evidenced where the organisation runs an integrated ISMS+PIMS programme? The DPO and CISO co-author the methodology; the Inventory is shared with discipline columns; the content tracks are differentiated.
- Is the consent-record discipline operational, every consent capture is recorded, version-controlled, retrievable on demand, retained per the schedule, and disposed of per the Disposal Log? Red flag: the consent records cannot be produced on demand.
- Is the breach-log discipline operational, every breach is recorded, the awareness moment is captured, the dual-clock pattern (CERT-In 6h + DPDP without delay plus a 72-hour detailed report) is evidenced, the investigation file is retained, and the regulator-notification records are retained?
- Is the DSAR-log discipline operational, every rights request is recorded, the response-window compliance is evidenced, the principal-response records are retained?
- For Indian SDFs, are the section 10 records (SDF DPIA library, independent-data-audit reports, algorithmic-software review records) maintained under the 7.5 discipline?
- Are the Consent Manager records (give, manage, review, withdrawal) maintained in the interoperable format retained for the prescribed period?
- Is the documented-information discipline resourced under Clause 7.1 (budget, FTE, tooling)?
- Has the documented-information discipline been refreshed in the last 12 months, Inventory currency, ROPA currency, Retention Schedule currency, matrices currency, Disposal Log currency, reconciliation outcomes?
Evidence the auditor will physically request
- The dated and signed Documented Information Policy and Document Control Procedure.
- The PIMS Documented Information Inventory (with the per-record fields populated and reconciled with the operational systems).
- The ROPA (current, reconciled with the application landscape).
- The Retention Schedule (covering every record family with the regulator and organisational drivers).
- The Disposal Log (current, with the method, the date, the witnessing authority, the legal-hold status).
- The Version-and-Approval Matrix and the Access-Control Matrix.
- Sampled records, typically a processing activity in the ROPA, a vendor contract in the DPA register, a breach incident in the breach log, a rights request in the DSAR log, a consent record for a sampled principal.
- The reconciliation-cycle records (the application-landscape reconciliation, the procurement-system reconciliation, the incident-response-system reconciliation, the support-ticketing-system reconciliation).
- The integrated-with-distinction evidence: the joint DPO + CISO authorship; the shared Inventory with discipline columns; the distinct content tracks.
- The Clause 10.2 corrective-action records that originated from documented-information gaps.
- The interview, the DPO and the document-control function asked to walk through the four control dimensions for sampled records.
Common Stage-1 nonconformities the auditor will write up
- NC pattern 1: The Inventory does not exist or covers only Families 1 and 2. Major NC. Remediation: Inventory build, 8 to 14 weeks.
- NC pattern 2: The ROPA does not reconcile with the application landscape. Major NC. Remediation: the Move 8 reconciliation, 6 to 12 weeks.
- NC pattern 3: The Retention Schedule is missing or does not cover the regulator layers. Major NC. Remediation: the Move 4 build, 4 to 10 weeks.
- NC pattern 4: The Disposal Log is missing or thin. Minor or major NC. Remediation: the Move 6 build, 3 to 8 weeks.
- NC pattern 5: The 7.5-versus-8.x collapse, the Inventory reproduces operational records. Minor NC. Remediation: the demarcation-with-linkage restructure, 2 to 6 weeks.
- NC pattern 6: The ISMS-reskin failure, the Inventory has no privacy-specific entries. Major NC. Remediation: the seven-family inventory build, 6 to 12 weeks.
- NC pattern 7: The consent records, breach log, DSAR log, or DPA register are not under the 7.5 discipline. Major NC. Remediation: the Family 3 discipline extension, 6 to 12 weeks.
- NC pattern 8: The ROPA-as-compliance-artefact pattern, the ROPA has not been refreshed in 12+ months. Remediation: the Move 3 refresh, 4 to 8 weeks.
- NC pattern 9: Reconciliation gaps surfaced without corrective actions. Minor NC. Remediation: the 7.5-to-10.2 pipeline, 2 to 6 weeks.
Metrics and KPIs
Figure · Measures
The measures that show Clause 7.5 is working
- Inventory completeness100 %Periodic
- Inventory currency95 % or abovePeriodic
- ROPA-to-application-landscape reconciliation100 %Periodic
- ROPA currency95 % or abovePeriodic
- Consent-record retrieval test100 %Periodic
- Inventory completeness, the percentage of records in the PIMS scope that have an Inventory entry. Target: 100 percent.
- Inventory currency, the percentage of Inventory entries that have been reviewed within the defined cadence. Target: 95 percent or above.
- ROPA-to-application-landscape reconciliation rate, the percentage of applications processing personal data that have a corresponding ROPA entry. Target: 100 percent.
- ROPA currency, the percentage of ROPA entries that have been reviewed within the last 12 months and on every material change. Target: 95 percent or above.
- Consent-record retrieval test, the percentage of sampled consent requests that can be retrieved within the SLA (typically 24 to 72 hours). Target: 100 percent.
- DSAR-log response-window compliance rate, the percentage of DSARs handled within the prescribed response period. Target: 100 percent.
- Breach-log completeness, the percentage of breach events in the incident-response system that have a corresponding breach-log entry. Target: 100 percent.
- DPA-register completeness, the percentage of vendors in the procurement system that have a corresponding DPA entry. Target: 100 percent for in-scope vendors.
- Retention-schedule coverage, the percentage of record types in the Inventory that have a defined retention period in the Retention Schedule. Target: 100 percent.
- Over-retention audit, the percentage of sampled records retained beyond the schedule period. Target: 0 percent.
- Under-retention audit, the percentage of sampled records disposed of before the schedule period. Target: 0 percent.
- Disposal-log completeness, the percentage of disposal events with the method, the date, the witnessing authority, and the legal-hold status recorded. Target: 100 percent.
- Approval-matrix compliance rate, the percentage of records approved by the defined authority. Target: 100 percent.
- Access-control over-permission audit, the percentage of sampled access permissions that exceed the least-privilege principle. Target: under 5 percent.
- Reconciliation-cycle gap-to-corrective-action conversion rate, the percentage of reconciliation gaps that produced a Clause 10.2 corrective action. Target: 100 percent for material gaps.
Common Pitfalls and Audit Failures
Pitfall 1, The shared-drive practice. Documents and records scattered across shared drives, individual mailboxes, contractor laptops, and shadow-IT repositories. No Inventory; no Retrieval discipline; no version control; no access control. The single most common 7.5 failure pattern in the Indian growing-company segment. Treatment: the seven-move programme (Section 7).
Pitfall 2, The ROPA-as-compliance-artefact. The ROPA exists as a one-off document produced for the last audit; it has not been refreshed; it does not reconcile with the application landscape. Treatment: the Move 3 ROPA build with the Move 8 reconciliation.
Pitfall 3, The 7.5-versus-8.x collapse. The Inventory tries to be the operational system, reproducing every operational record inside the Inventory. Treatment: the demarcation-with-linkage posture.
Pitfall 4, The ISMS-reskin failure. The Inventory extends the ISMS document-control register with a few privacy entries but does not address the privacy-specific load (ROPA, consent records, DPIA library, DPA register, breach log, DSAR log, transfer records). Treatment: the seven-family inventory build.
Pitfall 5, The missing Retention Schedule. No retention discipline; records retained indefinitely or disposed of arbitrarily. Treatment: the Move 4 Retention Schedule build.
Pitfall 6, The disposal-without-evidence pattern. Records are disposed of but the disposal events are not logged. The organisation cannot defend against an under-retention allegation. Treatment: the Move 6 Disposal Log build.
Pitfall 7, The over-retention pattern. Records are retained beyond the period the regulator permits (especially beyond the DPDP section 8(7) erasure-obligation period). Treatment: the Retention Schedule operationalisation with the 48-hour pre-erasure notice.
Pitfall 8, The under-retention pattern. Records are disposed of before the period the regulator requires (especially the CERT-In 180-day log-retention duty and the sector-regulator retention duties). Treatment: the Retention Schedule operationalisation.
Pitfall 9, The unapproved-record pattern. Records enter service without the defined approval; the Version-and-Approval Matrix is bypassed in practice. Treatment: the workflow enforcement in the DMS.
Pitfall 10, The over-permission pattern. The access-control matrix over-permits access; the privacy classification is not applied. Treatment: the least-privilege review.
Pitfall 11, The reconciliation-without-corrective-action pattern. The reconciliation cycles surface gaps but the gaps do not feed Clause 10.2. Treatment: the 7.5-to-10.2 pipeline.
Pitfall 12, The Consent Manager records not interoperable. The consent records are not in the interoperable format the Consent Manager registration requires. Treatment: the Consent Manager integration with the interoperability test.
Pitfall 13, The dual-clock records gap. The breach log records the CERT-In 6-hour clock but not the DPDP breach clock (intimation without delay, then a 72-hour report; or vice versa); the same breach event produces inconsistent records across the two regimes. Treatment: the dual-clock-aware breach log.
Pitfall 14, The SDF records missing. The organisation has crossed the DPDP section 10 SDF threshold without realising it; the SDF DPIA library, the independent-data-audit reports, and the algorithmic-software review records are not under the 7.5 discipline. Treatment: the SDF-records track.
Pitfall 15, The shadow-IT records gap. The application landscape reconciliation surfaces shadow-IT applications that process personal data but have no Inventory entry. Treatment: the Move 8 reconciliation with the corrective-action pipeline.
Pitfall 16, The DSAR-log misses. The support-ticketing system receives rights requests that are treated as casual enquiries and never enter the DSAR log. Treatment: the reconciliation cycle with the support-team awareness (Clause 7.3).
Pitfall 17, The DPA-register gap. The procurement system onboards vendors without the privacy-flow-down clauses; the DPA register is incomplete. Treatment: the procurement-system reconciliation with the procurement-team awareness.
Pitfall 18, The retention-conflict pattern. Multiple regulators prescribe conflicting retention periods for the same record type (DPDP says erase; CERT-In says retain 180 days; RBI says retain longer). Treatment: the Retention Schedule reconciliation with documented justification.
Pitfall 19, The paper-records blind spot. The Inventory covers digital records but not paper records (signed consent forms, signed DPA originals, printed notices in physical branches). Treatment: the Inventory extension to paper records with the physical-storage location.
Pitfall 20, The integrated-without-distinction failure. The organisation runs an integrated ISMS+PIMS programme but the Inventory has no discipline columns; the privacy-specific load is invisible. Treatment: the integrated-with-distinction posture.
Pitfall 21, The version-control-by-filename pattern. Version control by filename convention ("_final_v3_USE_THIS") with no system enforcement. Treatment: the DMS-enforced version control.
Pitfall 22, The legal-hold blind spot. The disposal discipline does not accommodate legal holds; records under a legal hold are disposed of. Treatment: the legal-hold workflow integration with the Disposal Log.
Pitfall 23, The contractor-records blind spot. The Inventory covers employee records but not contractor records, temp records, or intern records. Treatment: the Inventory extension to the contractor ecosystem.
Pitfall 24, The programme drift. The discipline was built three years ago and has not been refreshed. The regulatory landscape has shifted (DPDP Rules 2025; sector-regulator updates); the application landscape has changed; the Inventory is fiction. Treatment: the annual review cycle; Clause 10.1 improvement.
Illustrative Scenario 1: Failure, Karuna Insurance Loses the Breach Record (Illustrative)
Illustrative scenario, a composite example for guidance, not a specific Singahi engagement or a verified outcome. It is set after 13 May 2027, when the DPDP Act's duties and the Board's inquiry and penalty powers take effect.
Illustrative scenario. Karuna Insurance is a fictional Mumbai-based health insurer with 1,100 staff, an IRDAI licence, and a digital-first policyholder onboarding flow; the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation.
Karuna Insurance built its PIMS in 2024 ahead of an ISO/IEC 27701:2019 certification push. The documented-information discipline was an extension of the ISMS document-control register, the ISO/IEC 27001:2022 Clause 7.5 register with six privacy entries appended (the privacy policy, the ROPA, the DPA register, the consent-policy document, the breach-response procedure, the DSAR procedure). There was no Inventory; no Retention Schedule; no Disposal Log; no version-and-approval or access-control matrices. The ROPA existed as a one-off compliance artefact produced for the certification audit, a 200-row spreadsheet that had not been refreshed since the audit. The breach log lived in the incident-response platform with no linkage to the 7.5 discipline. The DSAR log lived in the support-ticketing system with no linkage to the 7.5 discipline. The consent records lived in the consent-capture platform with no linkage to the 7.5 discipline.
In March 2028 a misconfigured API endpoint exposed a policyholder-data subset (approximately 47,000 policyholders' health-questionnaire responses) to an unauthenticated external caller for approximately 11 days. The misconfiguration was discovered by an external security researcher on 14 March 2028; the researcher notified the IRDAI Cyber Cell, the CERT-In, and the Karuna CISO on the same day. The CISO confirmed the exposure on 16 March 2028. The breach log was opened in the incident-response platform on 16 March 2028.
The dual-clock reporting discipline required the CERT-In 6-hour clock (notification within 6 hours of noticing, under the CERT-In Directions 28 April 2022) and the DPDP clock (intimation without delay, then the detailed report within 72 hours, under DPDP Rules 2025 Rule 7). The CERT-In notification was sent on 16 March 2028 within the clock. The DPDP notification to the Data Protection Board was sent on 18 March 2028 within the clock. The IRDAI notification was sent on 19 March 2028 within the IRDAI clock.
The DPBI preliminary inquiry (under DPDP section 18) requested the contemporaneous breach records, the moment Karuna became aware, the form and manner of the notification, the affected-principal notifications, the investigation file. The CISO produced the breach log from the incident-response platform; the DPO produced the notification correspondence. The investigation file was incomplete, the timeline between the researcher notification (14 March) and the CISO confirmation (16 March) had not been recorded, the awareness moment under section 8(6) was ambiguous, and the affected-principal notifications (sent 22 to 28 March) lived in individual mailboxes rather than in a controlled store.
The DPBI inquiry identified three root causes. First, the breach log was a system-generated artefact with no 7.5 discipline, no version control, no approval, no classification, no retention entry, no linkage to the ROPA or the SoA. Second, the awareness moment was ambiguous because the CISO-to-DPO-to-legal-to-IRDAI flow had no defined record-keeping duty, each role maintained its own working file; the consolidated timeline did not exist. Third, the affected-principal notification template was version 4 (revised mid-cycle) but the version-control discipline could not demonstrate which principal received which version.
The DPBI imposed a penalty of approximately 80 lakh rupees (under section 33 + the Schedule). The certification body issued a major nonconformity on Clause 7.5 at the next surveillance audit, cascading into nonconformities on 5.2 (policy), 8.x (operational breach-response), Annex A.3.25 (logging), and 10.2 (corrective action, the record-keeping gap that produced the failure was not being captured because there was no reconciliation cycle).
Commercial cost: a board-visible regulatory penalty in a sensitive sector, an estimated 30 to 45 lakh rupees in legal and advisory cost, a 4-month freeze on enterprise sales, and an 8-month remediation programme costing approximately 1.8 crore rupees.
The lessons: a breach log in the incident-response platform without 7.5 discipline is a record the regulator can request but not a record the organisation can defend; the dual-clock reporting discipline depends on the contemporaneous record-keeping discipline; the section 8(6) awareness moment is a record-keeping question as much as an operational question.
Illustrative Scenario 2: Success, Tarini Commerce Builds a ROPA-Anchored Documented-Information Discipline (Illustrative)
Illustrative scenario. Tarini Commerce is a fictional Bengaluru-based D2C e-commerce platform with 850 staff, a Payment Aggregator licence, and a multi-jurisdiction customer base (India, EU/EEA, UK, US); the facts are composite from publicly reported sector patterns and should not be attributed to any real organisation.
Tarini Commerce ran an integrated ISO/IEC 27001:2022 + ISO/IEC 27701:2019 programme with a shared document-control register, the ISMS document-control register with 14 privacy entries appended. The 7.5 discipline was thin; the ROPA existed as a 250-row spreadsheet that had been refreshed twice in three years; the retention discipline was implicit in the records-management module but not operationalised against the DPDP, CERT-In, RBI, SEBI or GDPR retention drivers; the consent records, the breach log, and the DSAR log were not under the 7.5 discipline.
In Q1 2027 the DPO commissioned a 7.5 refresh ahead of the 27701:2025 transition. The workshop surfaced six material shifts: the discipline was an ISMS reskin (privacy-specific load invisible); the seven-family inventory had never been built (312 record types mapped); the ROPA did not reconcile with the application landscape (14 shadow-IT applications with no ROPA entries); the retention schedule had never been built (a uniform 7-year retention breaching DPDP section 8(7) for some record types and breaching CERT-In's 180-day duty for others); there was no Disposal Log; and the reconciliation cycles did not exist.
Tarini rebuilt the discipline: the Inventory of 312 record types across the seven families; the ROPA of 187 processing activities reconciled against the 64-application landscape; the Retention Schedule with the DPDP, CERT-In, RBI, SEBI and organisational layers; the matrices with the privacy-classification overlay; the Disposal Log with crypto-shredding for cloud-stored records; the reconciliation cycles running quarterly for the high-volume systems.
The outcome over the first 18 months: the integrated-with-distinction posture cut parallel-programme overhead; the ROPA reconciliation surfaced 14 shadow-IT applications (an estimated 4 to 7 avoided DPDP section 8 compliance gaps at 5 to 12 lakh rupees per gap); the retention-schedule reconciliation surfaced approximately 18,000 records over-retained beyond the section 8(7) period, the disposal freed 4.2 terabytes of storage and reduced the under-retention exposure for the CERT-In 180-day window; the reconciliation cycles surfaced 9 vendors without DPAs, 23 support tickets that should have been DSARs, and 4 incidents that should have been classified as personal-data breaches, all routed to the Clause 10.2 pathway; the dual-clock-aware breach log produced contemporaneous records that supported a clean DPBI engagement on a Q3 2027 near-miss event (no penalty imposed).
The lessons: the integrated-with-distinction posture is the highest-use delivery decision for most Indian growing companies; the ROPA reconciliation against the application landscape is the single most-cited 7.5 evidence in a Stage 1 audit; the reconciliation cycles are the operational discipline that converts the Inventory from a static document into a system; the dual-clock-aware breach log is the single highest-use record-keeping investment for a regulated Indian Data Fiduciary.
Multi-Framework Mapping
| 27701:2025 7.5 theme | GDPR article | DPDP Act (India) section | NIST Privacy Framework | SOC 2 TSC | ISO 27001:2022 / 27002:2022 | ISO 29100 principle |
|---|---|---|---|---|---|---|
| PIMS documented information (the Inventory) | Art 5(2) accountability; Art 24 | s.8 general obligations | Identify-P (data mapping; business environment) | CC2.2; CC6.5 | 27001 Clause 7.5; 27002 control 5.33 | Accountability |
| ROPA (the master record) | Art 30 controller (30(1)) / processor (30(2)) ROPA | s.8 records; s.10 SDF audit records | Identify-P (data mapping) | P3.0 (collection); P7.0 (quality) | 27001 Clause 7.5 | Accountability; Collection limitation |
| Privacy policy as documented information | Art 5(2); Art 12(1) | s.5 notice (policy-level) | Communicate-P (transparency) | P1.0 (notice) | 27001 Clause 5.2 + 7.5 | Openness/transparency/notice |
| Consent records | Art 7(1) demonstrate of consent; Art 7(3) withdrawal records | s.6 consent (free, specific, informed, unconditional, unambiguous); s.2(1)(g) Consent Manager | Control-P (data-processing management) | P2.0 (choice/consent) | 27002 control 5.34 | Consent & choice |
| DPIA library | Art 35(7) DPIA content | s.10 SDF DPIA | Identify-P (risk assessment) | P8.0 (monitoring) | 27001 Clause 6.1 + 8.2; ISO/IEC 29134 | Accountability |
| Processor / sub-processor DPA records | Art 28(3) DPA mandatory clauses | s.8 (processor flow-down); s.2(1)(k) Data Processor | Control-P (DUA) | CC9.2 (vendor controls) | 27002 controls 5.19 to 5.23 | Accountability |
| Breach records (the dual-clock pattern) | Art 33 (72h to supervisory authority); Art 34 (to data subjects) | s.8(6) (without delay to Board; detailed report within 72 hours); CERT-In Directions 28 April 2022 (6h clock + 180-day logs) | Communicate-P (reporting) | CC7.3; CC7.4; P6.0 | 27002 controls 5.24 to 5.27; A.3 incident controls | Security safeguards; Accountability |
| DSAR / rights-handling log | Arts 12(3), 15 to 22 | s.11 access; s.12 correction/erasure; s.13 grievance (prescribed period); s.14 nomination | Communicate-P (data-review; authorization) | P5.0 (access); P6.0 (disclosure) | 27002 control 5.34 | Individual participation & access |
| Transfer records (negative list / adequacy / SCCs) | Chapter V (Arts 44 to 49); Schrems II TIA | s.16 negative-list transfer | Control-P (data-processing management) | CC6.6 | (not in 27002) | Use, retention & disclosure limitation |
| Retention schedule + erasure | Art 5(1)(e) storage limitation; Art 17 erasure | s.8(7) erasure; Rules' retention + 48h pre-erasure notice | Control-P (data-processing management) | P4.0 (use/retention/disposal) | 27002 control 5.34; A.3.21 secure disposal | Use, retention & disclosure limitation; Data minimisation |
| Disposal log (secure deletion) | Art 17; Art 5(1)(f) integrity/confidentiality | s.8(7) erasure (evidenced) | Protect-P (data integrity) | CC6.5; CC7.1 | 27002 control 8.10 information deletion; A.3.21 | Security safeguards |
| Children's-data records | Art 8 child consent | s.9 verifiable parental consent; no behavioural tracking records | Control-P | P2.0 (consent) | 27002 control 5.34 | Consent & choice |
| SDF records (SDF DPIA / audit / AI-fairness) | Art 35(3)(a) DPIA; Art 22 ADM | s.10 SDF (DPIA, independent audit, algorithmic-software review) | Identify-P + Communicate-P | CC4.2; P8.0 | 27001 Clause 9.2; ISO/IEC 42001:2023 | Accountability |
| Grievance records | Art 13(2)(d) right to lodge complaint | s.13 grievance redressal (prescribed response period) | Communicate-P (reporting) | P6.0 | (none PII-specific) | Individual participation & access |
| Consent Manager records (interoperable, revocable) | (no direct EU analogue) | s.2(1)(g) + s.6 Consent Manager records | Control-P (data-processing management) | P2.0 | 27002 control 5.34 | Consent & choice |
| Version-and-approval matrix | Art 5(2); Art 24(1) | s.8 general obligations | Govern-P (governance) | CC3.2; CC3.3 | 27001 Clause 7.5 | Accountability |
| Access-control matrix (privacy-classification overlay) | Art 5(1)(f); Art 32 | s.8(5) safeguards | Protect-P (data security) | CC6.1 to CC6.5 | 27002 controls 5.12 to 5.18 (access control) + 8.2 to 8.5 | Security safeguards |
| Internal audit + management-review records | Art 5(2); Art 24(2); Art 32(1)(d) | s.8(5) safeguards; s.10 SDF audit | Govern-P (risk-management strategy) | CC4.1; CC4.2 | 27001 Clauses 9.2 + 9.3 + 7.5 | Accountability |
| Nonconformity + corrective-action records | Art 5(2); Art 24(1) | s.8 general obligations | Govern-P | CC4.2 | 27001 Clauses 10.2 + 7.5 | Accountability |
The densest cross-framework mappings are at the ROPA row (GDPR Art 30 / DPDP s.8 + s.10 / ISO/IEC 27001:2022 Clause 7.5), the consent-records row (GDPR Art 7(1) + 7(3) / DPDP s.6 + the Consent Manager s.2(1)(g) / ISO/IEC 27002:2022 control 5.34), the breach-records row (GDPR Art 33 to 34 / DPDP s.8(6) without delay, with a 72-hour detailed report / CERT-In 6h + 180-day), and the retention-and-erasure row (GDPR Art 5(1)(e) + Art 17 / DPDP s.8(7) / ISO/IEC 27002:2022 control 8.10).
The unique-to-India rows are the dual-clock-trigger row (CERT-In 6 hours + DPDP intimation without delay and a 72-hour report + sector six hours, no direct EU analogue exists), the Consent Manager records row (no direct GDPR analogue, a distinctive Indian construct), and the SDF-records row (DPDP section 10, the SDF DPIA, independent-data-audit and algorithmic-software review records).
Implementation Roadmap
30 days
- Adopt the Documented Information Policy (Move 1) and confirm the seven-family inventory decision.
- Stand up the PIMS Documented Information Inventory (Move 2), a structured spreadsheet is acceptable for the first cycle; the discipline is that every document and record is logged from day one.
- Build the Document Control Procedure (Section 9.2) covering the four control dimensions.
- Begin the Inventory population across Families 1 and 2 (Strategic and governance; Risk and treatment), the easiest families to capture because the artefacts are well-known.
- Begin the ROPA scoping (Move 3 Phase A), the application landscape walk.
90 days
- Complete the Inventory population across Families 3 (Operational privacy), 4 (Support evidence), 5 (Evaluation), 6 (Improvement) and 7 (Sector and regulatory).
- Build the ROPA (Move 3 Phases B and C), the processing-activity deep dive and the operational reconciliation.
- Build the Retention Schedule (Move 4) with the DPDP, CERT-In and organisational layers.
- Define the Version-and-Approval Matrix (Move 5) and the Access-Control Matrix with the privacy-classification overlay.
- Stand up the Disposal Log (Move 6) and the change-control workflow.
- Run the first reconciliation cycle (Move 7) for the highest-volume operational systems (the application landscape, the incident-response system).
180 days
- Run the full reconciliation cycle (Move 7) for the remaining operational systems (the procurement system, the support-ticketing system, the contract repository, the HR system).
- Route the reconciliation gaps to the Clause 10.2 corrective-action pathway.
- Present the documented-information profile to the management review (Clause 9.3) for the first time.
- Run the integrated-with-distinction review with the CISO (the shared Inventory with discipline columns, the distinct content tracks).
- Begin the sector-regulator overlay work for BFSI (RBI, SEBI, IRDAI), Healthcare, IT-ITeS or Edtech as applicable.
12 months
- Run the full quarterly and annual reconciliation cycles.
- Wire the documented-information profile into the management review (Clause 9.3).
- Run the first annual review of the Inventory currency, the ROPA currency, the Retention Schedule currency, the matrices currency, and the Disposal Log currency.
- Run an internal-audit test against the Section 11 checklist (Clause 9.2).
- Calibrate the metrics against the Section 12 targets.
- Reassess the SDF designation in light of the data-volume growth (where applicable) and build the SDF-records track ahead of the designation.
FAQ
Q1. We already have an ISO/IEC 27001:2022 Clause 7.5 document-control register. Can we reuse it for 27701?
Yes, with the integrated-with-distinction migration (Section 9.7). The ISMS register covers the ISMS-relevant records; the PIMS register adds the privacy-specific load, the seven-family inventory with the privacy-specific families (Family 3 Operational privacy; Family 7 Sector and regulatory), the ROPA-as-master-record concept, the retention-schedule overlay with the DPDP, CERT-In and sector-regulator layers. Most Indian growing companies run a single Inventory with discipline columns.
Q2. Our Inventory is a spreadsheet. Is that enough?
Yes for the first cycle. The test is whether the Inventory reconciles with the operational systems, whether every record has the per-record fields populated, and whether the reconciliation cycles are running. A spreadsheet that does all of that outperforms a GRC-platform record that does none of those things.
Q3. What is the difference between 7.5 (documented information) and Clause 8 (operation)?
Clause 7.5 governs how documented information is controlled, the version, the access, the retention, the disposal, the change. Clause 8 produces the operational records, the ROPA, the consent records, the DPIA library, the DPA register, the breach log, the DSAR log, the transfer records. The two interact (7.5 controls what Clause 8 produces) but the demarcation is load-bearing. The canonical failure is the collapse, the Inventory tries to be the operational system.
Q4. How often should we reconcile the Inventory against the operational systems?
The Singahi recommended cadence is quarterly for the high-volume reconciliations (the application landscape, the procurement system, the incident-response system, the support-ticketing system) and annually for the lower-volume reconciliations (the contract repository, the HR system). The reconciliation outcomes feed the awareness profile and the Clause 10.2 corrective-action pathway.
Q5. Does every record need an approving authority?
Yes, per the Version-and-Approval Matrix. The authority varies by record type, top management for the privacy policy; the DPO for the procedures; the DPO with the process owners for the ROPA entries; the incident-response lead with the DPO for the breach-log entries. The matrix is the operational discipline that prevents the unapproved-record pattern.
Q6. What is the ROPA, and why is it the master record?
The ROPA is the Records of Processing Activities, the single document that links processing activities to purposes, lawful bases, retention periods, recipients, transfers, controls and risks. It is the GDPR Article 30 analogue; the DPDP section 8 records-of-compliance artefact; the anchor for almost every other PIMS clause. The ROPA is the master record because every audit, every DPIA, every DSAR response, every breach investigation and every regulator engagement hangs off it.
Q7. How do we handle retention when multiple regulators prescribe conflicting periods?
The Retention Schedule reconciliation with documented justification for the selected period. Typically the longest applicable period is selected, but with documented justification where a shorter period is selected (e.g., the DPDP section 8(7) erasure obligation overriding a longer organisational retention for marketing-consent records where the principal has withdrawn consent). The 48-hour pre-erasure notice to the Data Principal must be honoured where the DPDP Rules apply.
Q8. We are not yet an SDF. Do we need the section 10 records?
The section 10 records (the SDF DPIA library, the independent-data-audit reports, the algorithmic-software review records) are mandatory for SDFs under DPDP section 10. The discipline is to run the SDF-designation analysis annually; if the thresholds are approachable, build the section 10 records track ahead of the designation. The 27701:2025 documented-information discipline is the natural single framework that satisfies both.
Q9. How do we handle the dual-clock pattern in the documented-information discipline?
The dual-clock-aware breach log (toolkit doc 08) records the same breach event under both regimes, the CERT-In 6-hour record (the ICT-incident angle) and the DPDP record (intimation without delay, then a 72-hour report; the personal-data-breach angle). For BFSI and listed entities, the sector-regulator record (RBI, SEBI, IRDAI) is added. The discipline ensures the awareness moment, the notification correspondence, the affected-principal notifications, and the investigation file are recorded contemporaneously and controlled under the 7.5 discipline.
Q10. Our consent records live in the consent-capture platform. Are they "documented information"?
Yes. Family 3 (Operational privacy records) includes the consent records. The 7.5 discipline applies, the consent records are version-controlled (the consent-text version), access-controlled (the privacy-classification overlay), retained per the Retention Schedule (the DPDP period plus the sector-regulator overlays), and disposed of per the Disposal Log. The Inventory links to the consent-capture platform without reproducing every consent record inside the Inventory.
Q11. What is the Consent Manager records duty under DPDP section 2(1)(g)?
A Consent Manager must enable the principal to give, manage, review and withdraw consent across multiple Data Fiduciaries. The consent records (give, manage, review, withdrawal) must be in the interoperable format, retained for the prescribed period, and made available to the principal and to the Board on demand. The 7.5 discipline must operationalise the Consent Manager registration conditions.
Q12. How do we measure whether the documented-information discipline is working?
The 15-KPI set (Section 12): Inventory completeness and currency; ROPA-to-application-landscape reconciliation rate; ROPA currency; consent-record retrieval test; DSAR-log response-window compliance rate; breach-log completeness; DPA-register completeness; retention-schedule coverage; over-retention and under-retention audits; disposal-log completeness; approval-matrix compliance rate; access-control over-permission audit; reconciliation-cycle gap-to-corrective-action conversion rate.
Q13. Our Inventory covers digital records but not paper records. Is that acceptable?
No, where paper records exist in the operational reality (signed consent forms, signed DPA originals, printed notices in physical branches). The Inventory extension to paper records with the physical-storage location and the retention entry is required. The Disposal Log records the secure-destruction event for the paper records (cross-cut shredding; certificate of destruction for outsourced disposal).
Q14. Can we run one combined documented-information discipline across multiple management systems (27001 + 27701 + 42001)?
Yes, with the harmonized-structure integration (Section 6.3). One Inventory with discipline columns, one Document Control Procedure, one retention schedule overlay, one Disposal Log. The content tracks are differentiated; the discipline is unified.
Q15. Our auditors sampled five records and one of them could not be traced through the four control dimensions. Is that a nonconformity?
A single un-traceable record is typically a minor NC with a targeted remediation (the record is reconstructed; the underlying discipline is reinforced). A pattern of un-traceable records is a major NC indicating the documented-information discipline is producing an Inventory but not the underlying control. The reconciliation cycles are the early-warning system.
Industry-Specific Requirements
BFSI
Banks, NBFCs, payment aggregators, payment gateways, insurers. The BFSI documented-information discipline carries the heaviest regulatory load: the DPDP records (sections 8, 8(6), 10), the CERT-In 180-day log retention, the RBI directives (Storage of Payment System Data 2018; Digital Lending 2022; Tokenisation; Cybersecurity Directions 2026), the SEBI CSCRF (2024), the IRDAI Information and Cyber Security Guidelines (2023). The Retention Schedule must reconcile the DPDP section 8(7) erasure obligation with the RBI payment-data retention (which may require longer retention for fraud-detection and AML purposes), the SEBI KYC retention, and the IRDAI policyholder-data retention. The dual-clock-aware breach log must accommodate the CERT-In 6-hour clock, the DPDP breach clock (intimation without delay; 72-hour report), the RBI six-hour clock, the SEBI 6-hour clock, and the IRDAI 24 to breach clock (intimation without delay; 72-hour report). The Inventory priority order for BFSI: the ROPA with the payment-data plane fully mapped; the breach log with the dual-clock-aware records; the consent records (borrower + marketing); the DPA register with the processor-chain discipline; the DSAR log with the policyholder-rights discipline.
Healthcare
Hospitals, telemedicine platforms, healthtech, insurers processing health data. The documented-information discipline must address the heightened sensitivity of health data (the DPDP section 9 analog for vulnerable data subjects; the SPDI Rules' explicit inclusion of health data; clinical-data-confidentiality expectations; the IRDAI framework where insurance is involved). The ROPA entries identifying health data carry the "restricted" or "privileged" privacy classification with the access-control overlay (the care team and the DPO; not the marketing team). The children's-data records (Family 3) are load-bearing for paediatric services, the verifiable-parental-consent records must be retained per the DPDP Rules. The Tier 2 heightened-records track is critical for AI-driven diagnostic engines (the algorithmic-software review records).
IT-ITeS and SaaS
IT services firms, BPOs, SaaS providers, cloud processors. The documented-information discipline is almost always "both", the customer's principals reached through the organisation's processing (processor-side load: the DPA register with the executed customer agreements; the sub-processor records with the change-notification and controller-approval records; the infringing-instruction records per Annex A.2.2.5; the breach-notification-to-controller records), and the organisation's own employees and marketing-lead contacts (controller-side load: the ROPA for the employee data and the marketing data; the consent records; the DSAR log). The contractor-records track (Family 4) is critical, the contractor-ecosystem records (often hundreds or thousands of personnel producing records) must be in the Inventory. The cross-border-transfer records are central, most ITeS firms process data of overseas principals under GDPR/CCPA jurisdiction; the transfer records and the transfer-impact assessments must be under the 7.5 discipline.
E-commerce and Retail
D2C brands, marketplaces, e-commerce platforms, omni-channel retailers. The documented-information discipline must address consumer-privacy records at scale, the children's-data records where minors are in the user base, the marketing-consent records (the section 6 consent discipline), the supplier-ecosystem DPA records, the payment-data overlays (RBI Tokenisation records, the Payment Aggregator records). The Consent Manager records (Family 3) are particularly relevant for consumer-facing firms; the documented-information discipline must accommodate the Consent Manager interoperability, the principal-side consent management, and the withdrawal records. The retention-schedule reconciliation is especially load-bearing for e-commerce, the marketing-consent records, the transactional records, the support records, the recommendation-engine records each carry different retention drivers.
Edtech
K-12 platforms, higher-edtech, skilling platforms, test-prep. The children's-data records (Family 3) are the central documented-information issue, the principal is a minor, the consent dynamic is parental, and the section 9 verifiable-parental-consent records and the no-behavioural-tracking records are load-bearing. The retention schedule for children's-data records must operationalise the DPDP Rules 2025 verifiable-parental-consent mechanism and the erasure discipline when the minor comes of age. The Tier 2 SDF records (algorithmic-software review for adaptive-learning engines) are critical.
Manufacturing
Discrete and process manufacturing, automotive, chemicals, pharma manufacturing. The documented-information discipline must address the OT-IT convergence (operational technology systems increasingly connected, with PII exposure in HR, contractor and visitor data records), the supply-chain processor records (the supplier-ecosystem DPAs), the geopolitical context for cross-border manufacturing data flows (the multi-jurisdiction ROPA). The principal set includes employees, contractors, visitors, customers (where the manufacturer operates a direct-to-customer channel), and patients (for pharma manufacturing with patient-level pharmacovigilance records). The contractor-records discipline (Family 4) is the highest-use single discipline for the manufacturing segment.
Cross-sector patterns
Three patterns recur across sectors.
The shadow-IT pattern. The application-landscape reconciliation surfaces shadow-IT applications that process personal data without Inventory entries. The Move 8 reconciliation with the corrective-action pipeline is the universal treatment.
The retention-conflict pattern. Multiple regulators prescribe conflicting retention periods for the same record type. The Retention Schedule reconciliation with documented justification is the universal treatment.
The dual-clock records pattern. BFSI and listed entities carry dual-regulator exposure, DPDP via the Data Protection Board plus the sector regulator. The dual-clock-aware breach log is the universal treatment.
Maturity Model
Figure · Tiers
Maturity levels for documented information
- OptimisedA continuous documented-information
- ManagedA demonstrable discipline. The Inventory
- DefinedA structured discipline
- ReactiveA programme exists but is mostly
- InitialA shared-drive practice
| Level | Description |
|---|---|
| L1, Initial | A shared-drive practice; documents and records scattered across shared drives, individual mailboxes, contractor laptops, shadow-IT repositories; no Inventory; a ROPA that exists as a one-off compliance artefact produced for the last audit; no Retention Schedule; no Disposal Log; version control by filename convention; the document-control register owned by ISMS or Quality with no privacy-specific entries. |
| L2, Reactive | A programme exists but is mostly the ISMS-reskin pattern with a few privacy entries; the Inventory covers Families 1 and 2 but not Families 3 or 7; the ROPA exists but has not been refreshed in 12-plus months; the Retention Schedule is partial; the Disposal Log is missing; reconciliation cycles are not running. |
| L3, Defined | A structured discipline with the seven-family inventory, the four control dimensions, the ROPA reconciled with the application landscape, the Retention Schedule with the DPDP, CERT-In and organisational layers, the matrices with the privacy-classification overlay, the Disposal Log, the reconciliation cycles running quarterly for the high-volume systems. |
| L4, Managed | A demonstrable discipline. The Inventory reconciles with every operational system. The retention-schedule reconciliation surfaces both over-retention and under-retention exposure. The dual-clock-aware breach log produces contemporaneous records that support a clean DPBI engagement. The reconciliation-cycle gaps feed the Clause 10.2 pathway. The SDF-records track is in place for SDFs. The integrated-with-distinction posture is operational. Cross-framework reconciliation (DPDP / GDPR / NIST / SOC 2 / ISO 27001 / ISO 27002 / ISO 42001). |
| L5, Optimised | A continuous documented-information capability. The Inventory is integrated with the operational systems in near-real-time (the consent records flow into the Inventory; the breach events flow into the Inventory; the DSAR events flow into the Inventory). The retention-schedule disposal runs automatically at end-of-life with the 48-hour pre-erasure notice wired into the principal-communication workflow. The dual-clock-aware breach log supports the regulatory engagement across all the applicable regimes. The documented-information discipline demonstrably reduces the regulatory exposure (every clock, every record, every right depends on the discipline). |
Emerging Trends
DPDP SDF designations and the section 10 records cadence. The Central Government is expected to designate the first wave of SDFs through 2026 and 2027. Designated SDFs must operationalise the SDF DPIA library, the independent-data-audit reports, and the algorithmic-software review records under the 7.5 discipline.
DPBI operational emergence. The Data Protection Board of India, constituted under DPDP section 18, is emerging through 2026 and 2027. Its early orders, its interpretation of the Schedule penalty maxima, and its precedent on the record-keeping duty will reshape the 7.5 landscape for every Indian Data Fiduciary. The contemporaneous-record-keeping discipline is the operational hedge.
Consent Manager ecosystem emergence. The DPDP Rules 2025 prescribe Consent Manager registration conditions; the first Consent Managers are expected through 2026 and 2027. The Consent Manager records (give, manage, review, withdrawal in the interoperable format) become operational.
AI-driven processing and the algorithmic-fairness records dimension. The Rule 13(3) algorithmic-software review and the parallel development of ISO/IEC 42001:2023 (AI Management System) are reshaping the 7.5 documented-information landscape. For organisations using AI/ML on personal data, the algorithmic-fairness records dimension is the highest-use Tier 2 addition.
Integrated management systems documented information. The harmonized structure enables integrated 27001 + 27701 + 42001 + 22301 governance. The documented-information discipline is the natural point of integration, a single Inventory with discipline columns, a single Document Control Procedure, a single Retention Schedule overlay.
Generative AI in the documented-information discipline itself. The use of generative AI inside the discipline (for Inventory reconciliation, for ROPA drafting, for retention-schedule conflict resolution) is a 7.5 trend, and a 7.5 risk (the discipline must not leak personal data through the generative-AI tooling).
Privacy-platform-as-a-service. The Indian market is seeing the emergence of privacy-platform-as-a-service offerings, managed platforms that bundle the ROPA module, the consent module, the DSAR module, the breach module, the retention module, the disposal module. For growing companies without the internal FTE, the as-a-service model is a viable L3 / L4 pathway.
Reconciliation-as-a-discipline. The audit-evidence expectation is shifting from the static Inventory to the reconciliation discipline. The 7.5 programme that delivers reconciliation evidence is increasingly the auditor's expectation; the programme that delivers only a static Inventory is increasingly the auditor's finding.
References and Further Reading
Primary instruments (India). Digital Personal Data Protection Act, 2023 (Act No. 22 of 2023, enacted 11 August 2023), MeitY, sections 4, 5, 6, 8 (8(5) safeguards, 8(6) the breach clock (intimation without delay; 72-hour report), 8(7) erasure), 9 (children and persons with disability), 10 (SDF), 11 to 14 (rights), 16 (cross-border negative list), 18 (DPBI), 33 + Schedule (penalty maxima). Digital Personal Data Protection Rules, 2025 (notified 13 November 2025), MeitY, Rule 7 (breach intimation without delay, the 72-hour detailed report and format); SDF thresholds; Consent Manager registration; verifiable parental consent; the data-retention and erasure timelines including the 48-hour pre-erasure notice; the grievance-redressal response periods. Information Technology Act, 2000, sections 43A, 72A. IT (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011 (notified 11 April 2011). CERT-In Directions 20(3)/2022-CERT-In (28 April 2022), the 6-hour clock and the 180-day log retention. RBI Storage of Payment System Data (6 April 2018); RBI Digital Lending Guidelines (2 September 2022); RBI Tokenisation (22 September 2021); RBI Cybersecurity Directions 2026 (31 July 2026). SEBI Cybersecurity and Cyber Resilience Framework (20 August 2024); SEBI KRA Regulations and Master Circular (May 2024). IRDAI Information and Cyber Security Guidelines 2023 (24 April 2023). Companies Act 2013 (for listed entities, the Risk Management Committee discipline and the records-retention expectations).
Primary jurisprudence (India). K.S. Puttaswamy v. Union of India, (2017) 10 SCC 1 (nine-judge Bench, 24 August 2017). Justice K.S. Puttaswamy (Retd.) v. Union of India (Aadhaar), (2019) 1 SCC 1 (five-judge Bench, 26 September 2018).
Primary instruments (global). Regulation (EU) 2016/679 (GDPR), OJ L 119, 4.5.2016, p. 1, Article 5(2) (accountability), Article 24 (controller responsibility), Article 28(3) (DPA mandatory clauses), Article 30 (ROPA), Article 32 (security of processing), Article 33 to 34 (breach notification records), Article 35(7) (DPIA content). EDPB Guidelines 4/2019 on Article 25. Article 29 WP248 rev.01, Guidelines on DPIA. AICPA, 2017 Trust Services Criteria, CC2.2, CC6.5, CC7.1, the Privacy category P3.0. NIST Privacy Framework v1.0, NIST.CSWP.01162020, 16 January 2020, Identify-P and Communicate-P. Brazil LGPD, Lei nº 13.709/2018. China PIPL, Article 55 (mandatory PIA). ISO/IEC 27001:2022 Clause 7.5. ISO/IEC 27002:2022 controls 5.33 (Protection of records), 5.34 (Privacy and protection of PII), 8.10 (Information deletion). ISO/IEC 29100:2011. ISO/IEC 29134:2017 (DPIA guidelines). ISO/IEC 27018:2019. ISO/IEC 42001:2023 (AI Management System). ISO/IEC 27706:2025 (PIMS cert-scheme competence).
This guide accompanies the Singahi toolkit "ISO/IEC 27701:2025 Clause 7.5, Documented Information". The ISO/IEC 27701:2025 clause text is copyrighted by ISO/IEC and has not been reproduced; all requirements are paraphrased.